

reverse-shell-generator
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
ctfexploitationpayload-development+6
4.1k
0dayctf/reverse-shell-generatorHosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 xxdndxx/ctf-tracker
Offline-first dashboard for tracking CTF machines and labs, with attack lifecycle management, dynamic reverse shell builder, and embedded writeup…
 ariary/notionterm
Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 dotnetguard/cve-2025-55182-exploit
CVE-2025-55182 — Next.js Flight Deserialization RCE exploit with interactive shell, single-command execution and multi-payload reverse shell chain.…
 0xdak/cve-2026-14483_exploit
Unauthenticated arbitrary file upload exploit for Realtyna WPL/Organic IDX WordPress plugin, chains PHP webshell upload to RCE, with command…
 davuxvi/cve-2023-27163
Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
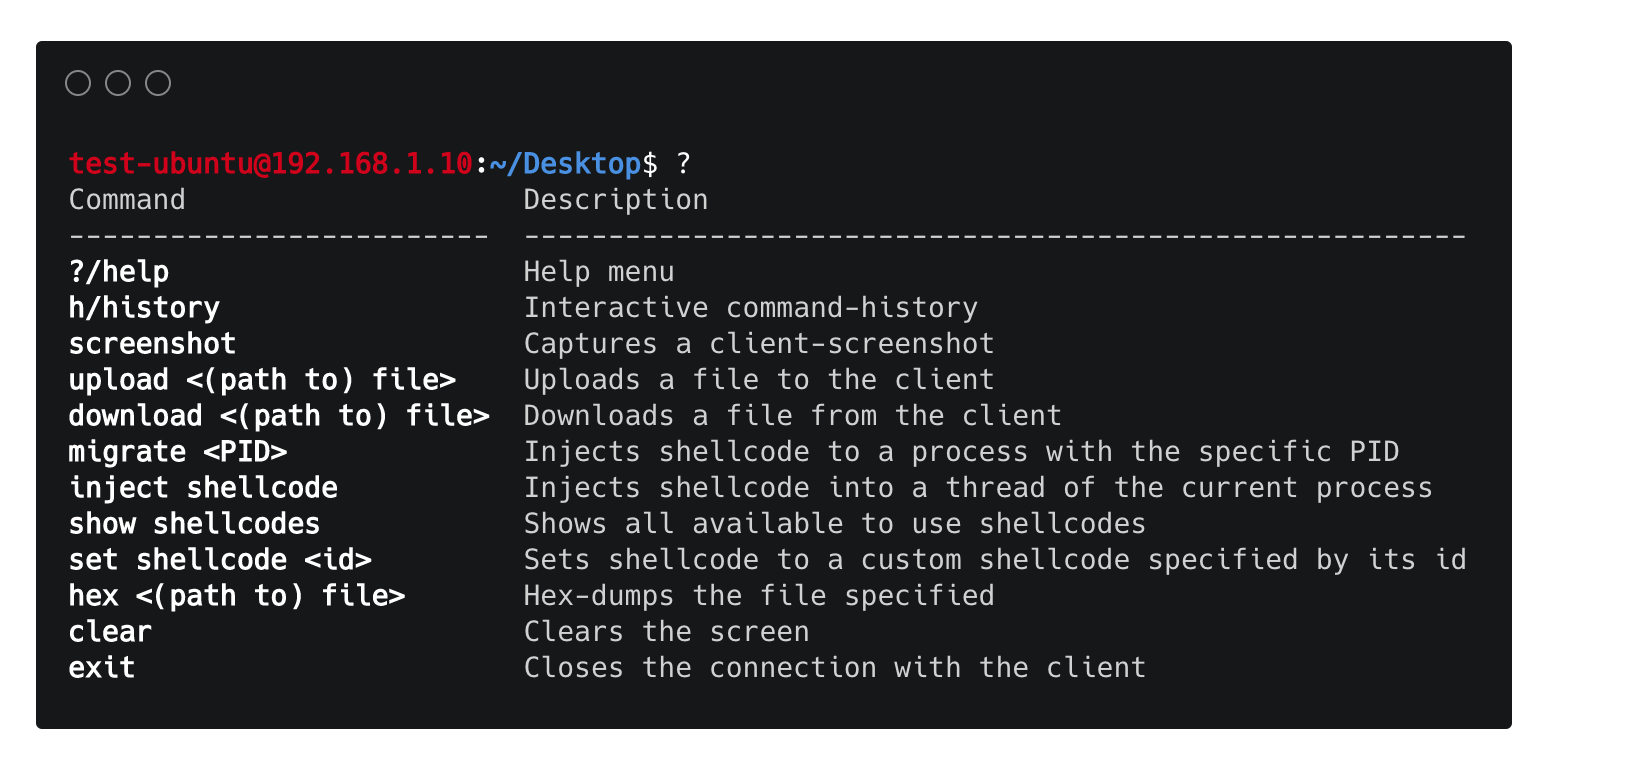 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 e5dfdd568a75282b712b6d93a7a18e12/cve-2025-32432
Python exploit for CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii2 __class injection, with command execution and reverse shell support.
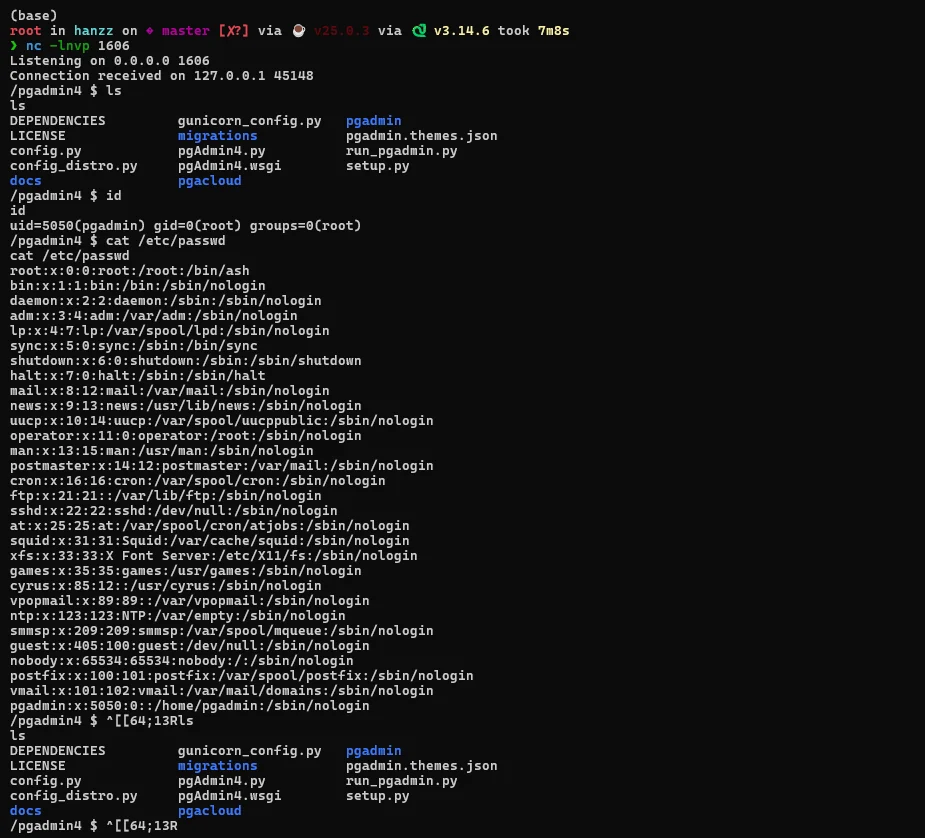 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
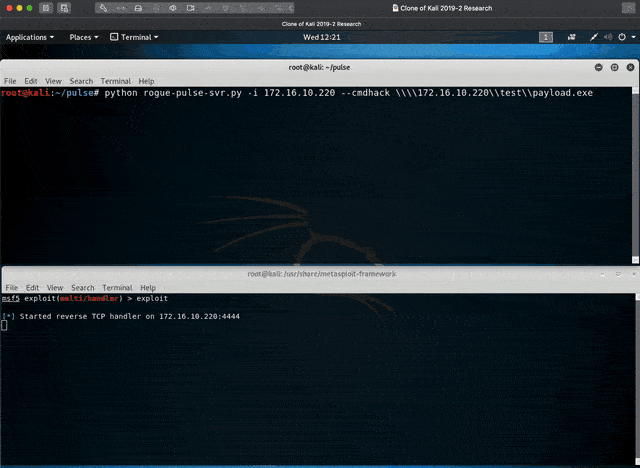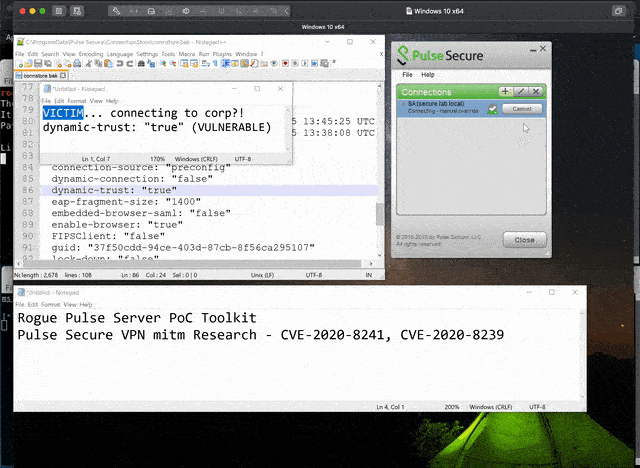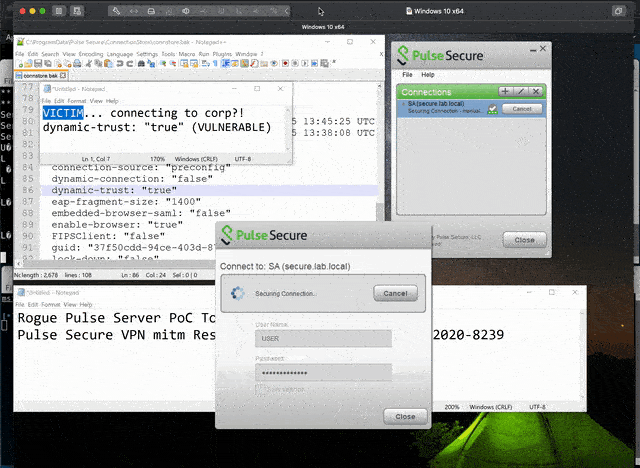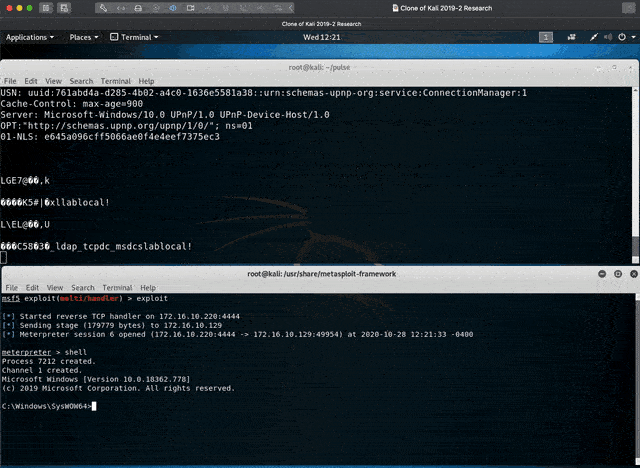 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
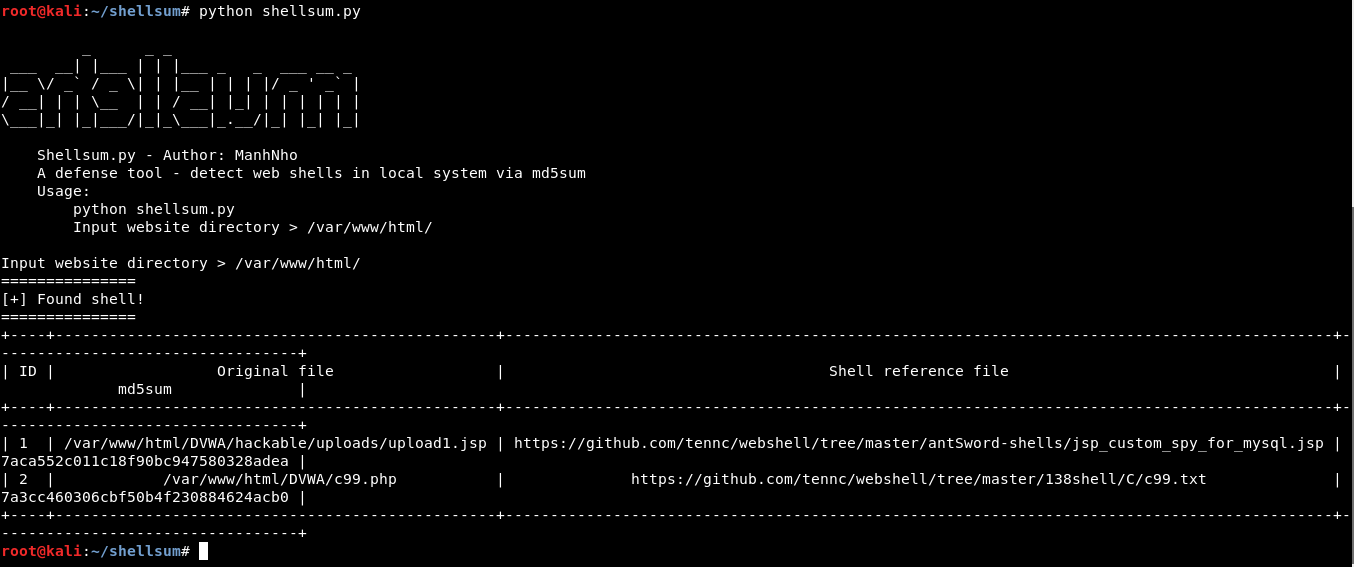 manhnho/shellsum
A defense tool - detect web shells in local directories via md5sum
 emposha/php-shell-detector
Web Shell Detector – is a php script that helps you find and identify php/cgi(perl)/asp/aspx shells. Web Shell Detector has a “web shells” signature…