

web2py-e94946d-CVE-2016-3957
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
authenticationcode-analysisdatabase-security+3
sj/web2py-e94946d-cve-2016-3957web2py/web2py @ e94946d
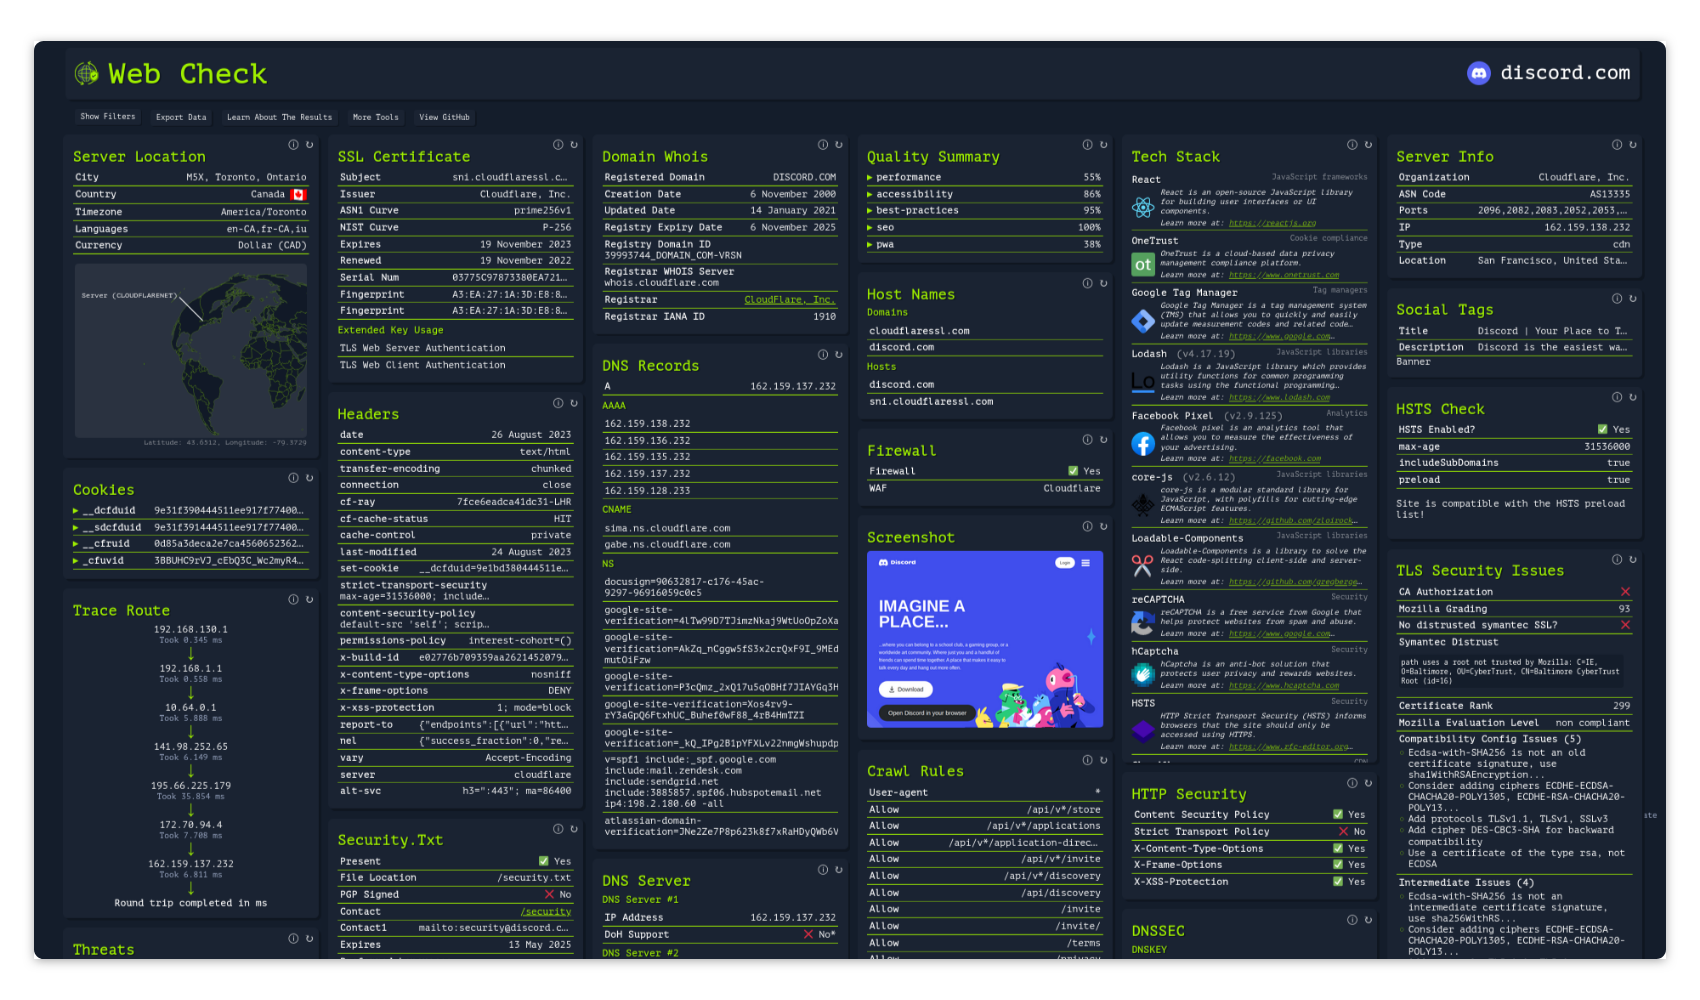 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
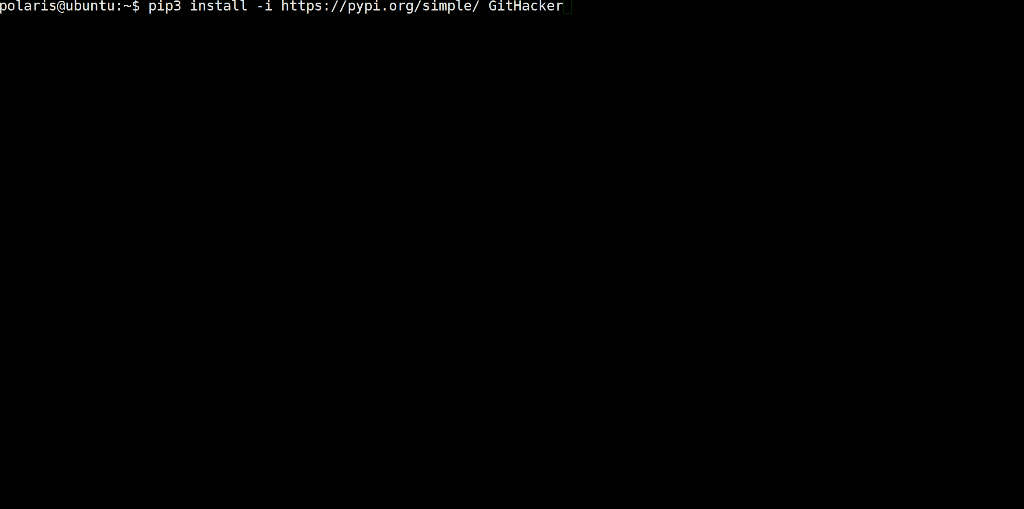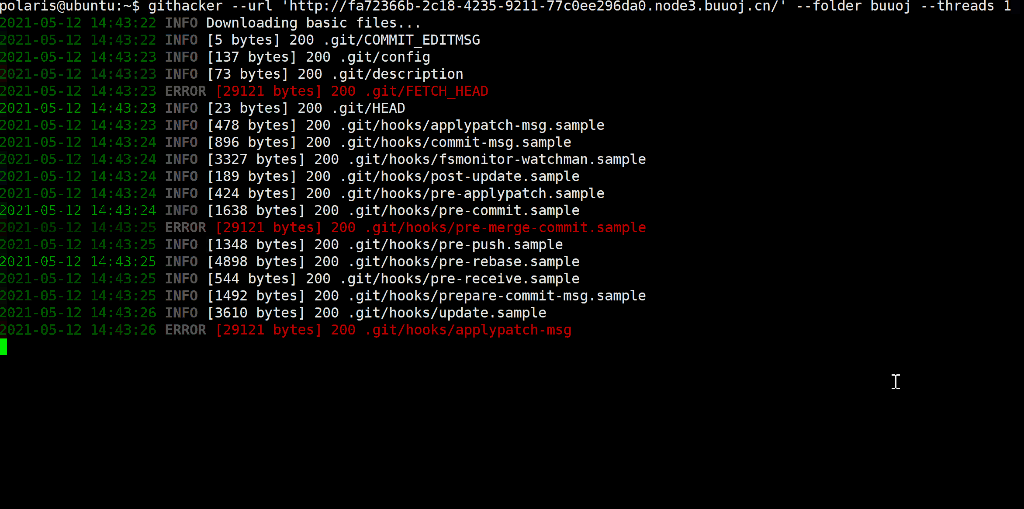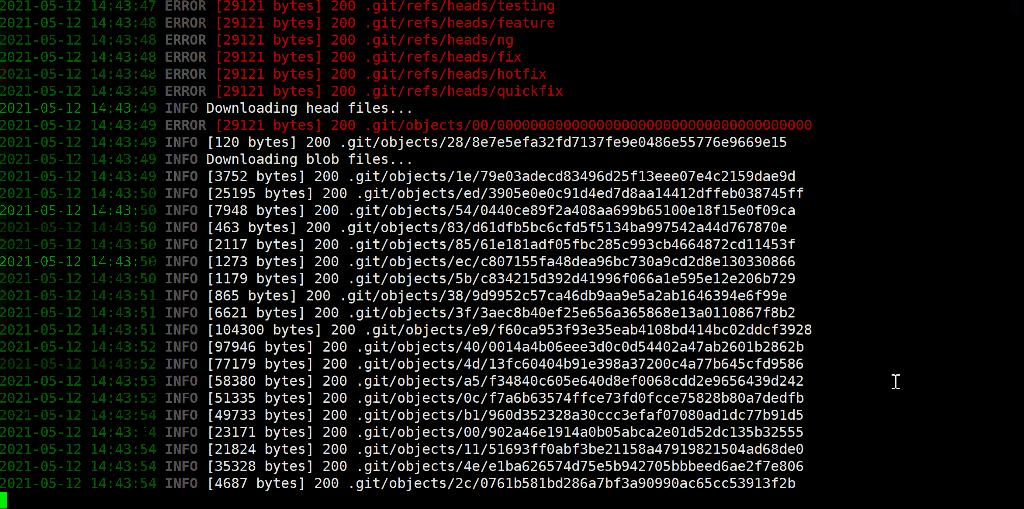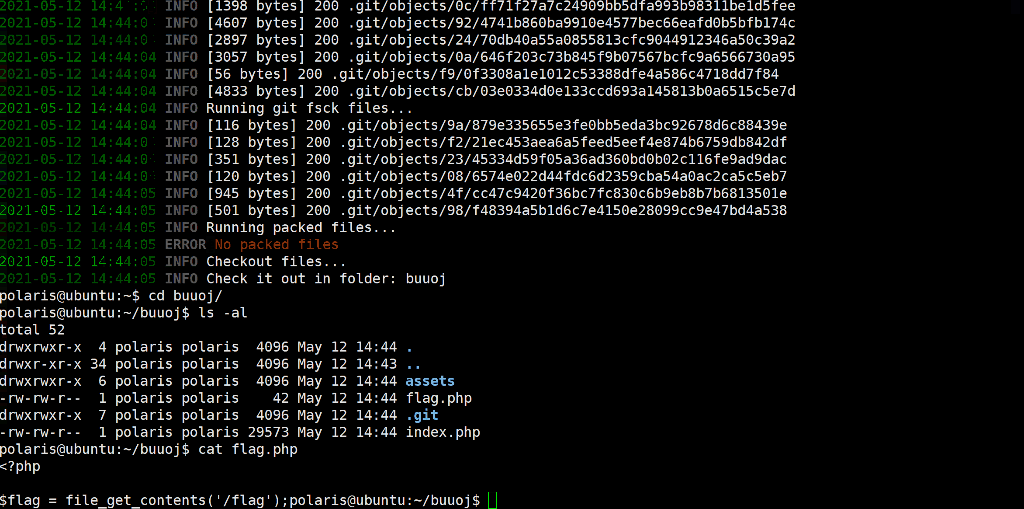 wangyihang/githacker
🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.
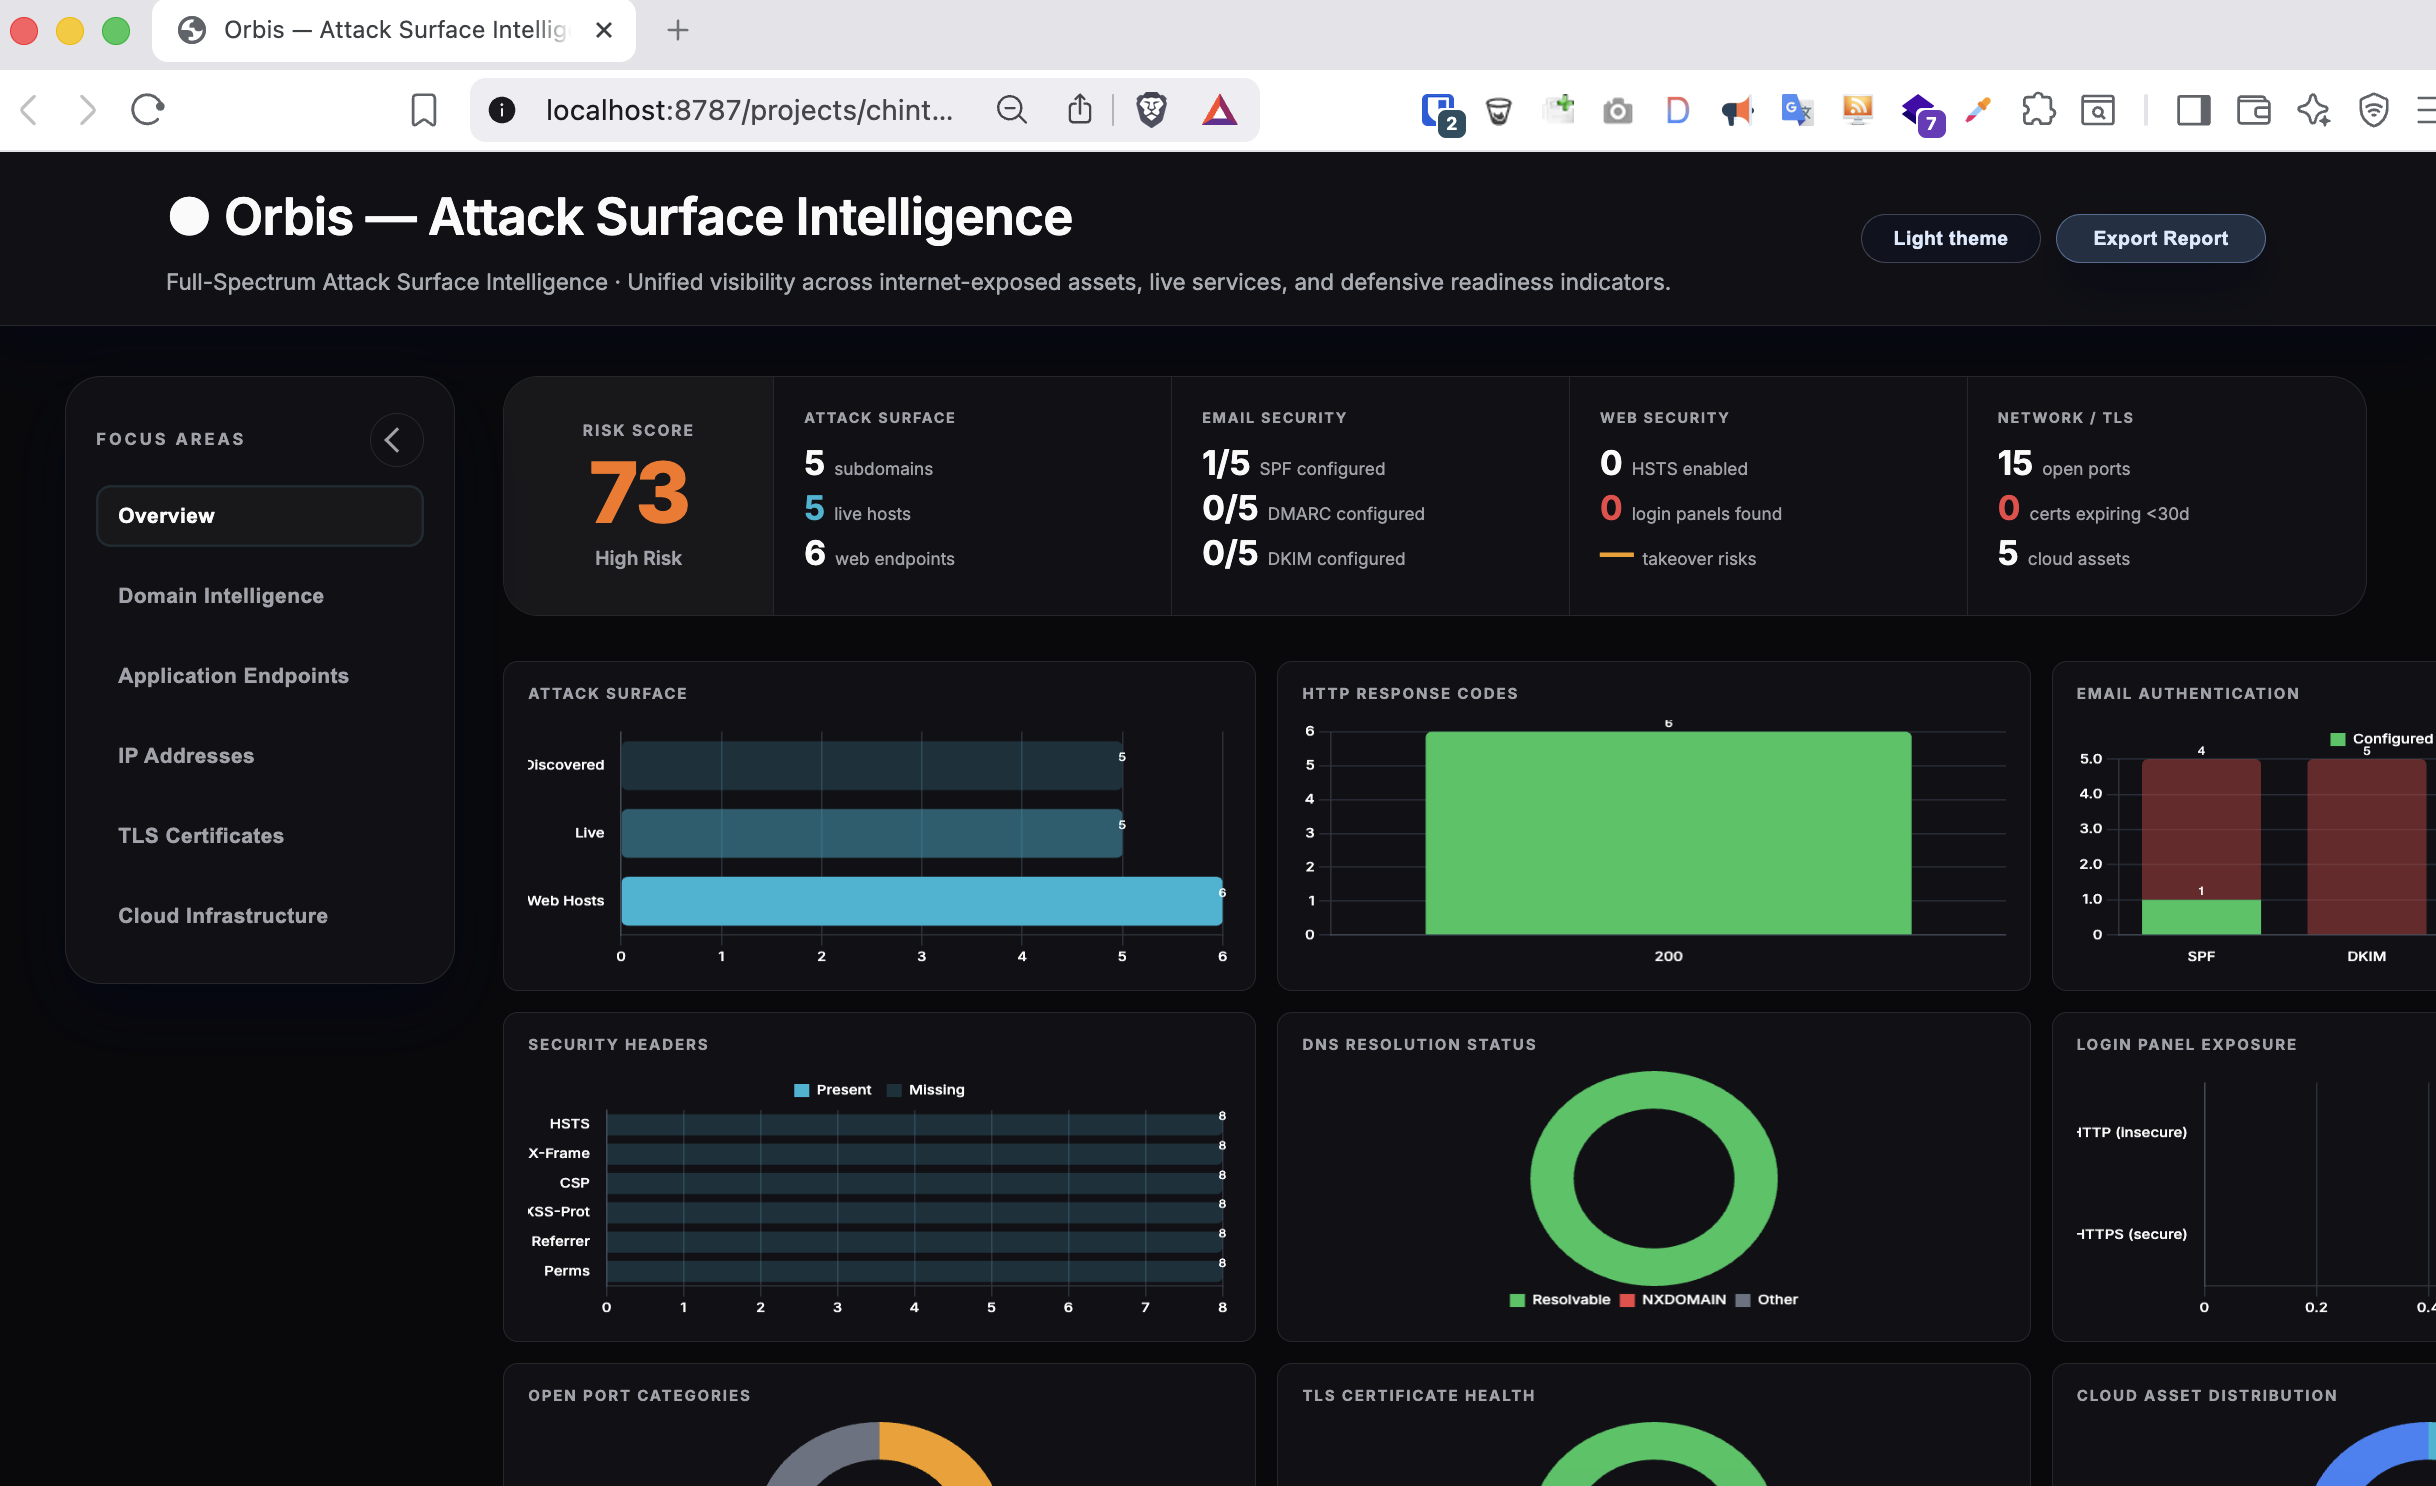 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
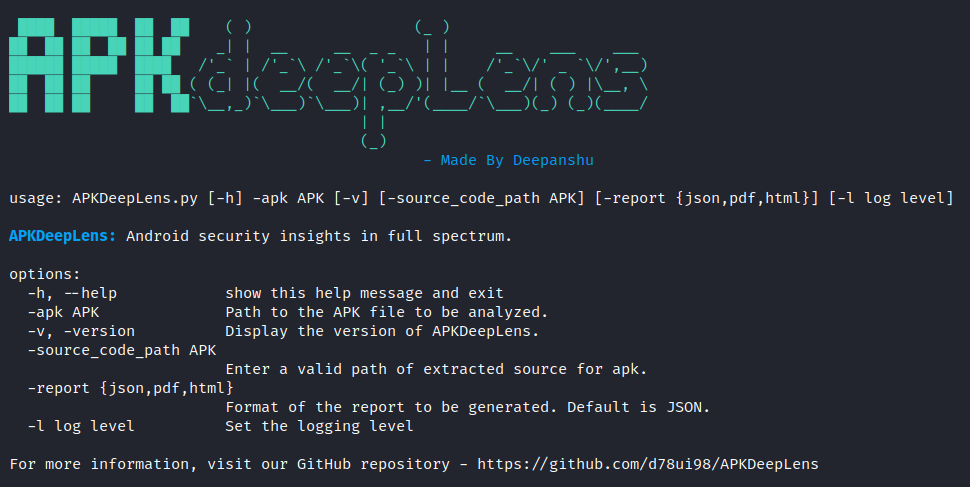 d78ui98/apkdeeplens
Android security insights in full spectrum.
 bitquark/shortscan
Fast IIS short filename enumeration tool that identifies hidden files and directories via tilde vulnerability, with automatic full filename…
 spyboy-productions/omnisci3nt
Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 ruisiang/pow-shield
Project dedicated to fight Layer 7 DDoS with proof of work, with an additional WAF and controller. Completed with full set of features and…
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
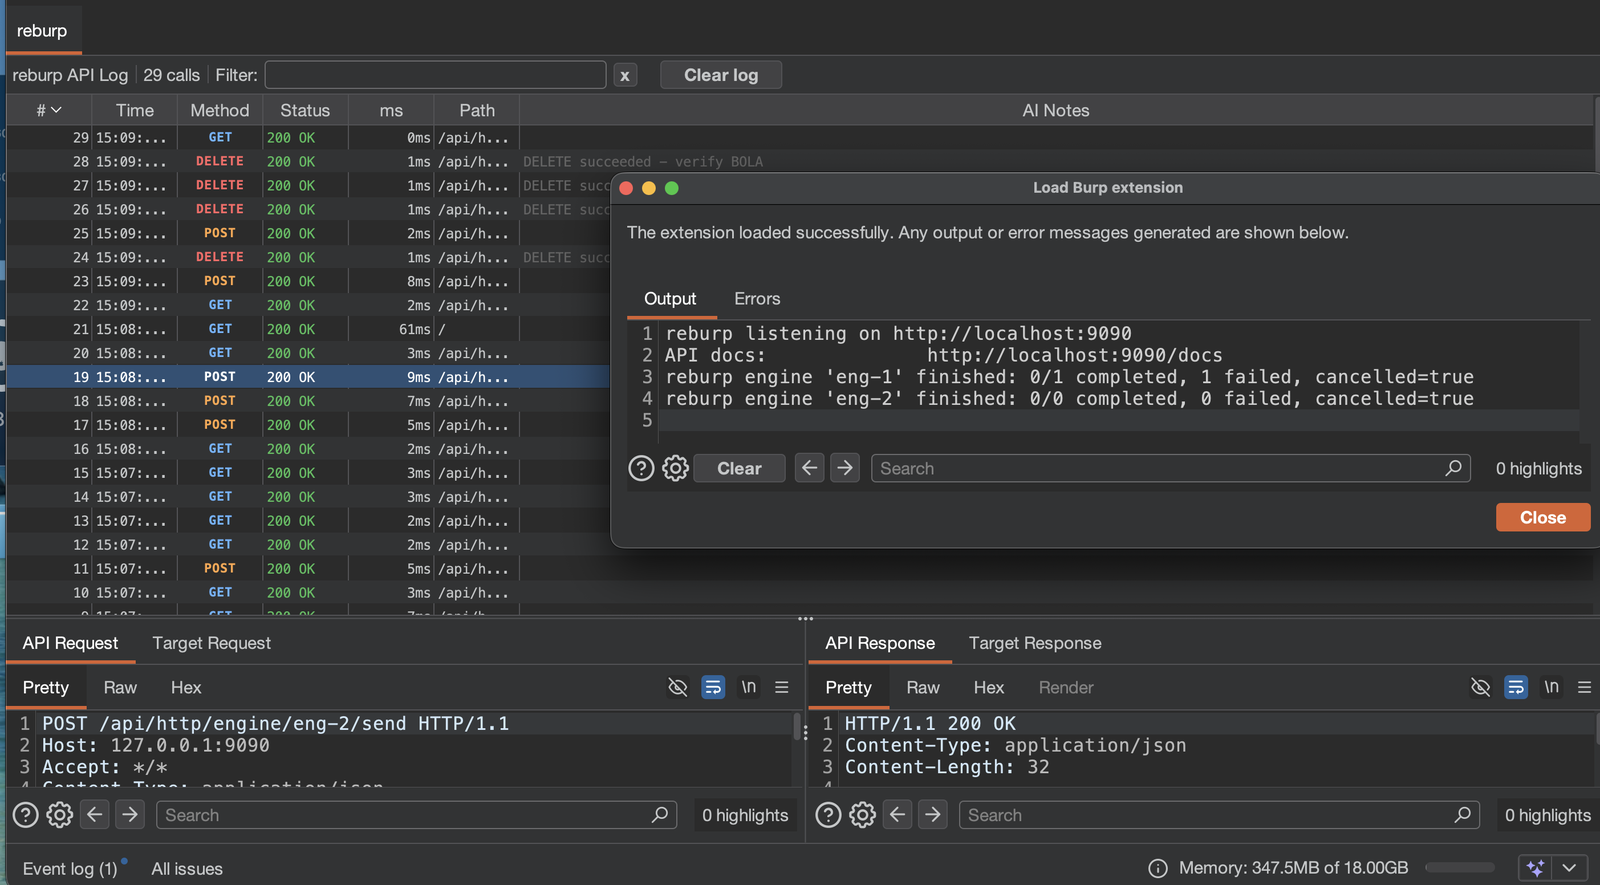 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
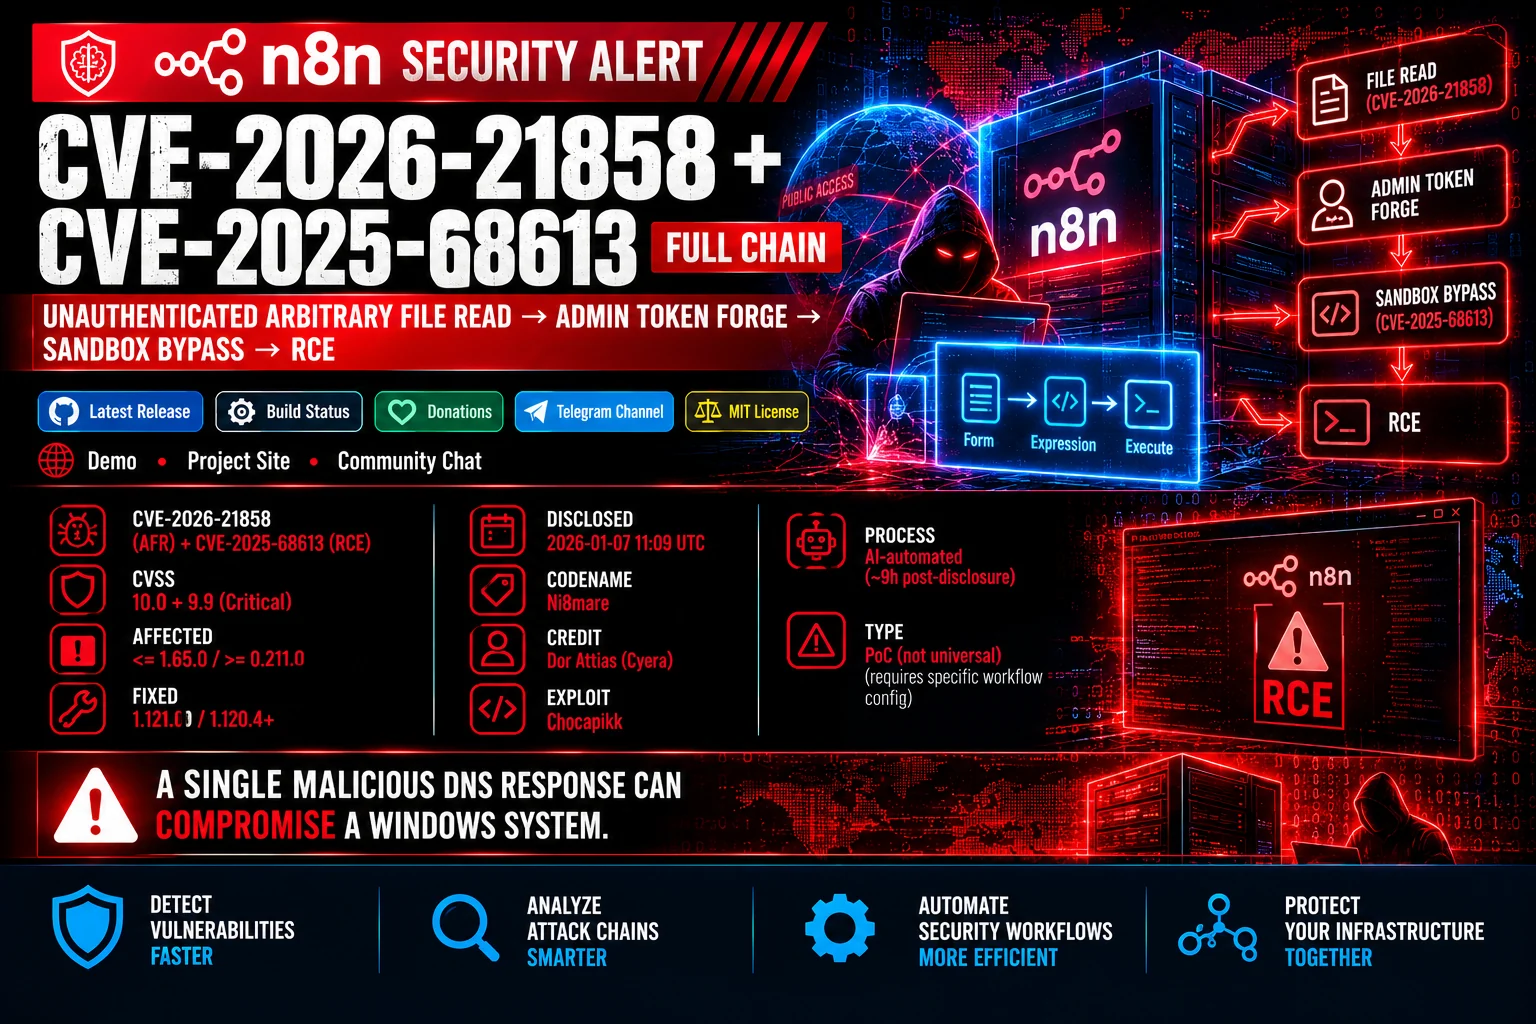 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 carlosevieira/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 perimeterx/cve-2020-6519
Proof-of-concept exploit for CVE-2020-6519, a Content Security Policy bypass vulnerability in Chromium 83, enabling full CSP bypass across platforms.
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…