
METATRON
 sooryathejas/metatron
AI-powered penetration testing assistant using local LLM on linux (Parrot OS)
ai-securityeducationexploitation+5
sooryathejas/metatronAI-powered penetration testing assistant using local LLM on linux (Parrot OS)
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.
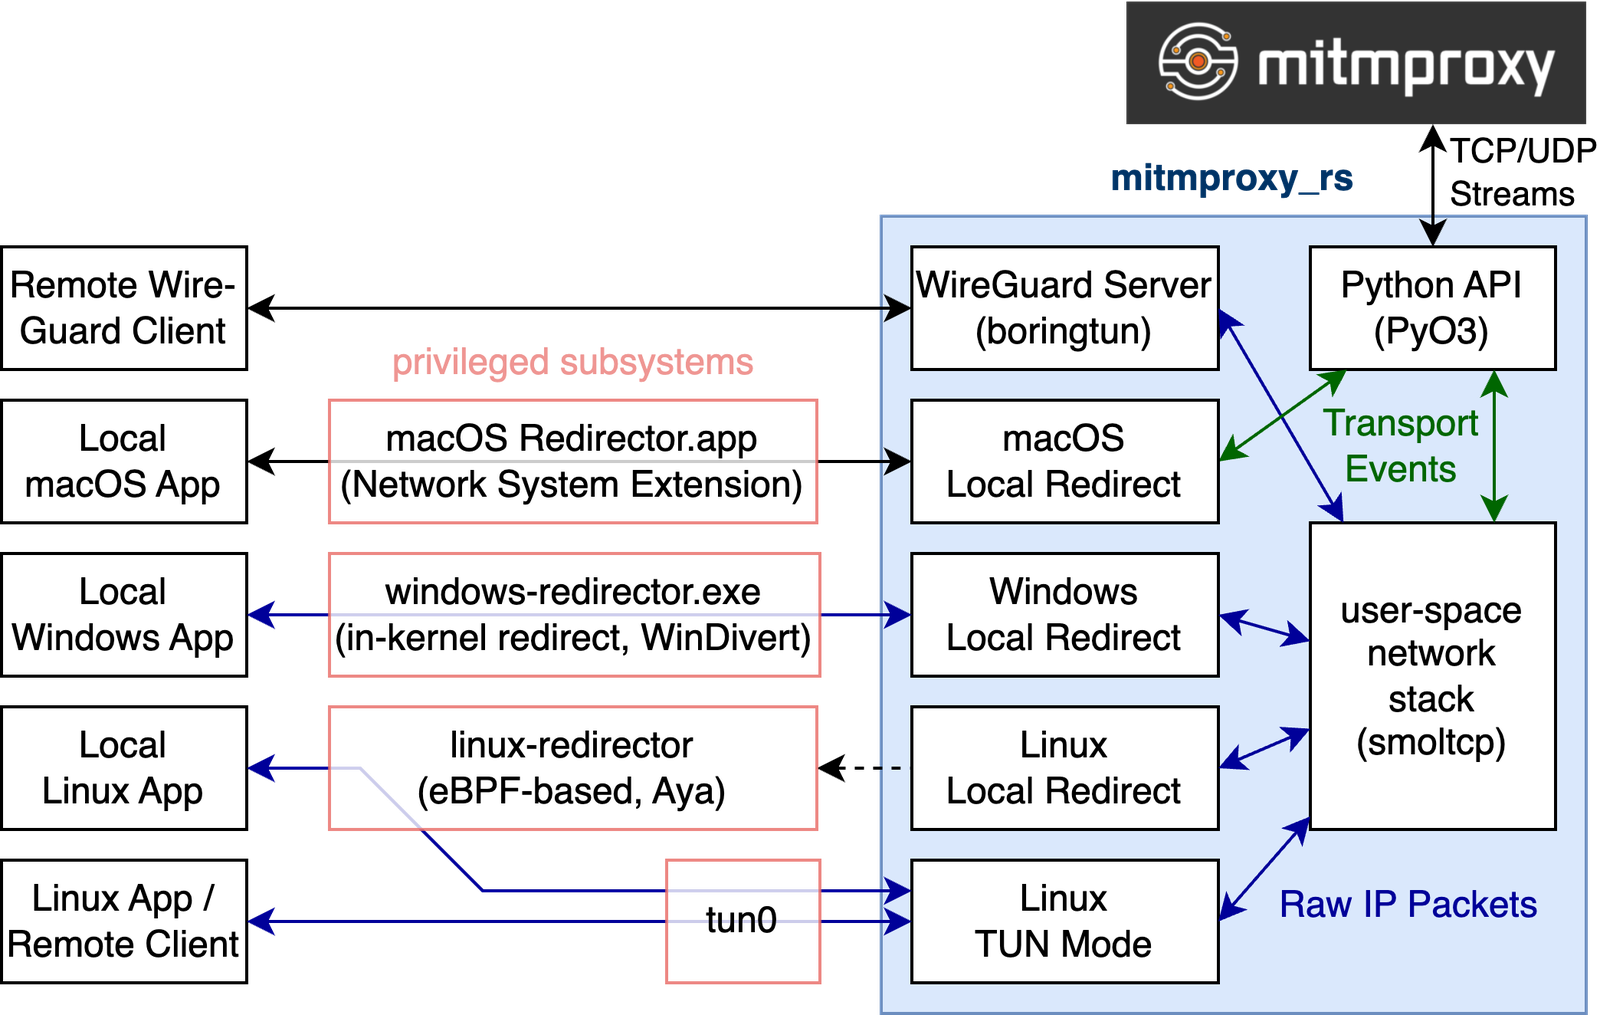 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 defaultnamehere/cookie_crimes
Read local Chrome cookies without root or decrypting
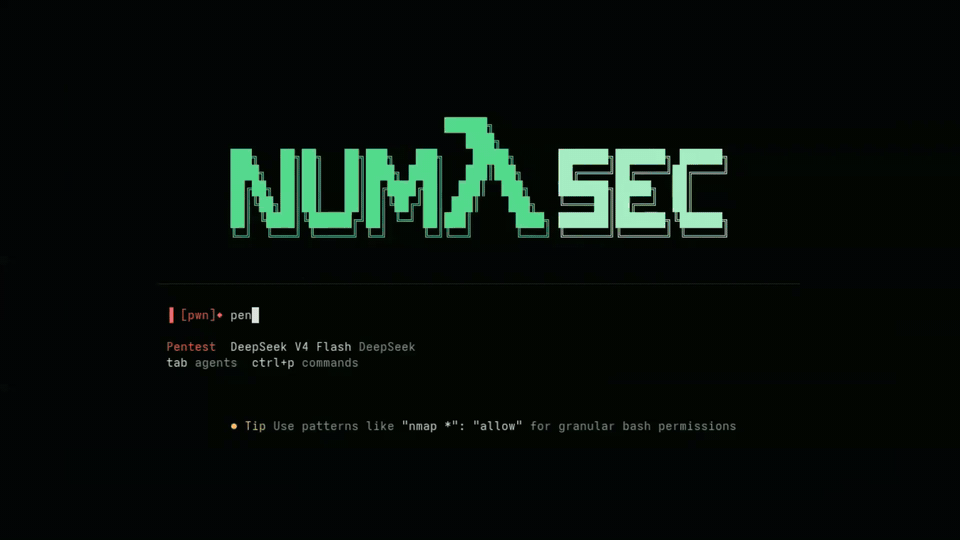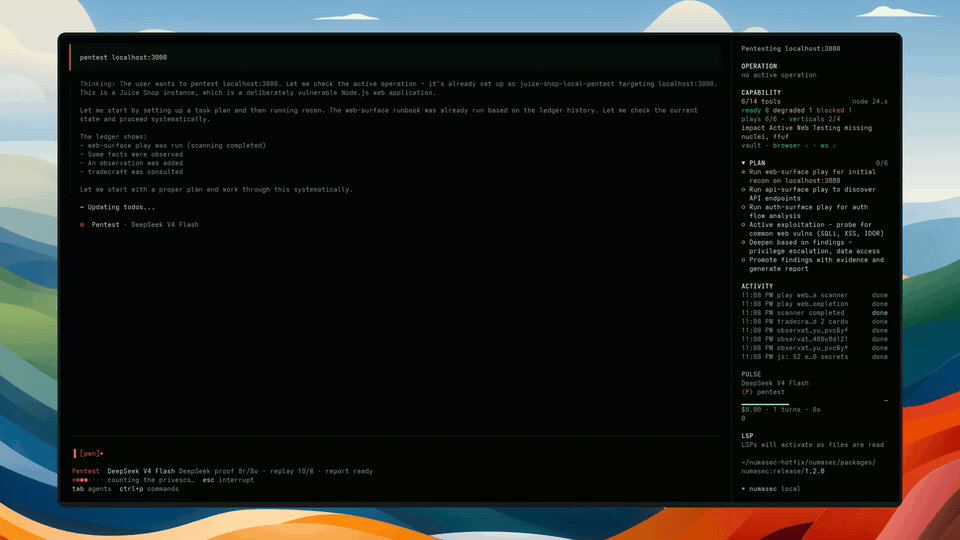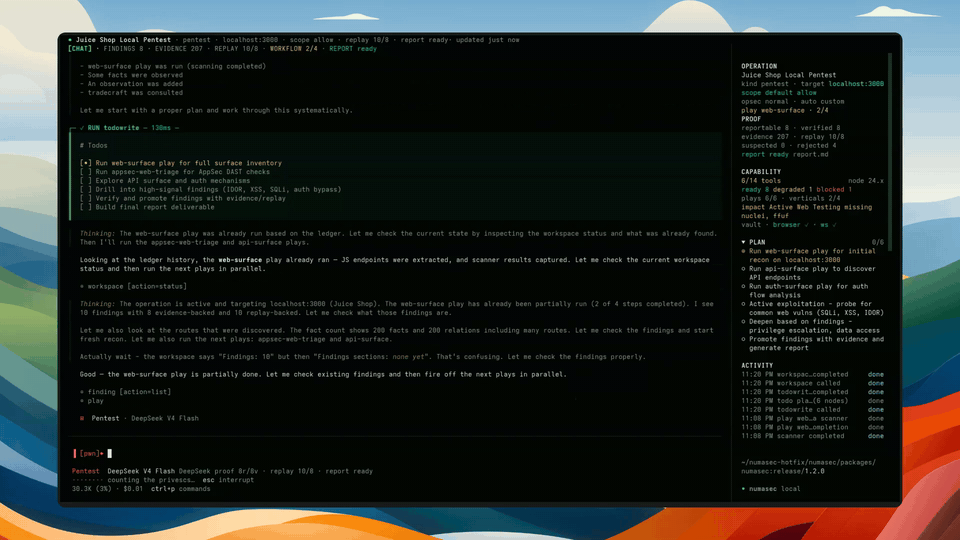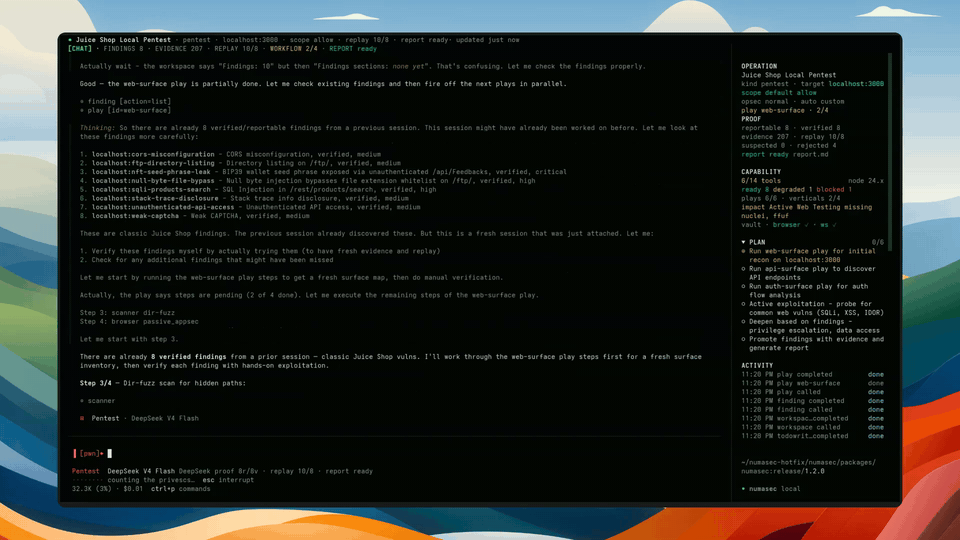 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
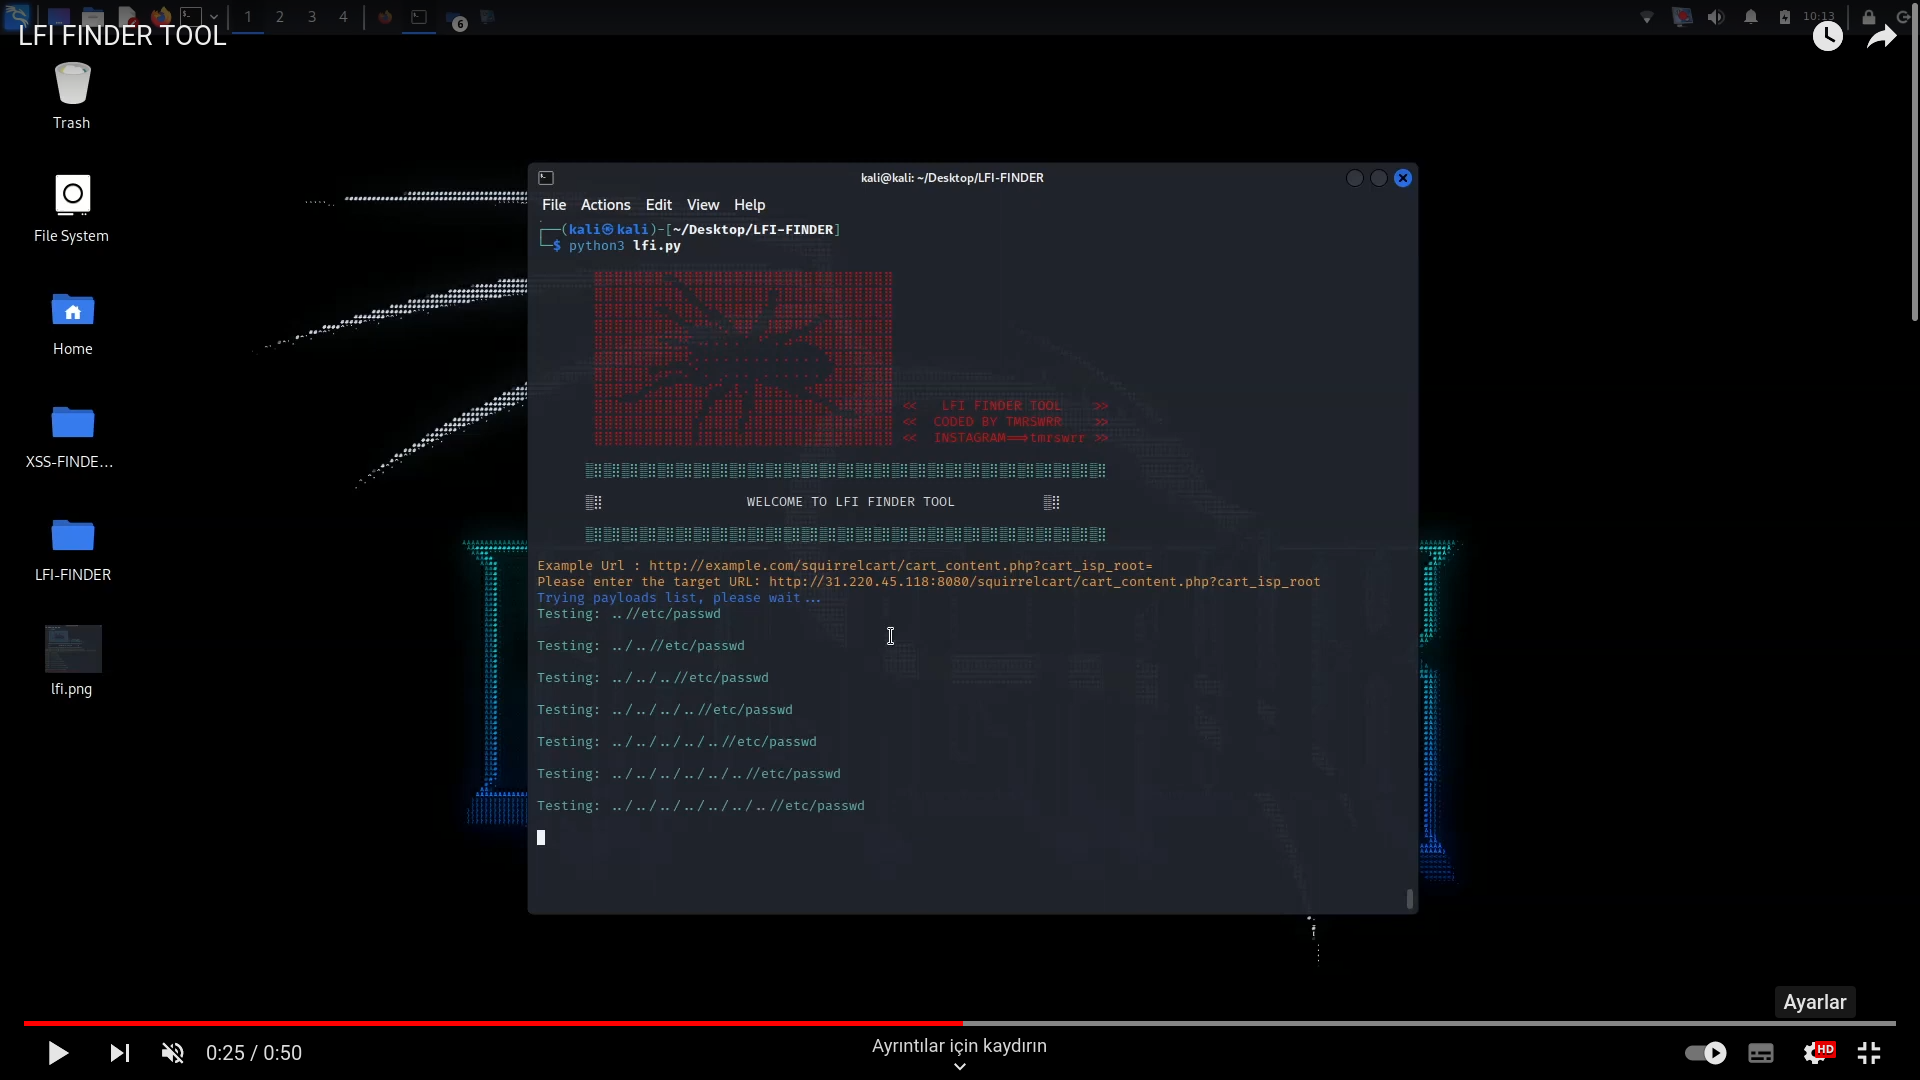 capture0x/lfi-finder
Automated scanner for detecting Local File Inclusion (LFI) vulnerabilities in web applications by analyzing URLs and testing payloads via geckodriver.
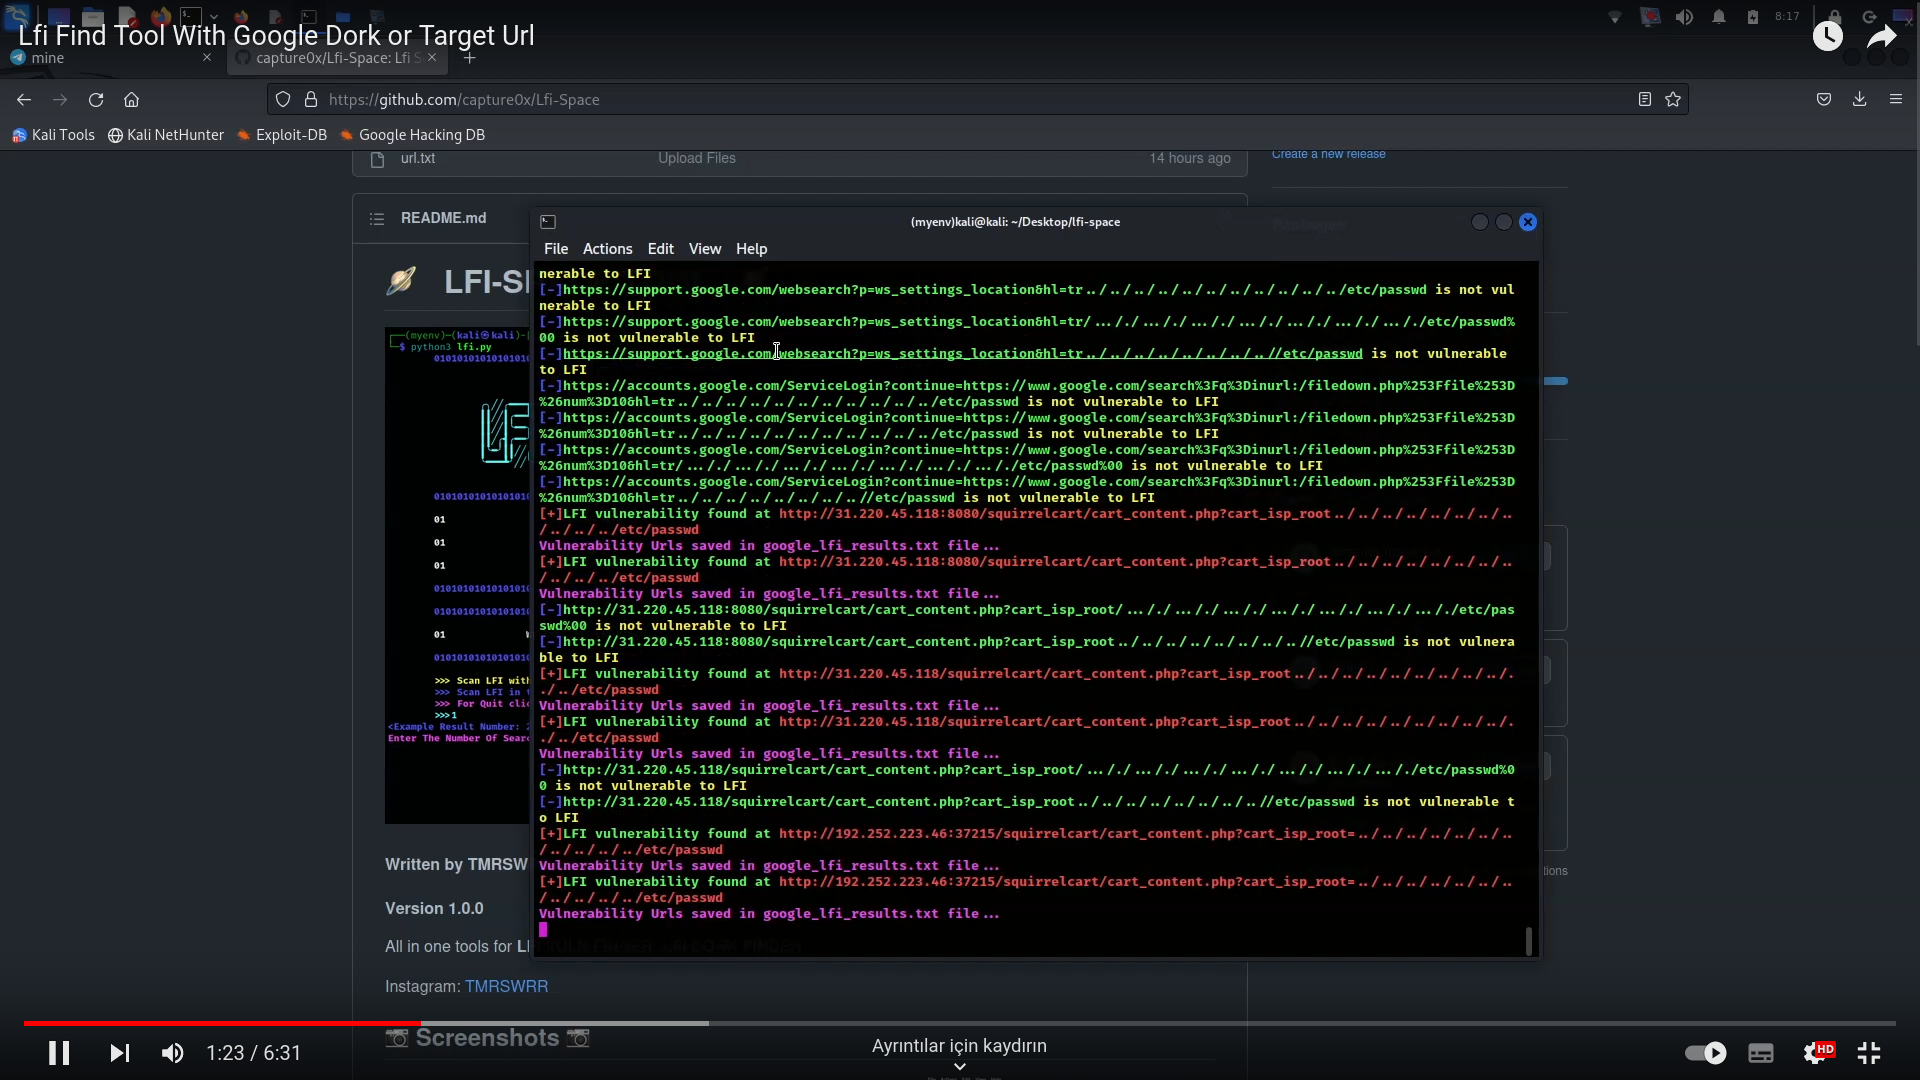 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
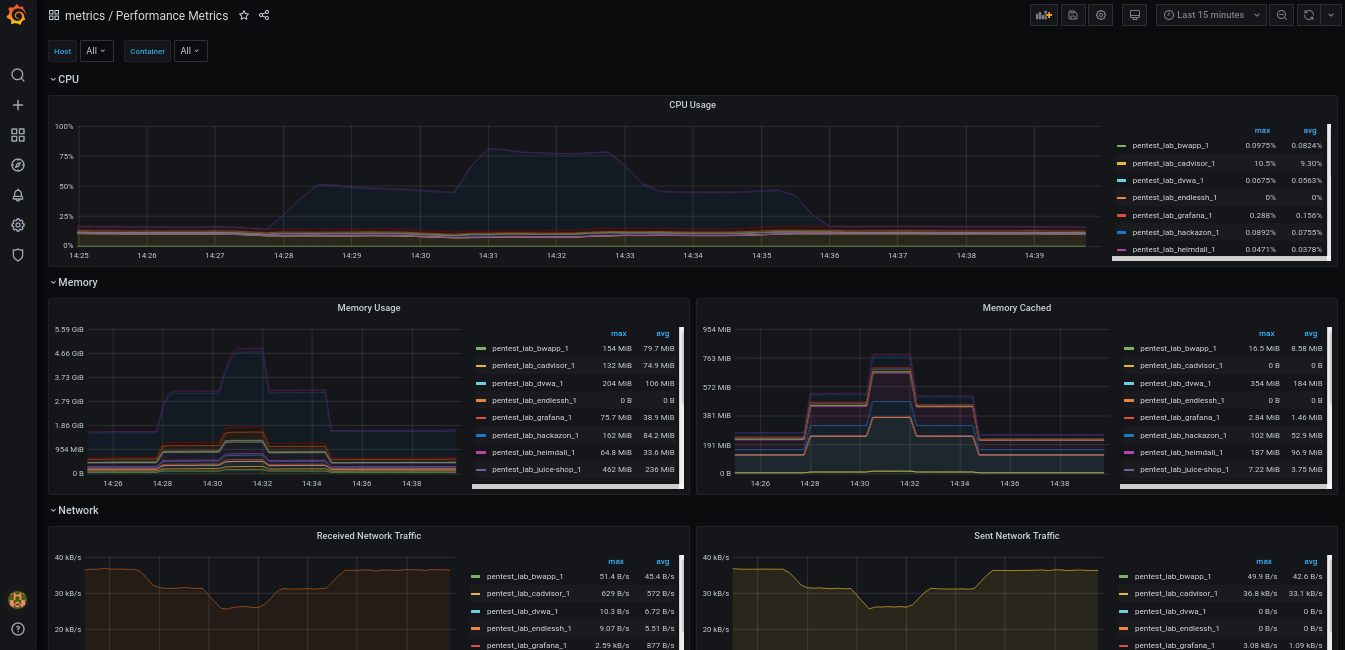 oliverwiegers/pentest_lab
Local penetration testing lab using docker-compose.
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
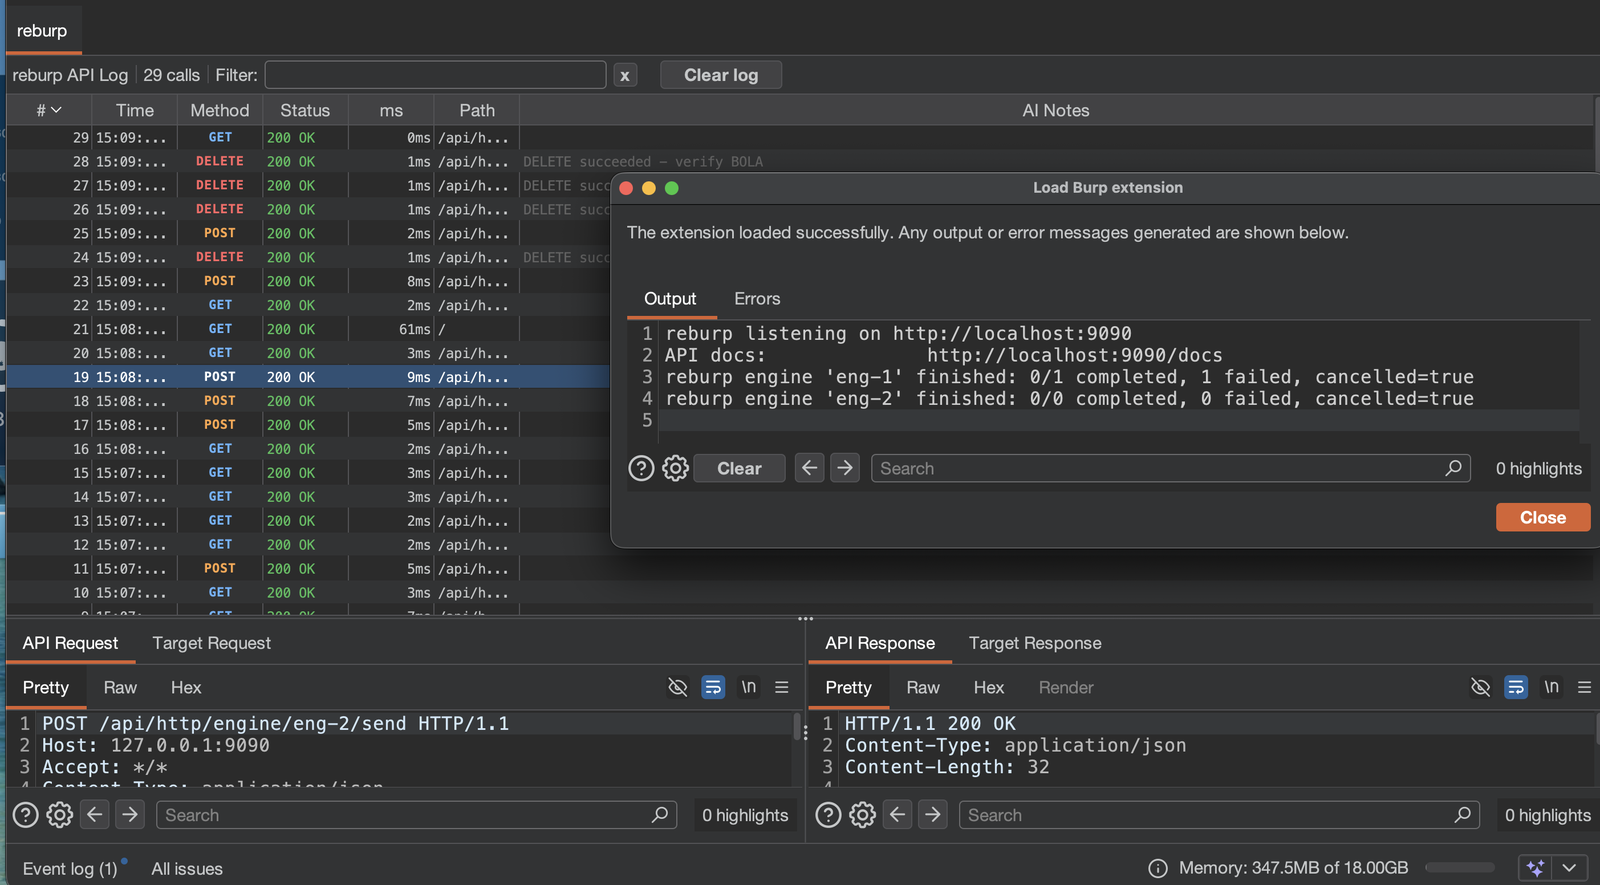 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
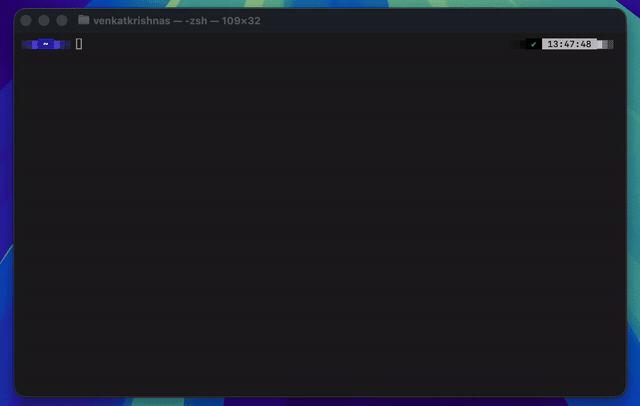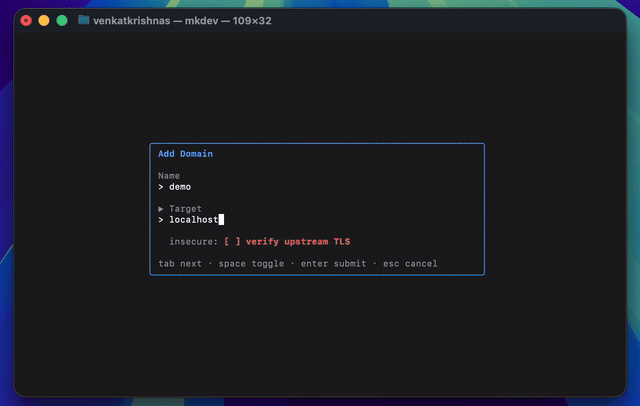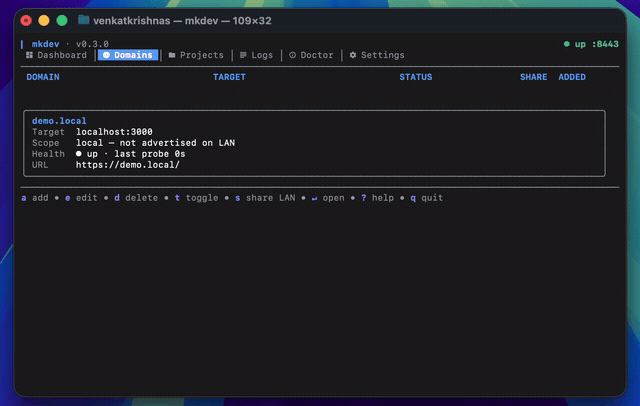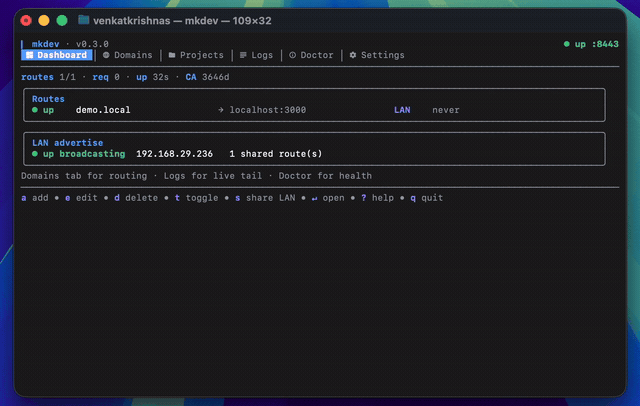 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
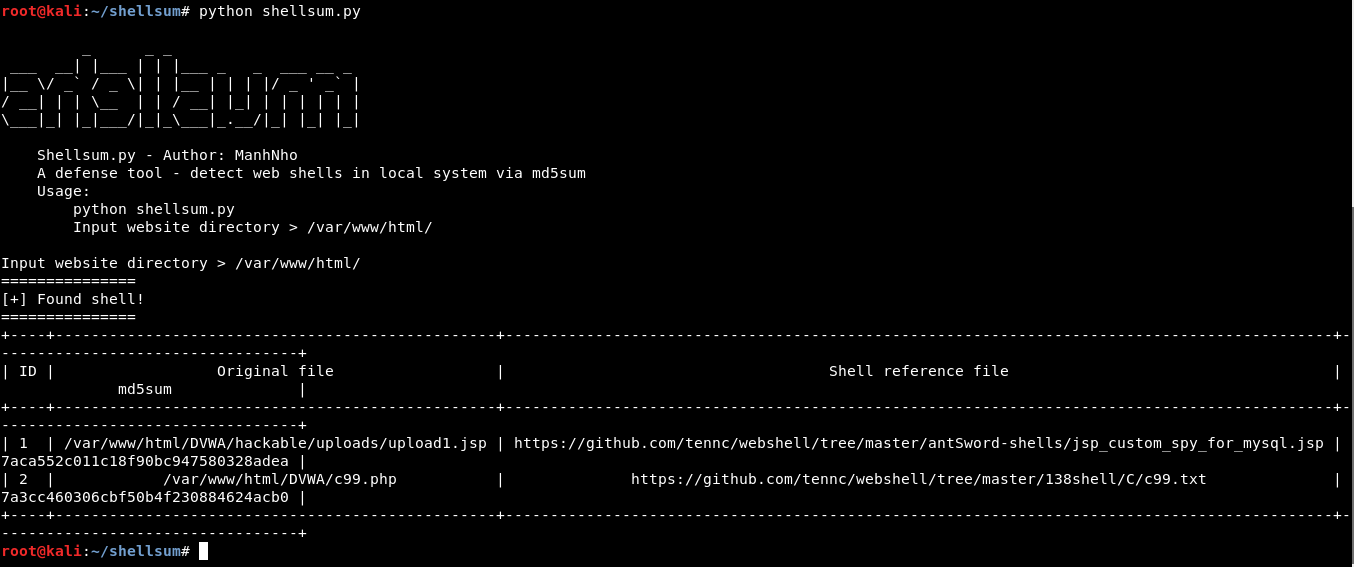 manhnho/shellsum
A defense tool - detect web shells in local directories via md5sum
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…