
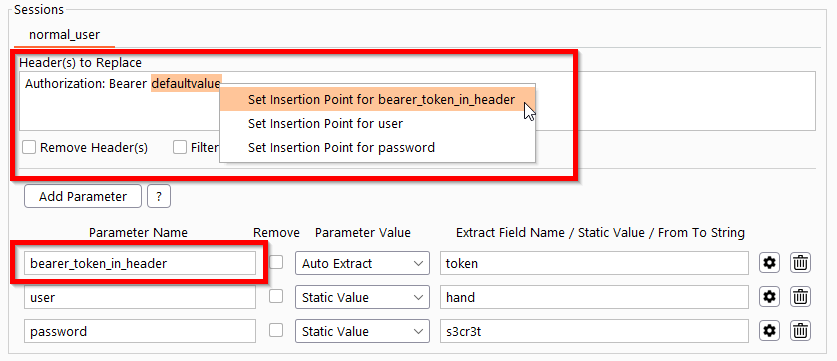
auth_analyzer
 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
api-security-testingauthentication-authorizationpenetration-testing+1
221
simioni87/auth_analyzerBurp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 wish-i-was/femida
Automated blind-xss search for Burp Suite
 gonzosint/whatcms
Shell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
 ostesayed/oste-meta-scan
Multi-engine DAST scanner aggregating Nikto, ZAP, Nuclei, SkipFish, and Wapiti for automated web injection vulnerability detection with consolidated…
 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…
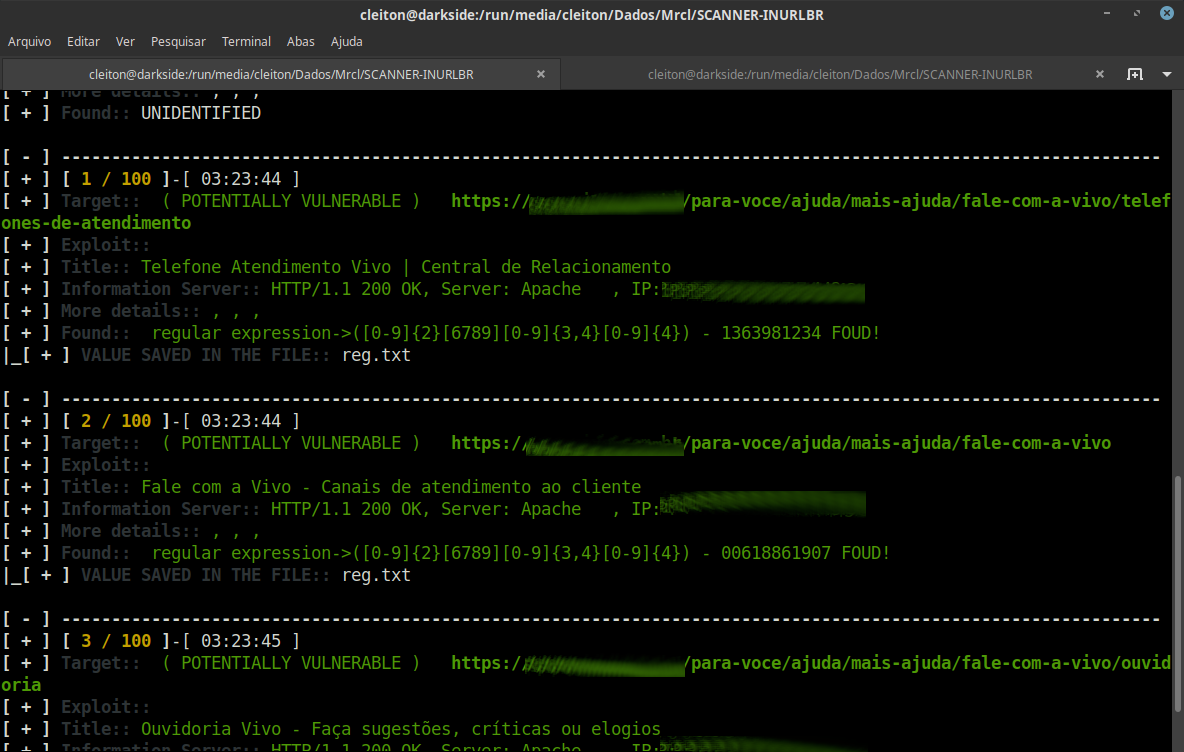 mrcl0wnlab/scanner-inurlbr
Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…
 hhhrrrttt222111/dorkify
Automated Google Dorking tool for OSINT reconnaissance, vulnerability discovery, and information gathering via advanced search operators and targeted…
 mad-robot/spartan
Automated reconnaissance framework integrating subdomain enumeration, live host probing, port scanning, CMS detection, and directory brute-forcing…
 percx/praeda
Automated data harvesting tool for extracting sensitive information (backups, clones, address books) from web servers via targeted scanning and…
 m4cs/traxss
traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019
 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…
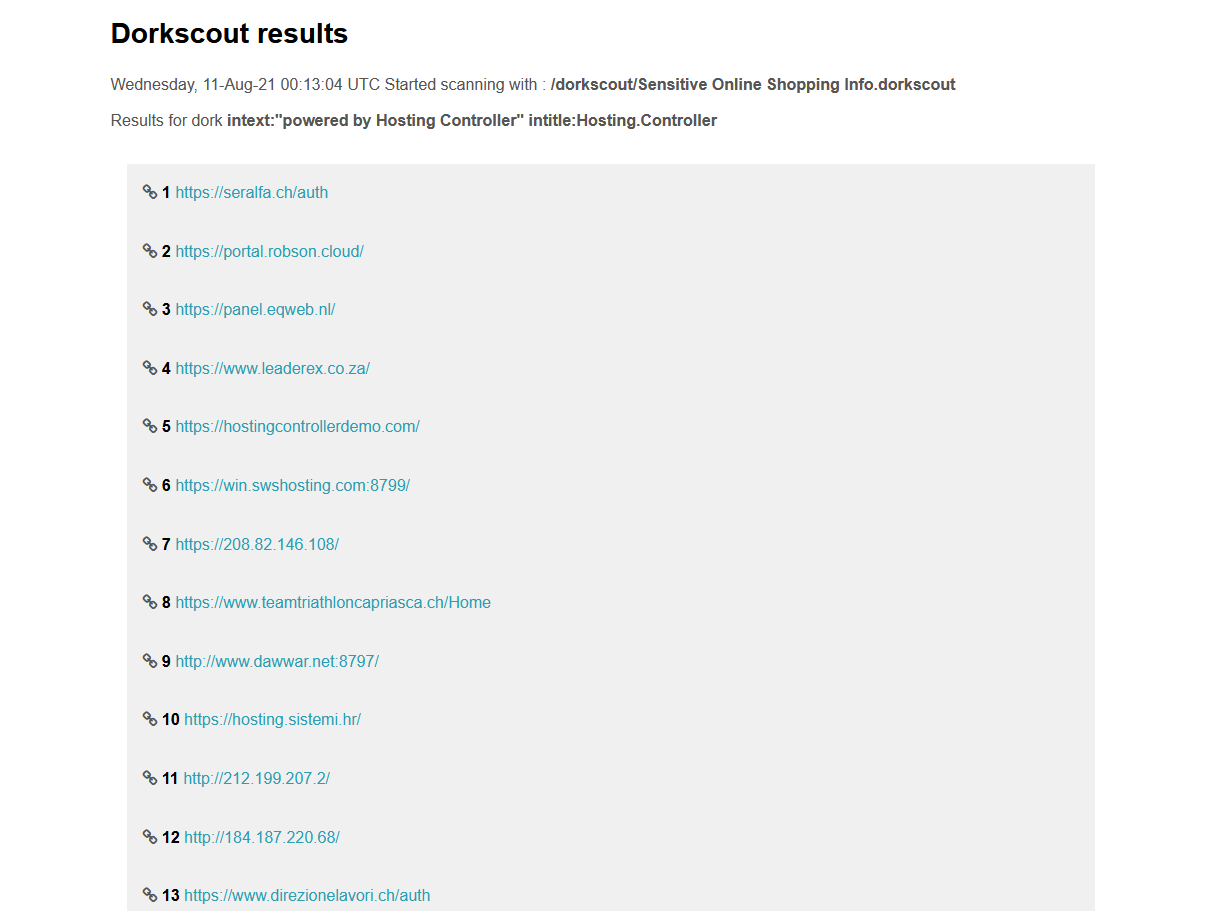 r4ygm/dorkscout
Automated Google dork scanner that fetches exploit-db dork lists and scans targets or the entire internet for vulnerable applications, secret files,…
 trufflesecurity/of-cors
Automated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…
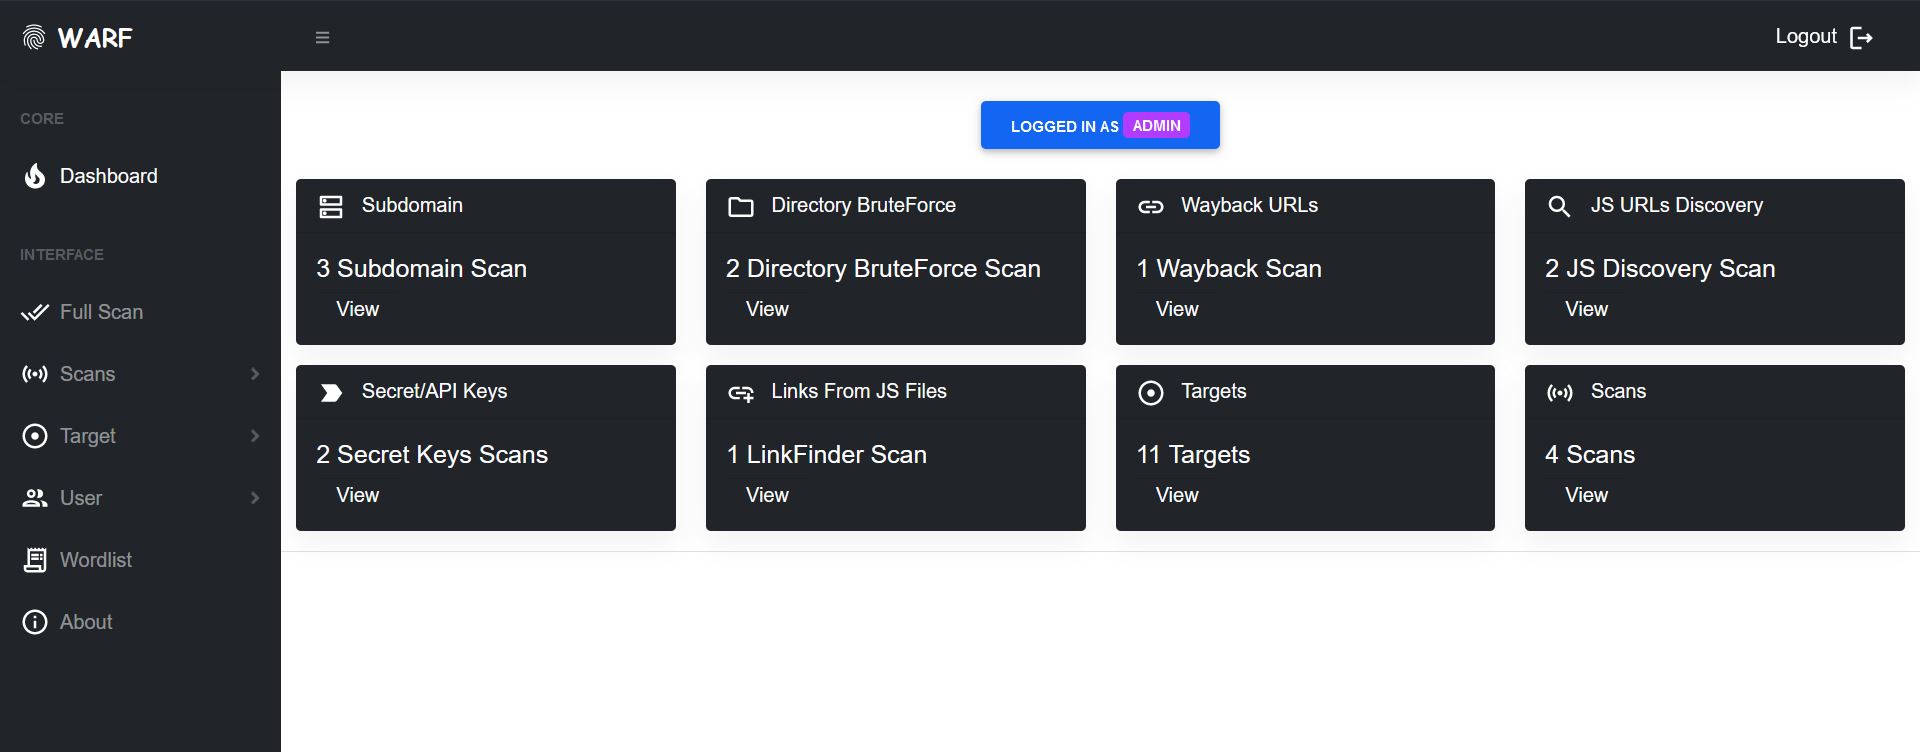 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript