http-request-smuggler

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…

Automated script for performing Padding Oracle attacks

Automated HTTP Request Repeating With Burp Suite

Automated OSINT reconnaissance tool that queries Google and social platforms to gather intelligence on usernames and queries, with proxy rotation and…

Advanced cross-platform web crawler for security professionals, enabling automated reconnaissance, information gathering, and OSINT data collection…

Orbis is an full spectrum automated external attack surface intelligent toolkit.

CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…

Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…

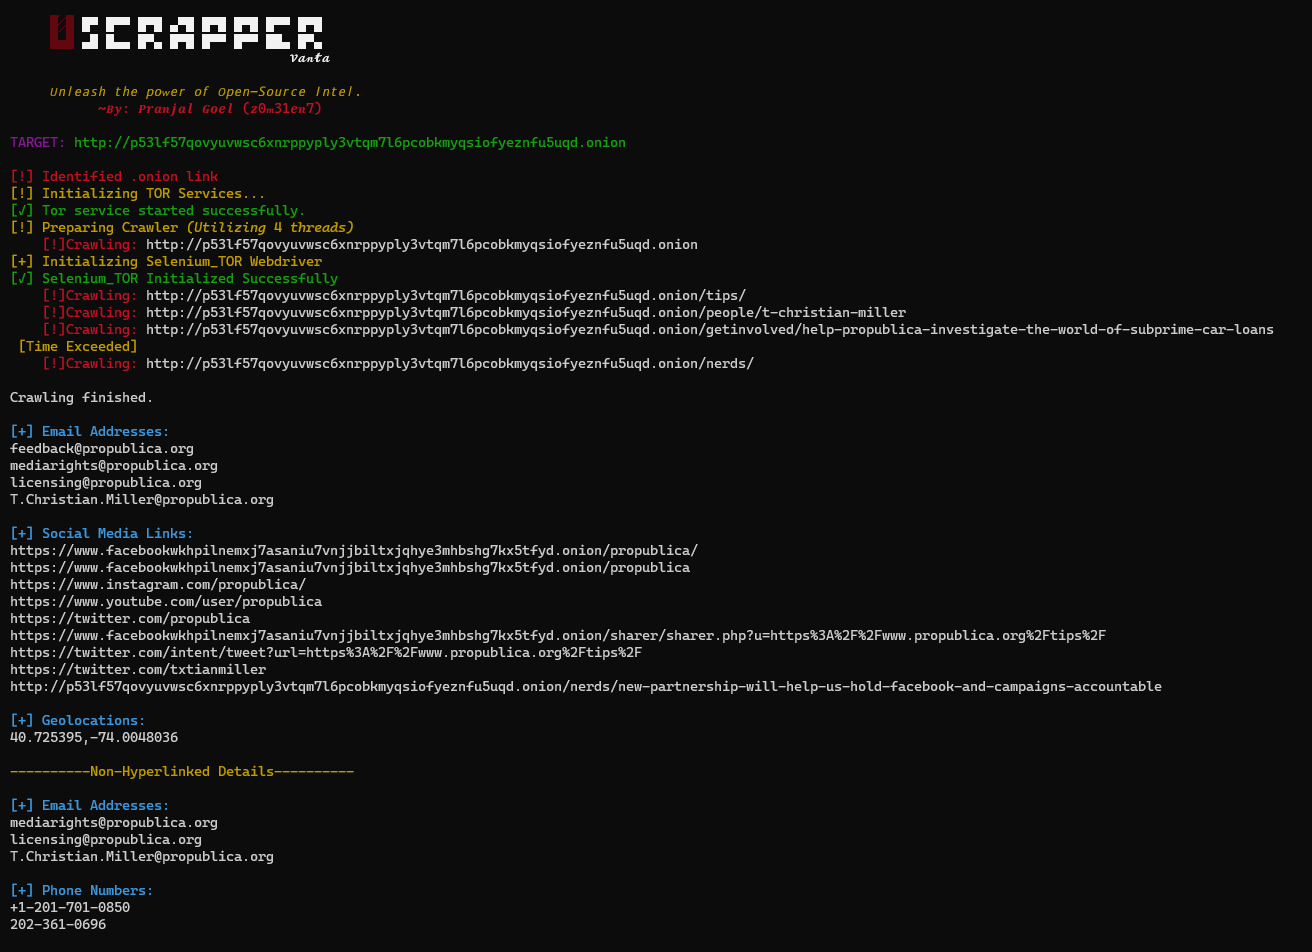
Uscrapper Vanta: Dive deeper into the web with this powerful open-source tool. Extract valuable insights with ease and efficiency, from both surface…


Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…

Passive URL discovery tool that collects domain-associated URLs from multiple public sources via command-line, supporting stdin/stdout and JSONL…

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…

BFAC (Backup File Artifacts Checker): An automated tool that checks for backup artifacts that may disclose the web-application's source code.

Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…