
Archived
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 edoverflow/bugbounty-cheatsheet
A list of interesting payloads, tips and tricks for bug bounty hunters.
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 hightechsec/git-scanner
A tool for bug hunting or pentesting for targeting websites that have open .git repositories available in public
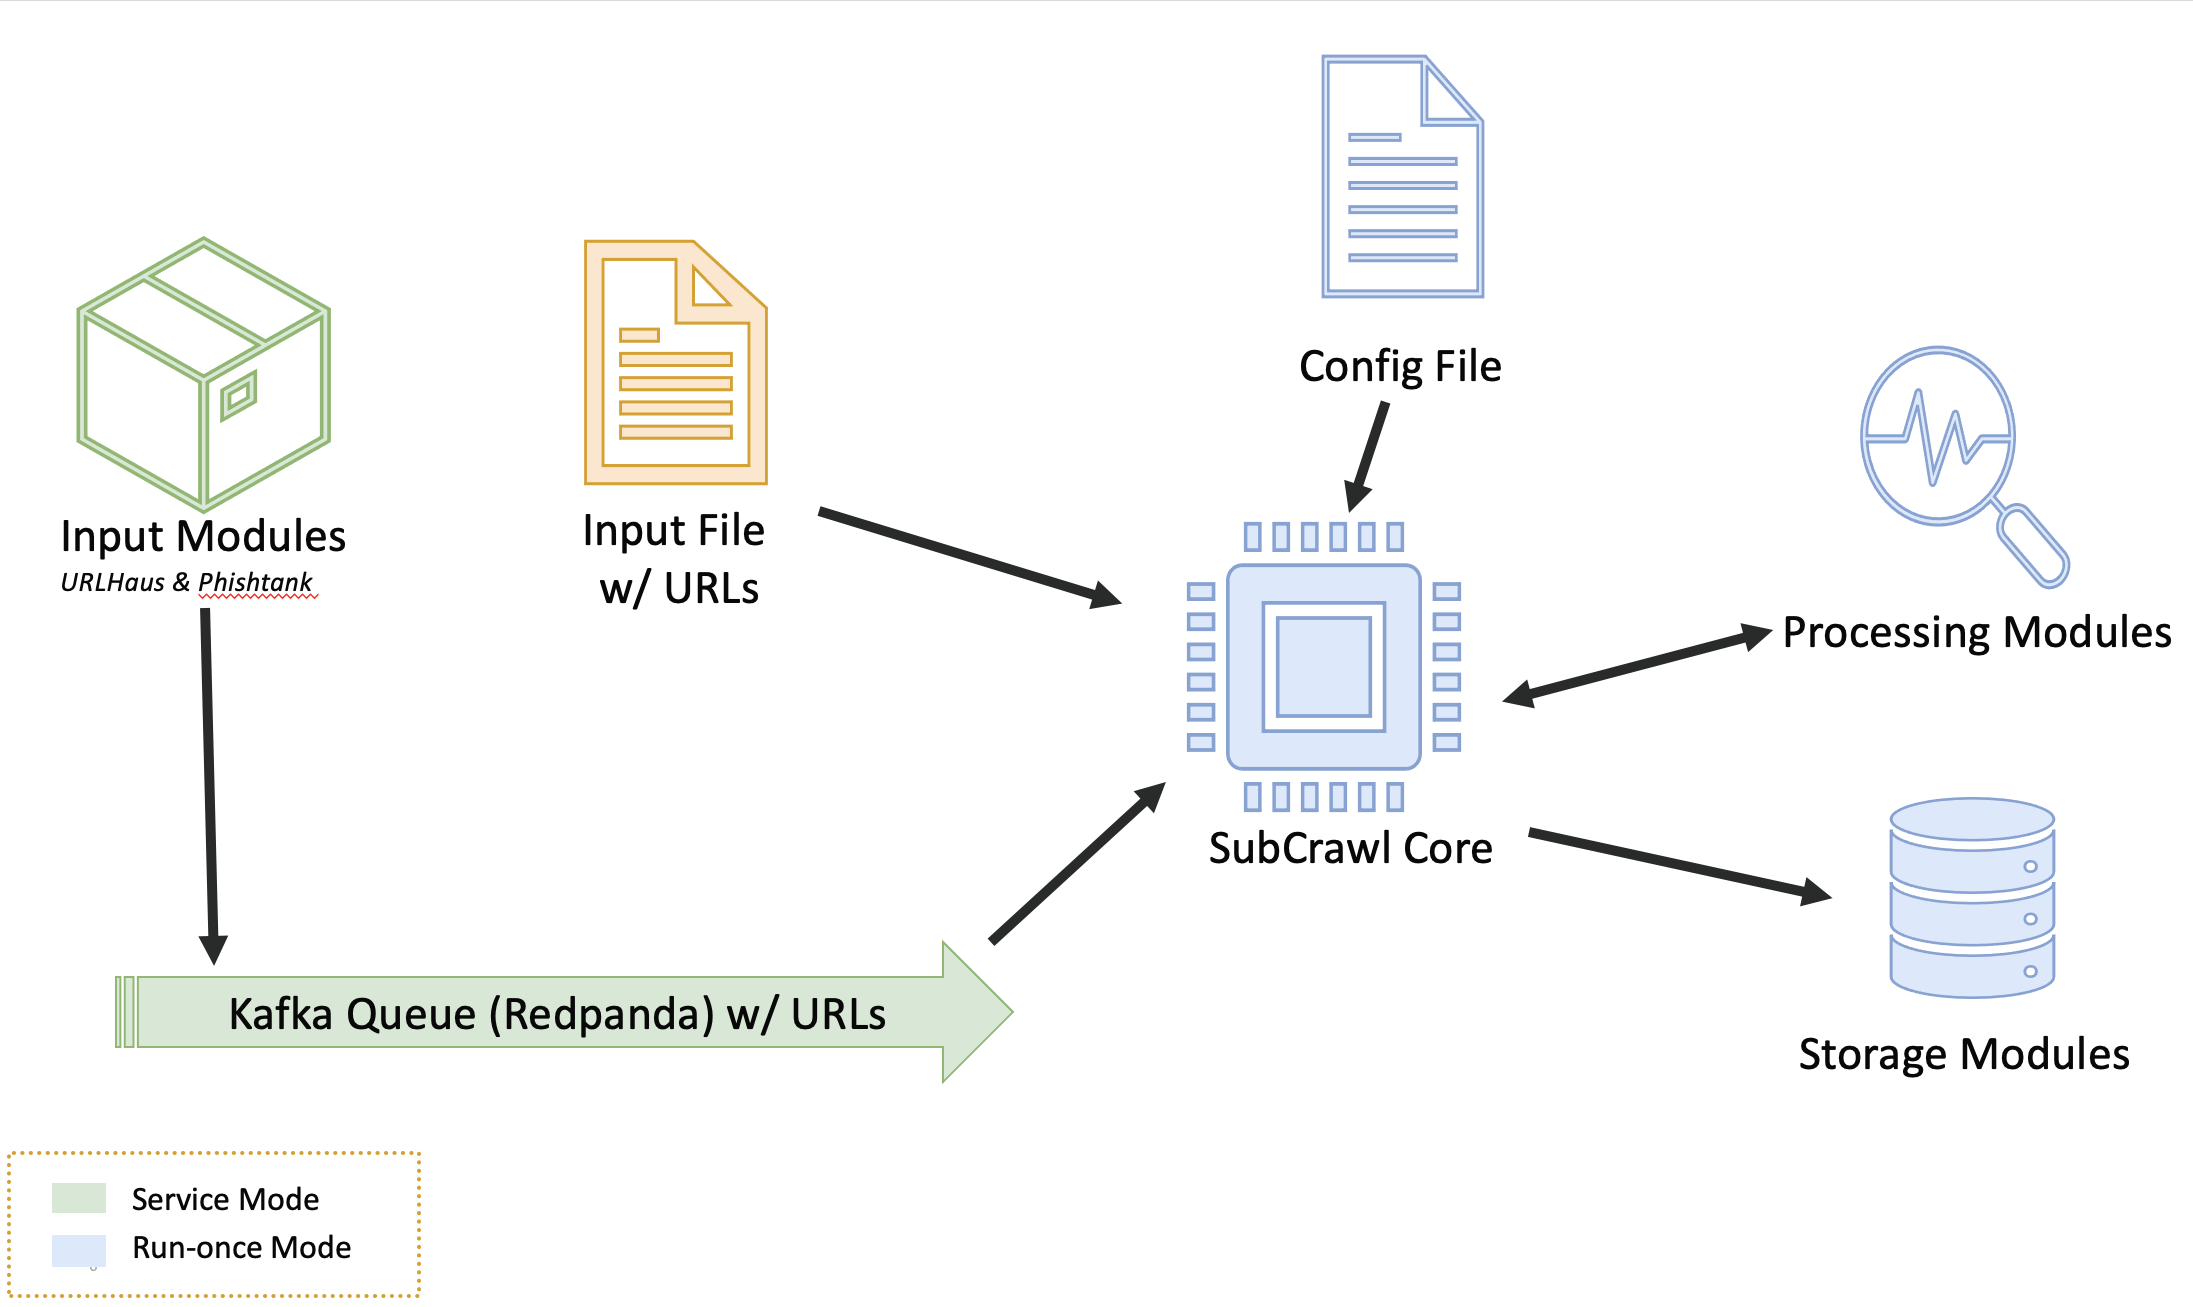 hpthreatresearch/subcrawl
Modular framework for discovering and analyzing open directories on the web. Crawls URLs, extracts content, applies YARA/ClamAV scanning, and outputs…
 belmind/heartbleed
A collection of scripts and instructions to test CVE-2014-0160 (heartbleed). ❤️ 🩸
 sc1341/instagramosint
An Instagram Open Source Intelligence Tool - Archive
 danmcinerney/device-pharmer
Opens 1K+ IPs or Shodan search results and attempts to login
 c0oki3s/veilgate
Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 s-rah/onionscan
OnionScan is a free and open source tool for investigating the Dark Web.
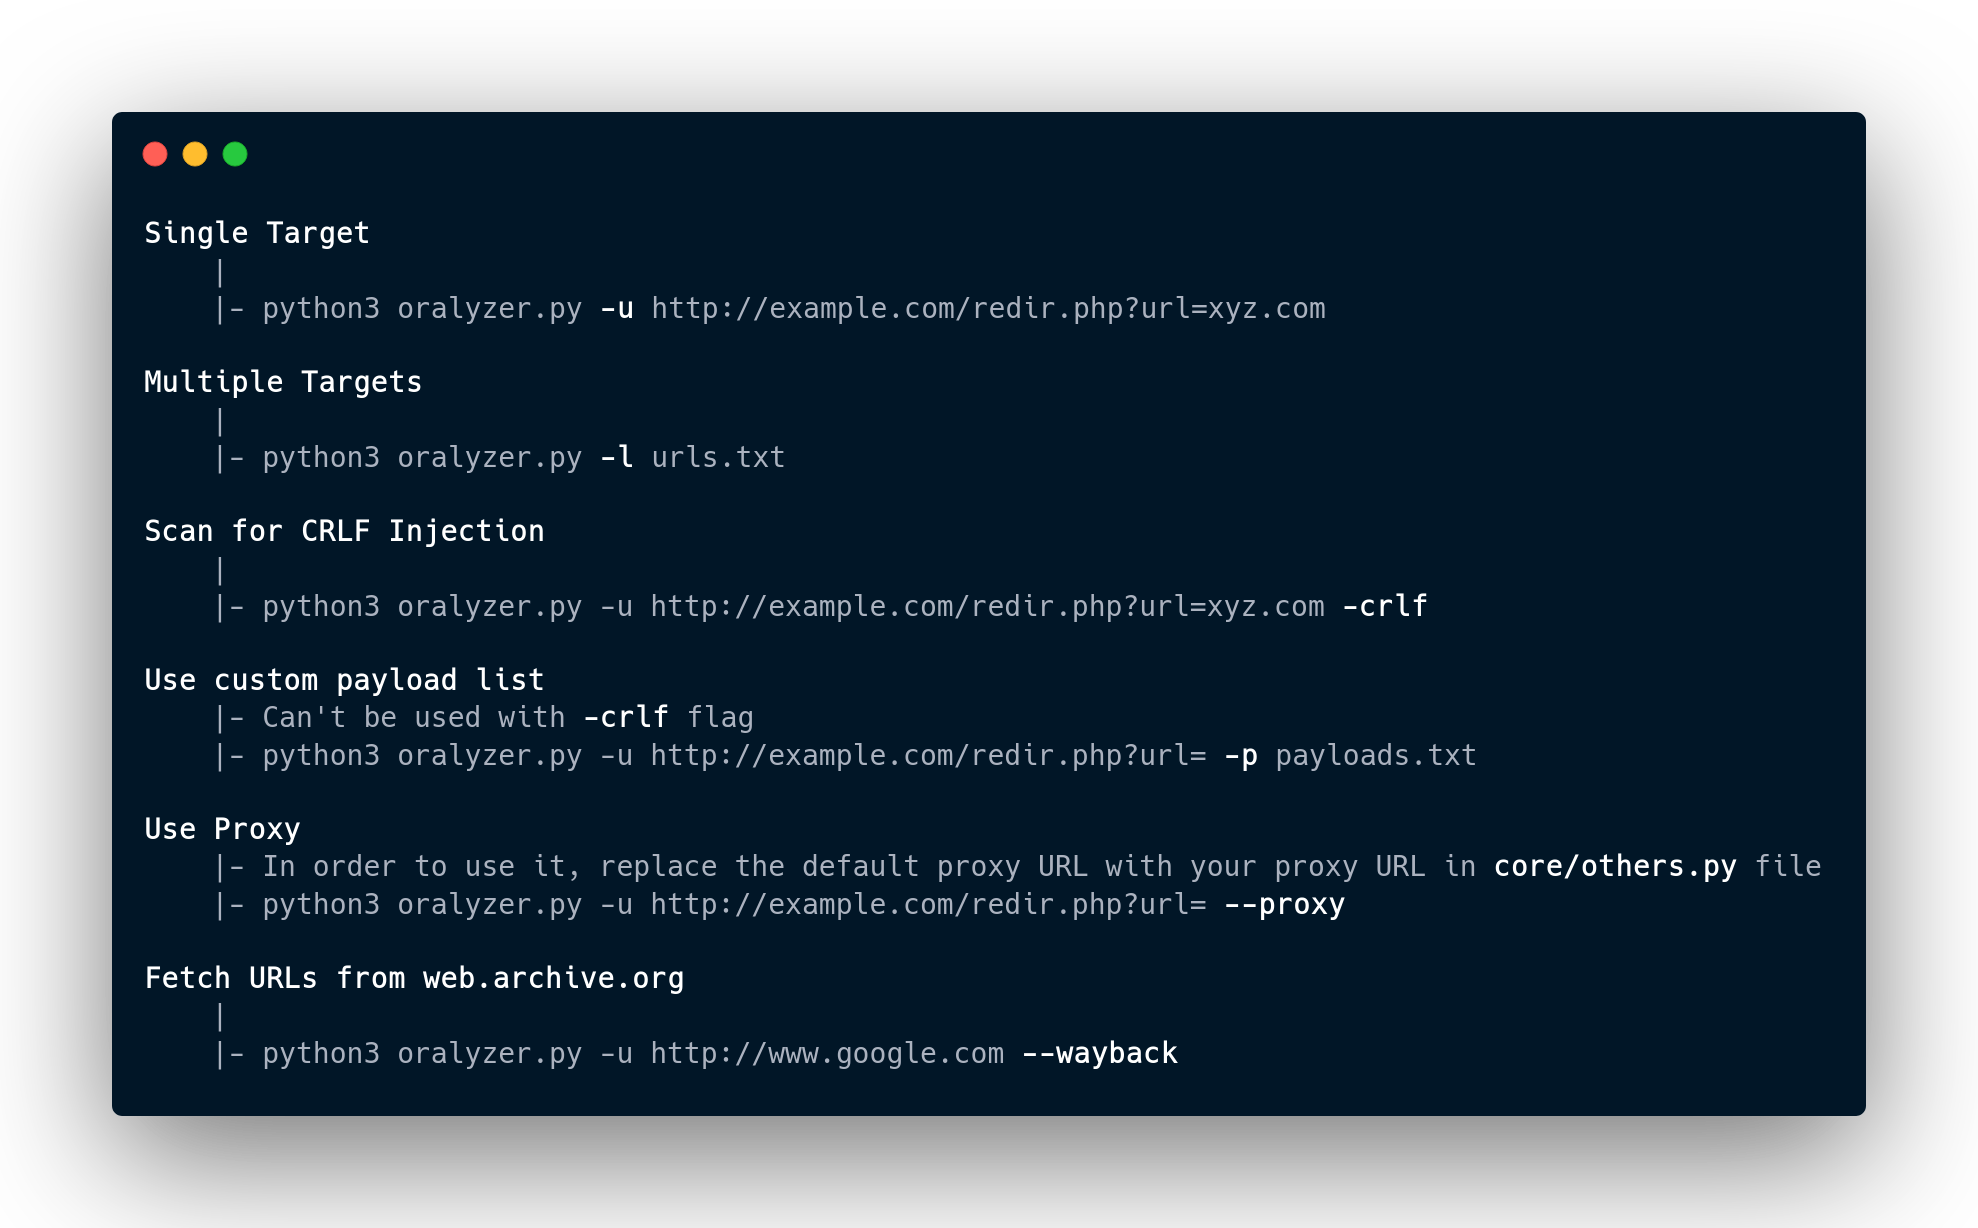 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
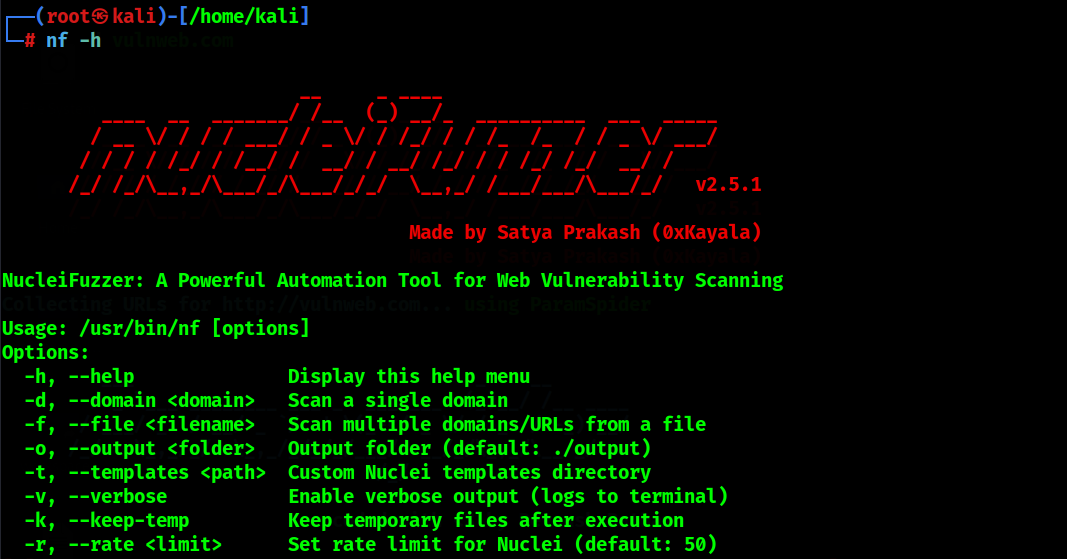 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
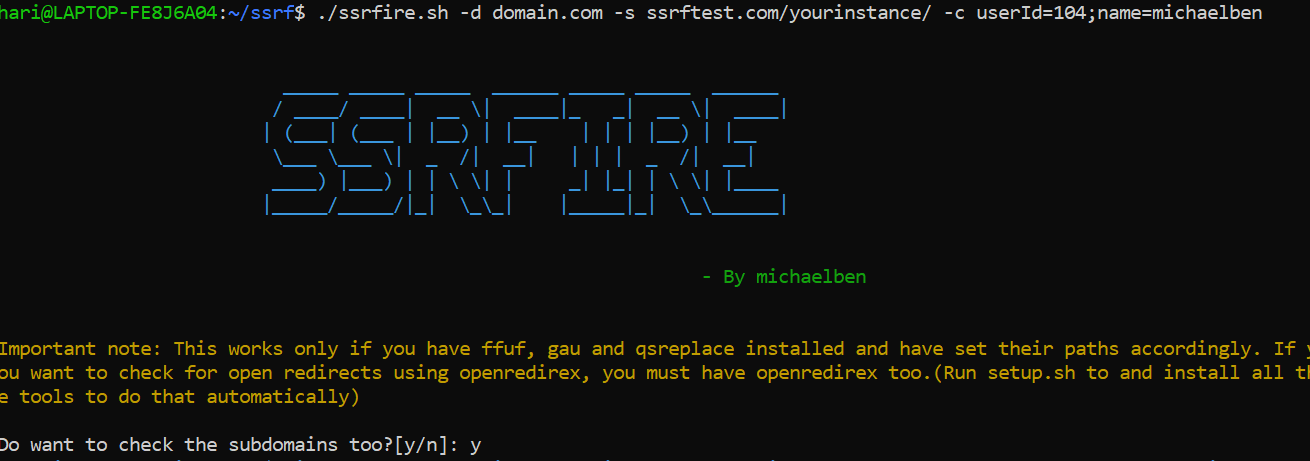 ksharinarayanan/ssrfire
An automated SSRF finder. Just give the domain name and your server and chill! ;) Also has options to find XSS and open redirects