

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
git-scanner — A tool for bug hunting or pentesting for targeting websites that have open .git repositories available in public | Kitploit
Tools/GitHubGitHub/hightechsec/git-scanner
Vulnerability ScannersInformation GatheringWeb SecurityPenetration Testing
GitHubhightechsec/git-scanner

git-scanner

A tool for bug hunting or pentesting for targeting websites that have open .git repositories available in public

View Repository
38493636 years agoReviewed by Kitploit
Share

Git Scanner Framework

License Build Build GitHub code size in bytes GitHub repo size GitHub last commit GitHub stars GitHub pull requests GitHub forks GitHub issues GitHub watchers

This tool can scan websites with open .git repositories for Bug Hunting/ Pentesting Purposes and can dump the content of the .git repositories from webservers that found from the scanning method. This tool works with the provided Single target or Mass Target from a file list.

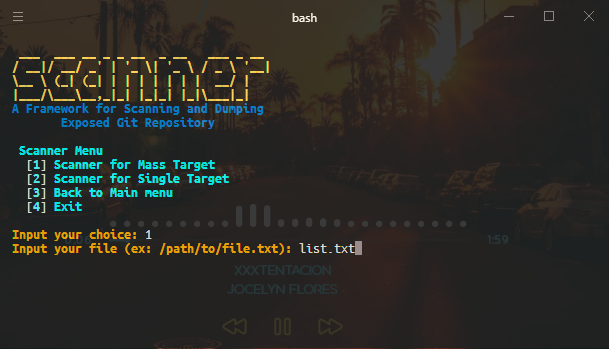
Installation

- git clone https://github.com/HightechSec/git-scanner
- cd git-scanner
- bash gitscanner.sh

or you can install in your system like this

- git clone https://github.com/HightechSec/git-scanner
- cd git-scanner
- sudo cp gitscanner.sh /usr/bin/gitscanner && sudo chmod +x /usr/bin/gitscanner
- $ gitscanner

Usage

  • Menu's
    • Menu 1 is for scanning and dumping git repositories from a provided file that contains the list of the target url or a provided single target url.
    • Menu 2 is for scanning only a git repositories from a provided file that contains the list of the target url or a provided single target url.
    • Menu 3 is for Dumping only the git repositories from a provided file that contains list of the target url or a provided single target url. This will work for the Maybe Vuln Results or sometimes with a repository that had directory listing disabled or maybe had a 403 Error Response.
    • Menu 4 is for Extracting files only from a Folder that had .git Repositories to a destination folder
  • URL Format
    • Use http:// like http://example.com or https:// like https://example.com for the url formatting
    • Make sure use this format in the files that contains the list of possible target that you have, Example:
      • https://target.com
      • http://hackerone.com
      • https://bugcrowd.com
  • Extractor
    • When using Extractor, make sure the location of the git repositories that you select are correct. Remember, The first option is for inputing the Selected git repository and the second option is for inputing the Destination folder

Requirements

  • curl
  • bash
  • git
  • sed

Todos

  • Creating a Docker Images if it's possible
  • Adding Extractor on the next Version Added in version 1.0.2#beta but still experimental.
  • Adding Thread Processing Multi Processing (Bash doesn't Support Threading)

Changelog

All notable changes to this project listed in this file

Credits

Thanks to:

  • GitTools by internetwache
  • Mass Git Scanner by Ade Little
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →






