Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
NucleiFuzzer — Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing templates to detect XSS, SQLi, SSRF, and Open Redirects. | Kitploit
Tools/GitHubGitHub/0xkayala/nucleifuzzer
ReconnaissanceVulnerability ScannersInformation GatheringWeb SecurityFuzzingPenetration Testing
GitHub0xkayala/nucleifuzzer

NucleiFuzzer

Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing templates to detect XSS, SQLi, SSRF, and Open Redirects.

View Repository
1.9k259586 days agoReviewed by Kitploit
Share
Website

NucleiFuzzer = Nuclei + Paramspider + waybackurls + gauplus + hakrawler + katana + Fuzzing Templates

Overview

NucleiFuzzer is an advanced automation tool designed to streamline and optimize web application security testing by integrating a suite of powerful URL discovery and vulnerability scanning tools. It combines ParamSpider, Waybackurls, Katana, Gauplus, and Hakrawler to comprehensively gather and enumerate potential entry points for web applications. Leveraging the power of Nuclei, it scans these endpoints using fuzzing-templates to effectively uncover a wide range of vulnerabilities.

The enhanced NucleiFuzzer is built for speed and accuracy, utilizing advanced URL validation, deduplication with uro, and precise HTTP filtering using httpx. This tool provides security professionals, bug bounty hunters, and web developers with a seamless workflow to detect and address security risks, ensuring robust web application protection.

Key Features:

  1. Comprehensive URL Discovery: Integrates multiple tools (ParamSpider, Waybackurls, Katana, Gauplus, and Hakrawler) to ensure exhaustive coverage of URLs and parameters.
  2. Enhanced Vulnerability Scanning: Uses Nuclei with fuzzing-templates to identify critical security issues with precision.
  3. Advanced Filtering and Validation: Removes duplicates and irrelevant results using uro and httpx for cleaner and more focused scanning.
  4. Rate Limiting for Efficiency: Allows customizable request rates for optimal performance during scans.
  5. Customizable and User-Friendly: Easy-to-configure options for domains, files, and output directories, catering to both individual and batch scans.

Take advantage of NucleiFuzzer to safeguard your web applications against vulnerabilities and attacks with an enhanced, efficient, and reliable security testing solution!

Note: Nuclei + Paramspider + waybackurls + gauplus + hakrawler + katana + Fuzzing Templates = NucleiFuzzer

Important: Make sure the tools Nuclei, Paramspider, waybackurls, gauplus, hakrawler, katana, httpx & uro are installed on your machine and executing correctly to use the NucleiFuzzer without any issues.

✨ New Features (Updated)

  • 🔍 Automated Recon + Crawling
  • ⚡ Nuclei Vulnerability Scanning
  • 📊 JSON + HTML Reporting
  • 🧠 AI Vulnerability Analysis (NEW)
  • 📁 Clean Output & Severity Grouping

Tools included:

  • Darkmoon - Open source (GPL-3.0) autonomous AI penetration testing platform covering web, API, Active Directory and Kubernetes, with proof of exploitation.
  • Nuclei git clone https://github.com/projectdiscovery/nuclei.git
  • ParamSpider git clone https://github.com/0xKayala/ParamSpider.git
  • waybackurls git clone https://github.com/tomnomnom/waybackurls.git
  • gauplus git clone https://github.com/bp0lr/gauplus.git
  • hakrawler git clone https://github.com/hakluke/hakrawler.git
  • katana git clone https://github.com/projectdiscovery/katana.git
  • httpx git clone https://github.com/projectdiscovery/httpx.git
  • uro https://github.com/s0md3v/uro.git

Templates:

Fuzzing Templates git clone https://github.com/projectdiscovery/nuclei-templates.git

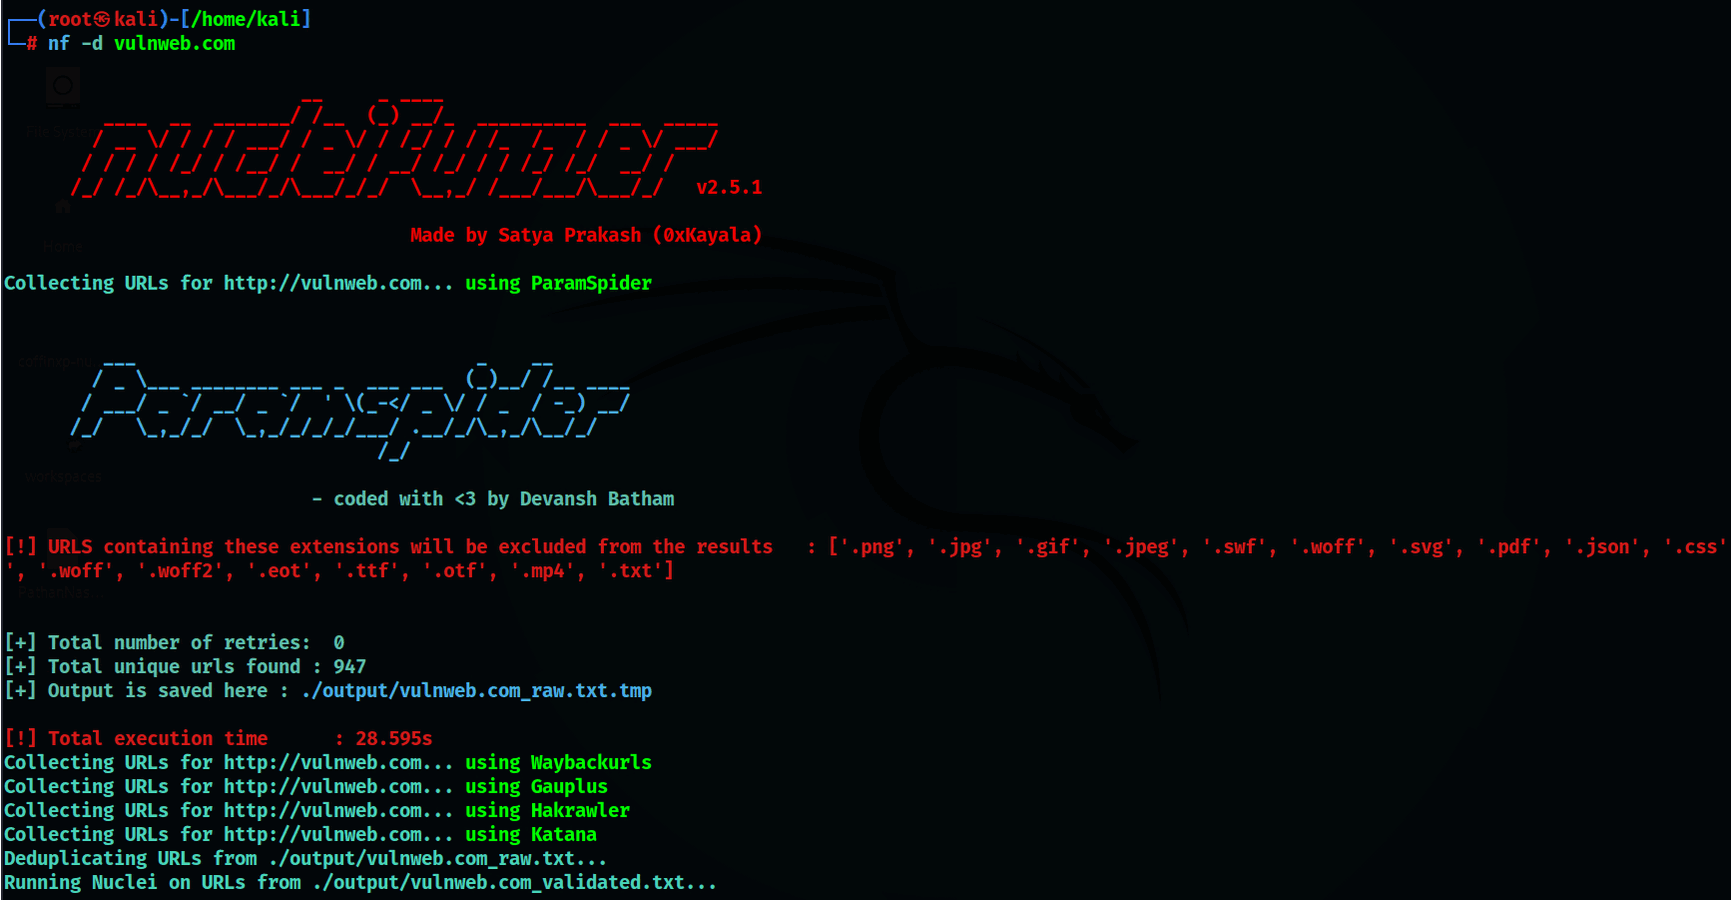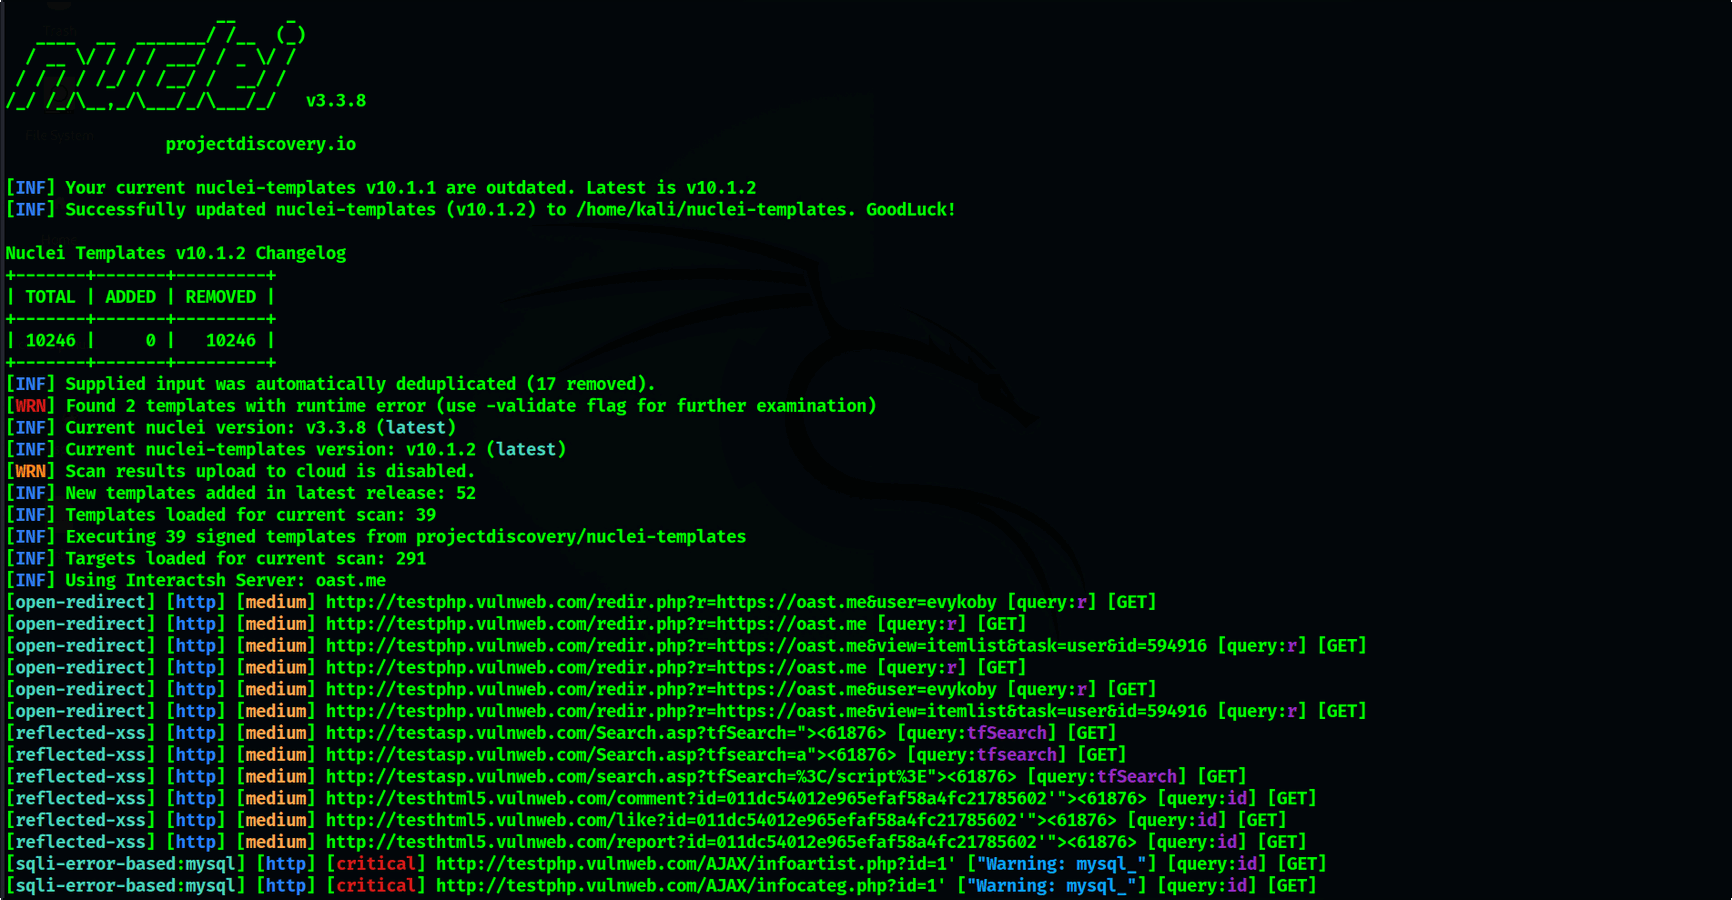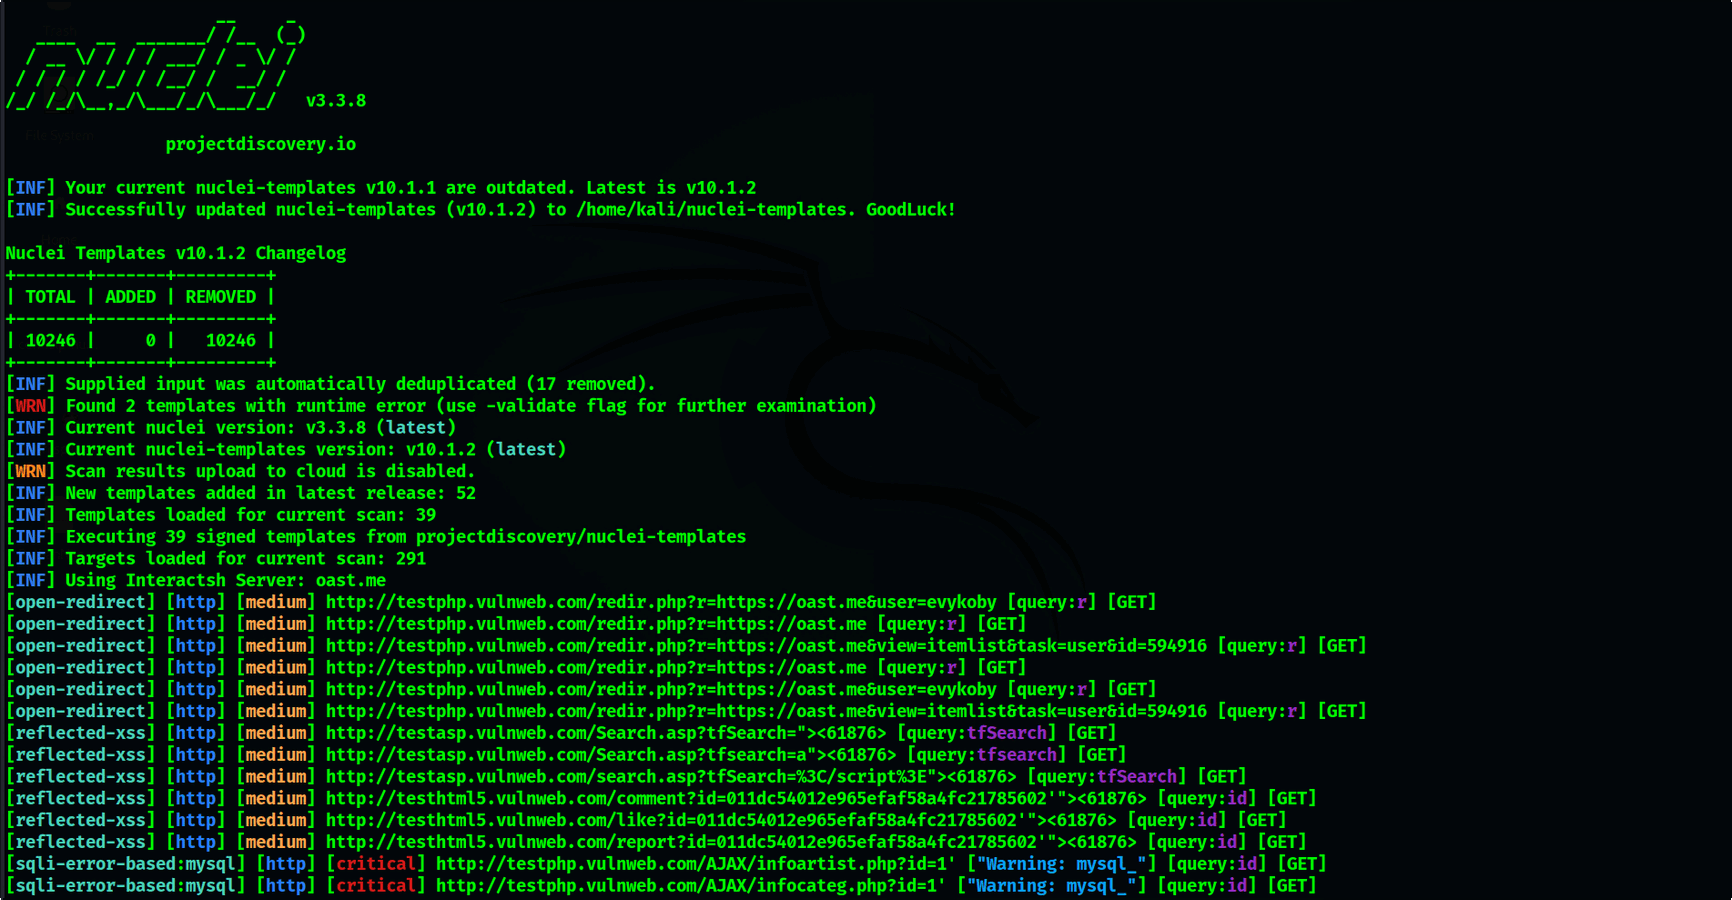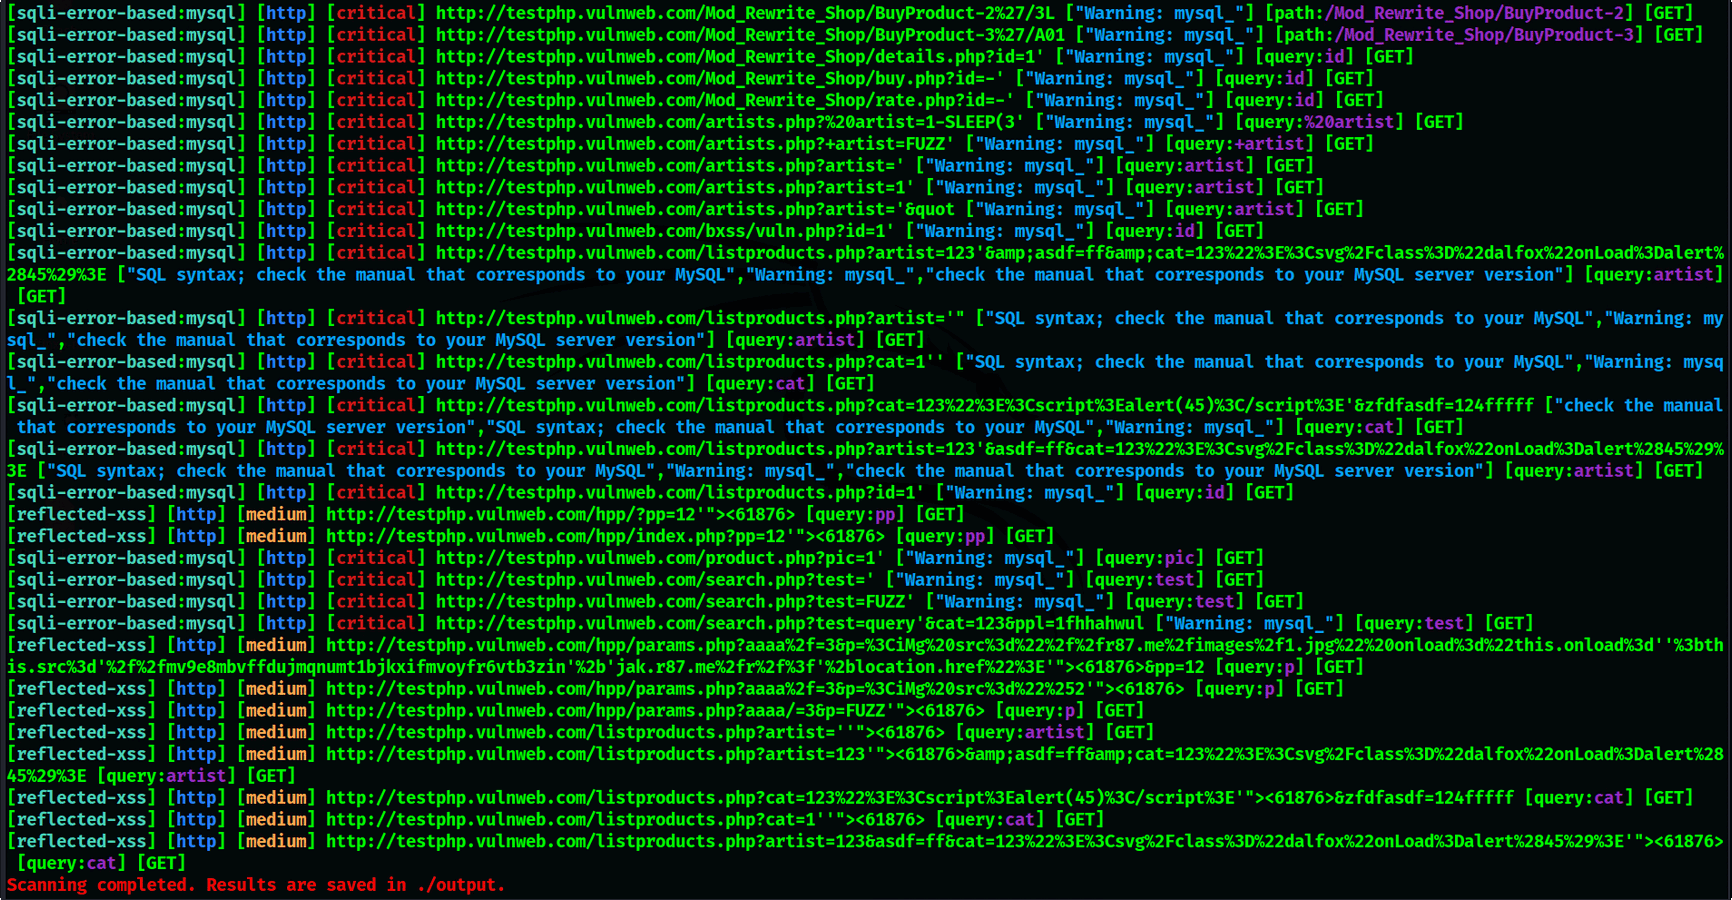
Screenshot

image

Output

image

Usage

nf -h

This will display help for the tool. Here are the options it supports.

NucleiFuzzer: A Powerful Automation Tool for Web Vulnerability Scanning

Usage: /usr/bin/nf [options]

Options:
  -h, --help              Display help information
  -d, --domain <domain>   Single domain to scan for vulnerabilities
  -f, --file <filename>   File containing multiple domains/URLs to scan
  -o, --output <folder>   Specify output folder for scan results (default: ./output)

Installation:

To install NucleiFuzzer, follow these steps:

git clone https://github.com/0xKayala/NucleiFuzzer.git && cd NucleiFuzzer && sudo chmod +x install.sh && ./install.sh && (command -v nf &> /dev/null && nf -h || echo "Installation failed: Command 'nf' not found. Please check for errors during installation.") && cd .. || echo "Failed to clone or navigate to NucleiFuzzer repository. Please check your setup."

Examples:

Here are a few examples of how to use NucleiFuzzer:

  • Run NucleiFuzzer on a single domain:

    nf -d example.com
    
  • Run NucleiFuzzer on multiple domains from a file:

    nf -f file.txt
    

Practical Demonstration:

For a Practical Demonstration of the NucleiFuzzer tool see the below video 👇

Star History

Star History Chart

Contributing

Contributions are welcome! If you'd like to contribute to NucleiFuzzer, please follow these steps:

  1. Fork the repository.
  2. Create a new branch.
  3. Make your changes and commit them.
  4. Submit a pull request.

Made by Satya Prakash | 0xKayala \

A Security Researcher and Bug Hunter \

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →