
CVE-2022-22947-Rce_POC
 hunzi0/cve-2022-22947-rce_poc
批量url检测Spring-Cloud-Gateway-CVE-2022-22947
api-security-testingexploitationpenetration-testing+3
7
hunzi0/cve-2022-22947-rce_poc批量url检测Spring-Cloud-Gateway-CVE-2022-22947
 mathis2001/cve-2018-25031
CVE-2018-25031 tests
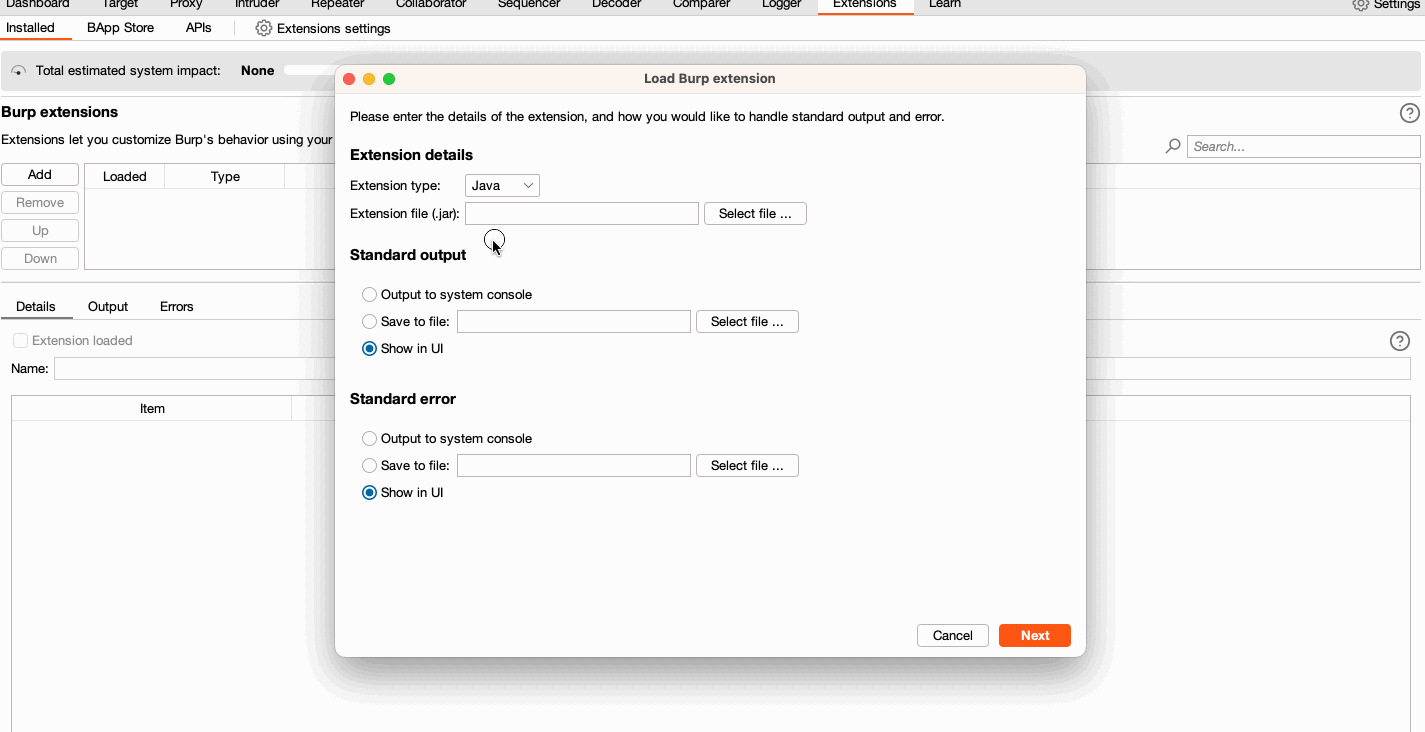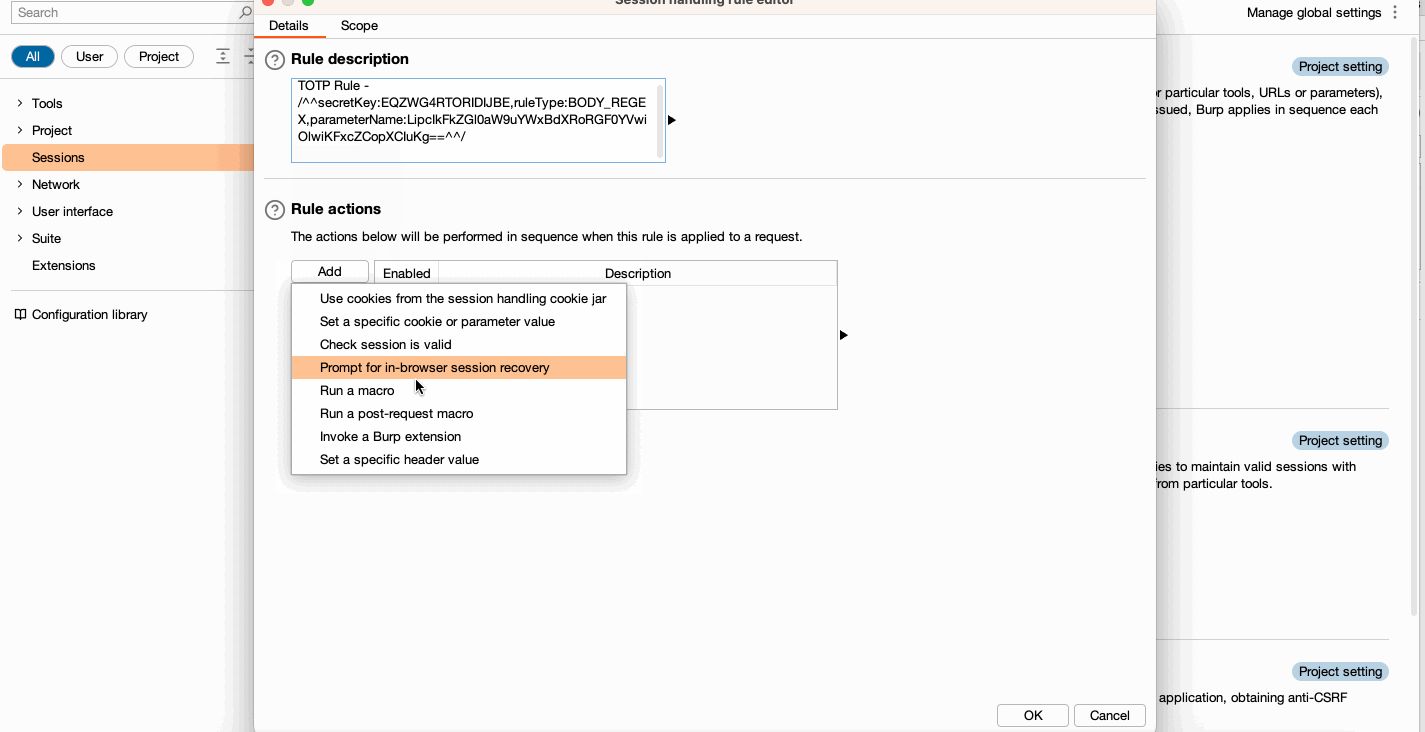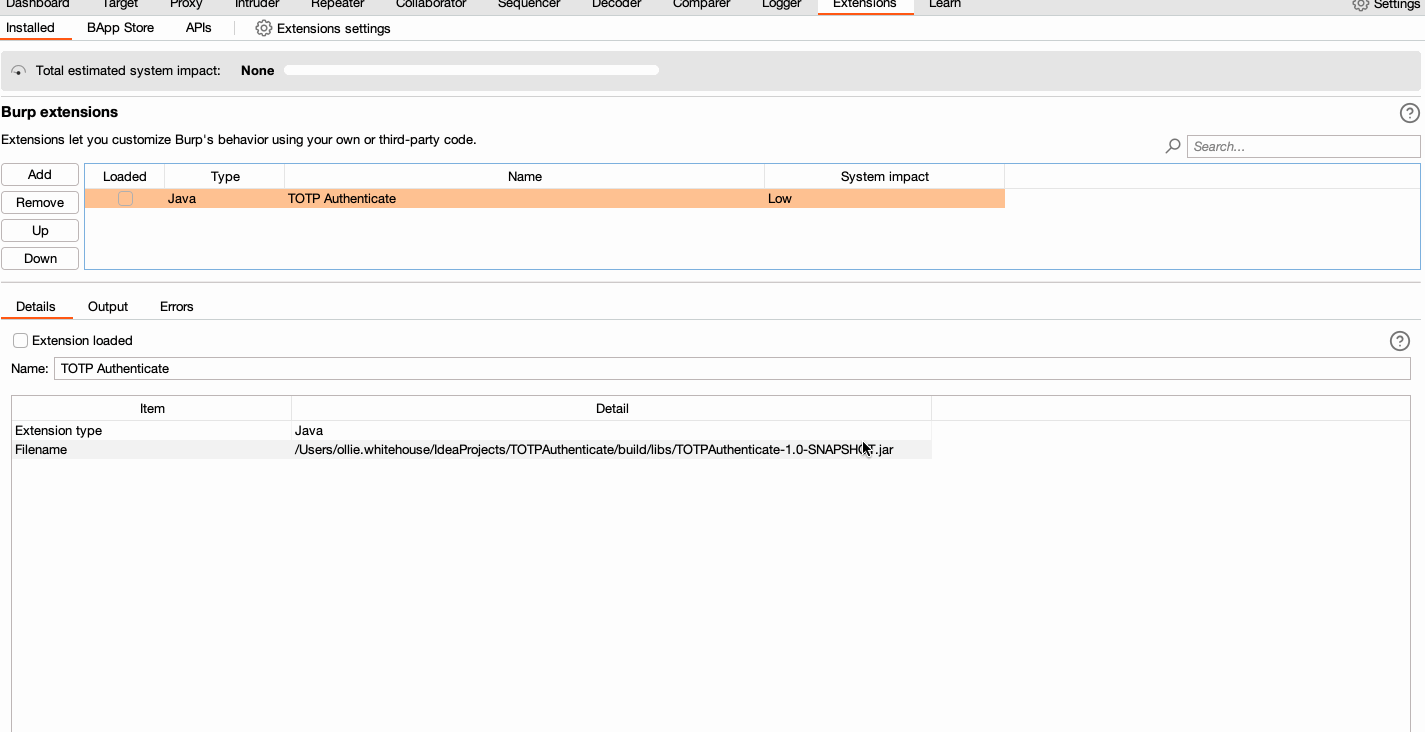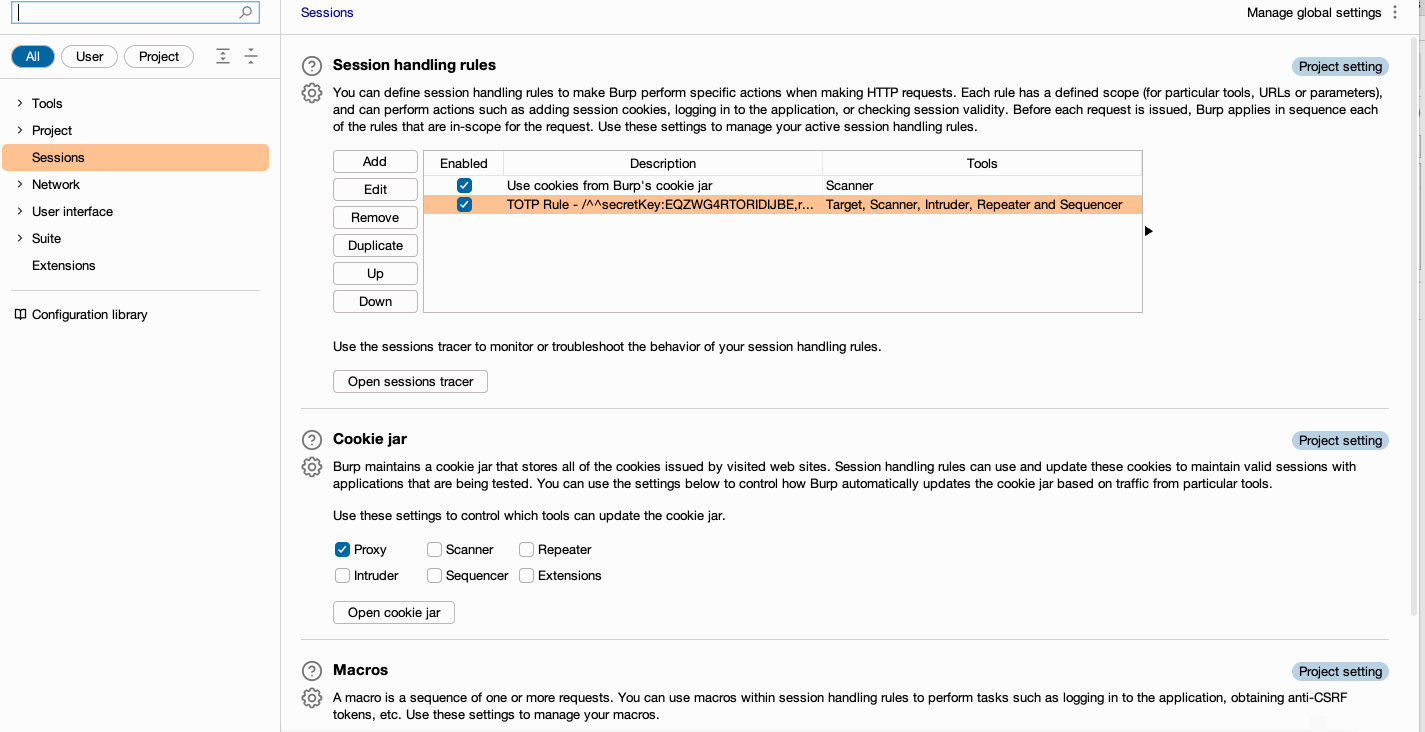 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
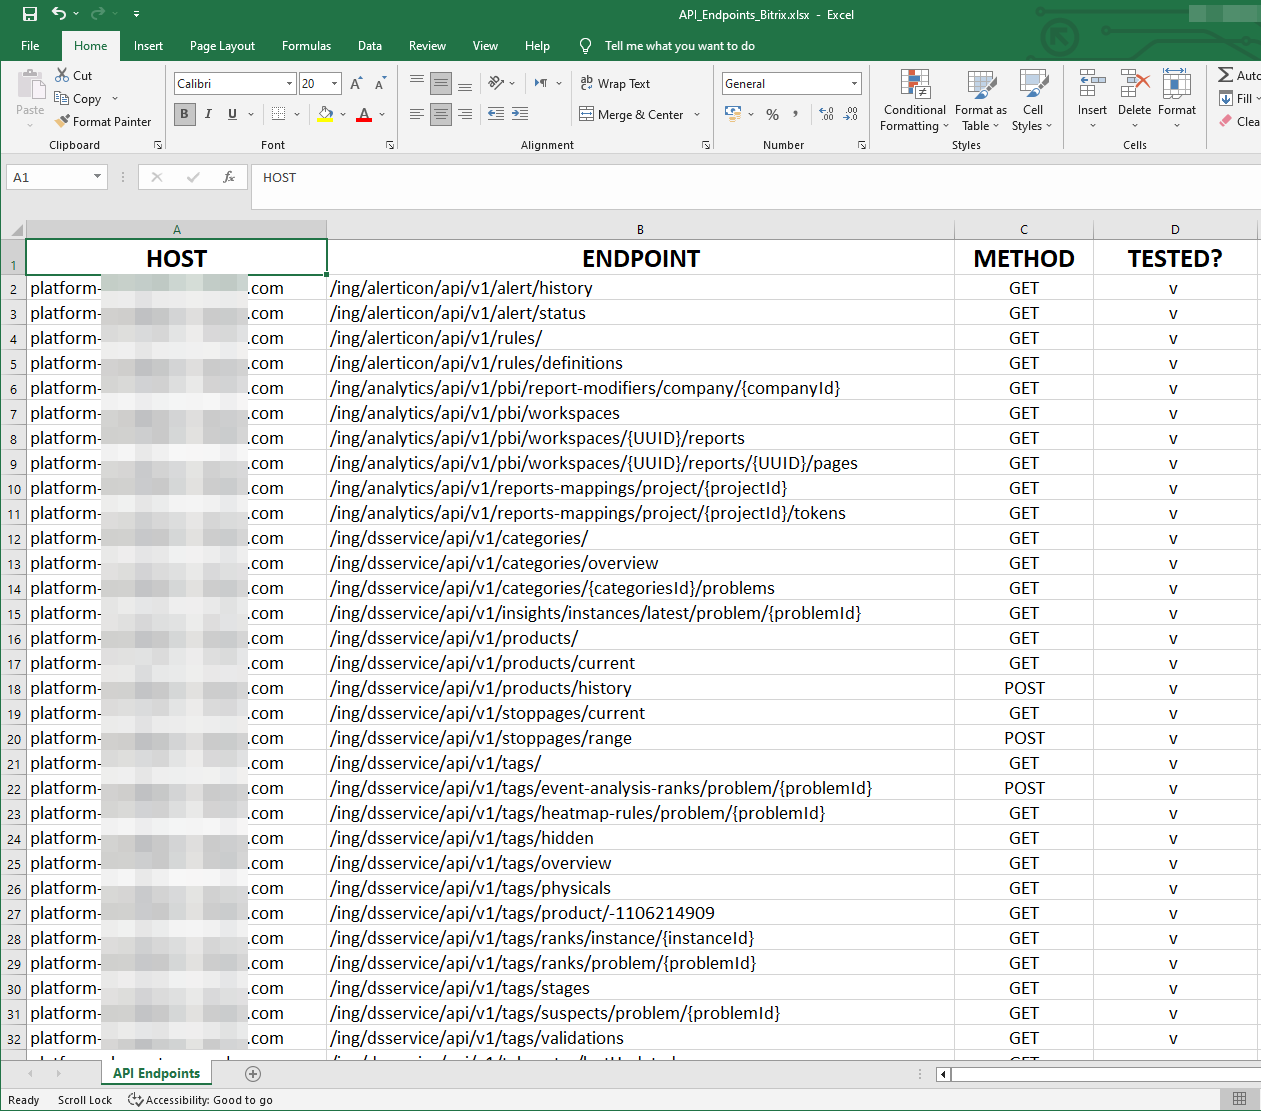 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 bandit92/cve2022-1388_testapi
A Test API for testing the POC against CVE-2022-1388
 loneyers/spring4shell
Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
 0xmaximus/apache-commons-text-cve-2022-42889
Burp Bounty profile for detecting Apache Text4Shell (CVE-2022-42889), an RCE in Commons Text 1.5-1.9, by scanning HTTP requests.
 ebrasha/abdal-cve-2026-63030
Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 sevdakhidirova/cve-2025-32375-poc
Python proof-of-concept exploit for CVE-2025-32375 in BentoML, demonstrating and validating the vulnerability against affected deployments.
 kabiri-labs/cve-2024-40094
This script exploits the CVE-2024-40094 vulnerability in graphql-java
 george0papasotiriou/cve-2026-5432-graphql-batching-alias-confusion-sql-injection
Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…
 foxer131/cve-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…
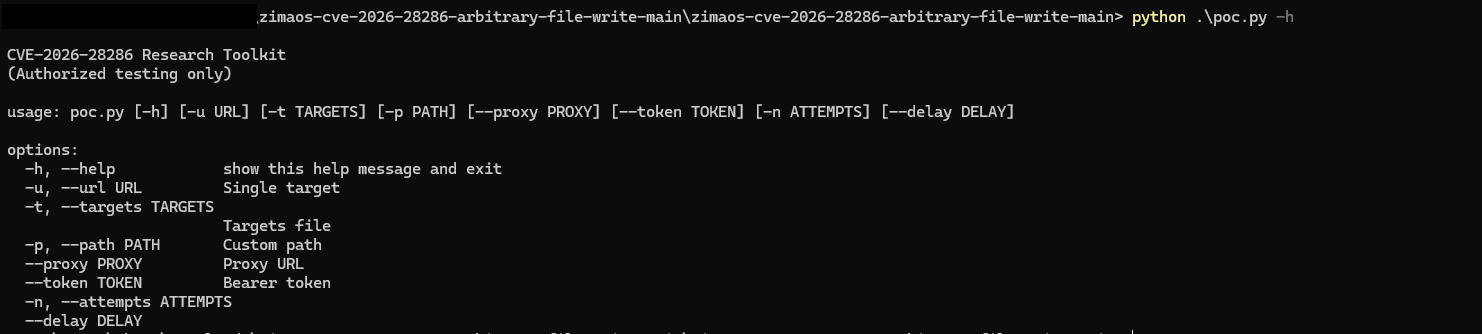 rushi9/zimaos-cve-2026-28286-arbitrary-file-write
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…