
caddy
 caddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
anti-botencryption-decryption-toolsgeneral-purpose-utilities+1
74.8k7h 16m ago
caddyserver/caddyFast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 beefproject/beef
The Browser Exploitation Framework Project
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 timvisee/send
📬 Simple, private file sharing. Mirror of https://gitlab.com/timvisee/send
 owasp/securityshepherd
Web and mobile application security training platform
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
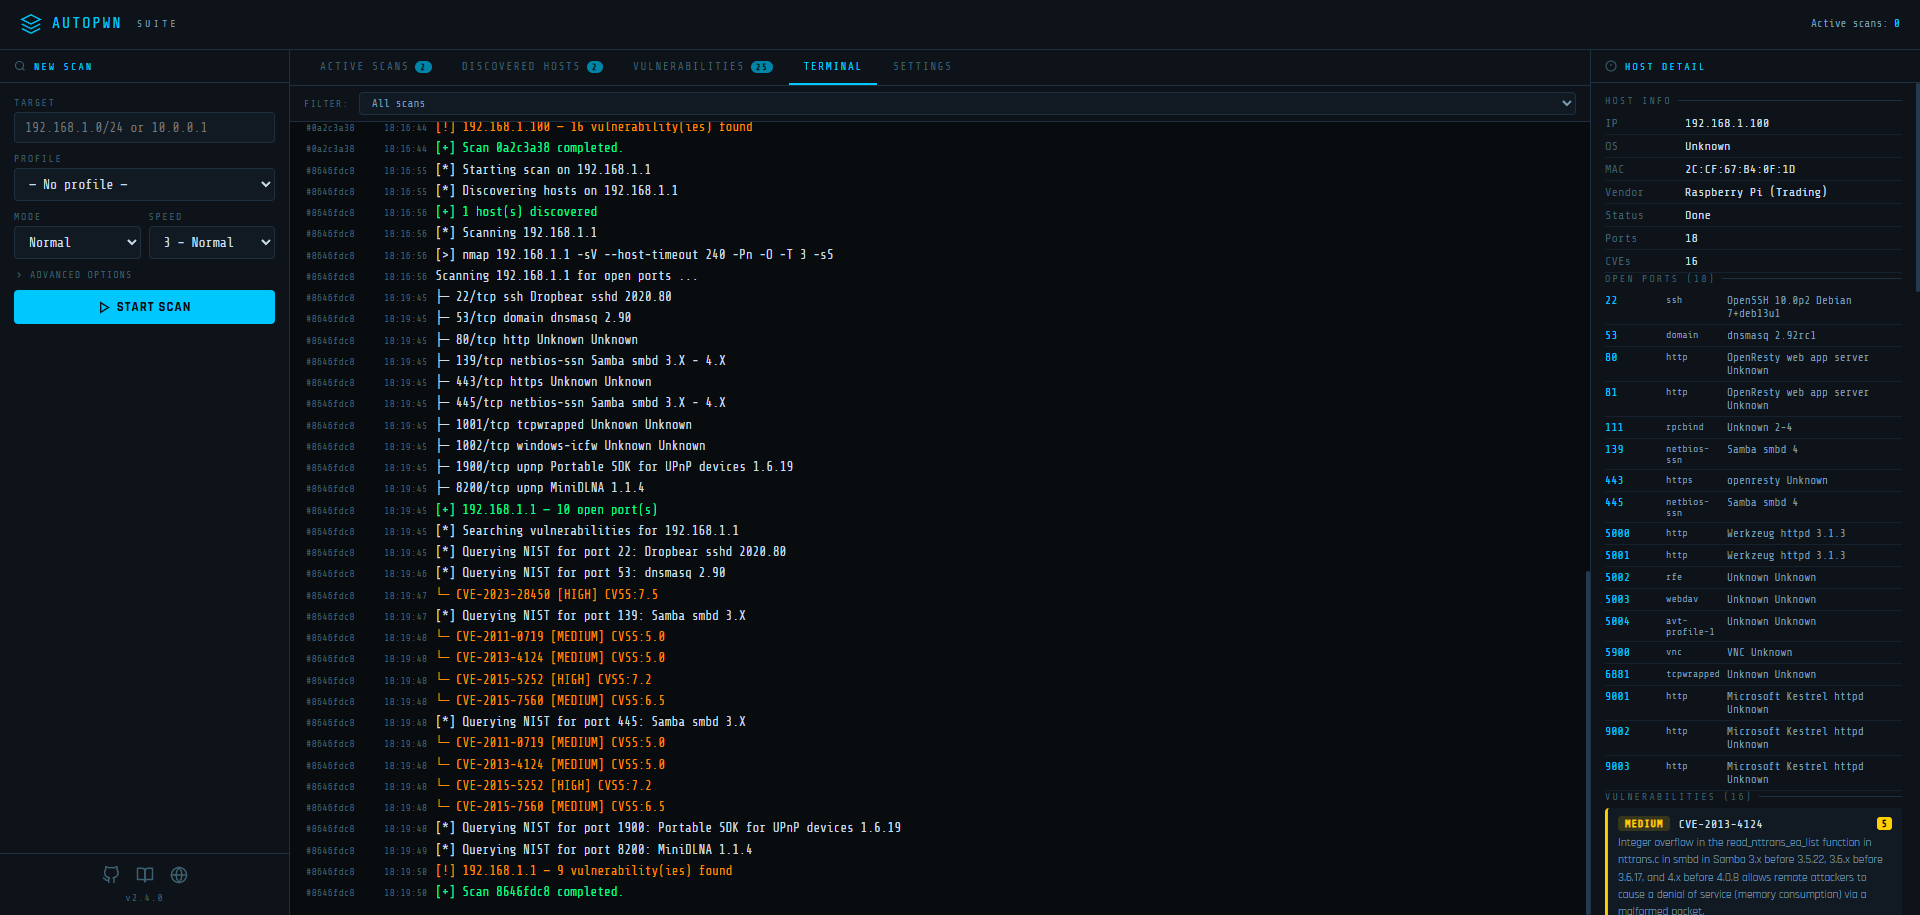 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
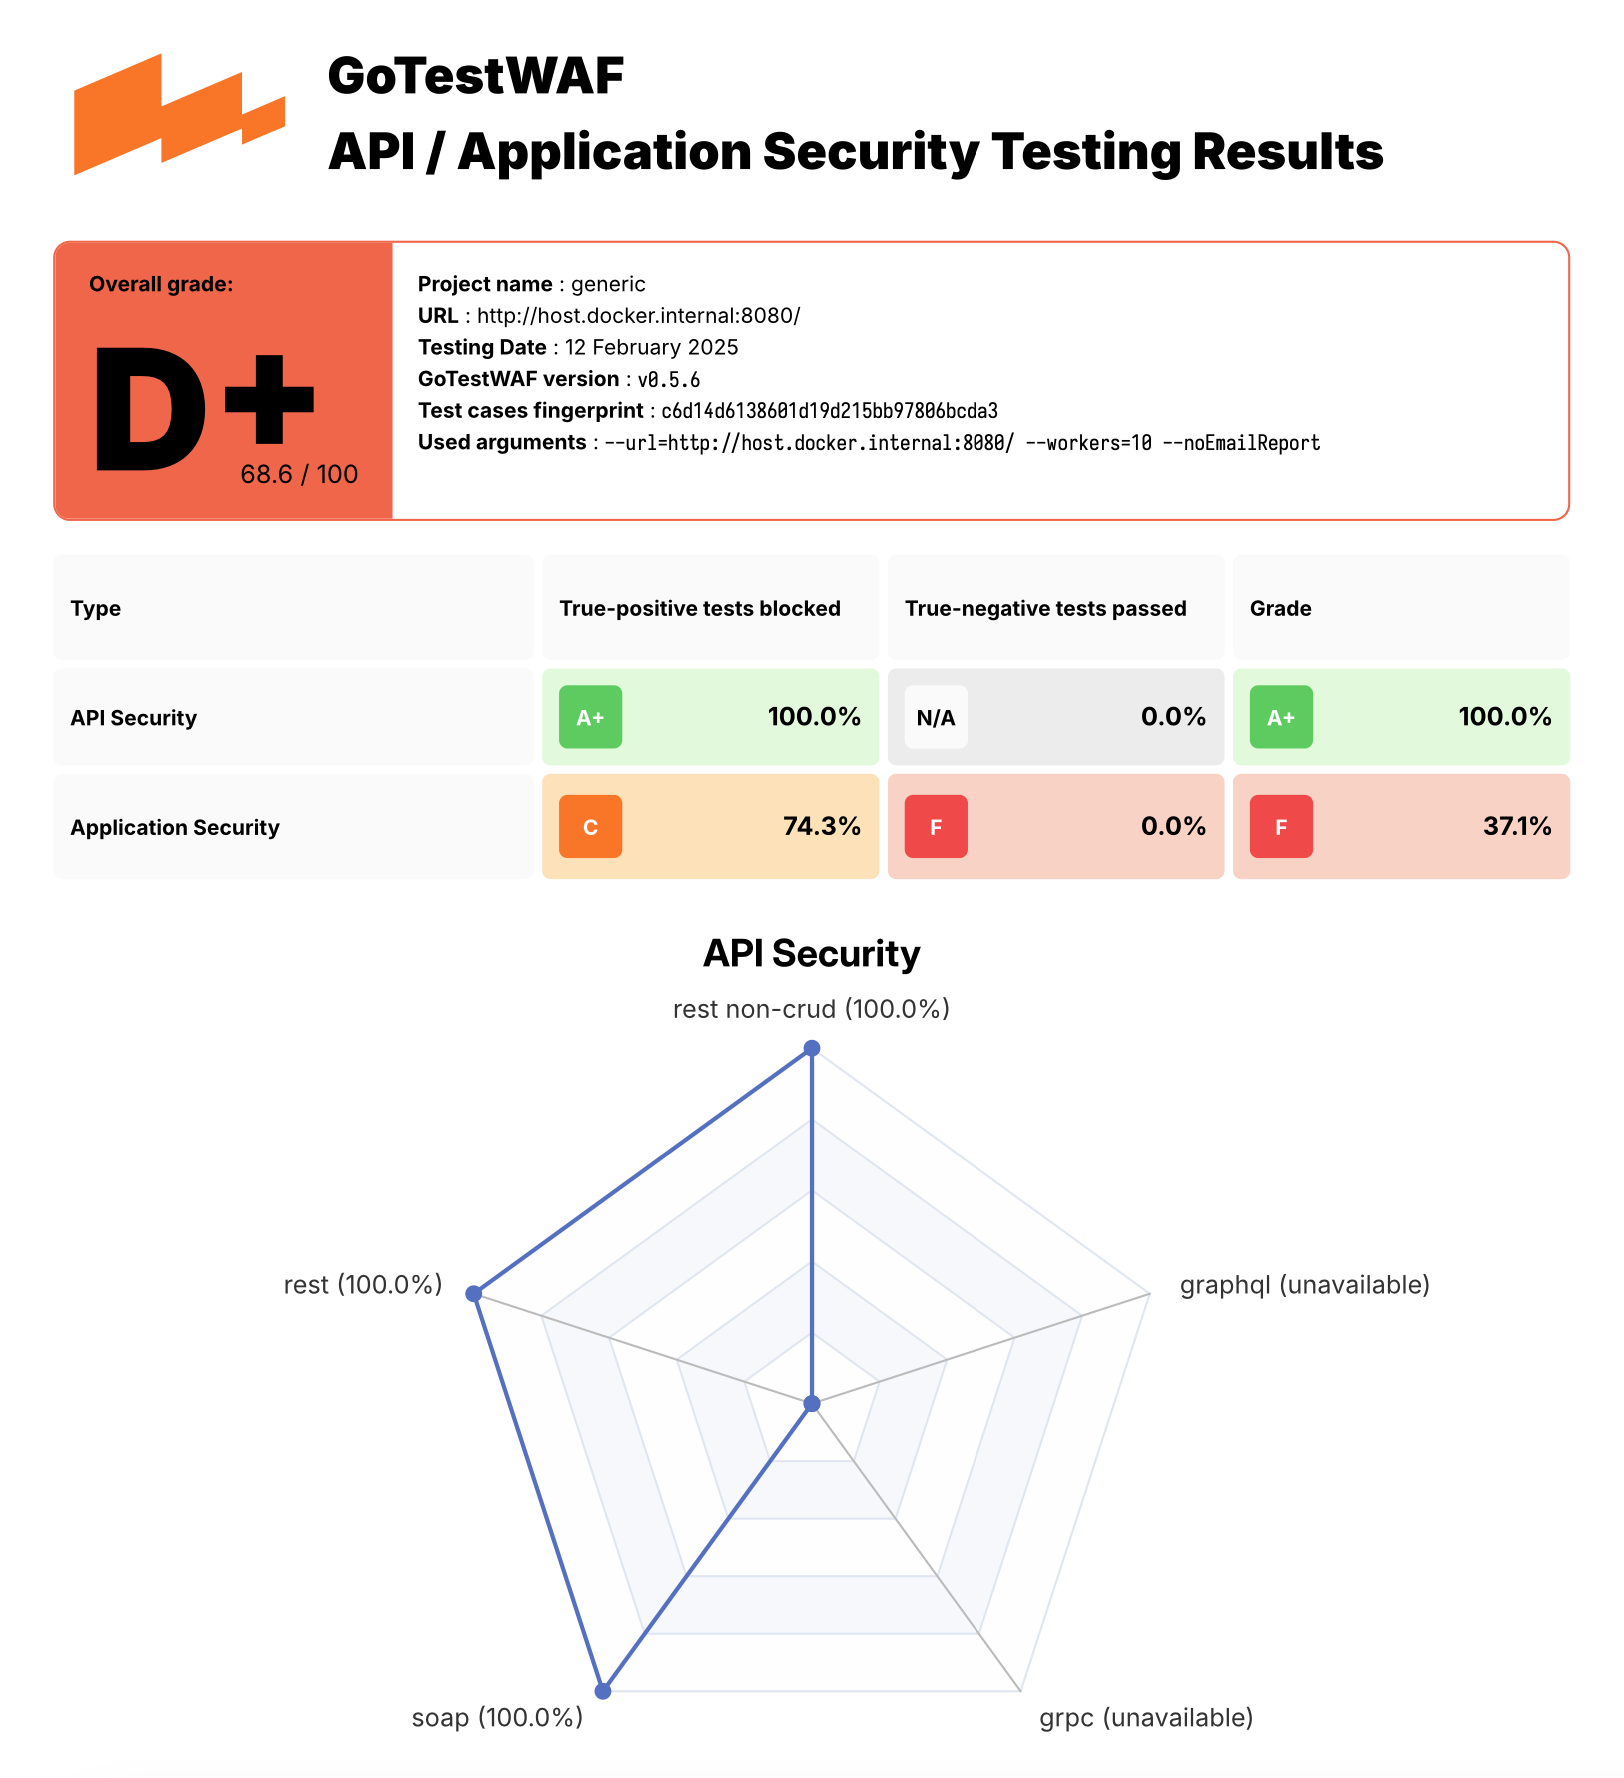 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
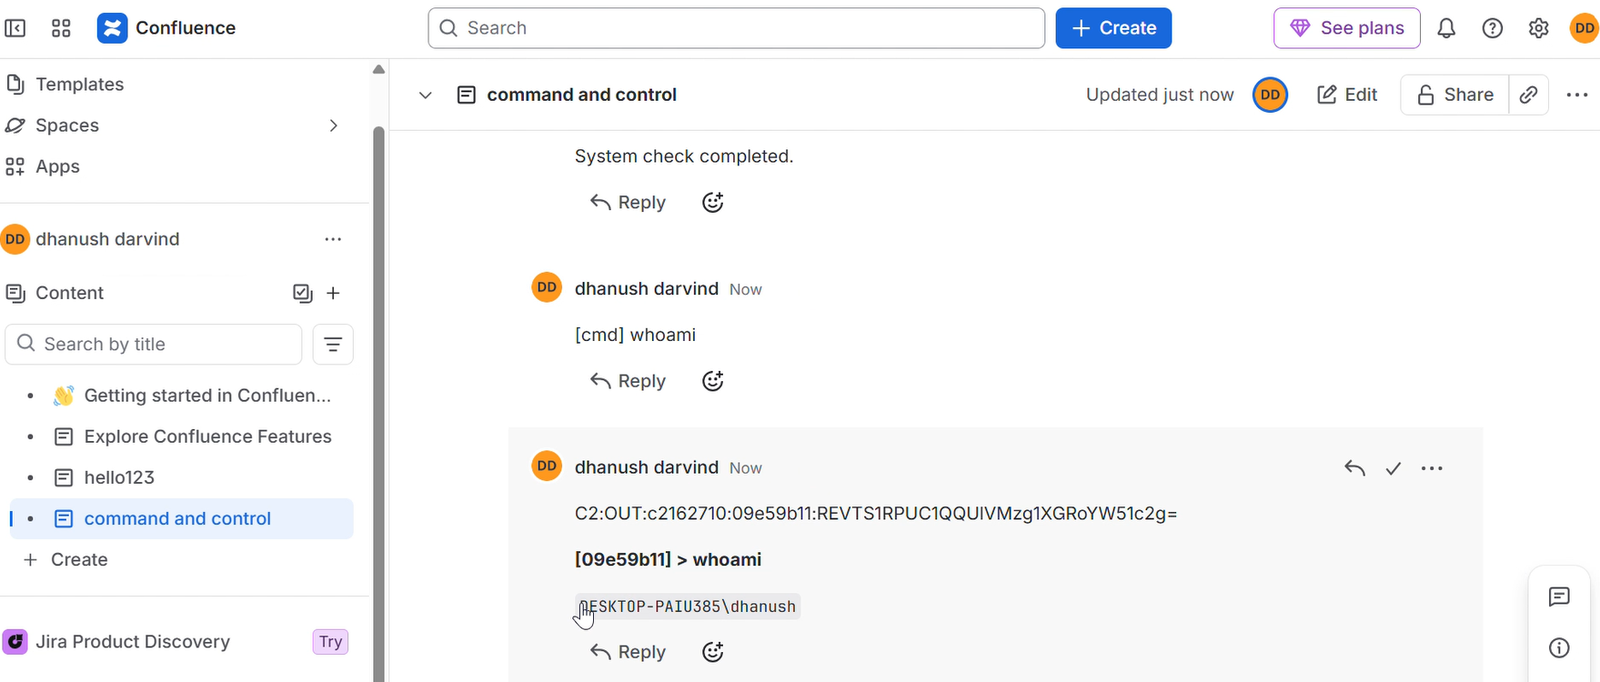 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 bst04/cybersources
A curated list of cybersecurity tools and resources.