
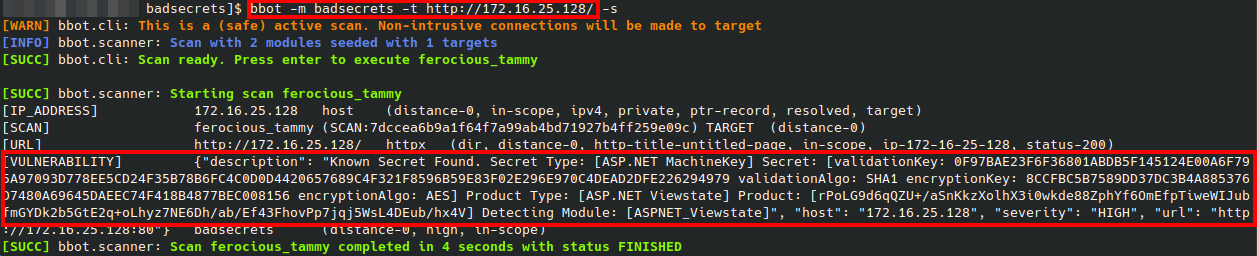
badsecrets
 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
cryptographypenetration-testingsecret-detection+2
832
blacklanternsecurity/badsecretsA library for detecting known secrets across many web frameworks
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
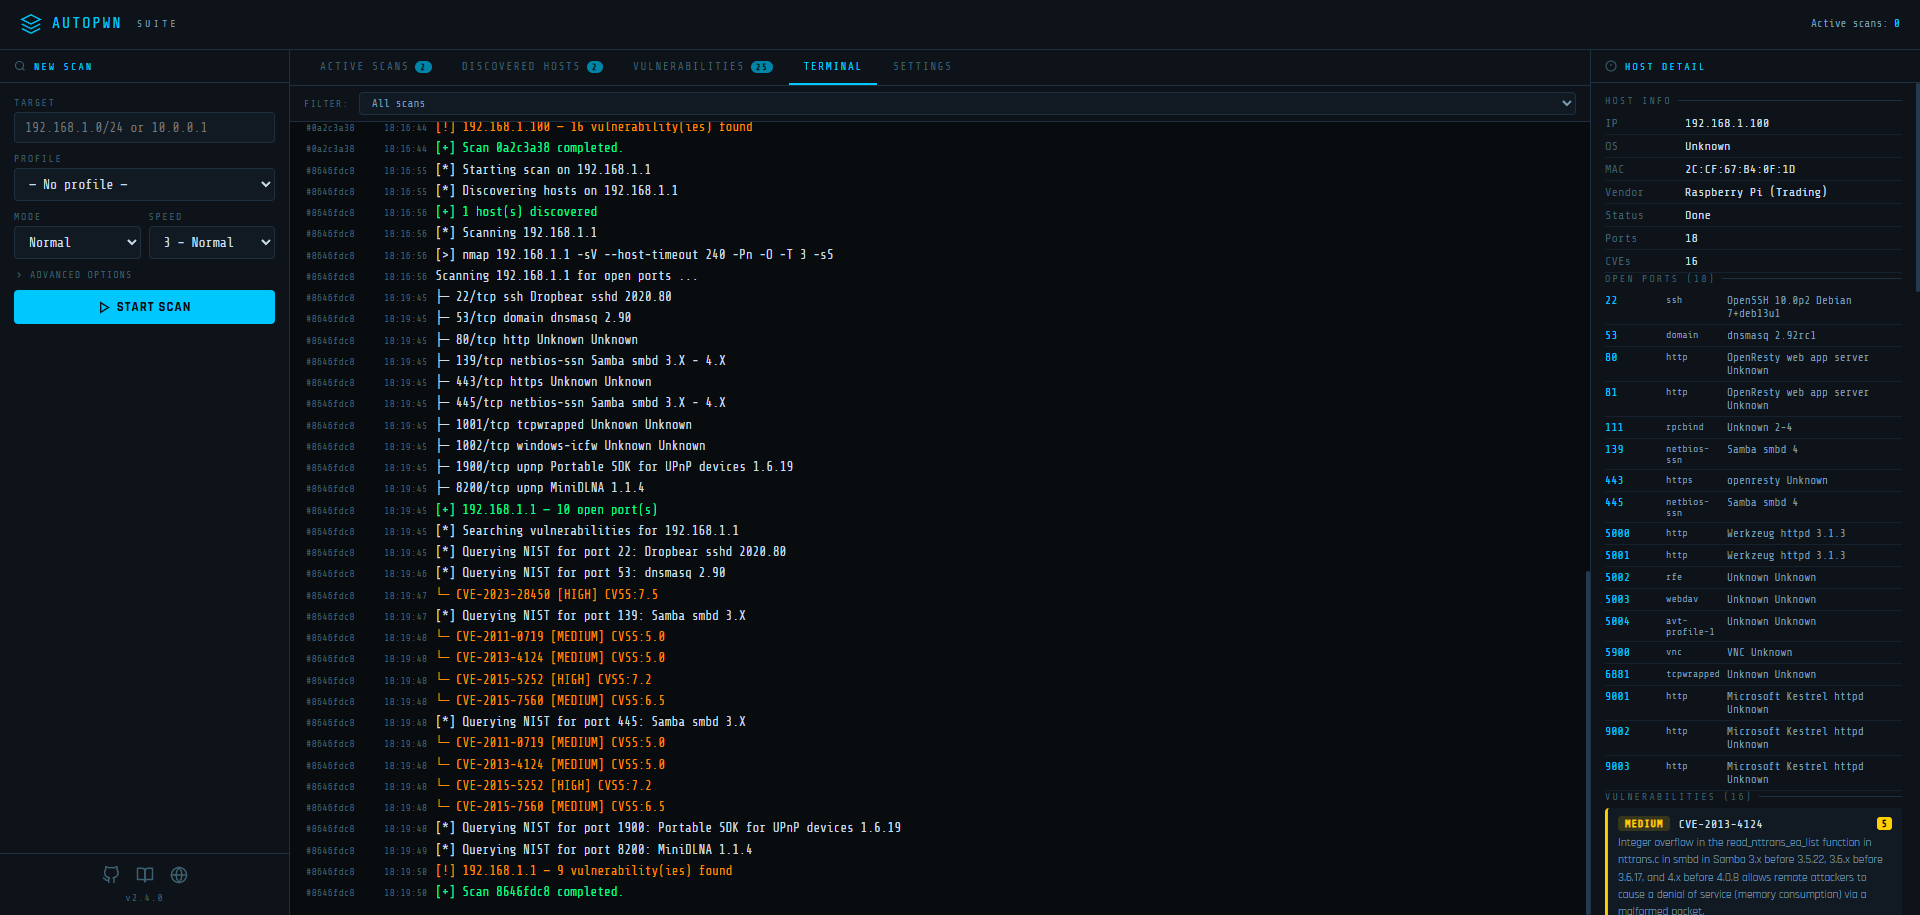 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 rknf404/chromium-hardening-guide
Harden chromium (somewhat) for privacy and security (and performance)
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 projectdiscovery/pd-agent
ProjectDiscovery Cloud - Agent
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
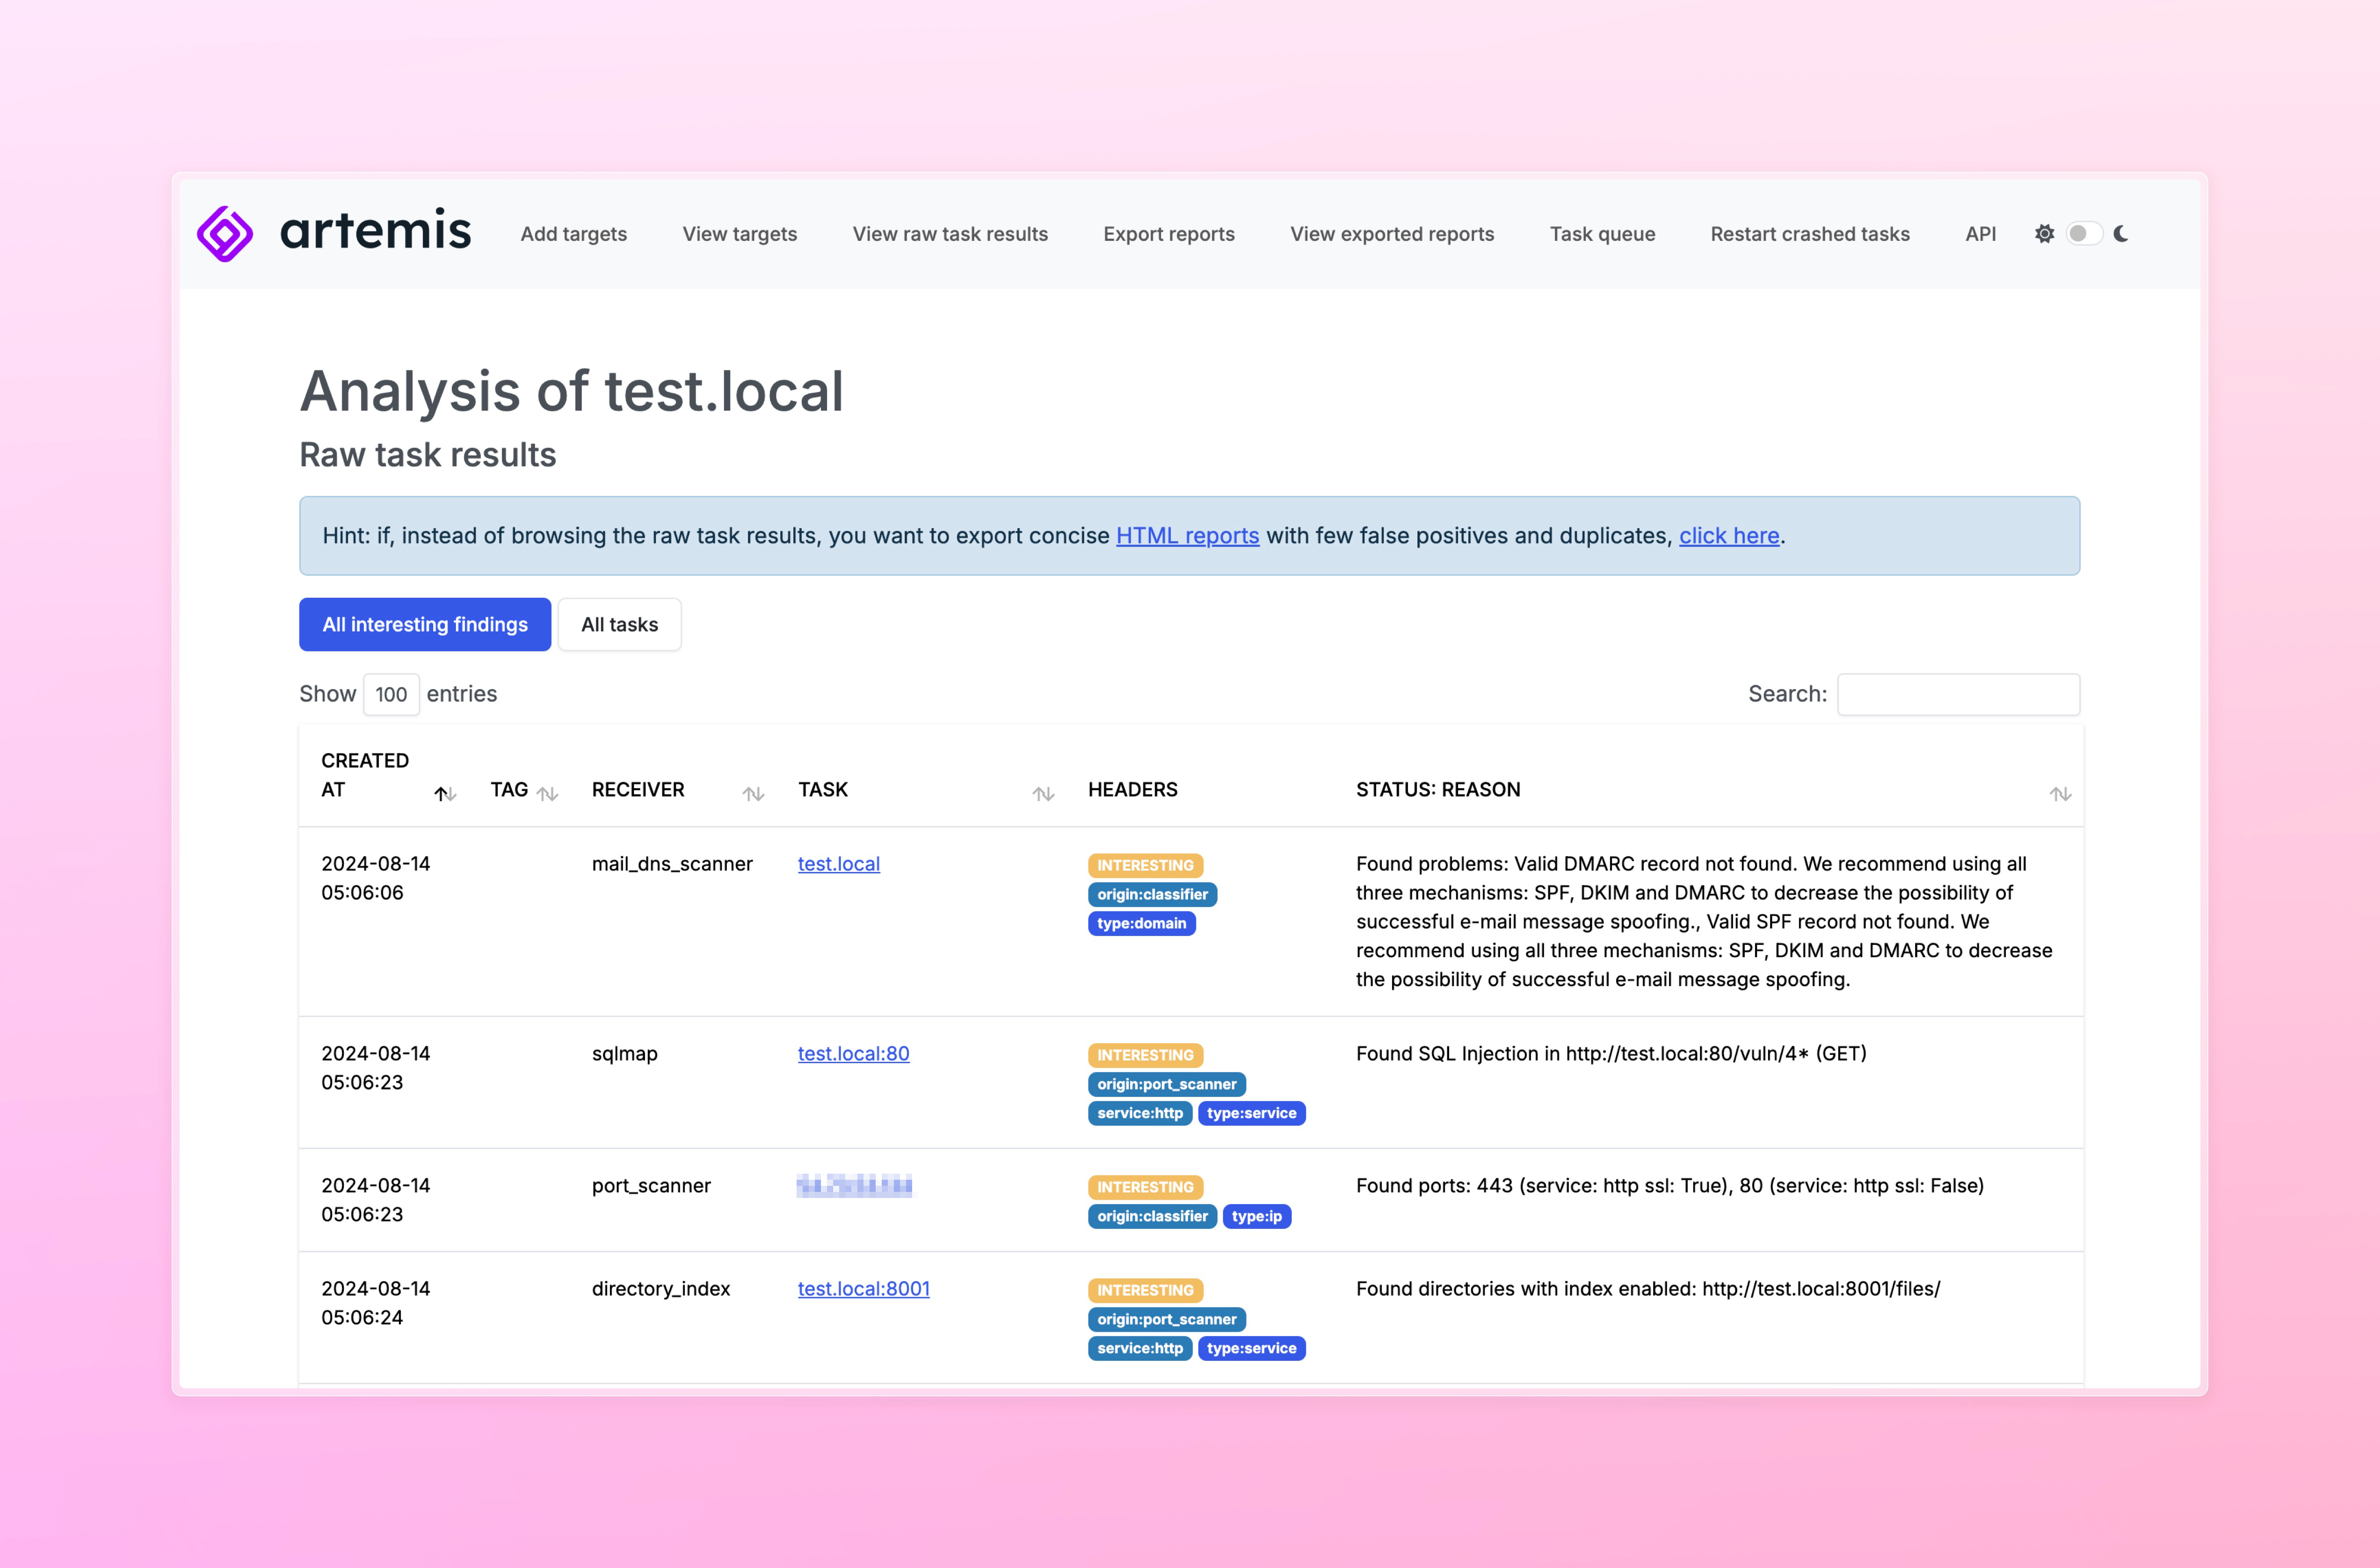 cert-polska/artemis
A modular vulnerability scanner with automatic report generation capabilities.
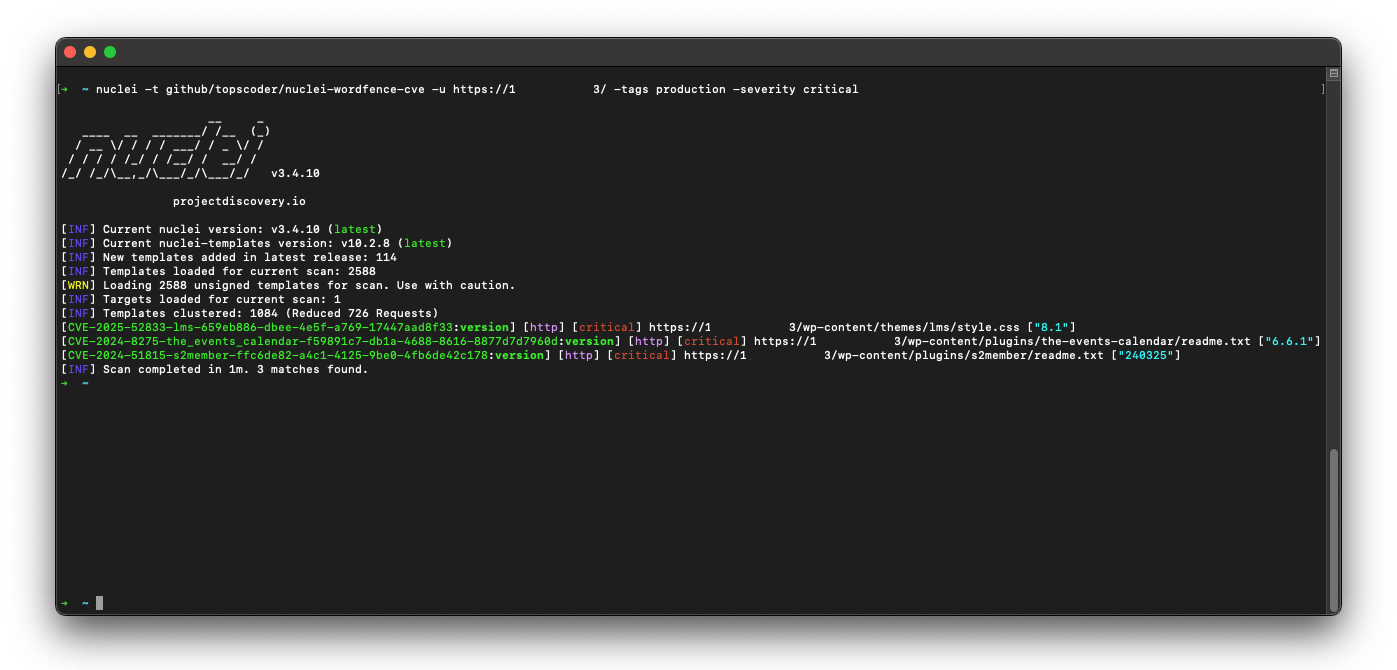 topscoder/nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
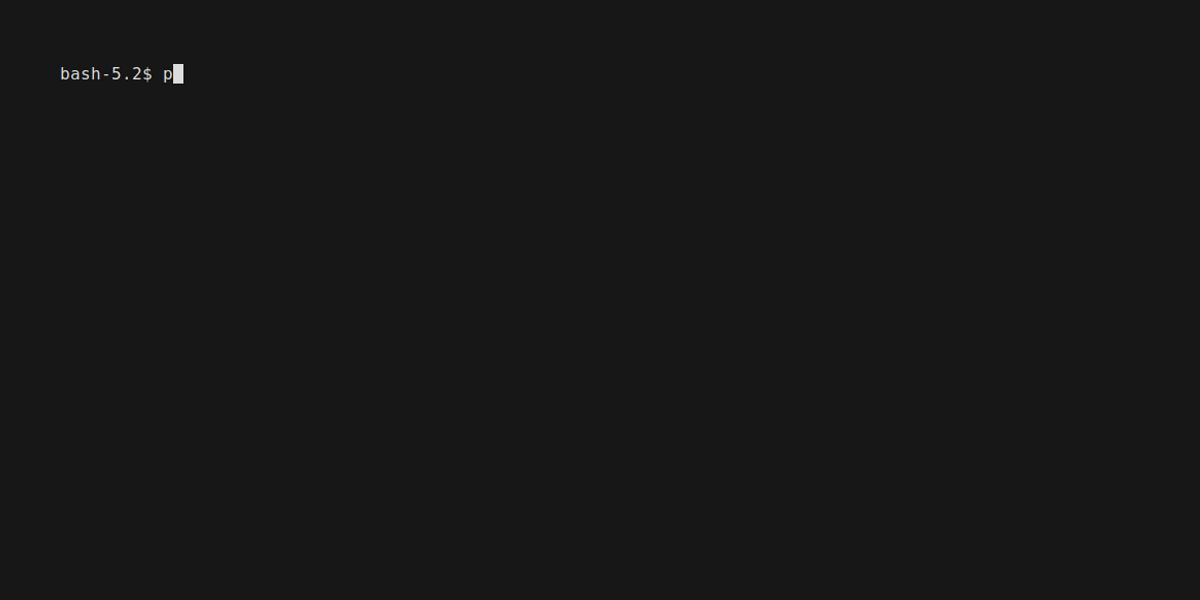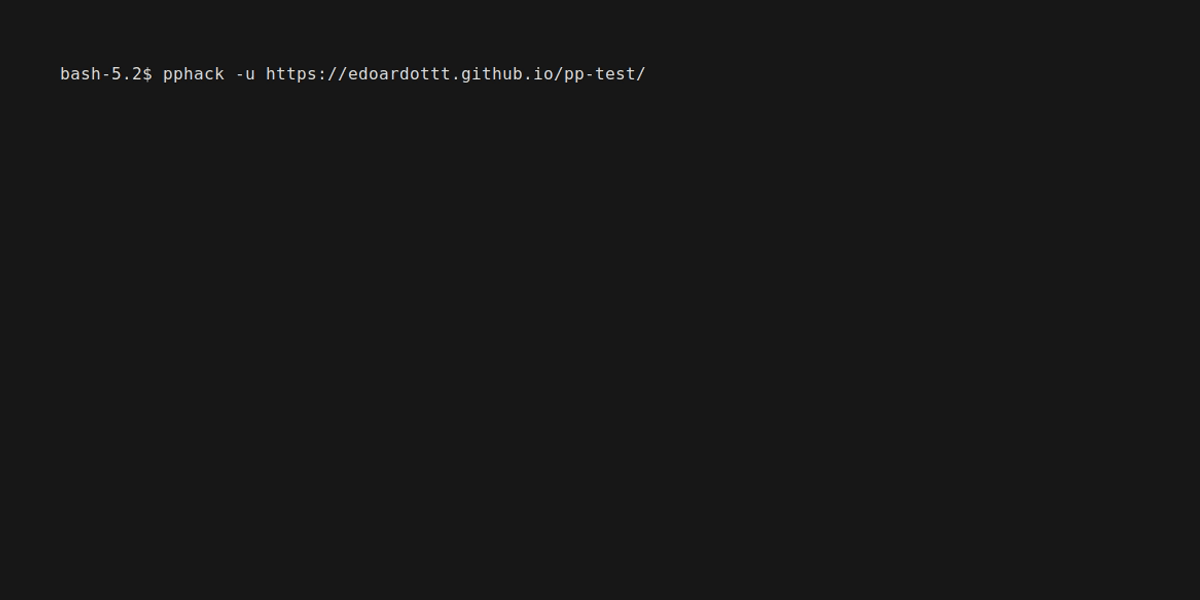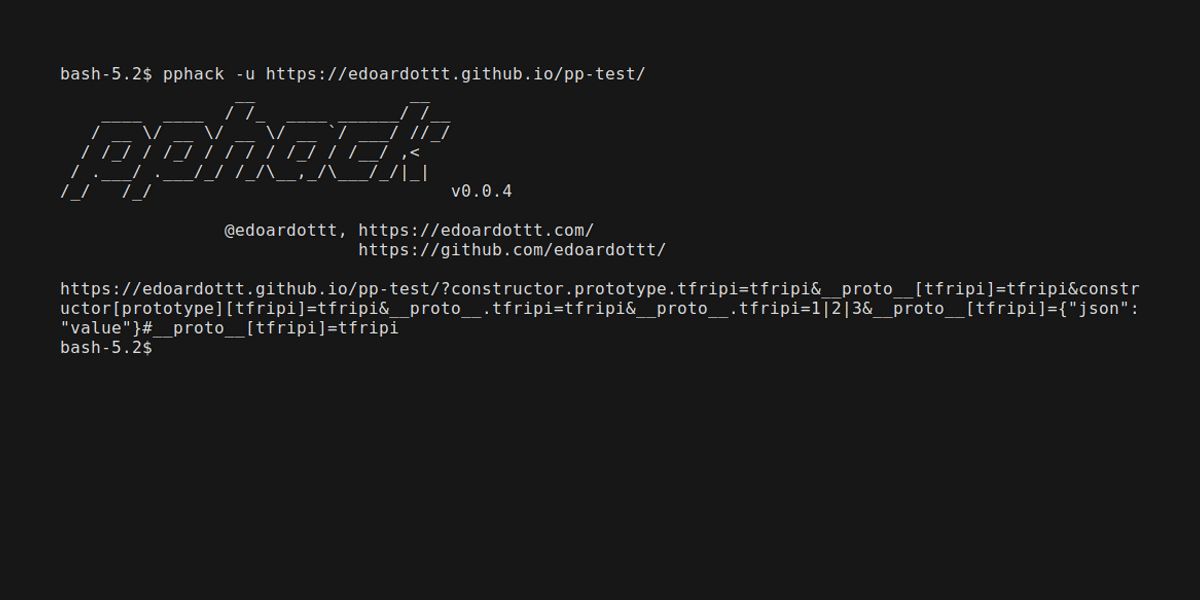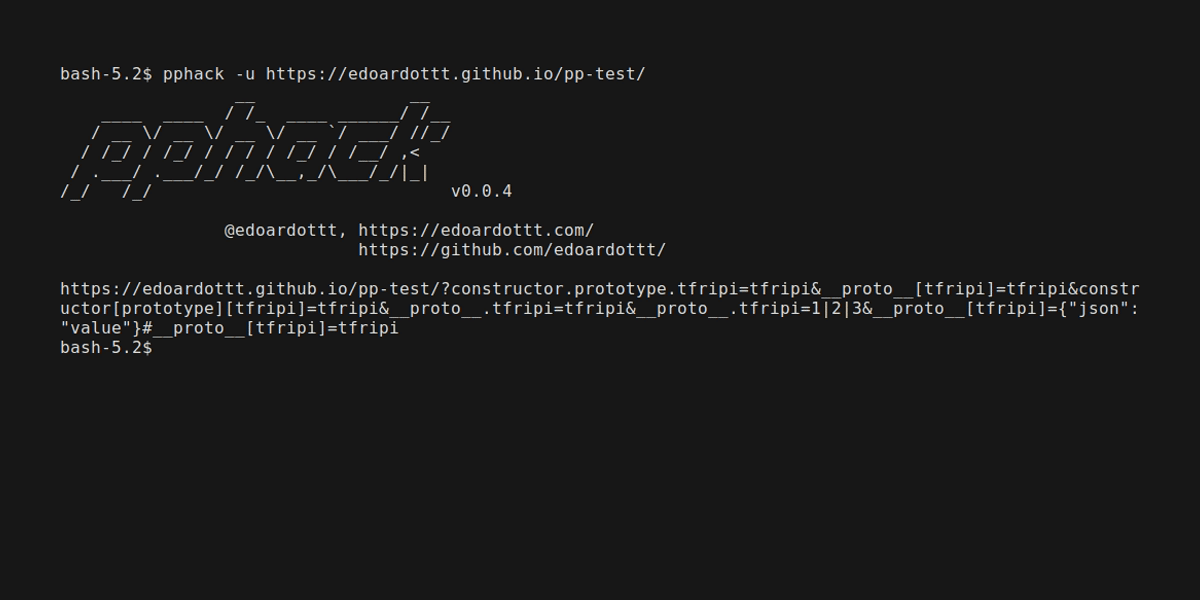 edoardottt/pphack
Advanced Client-Side Prototype Pollution Scanner