
burp-awesome-tls
 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
anti-botfingerprint-spoofingids-ips-evasion+3
1.9k
sleeyax/burp-awesome-tlsBurp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 xiaoqimikko/tomcat-check
查出 Spring Boot 内嵌 Tomcat 的真实版本(pom 里没有),并对每条 2026 年 CVE 同时给出 ASF 官方评级与 GitHub 评级、触发条件、以及这条会不会进 Dependabot 告警 CVE-2026-41293
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
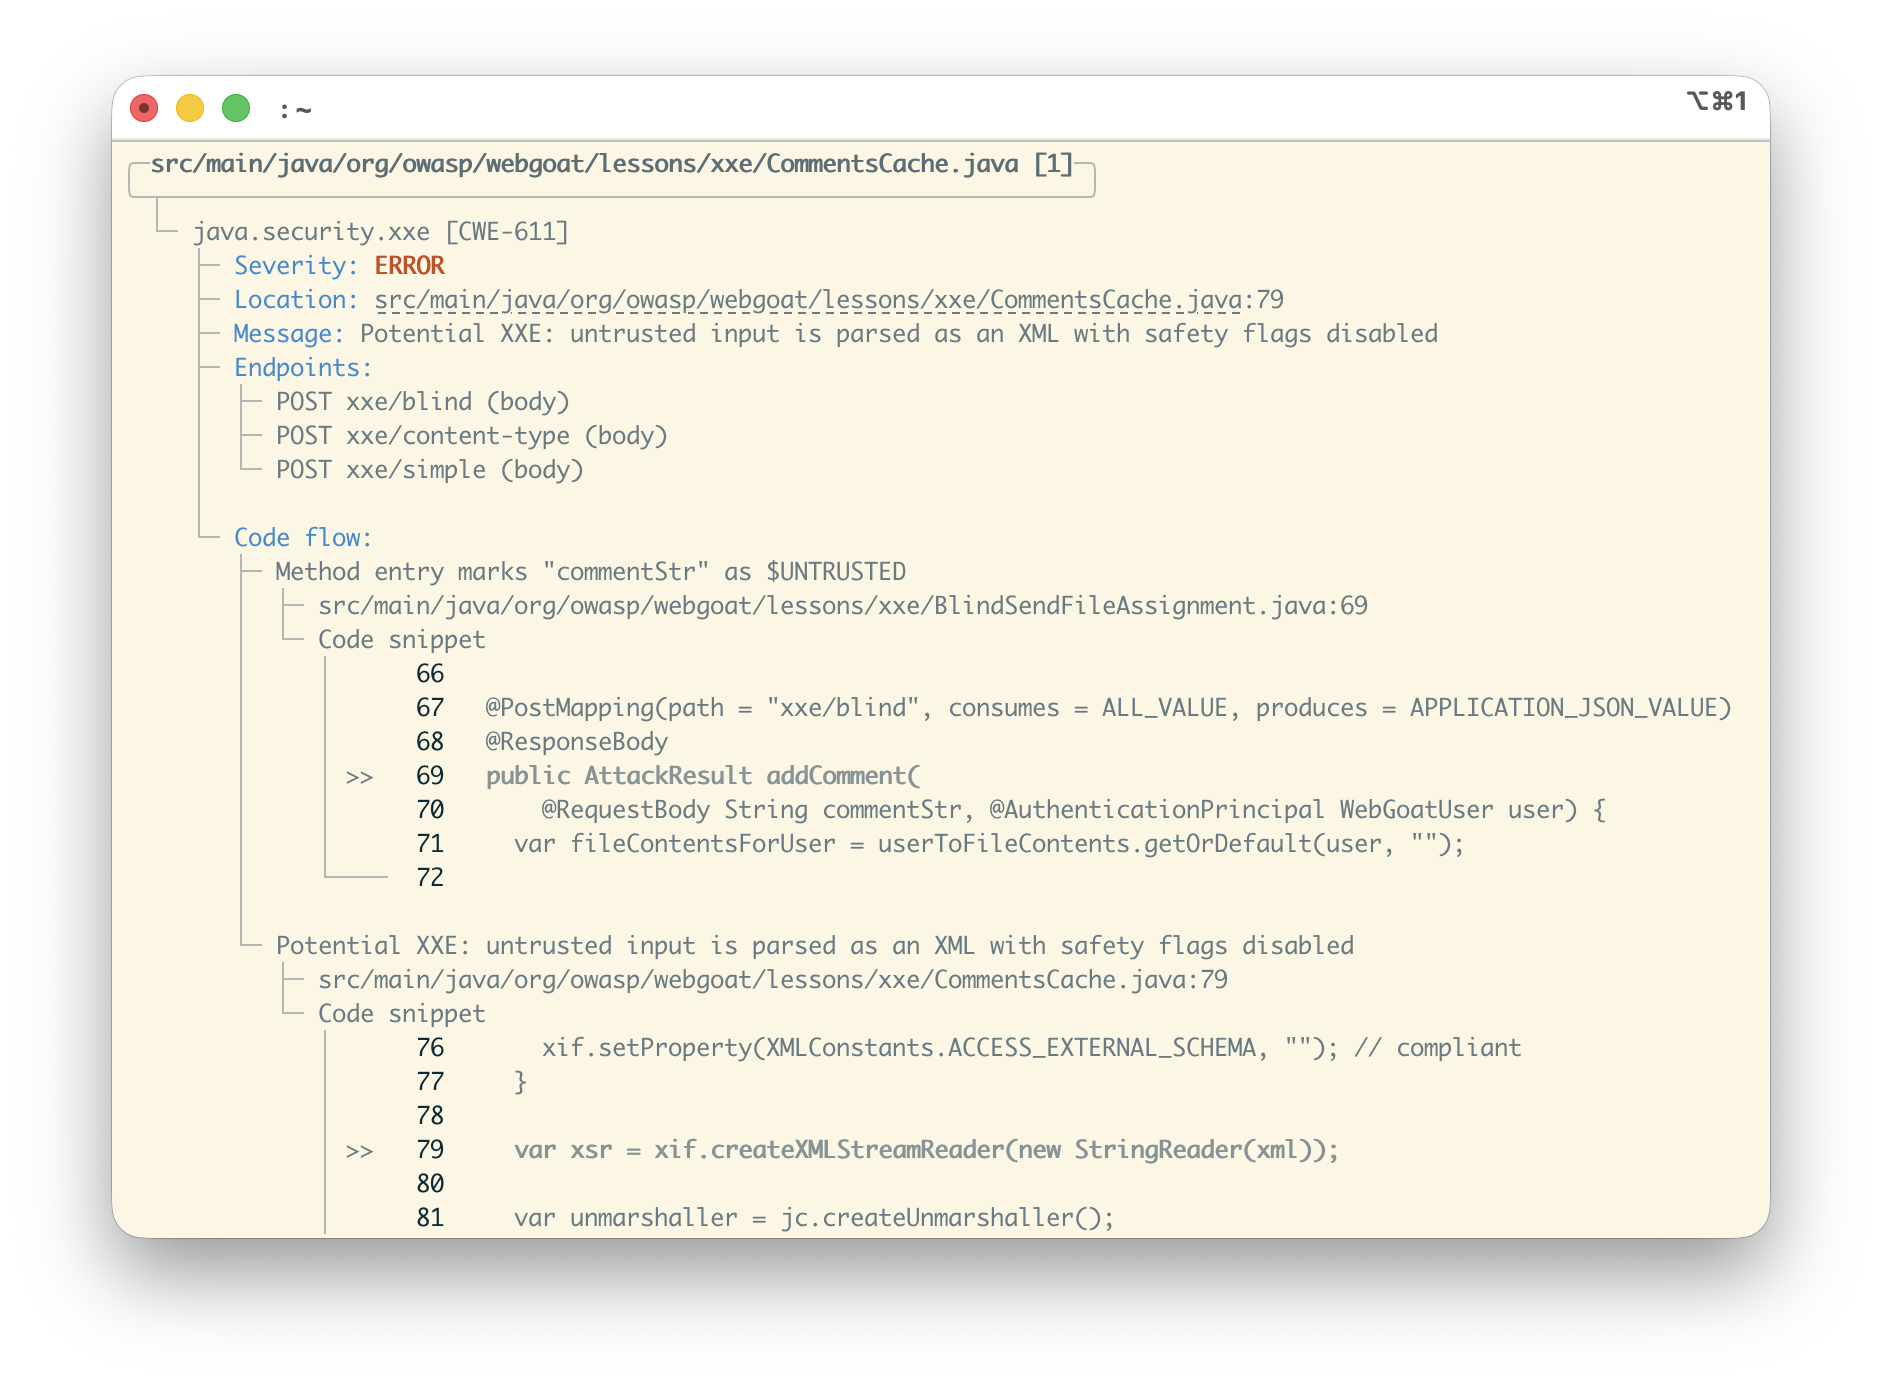 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
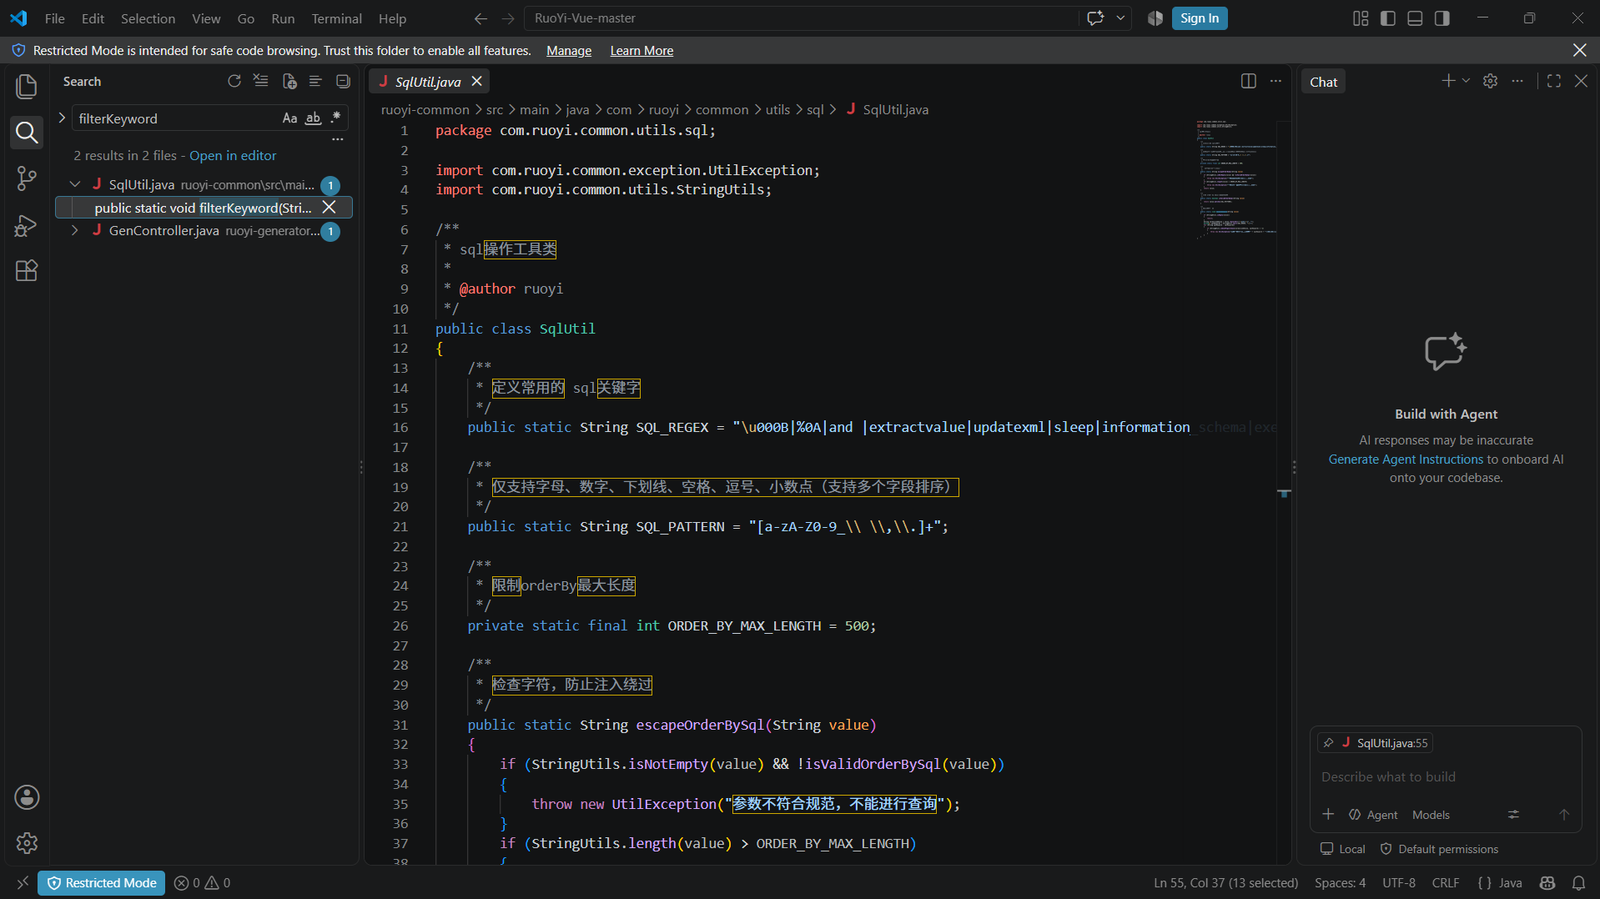 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 hoodoer/colonelclustered
A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 xiaoqimikko/tomcat85-check
CVE-2025-55752:Tomcat 8.5 已 EOL,终版 8.5.100。Apache 逐条声明「8.5 也受影响」的 2025 CVE 有 14 条,其中 10 条在 NVD 按 8.5.100 查不到。离线单 jar,读 conf/ 判断你到底中了哪几条。
 xiaoqimikko/tomcat-line-check
CVE-2026-24880: does Apache's upgrade advice actually apply to your Tomcat? Detects the fix by class presence, not version comparison. Covers…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 dinosn/log4j-4255
End-to-end Docker lab reproducing Apache log4j2 #4255 — FilteredObjectInputStream allowlist bypass via java.rmi.MarshalledObject (unfiltered…
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 cypherhippie/cve-2026-34486---unauthenticated-rce-via-java-deserialization
EncryptInterceptor fail-open bypass in Apache Tomcat Tribes clustering leading to unauthenticated RCE via Java deserialization.