
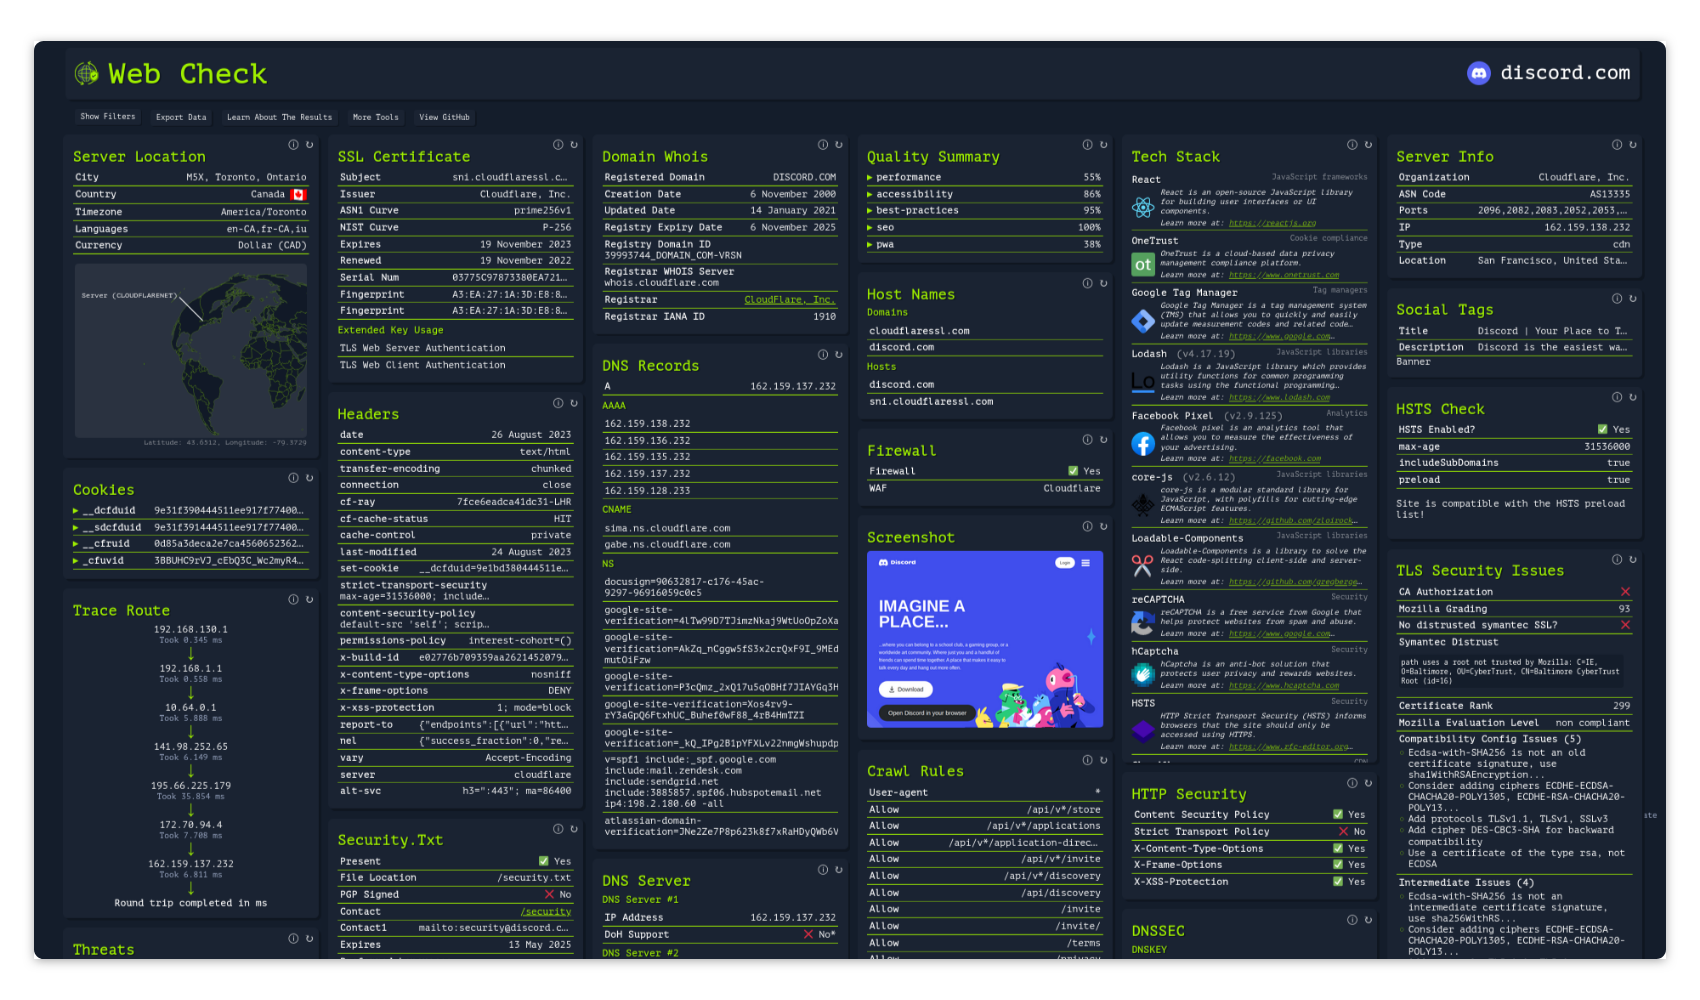
web-check
 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
dns-analysisemail-harvestinginformation-gathering+10
lissy93/web-check🕵️♂️ All-in-one OSINT tool for analysing any website
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
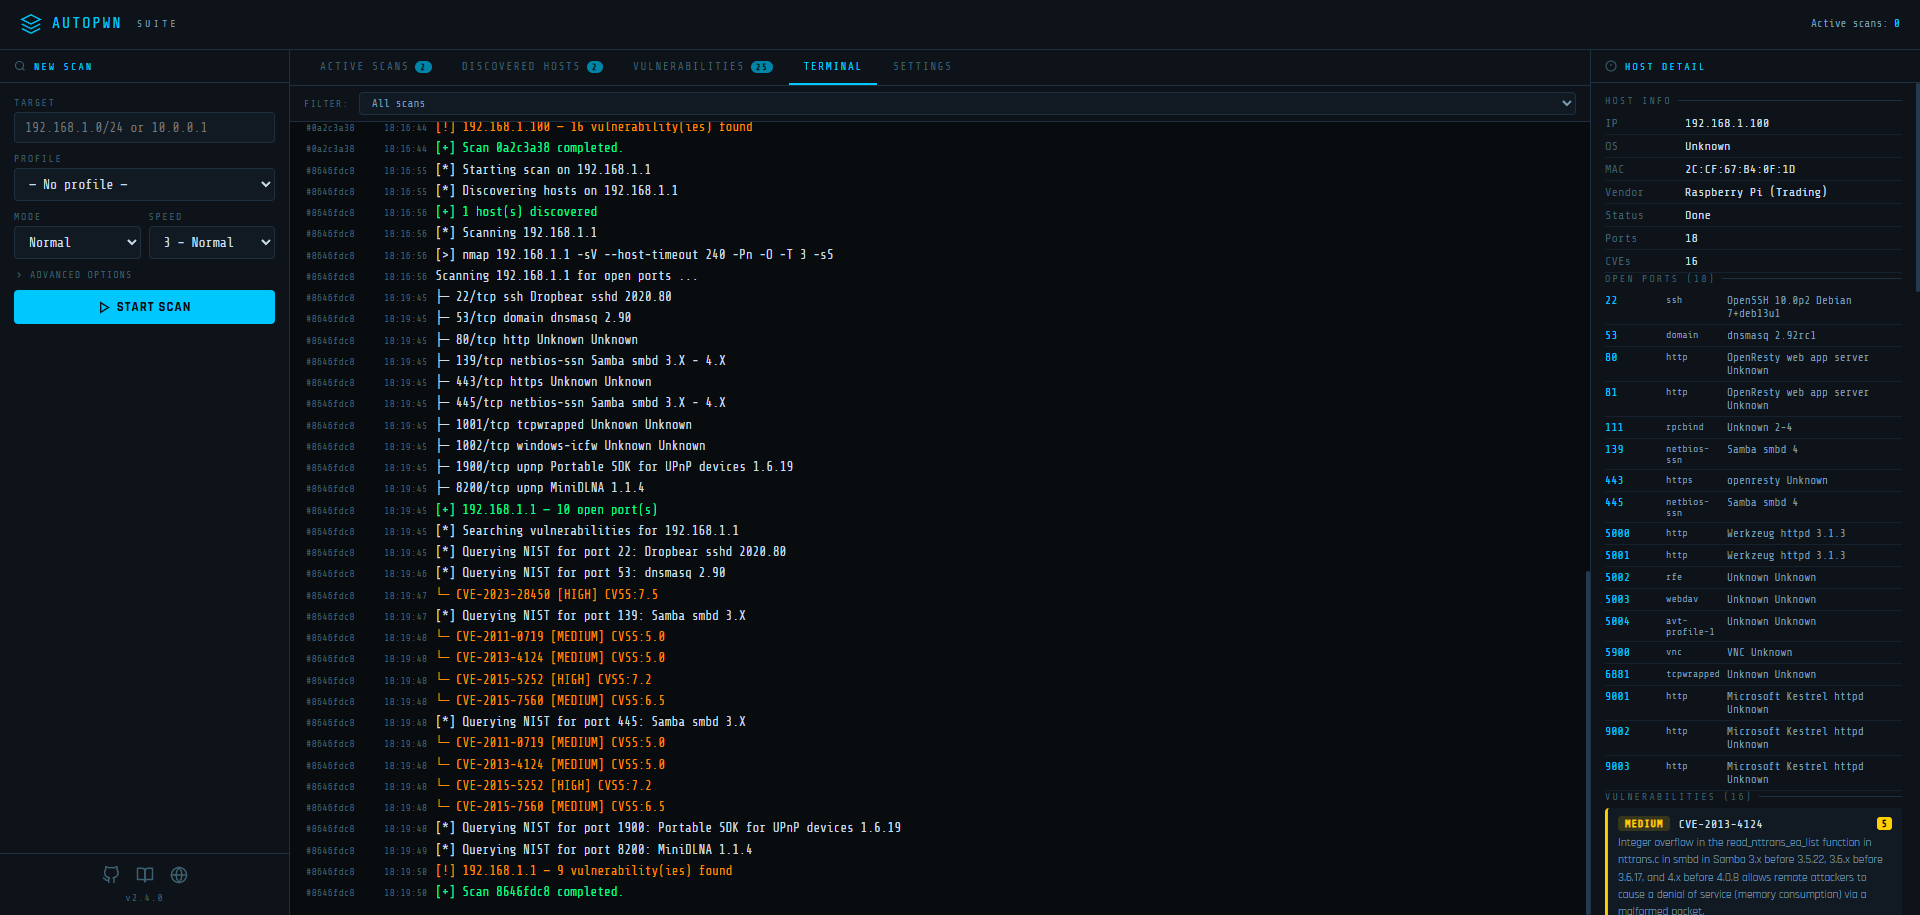 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 dgtlmoon/changedetection.io
Best and simplest tool for website change detection, web page monitoring, and website change alerts. Perfect for tracking content changes, price…
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 lutfifakee-project/cve-2026-87902
Proof-of-concept exploit for CVE-2026-87902, a WordPress Core pre-auth path traversal chaining LFI to remote code execution.
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 toanln-cov/cve-2026-76569
Reflected XSS via search GET Parameter in Phoca Download
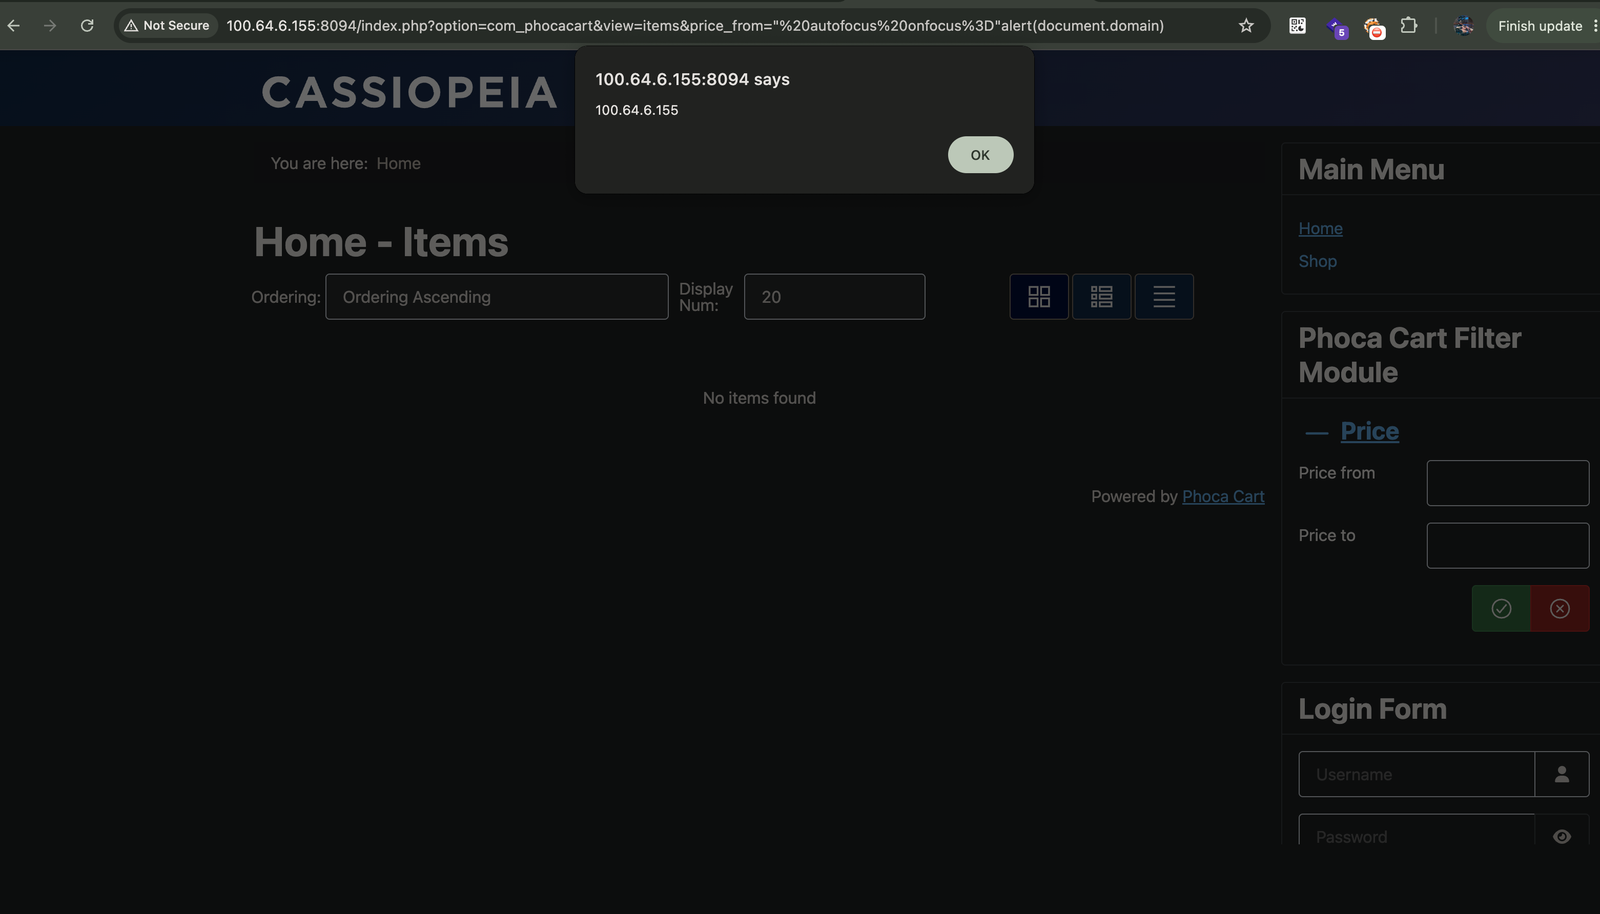 toanln-cov/cve-2026-76565
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 stamparm/dsxs
Damn Small XSS Scanner
 stamparm/dsss
Damn Small SQLi Scanner
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
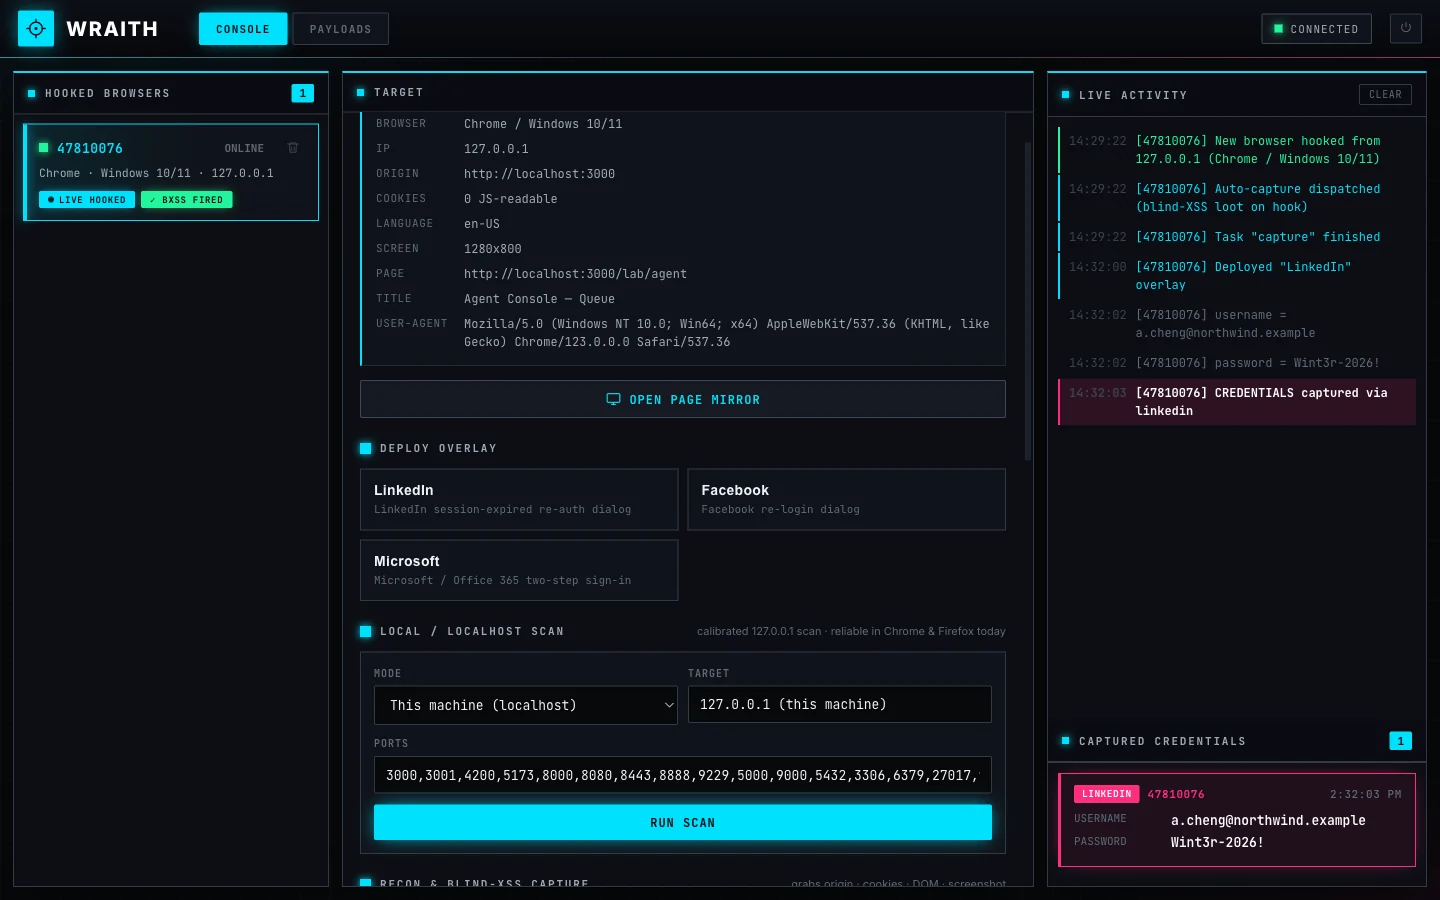 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 theopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8