

TWAPT
 moisestapia/twapt
Deploy your own lab of web application penetration testing with docker and docker-compose, webgoat, dvwap, bwapp and Juice Shop
container-securitydevsecopseducation+5
75
moisestapia/twaptDeploy your own lab of web application penetration testing with docker and docker-compose, webgoat, dvwap, bwapp and Juice Shop
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 narfindustries/http-garden
Differential testing framework for HTTP implementations
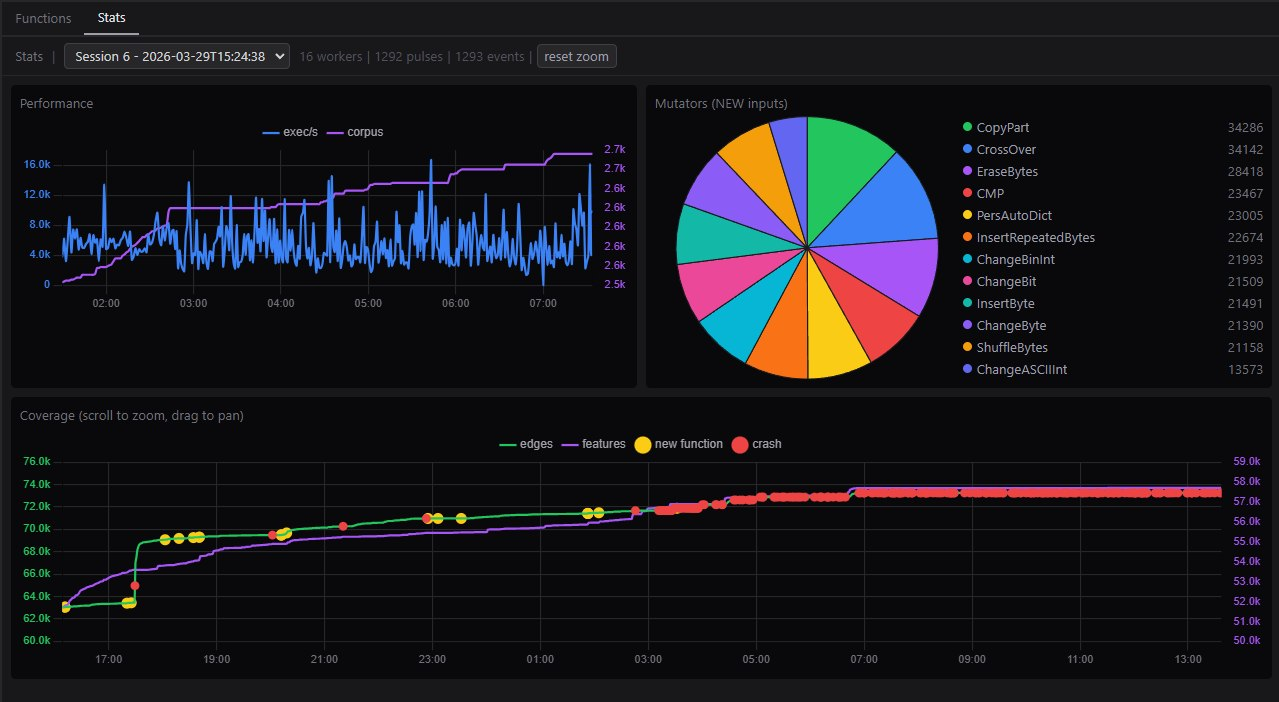 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 rocklambros/react2shell_hunter
AWS Organization-wide detection toolkit for CVE-2025-55182 & CVE-2025-66478 (React Server Components / Next.js RCE vulnerabilities)
 oscerd/cve-2026-46726
Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…
 oscerd/cve-2026-46592
Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…
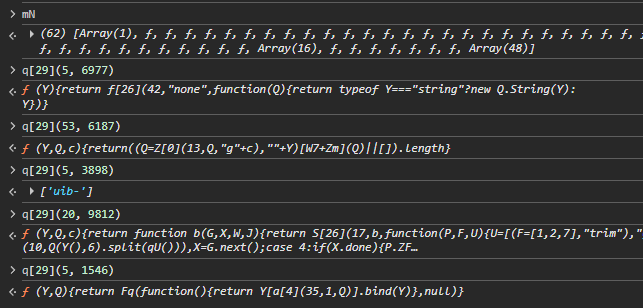 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA

 urbanadventurer/whatweb
Next generation web scanner
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings