

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
284 results
unKover preview

unKover

GitHubbrutelogic/unkover

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
api-security-testinginformation-gatheringpenetration-testing+7
109
5 days ago
gitea-hostmatcher-0000-ssrf preview

gitea-hostmatcher-0000-ssrf

GitHubabraxas/gitea-hostmatcher-0000-ssrf

Proof-of-concept lab demonstrating an authenticated SSRF in Gitea's hostmatcher allow-list, where a webhook to http://0.0.0.1 reaches loopback…
exploitationlabs-practicepenetration-testing+3
18 days ago
gitlab-webhook-0net-ssrf preview

gitlab-webhook-0net-ssrf

GitHubabraxas/gitlab-webhook-0net-ssrf

Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…
exploitationlabs-practicepenetration-testing+3
18 days ago
CVE-2026-14281-check preview

CVE-2026-14281-check

GitHubabatsakidis/cve-2026-14281-check

A Windows-friendly, non-destructive Python checker for detecting WordPress installations potentially affected by CVE-2026-14281.

defensive-toolsinformation-gatheringreconnaissance+4
21 days ago
bifrost preview

bifrost

GitHubbifrost-proxy/bifrost

High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…


api-security-testingnetwork-securitypacket-sniffing-analysis+6
1634 days ago
wordpress-cve-scanner preview

wordpress-cve-scanner

GitLabvaltersit/wordpress-cve-scanner

Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
configuration-auditingdevsecopsvulnerability-analysis+3
20 days ago
waybend preview

waybend

GitHubprinciplebreach/waybend

Self-hosted SSRF redirect, payload, callback, and DNS workbench
command-and-controldns-analysisinformation-gathering+9
51 month ago
EXPLOIT-CVE-2026-87902 preview

EXPLOIT-CVE-2026-87902

GitHubjoaovicdev/exploit-cve-2026-87902

Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
container-securityeducationexploitation+6
24 days ago
cve-2026-87902 preview

cve-2026-87902

GitHubzyphorixofficialmain-lab/cve-2026-87902

Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
exploitationinformation-gatheringpayload-development+6
25 days ago
CVE-2026-87902-A-working-PoC-for-WordPress-s-critical-path-traversal preview

CVE-2026-87902-A-working-PoC-for-WordPress-s-critical-path-traversal

GitHubrabakuku/cve-2026-87902-a-working-poc-for-wordpress-s-critical-path-traversal

Reference notes and mitigation configs for CVE-2026-87902, a WordPress Core unauthenticated path traversal and LFI flaw chainable to RCE, with Nginx,…
defensive-toolseducationpapers-research+3
26 days ago
Web-App-PenTesting preview

Web-App-PenTesting

GitHubsarthak4126/web-app-pentesting

Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
227 days ago
CVE-2019-9053 preview

CVE-2019-9053

GitHub4nner/cve-2019-9053

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…

exploitationpassword-crackingpenetration-testing+3
113 years ago
XXStrike preview

XXStrike

GitHubanonmoty/xxstrike

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
dynamic-code-analysisfuzzingpenetration-testing+5
41 month ago
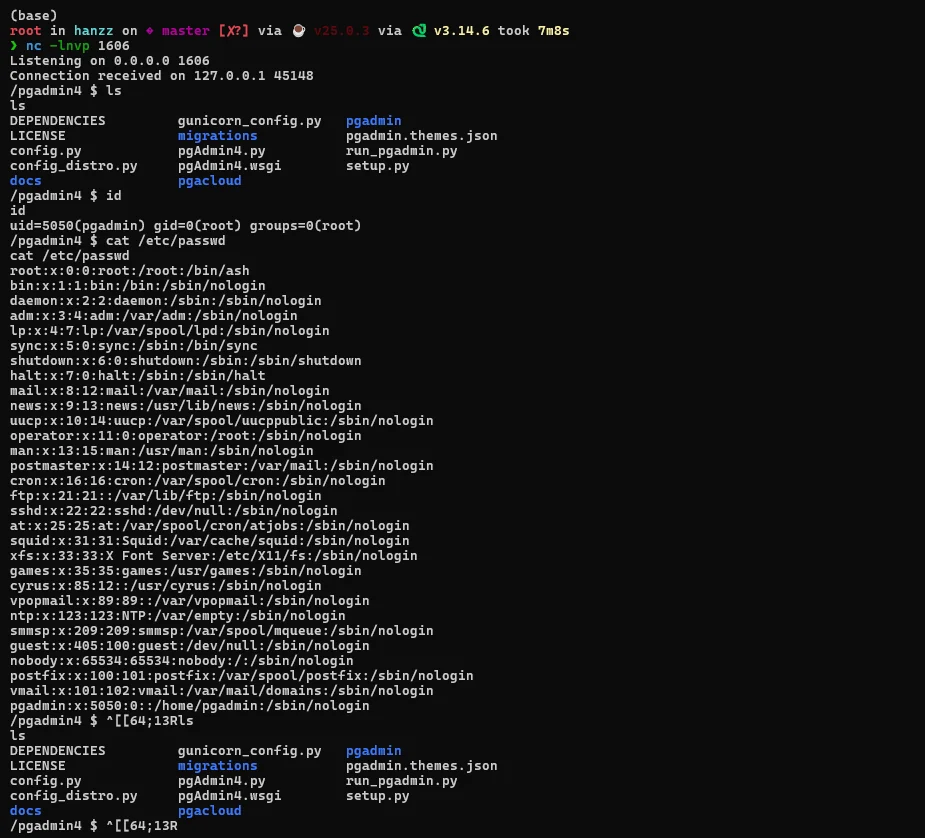
CVE-2024-2044 preview

CVE-2024-2044

GitHubhanzzly/cve-2024-2044

Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
exploitationpayload-developmentpenetration-testing+5
11 month ago
tomcat-cve-2025-24813-lab preview

tomcat-cve-2025-24813-lab

GitHubmega-starmie/tomcat-cve-2025-24813-lab

Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.

educationexploitationlabs-practice+4
1 month ago
linux-entra-sso-PoC preview

linux-entra-sso-PoC

GitHubsqueeze440/linux-entra-sso-poc

PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
authenticationexploitationinformation-gathering+5
1 month ago
CVE-2026-82222 preview

CVE-2026-82222

GitHubghostlyrootb2h/cve-2026-82222

Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
command-and-controlexploitationinformation-gathering+5
1 month ago
cve-2026-75650-magento-validation-lab preview

cve-2026-75650-magento-validation-lab

GitHubdinosn/cve-2026-75650-magento-validation-lab

Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.

curated-resourceseducationexploitation+3
61 month ago
Previous12…16Next