

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
97 results
ColonelClustered preview

ColonelClustered

GitHubhoodoer/colonelclustered

A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
fuzzingmachine-learningpenetration-testing+5
12
1 month ago
CVE-2026-0603 preview

CVE-2026-0603

GitHubyym8538/cve-2026-0603

Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
database-securityeducationexploitation+4
12 months ago
Weblogic_CVE-2020-14645 preview

Weblogic_CVE-2020-14645

GitHubjlvsjp/weblogic_cve-2020-14645

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

exploitationpayload-developmentpenetration-testing+4
6 years ago
JavaSecLab preview

JavaSecLab

GitHubwhgojp/javaseclab

Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
code-analysisctfdevsecops+6
8844 months ago
CVE-2024-57521-RuoYi-SQLi preview

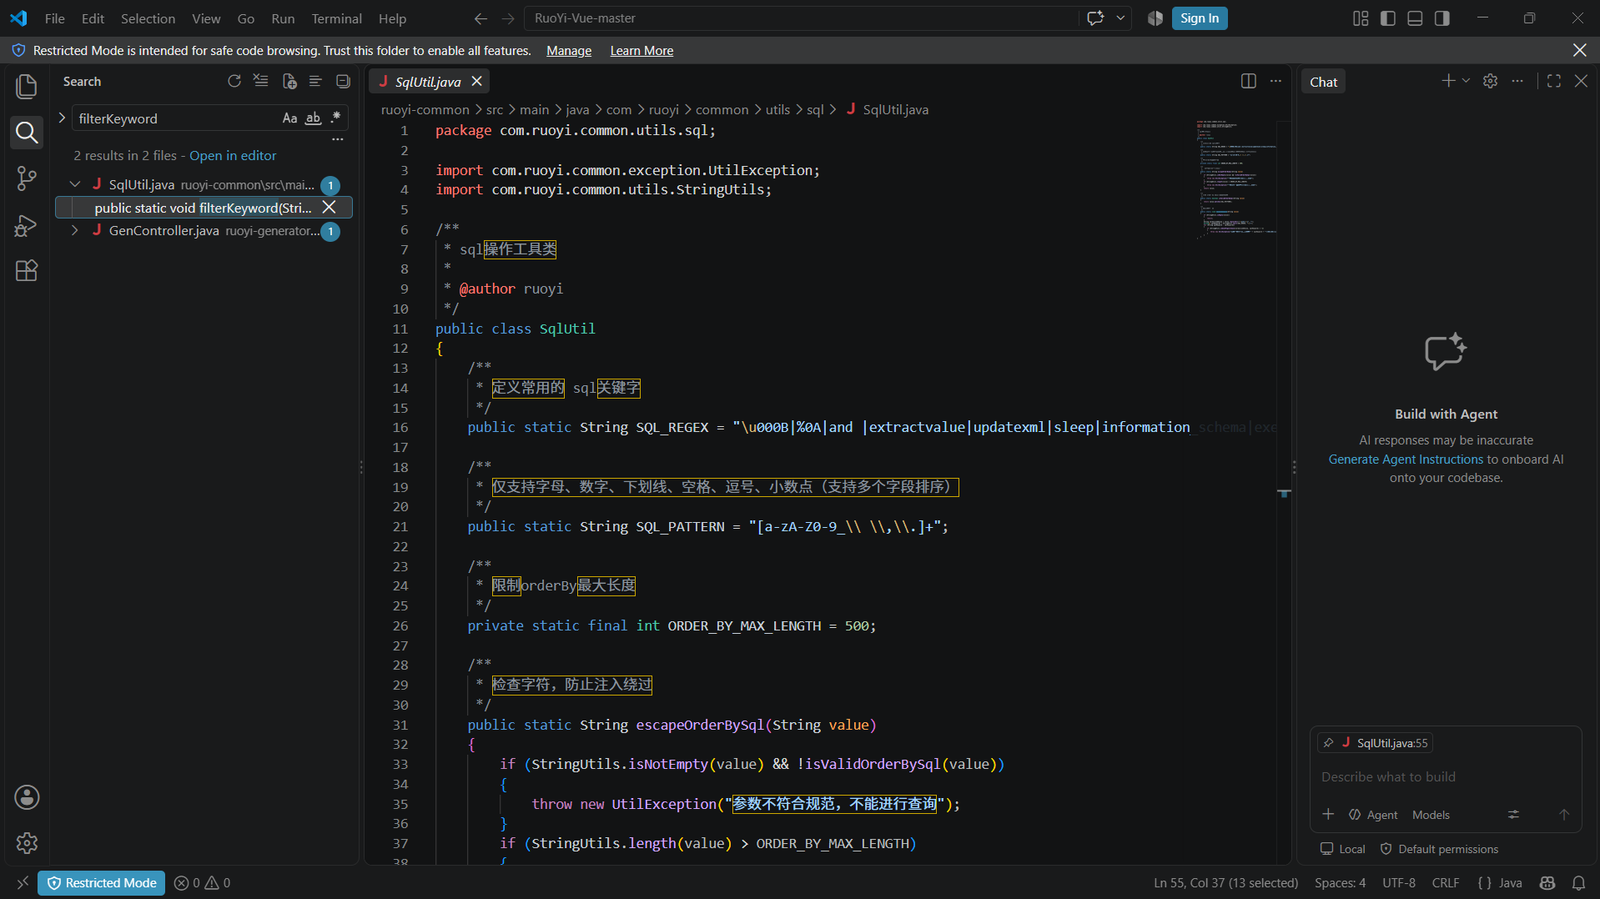
CVE-2024-57521-RuoYi-SQLi

GitHubxs2024770/cve-2024-57521-ruoyi-sqli

Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
educationexploitationpapers-research+4
23 days ago
netty-resolver-dns-check preview

netty-resolver-dns-check

GitHubxiaoqimikko/netty-resolver-dns-check

Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…

configuration-auditingdefensive-toolsdns-analysis+5
1 month ago
jetty-line-check preview

jetty-line-check

GitHubxiaoqimikko/jetty-line-check

CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
configuration-auditingdefensive-toolsstatic-analysis+4
1 month ago
netty-http-check preview

netty-http-check

GitHubxiaoqimikko/netty-http-check

Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
configuration-auditingdevsecopsstatic-analysis+3
1 month ago
struts2-tool preview

struts2-tool

GitHubgu-007/struts2-tool

Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
command-and-controlexploitationpayload-development+5
11 month ago
tomcat85-check preview

tomcat85-check

GitHubxiaoqimikko/tomcat85-check

CVE-2025-55752:Tomcat 8.5 已 EOL,终版 8.5.100。Apache 逐条声明「8.5 也受影响」的 2025 CVE 有 14 条,其中 10 条在 NVD 按 8.5.100 查不到。离线单 jar,读 conf/ 判断你到底中了哪几条。
cloud-infrastructure-securityconfiguration-auditingdevsecops+3
1 month ago
tomcat-line-check preview

tomcat-line-check

GitHubxiaoqimikko/tomcat-line-check

CVE-2026-24880: does Apache's upgrade advice actually apply to your Tomcat? Detects the fix by class presence, not version comparison. Covers…
configuration-auditingsupply-chain-securityvulnerability-scanners+1
1 month ago
log4j-4255 preview

log4j-4255

GitHubdinosn/log4j-4255

End-to-end Docker lab reproducing Apache log4j2 #4255 — FilteredObjectInputStream allowlist bypass via java.rmi.MarshalledObject (unfiltered…
binary-exploitationeducationexploitation+2
281 month ago
log4shell-honeypot preview

log4shell-honeypot

GitHubvulnerable-apps/log4shell-honeypot

Java application vulnerable to the CVE-2021-44228 (a.k.a log4shell) vulnerability
vulnerability-analysisweb-security
4 years ago
CVE-2026-33701-Unsafe-Deserialization-in-OpenTelemetry-Java-Agent-RMI-Instrumentation preview

CVE-2026-33701-Unsafe-Deserialization-in-OpenTelemetry-Java-Agent-RMI-Instrumentation

GitHubpl4tyz/cve-2026-33701-unsafe-deserialization-in-opentelemetry-java-agent-rmi-instrumentation

Technical analysis of CVE-2026-33701, an unsafe deserialization vulnerability in OpenTelemetry Java Agent RMI instrumentation, including exploit…
educationexploitationvulnerability-analysis+1
6 months ago
CVE-2026-22679 preview

CVE-2026-22679

GitHubkeraattin/cve-2026-22679

Unauthenticated RCE exploit and detection scanner for Weaver E-cology, targeting the dubboApi debug endpoint. Includes PoC, Nmap NSE script, and…
exploitationpenetration-testingreconnaissance+3
56 months ago
log4j preview

log4j

GitHubhassaanahmad813/log4j

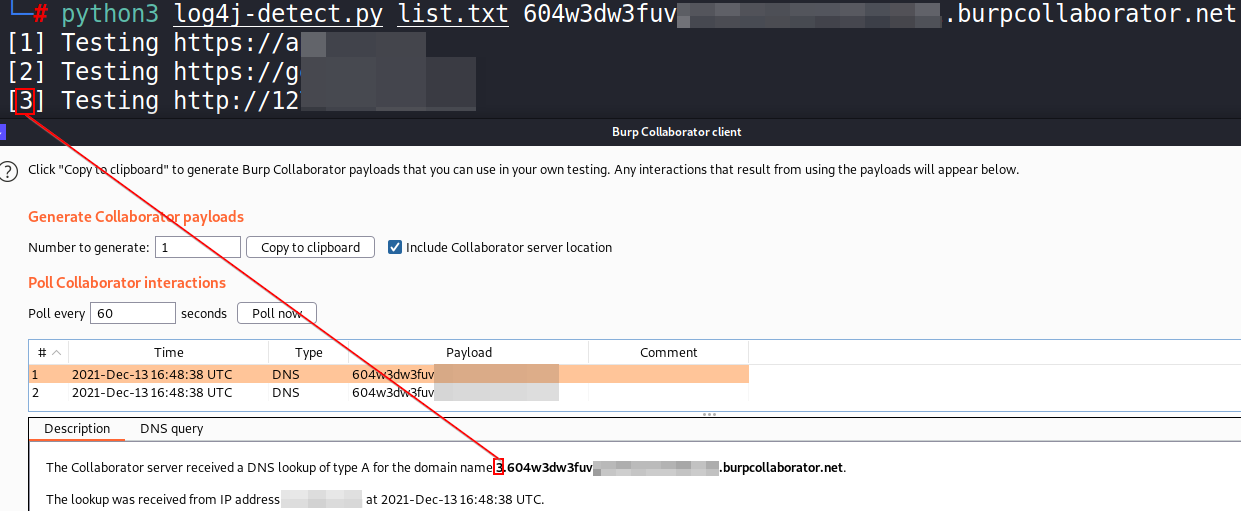
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
dns-analysisexploitationinformation-gathering+2
4 years ago
CVE-2021-31805-POC preview

CVE-2021-31805-POC

GitHubjordanandjohn/cve-2021-31805-poc

Apache Struts2 S2-062(CVE-2021-31805)远程代码执行批量检测(无利用)
exploitationpenetration-testingvulnerability-analysis+2
14 years ago
CVE-2026-34486---unauthenticated-RCE-via-Java-deserialization preview

CVE-2026-34486---unauthenticated-RCE-via-Java-deserialization

GitHubcypherhippie/cve-2026-34486---unauthenticated-rce-via-java-deserialization

EncryptInterceptor fail-open bypass in Apache Tomcat Tribes clustering leading to unauthenticated RCE via Java deserialization.

exploitationpayload-generationpenetration-testing+2
2 months ago
Previous123456Next