w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
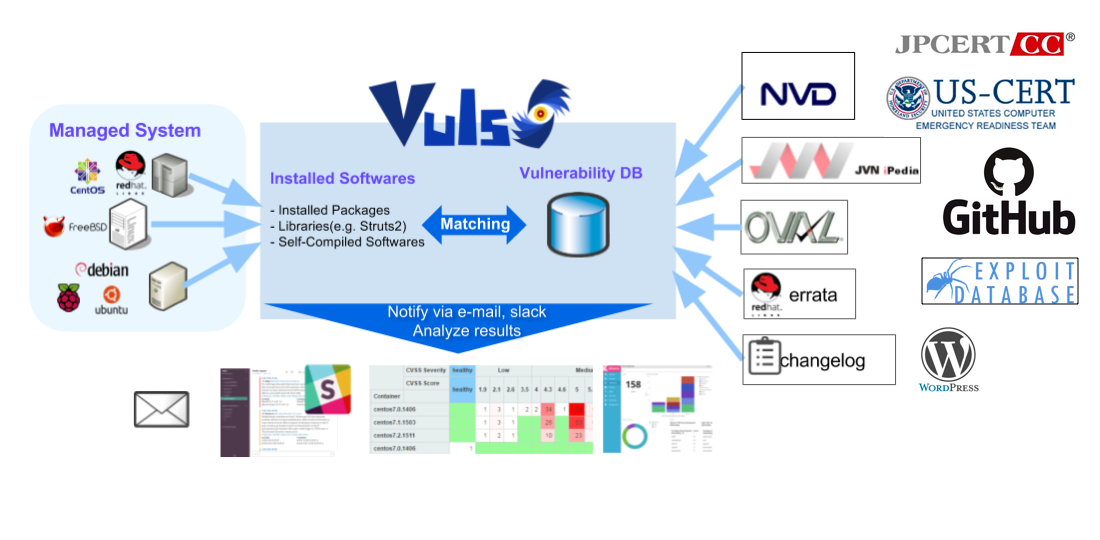 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
 ixsly/cve-2022-41401
Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…