reverse-engineering-browser

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

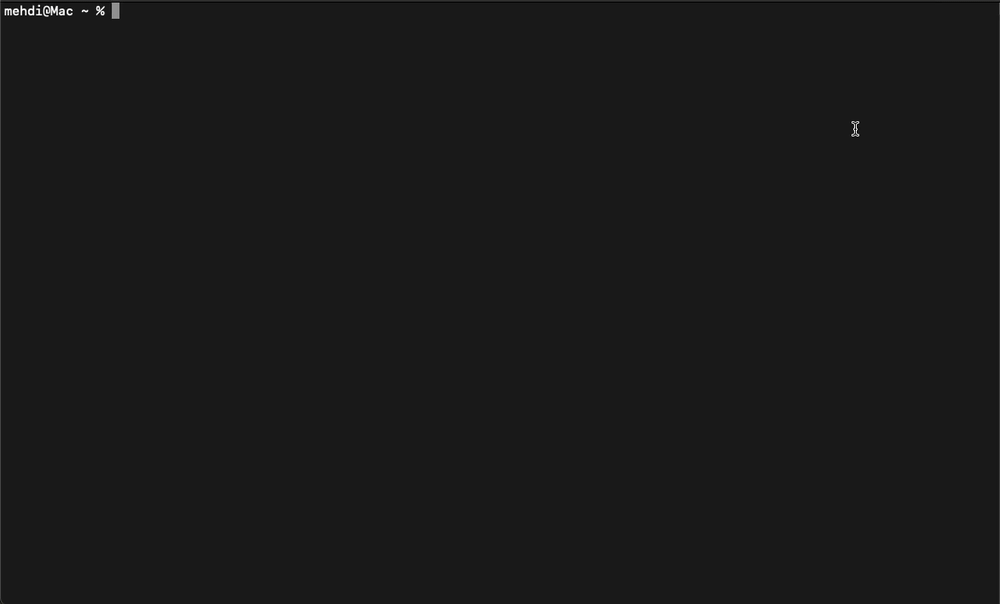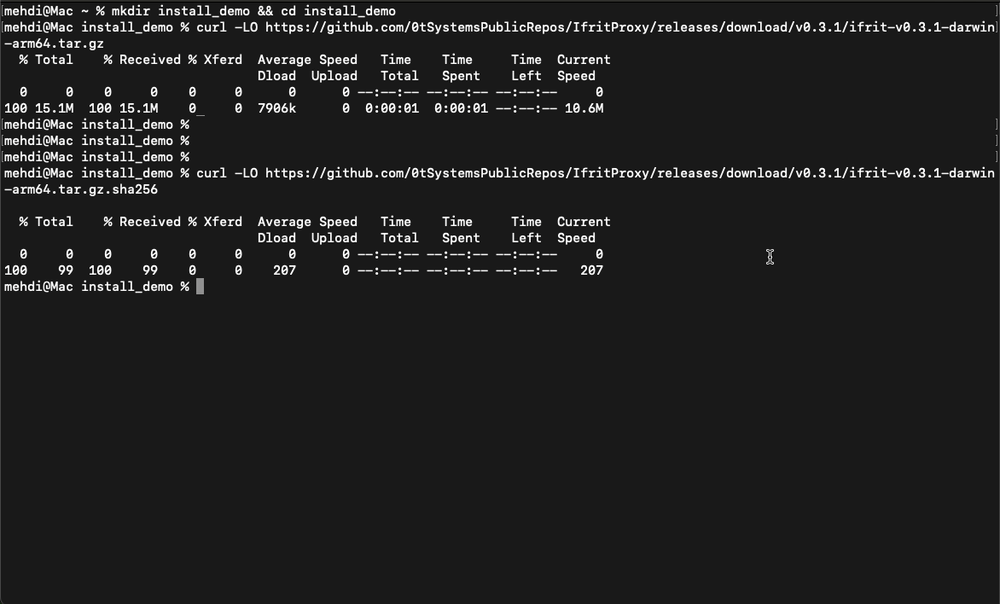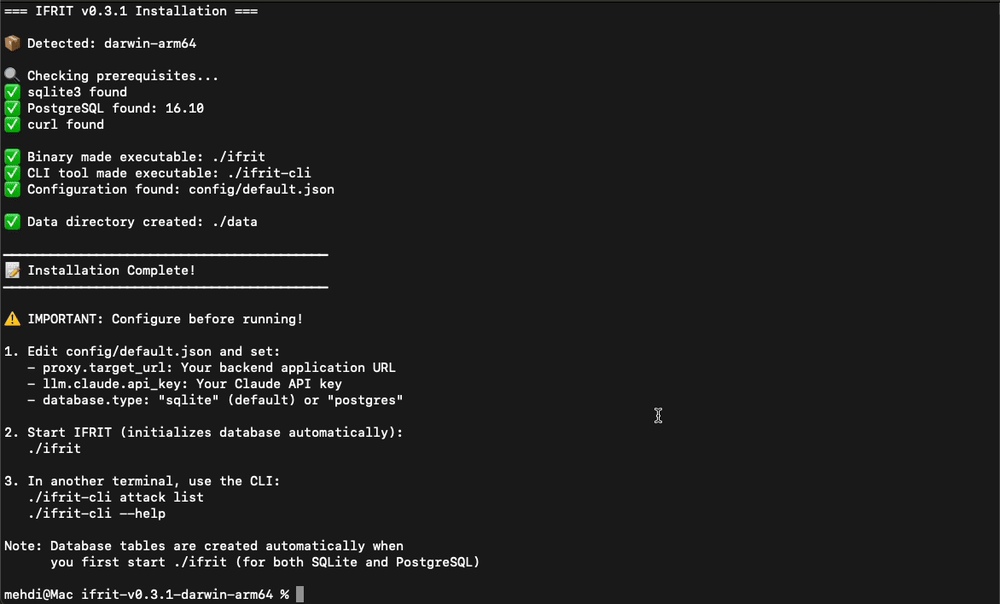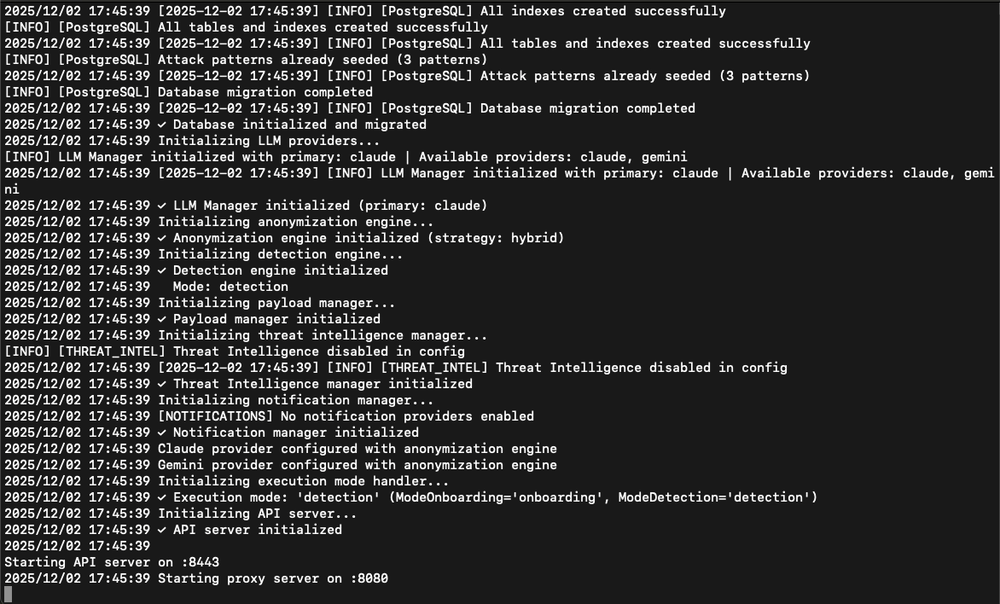
IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…

HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks

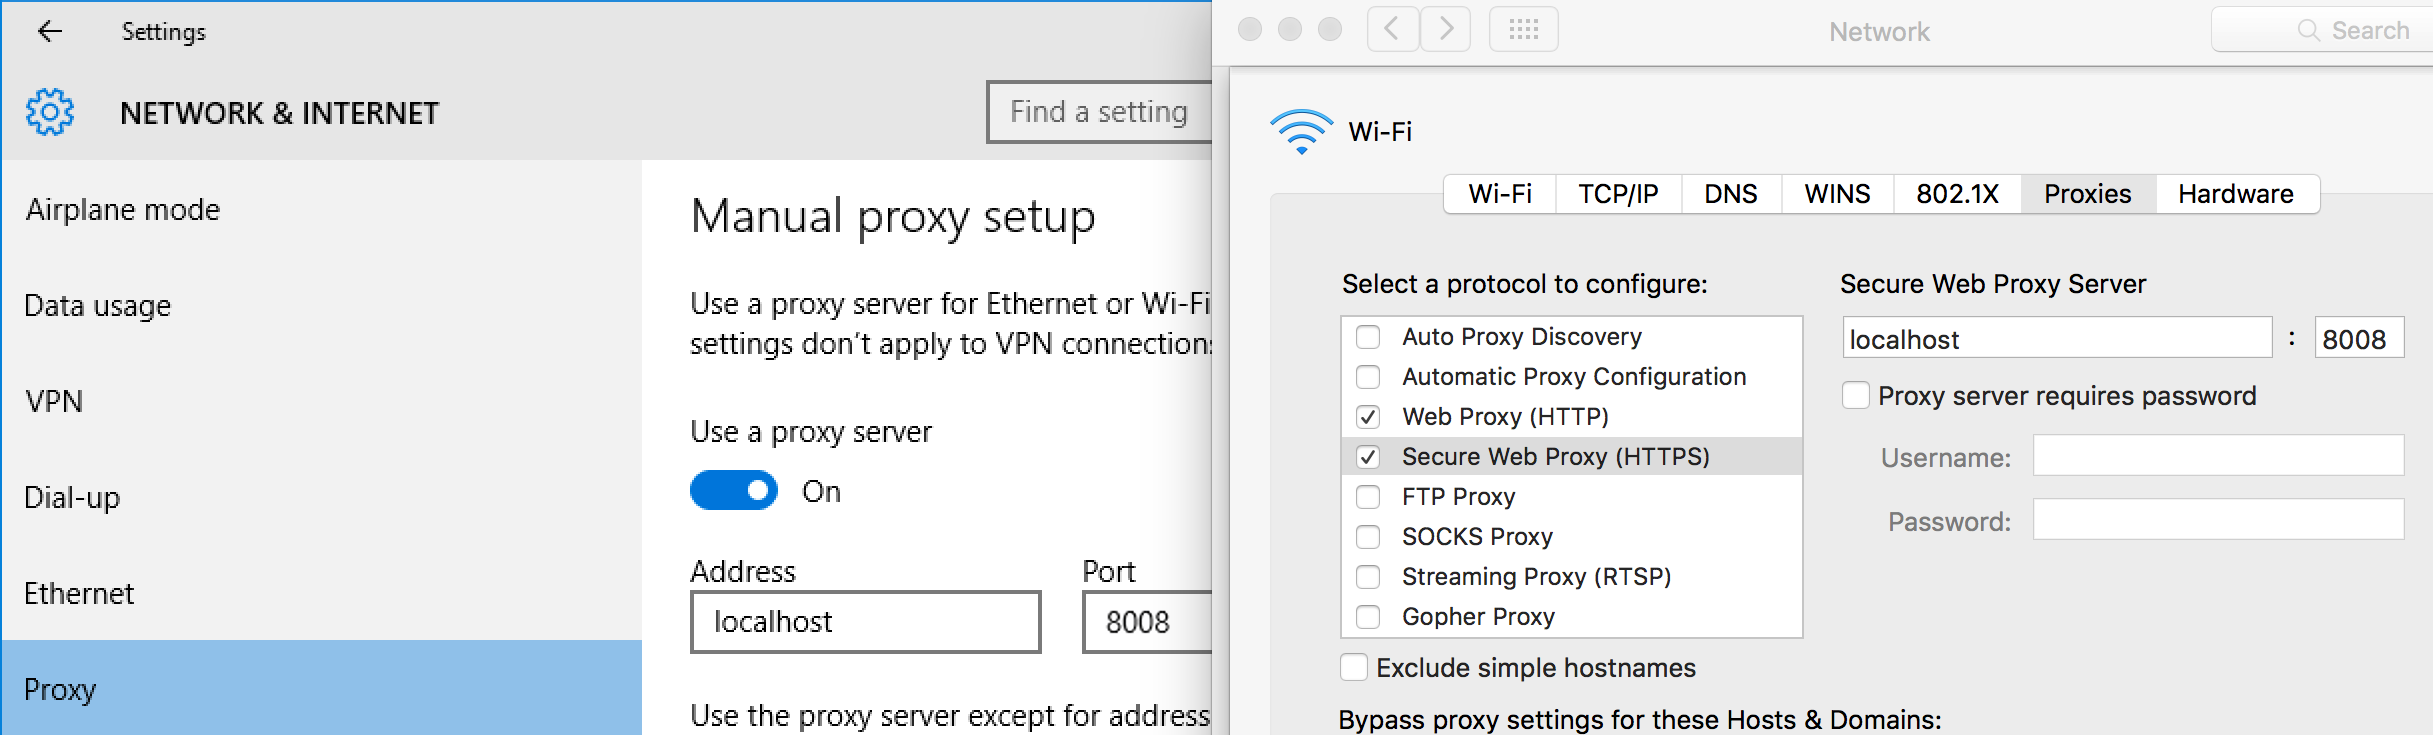
HTTP/HTTPS proxy in a single python script

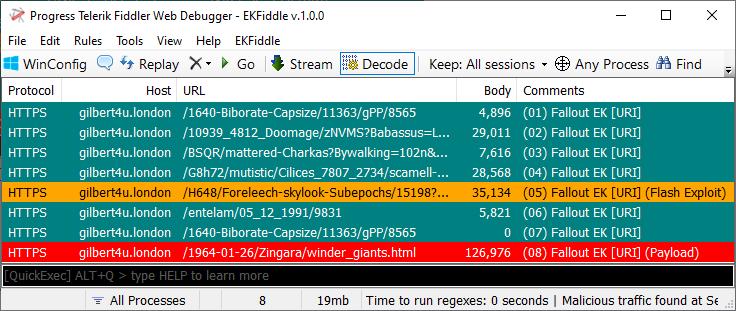
Your Swiss Army knife to analyze malicious web traffic based on the popular Fiddler web debugger.

Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML

A versatile and portable proxy for capturing, manipulating, and replaying HTTP/HTTPS traffic on the go.

:zap: Web Debugging Proxy based on Chrome DevTools Network panel.

Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…

Automated HTTP Request Repeating With Burp Suite

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

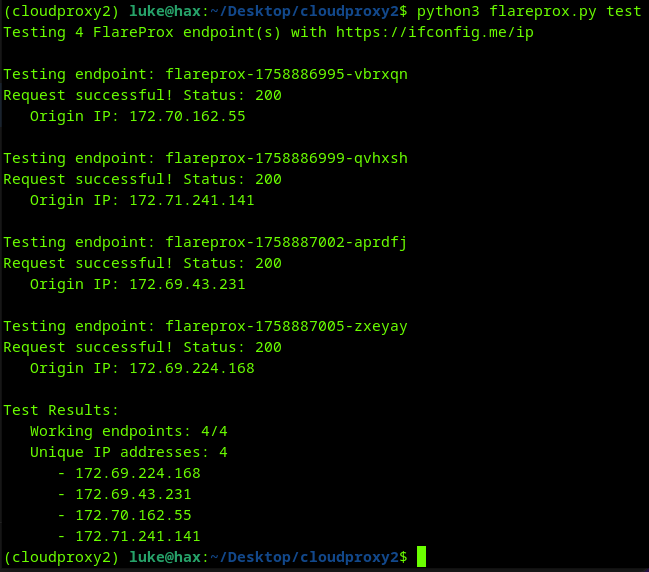
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox

An on-path blackbox network traffic security testing tool

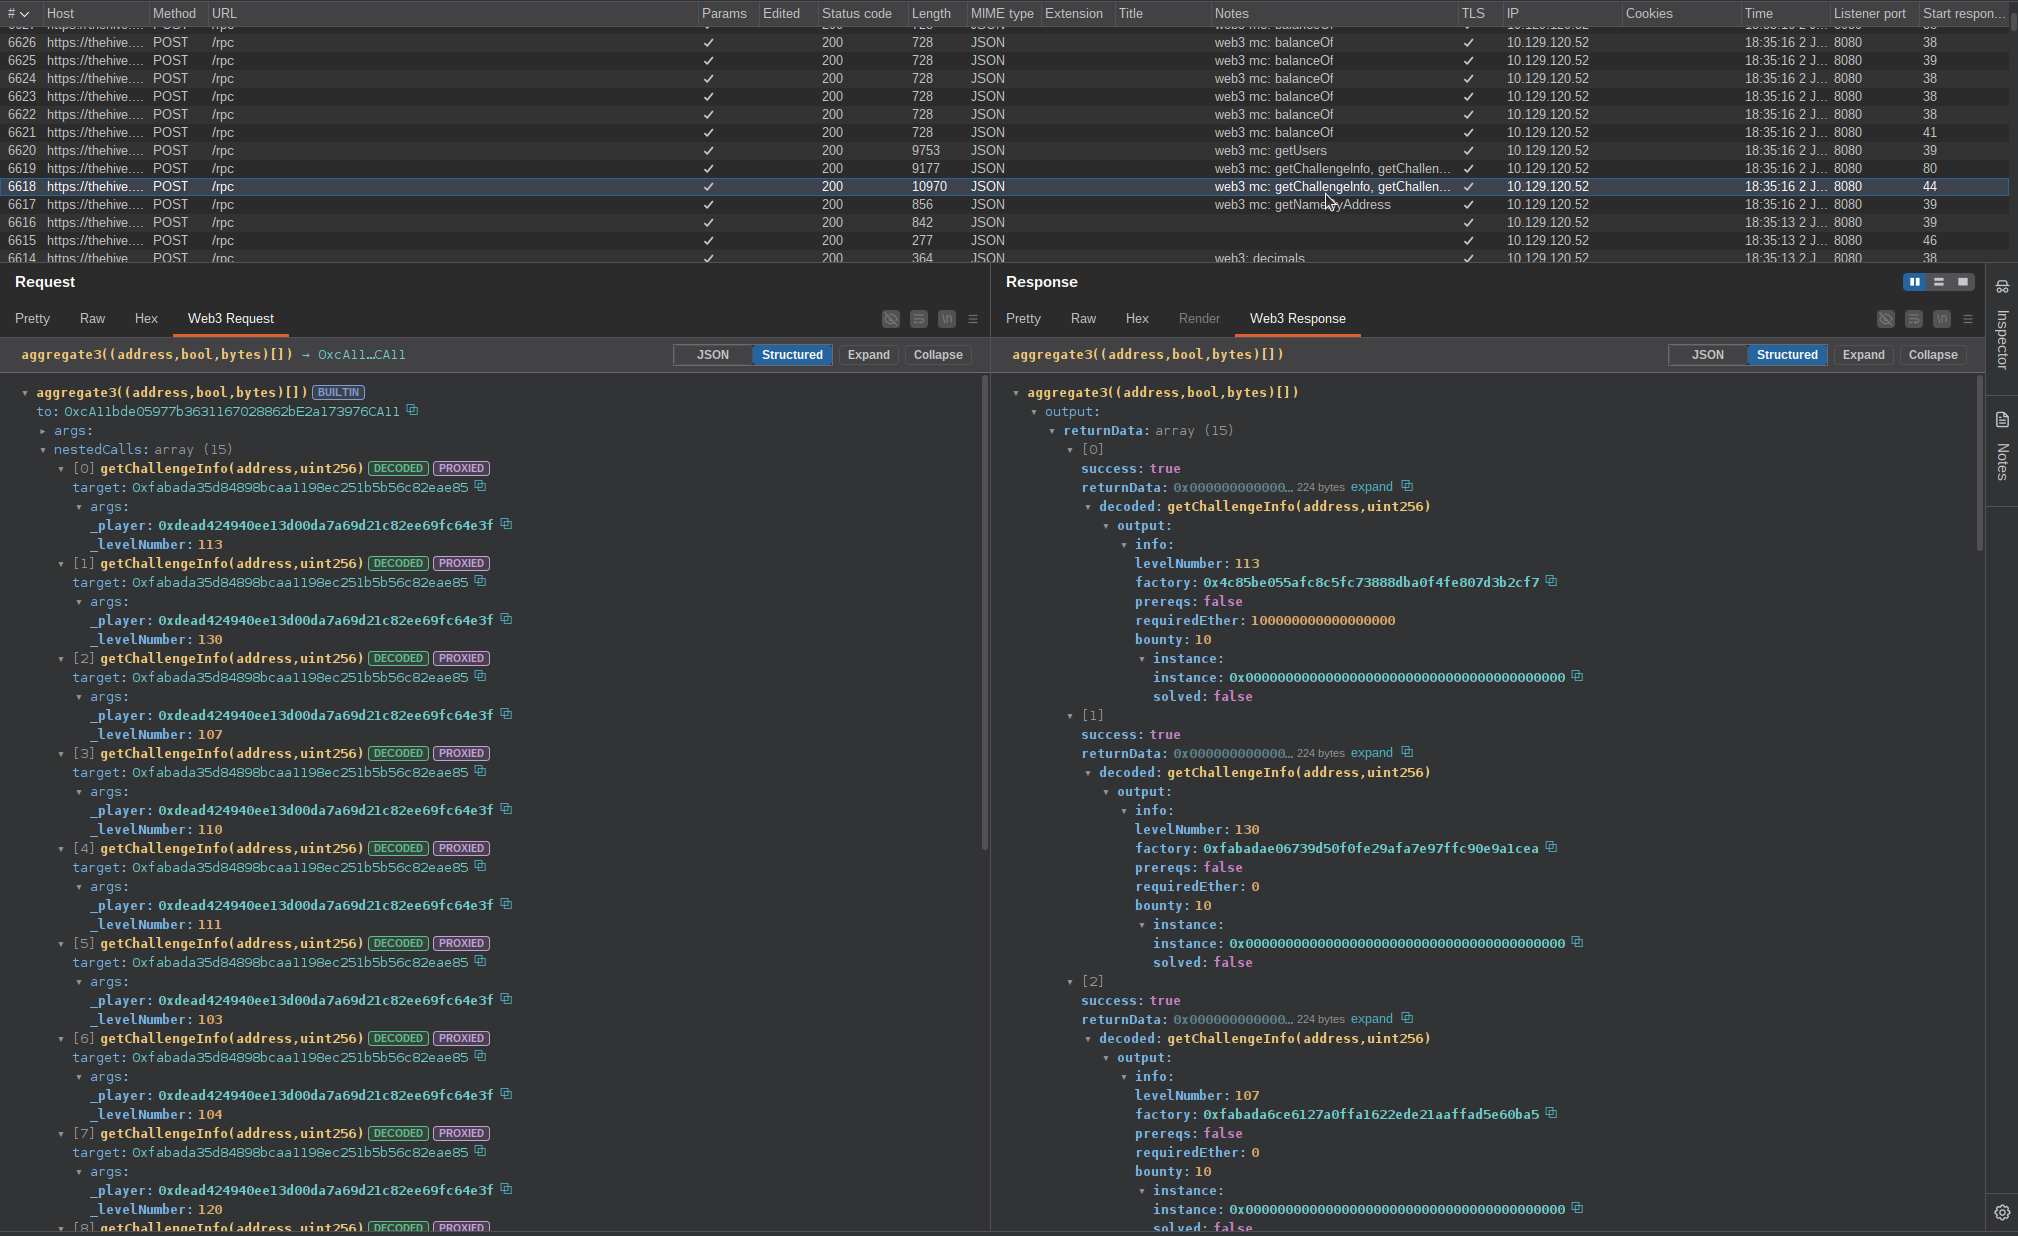
Burp Suite extension for decoding Web3 JSON-RPC traffic, including smart contract function calls, responses, and ABI resolution with proxy-aware and…

CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4