
jaeles
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
dynamic-code-analysispenetration-testingvulnerability-scanners+2
2.4k3 months ago
jaeles-project/jaelesThe Swiss Army knife for automated Web Application Testing
 urbanadventurer/whatweb
Next generation web scanner

 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
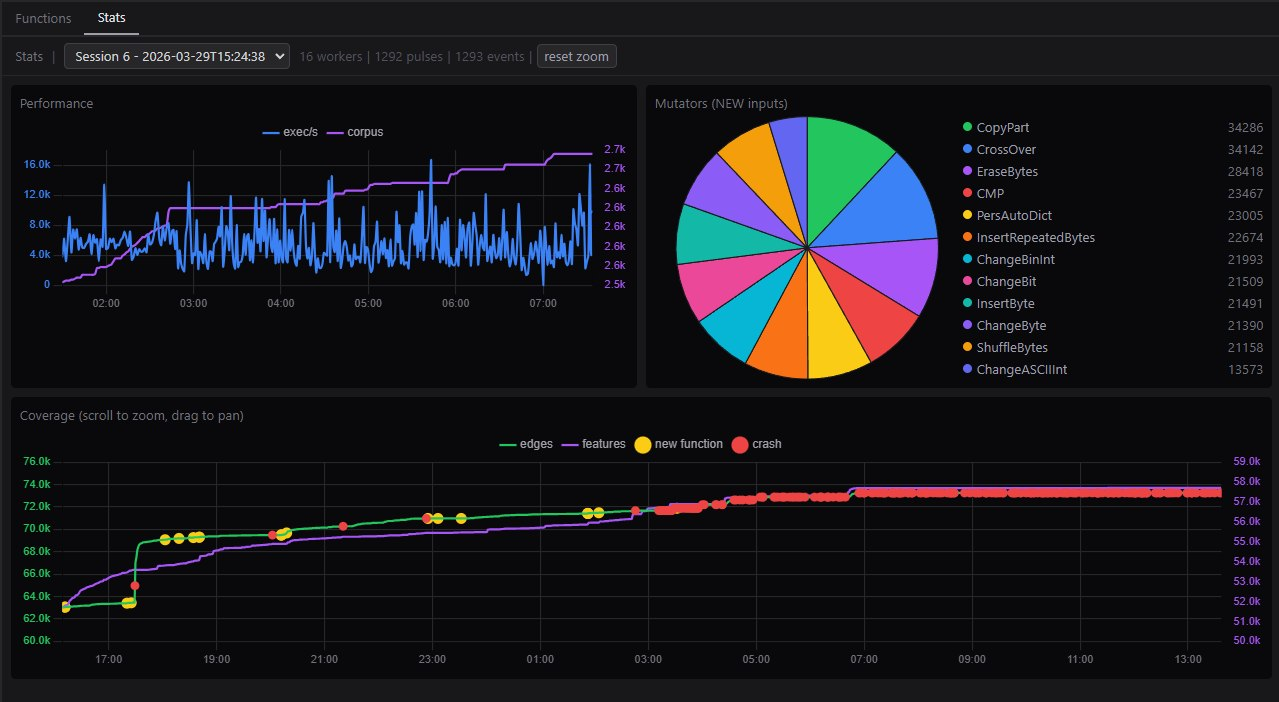 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server