

redknife
 yukibtc/redknife
A Swiss Army knife for offensive security.
command-and-controlinformation-gatheringpenetration-testing+4
yukibtc/redknifeA Swiss Army knife for offensive security.

 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
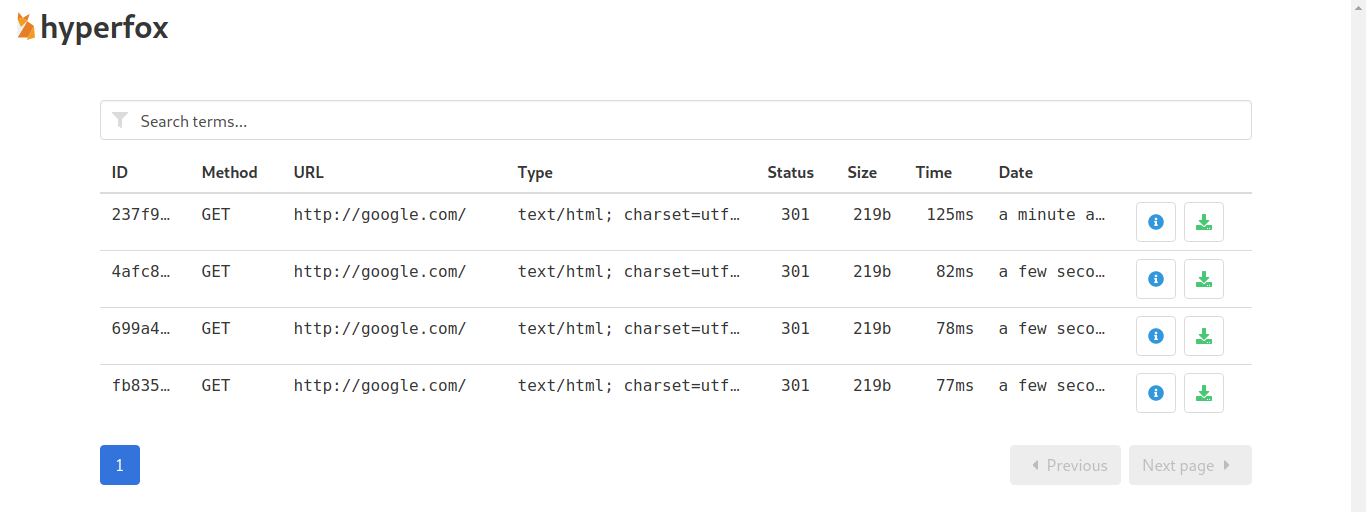 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.