

raider
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
101
owasp/raiderOWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 rvermeulen/apache-struts-cve-2017-9805
Exploit for Apache Struts CVE-2017-9805, a remote code execution vulnerability in the REST plugin. Enables penetration testing and security…
 cyberharsh/ruby-on-rails-path-traversal-vulnerability-cve-2018-3760-
Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 sonpt-afk/cve-2018-11776-fis
Exploit for CVE-2018-11776, a remote code execution vulnerability in Apache Struts via OGNL injection. Demonstrates the attack vector and impact for…
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 nyakki-labs-0x420/myesve
CVE-2024-38475 exploitation & scanning tool with Mullvad VPN rotation
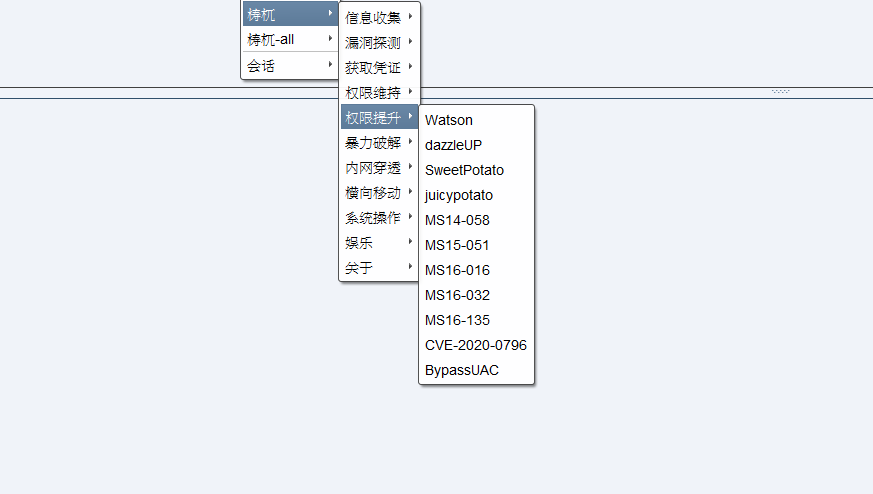 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
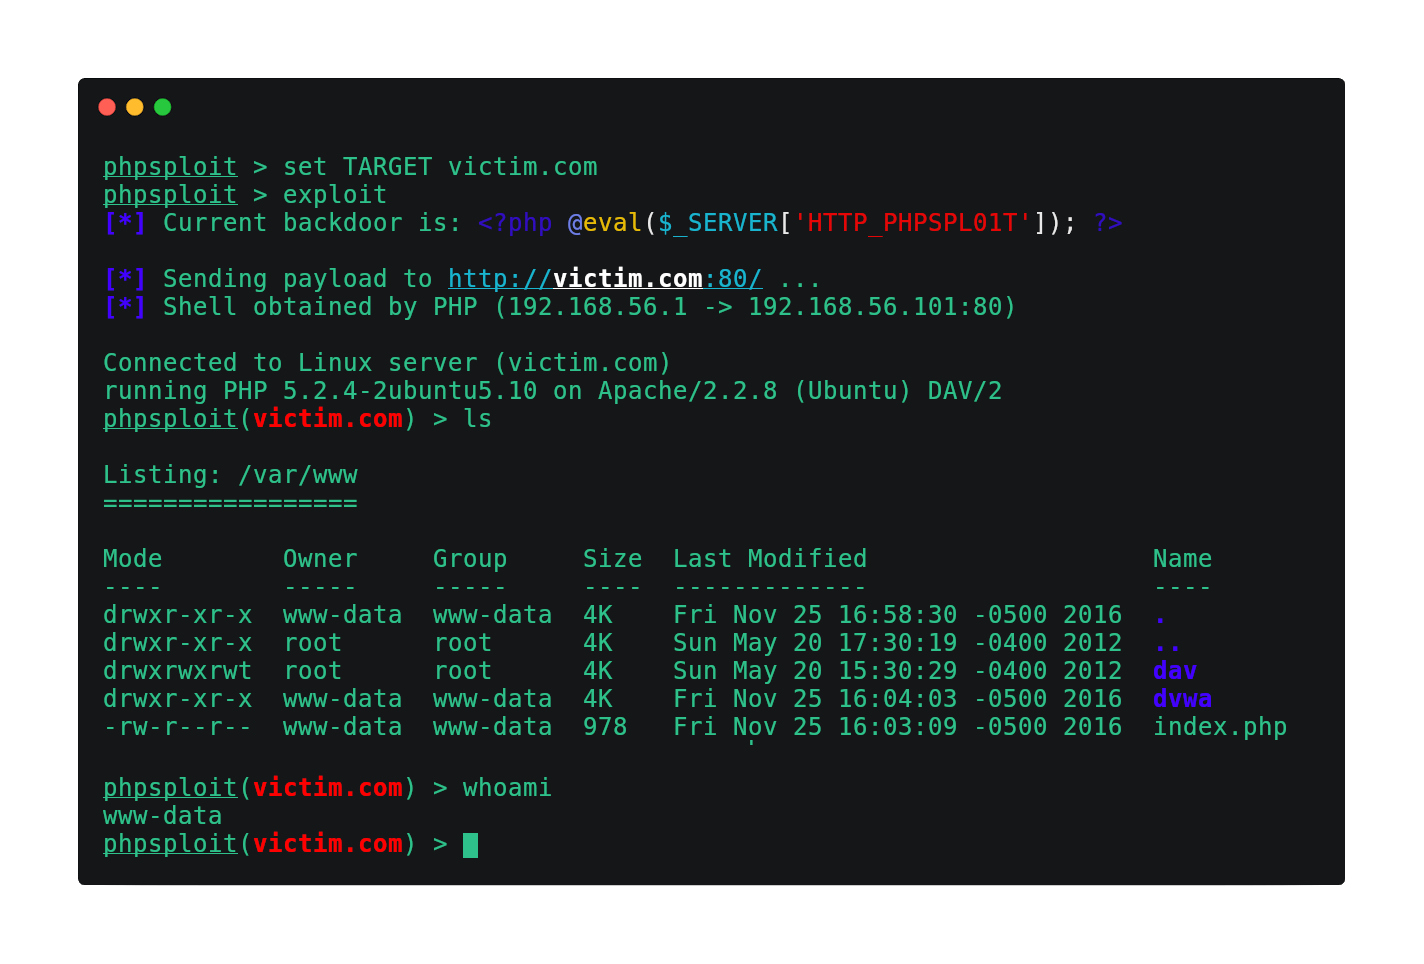 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 sysdream/pysqli
Python SQL injection framework
 bishopfox/joro
A collaborative web exploitation framework.
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 chrisallenlane/novahot
A webshell framework for penetration testers.
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on