
MemShellParty
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
exploit-frameworkspayload-generationpenetration-testing+3
1.6k
reajason/memshellparty一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 bishopfox/joro
A collaborative web exploitation framework.
 beefproject/beef
The Browser Exploitation Framework Project
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 guila95/cve-2026-86426
Proof-of-concept and recon framework for CVE-2026-86426, a LibreNMS API authentication bypass via type confusion, extracting SNMP credentials and…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 nu11secur1ty/sqlmap-nu11secur1ty
Professional extension of sqlmap project
 industri4l-h3ll-xpl0it3rs/cve-2025-55182-react2shell
CVE-2025-55182 Exploit | by infrar3d
 shenril/sitadel
Web Application Security Scanner
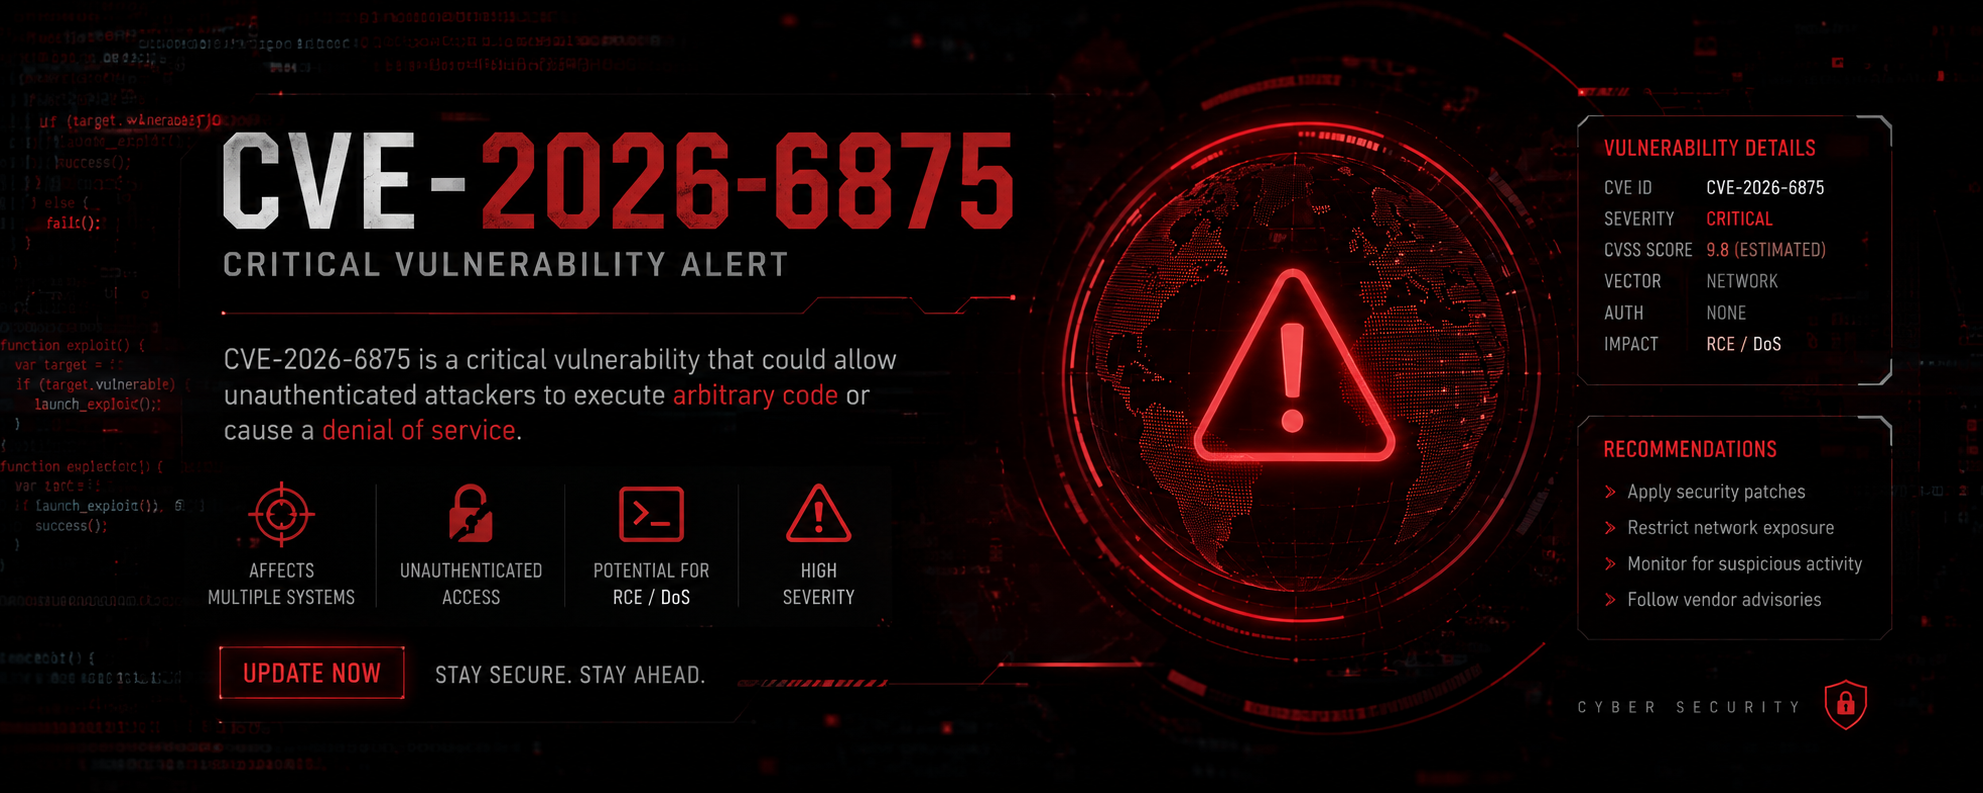 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
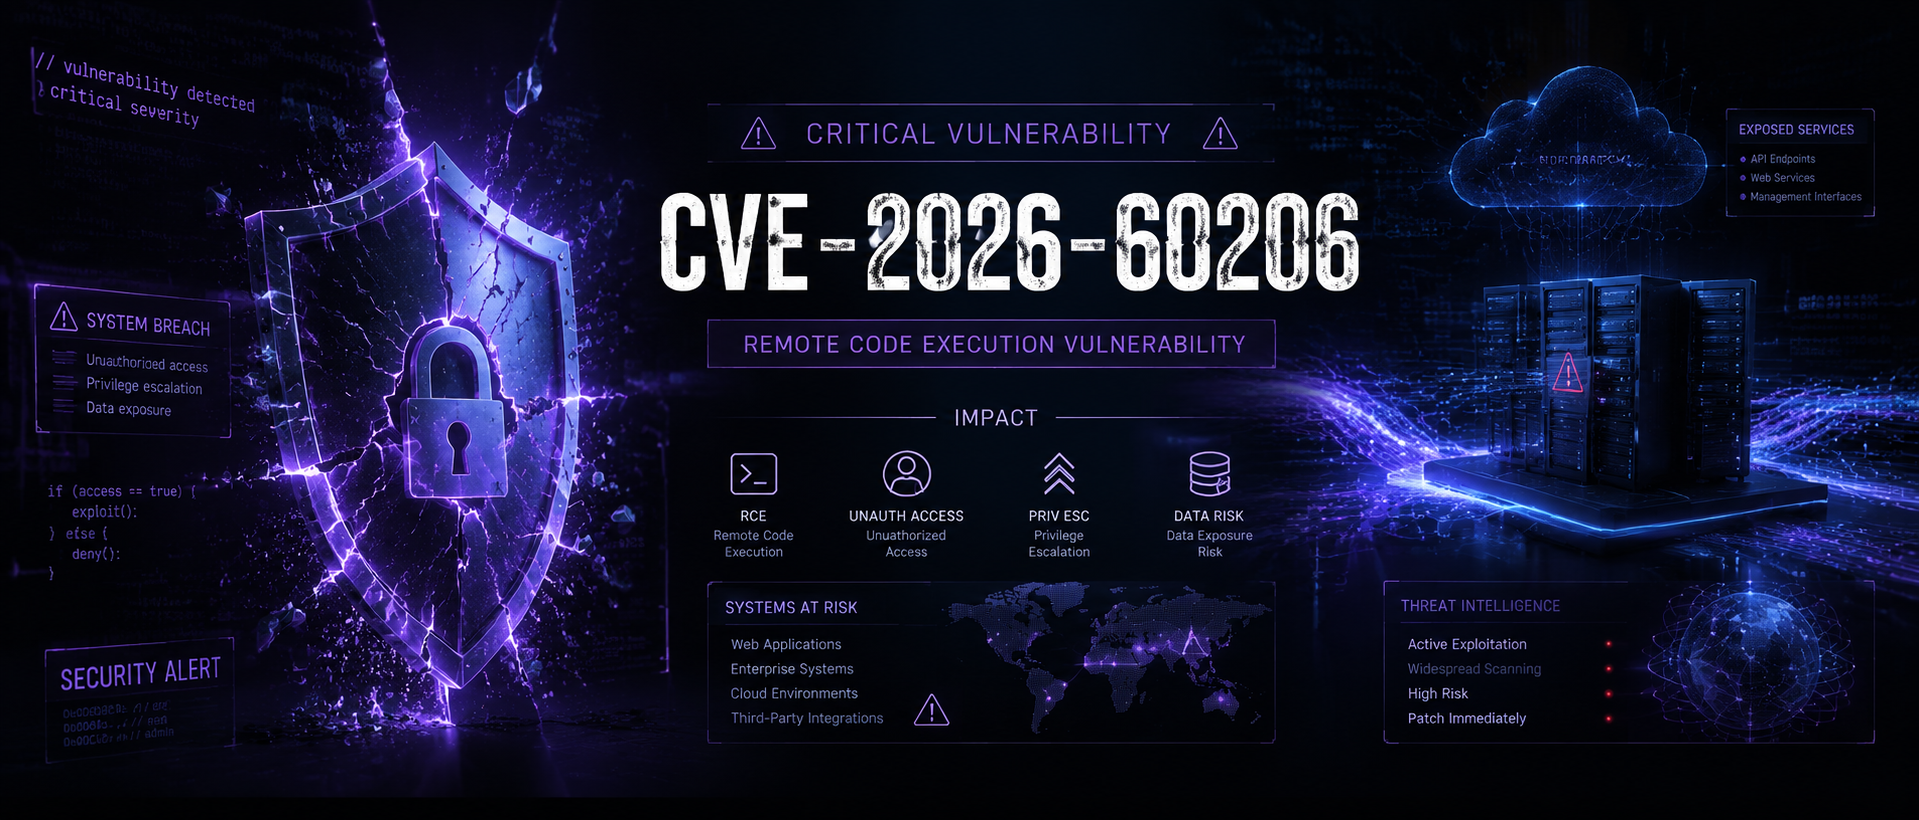 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
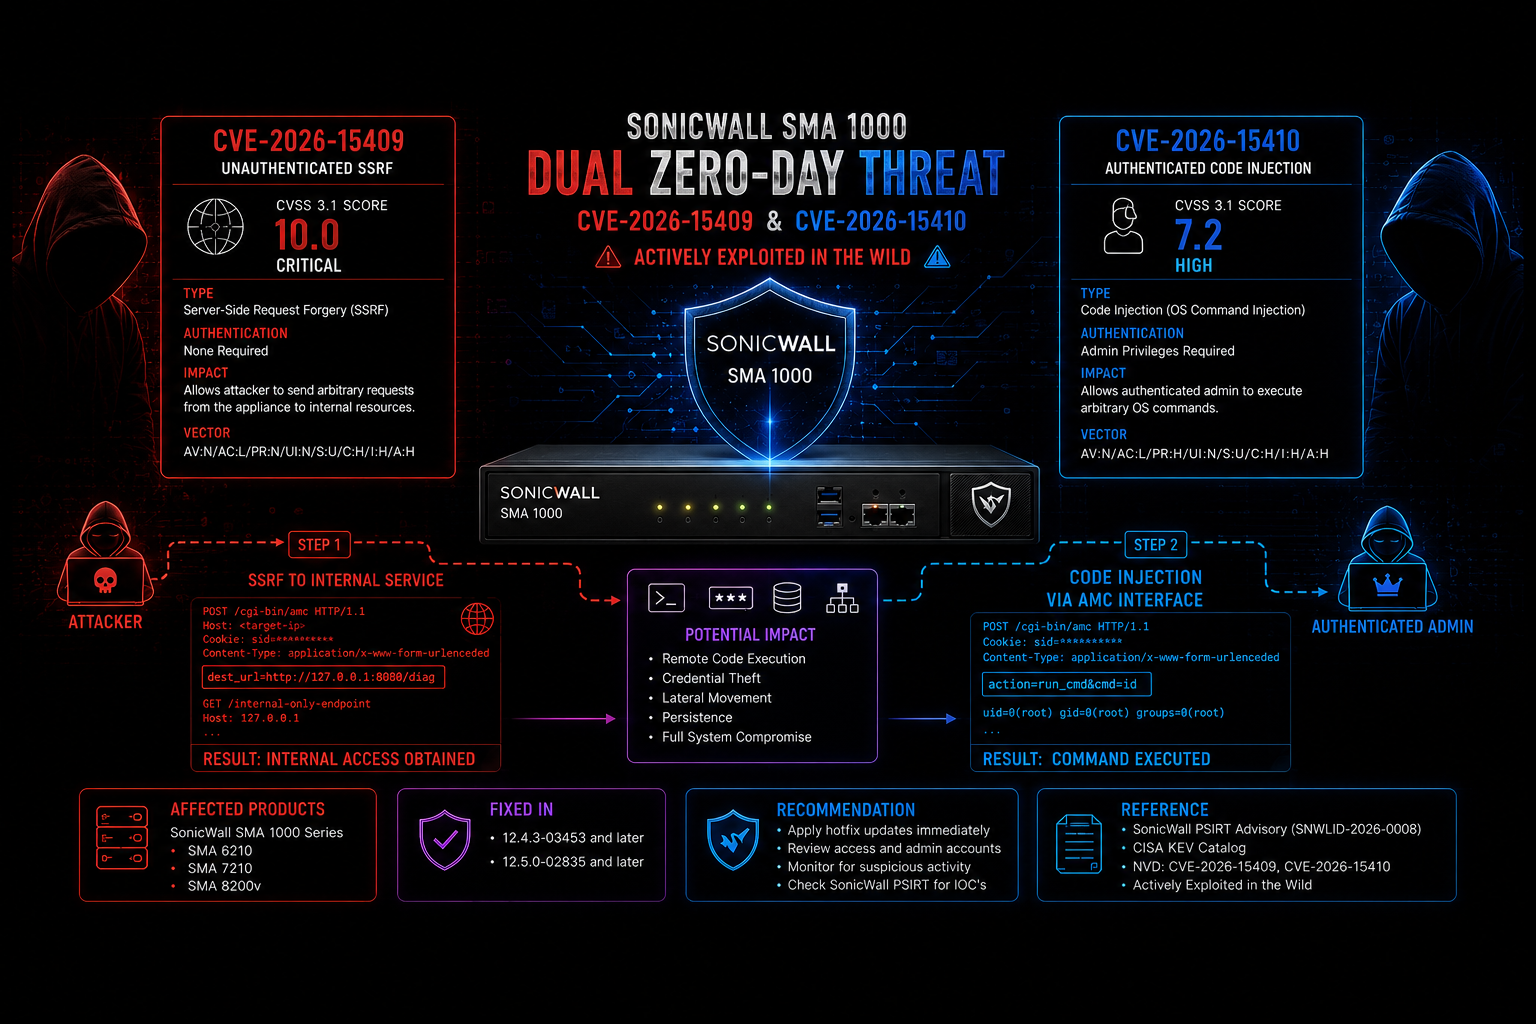 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.