
fuzz
 xsscx/fuzz
Commodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
curated-resourcesexploitationfuzzing+6
xsscx/fuzzCommodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
 7iosecurity/xss-payloads
Collection of cross-site scripting (XSS) payloads for web application security testing, filter bypass research, and penetration testing engagements.
 cujanovic/crlf-injection-payloads
Collection of CRLF injection payloads gathered from bug bounty reports, used as a reference for testing HTTP header and response splitting…
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 nishikawaakira/waf-dojo
Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…
 oscerd/cve-2026-90885
Runnable proof-of-concept reproducer for CVE-2026-90885, an XXE (CWE-611) in Apache Camel camel-saxon XQuery, with Spring Boot and Quarkus builds and…
 oscerd/cve-2026-95628
Runnable proof-of-concept reproducer for CVE-2026-95628, an absolute-path validation gap in Apache Camel camel-docling, with Spring Boot and Quarkus…
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
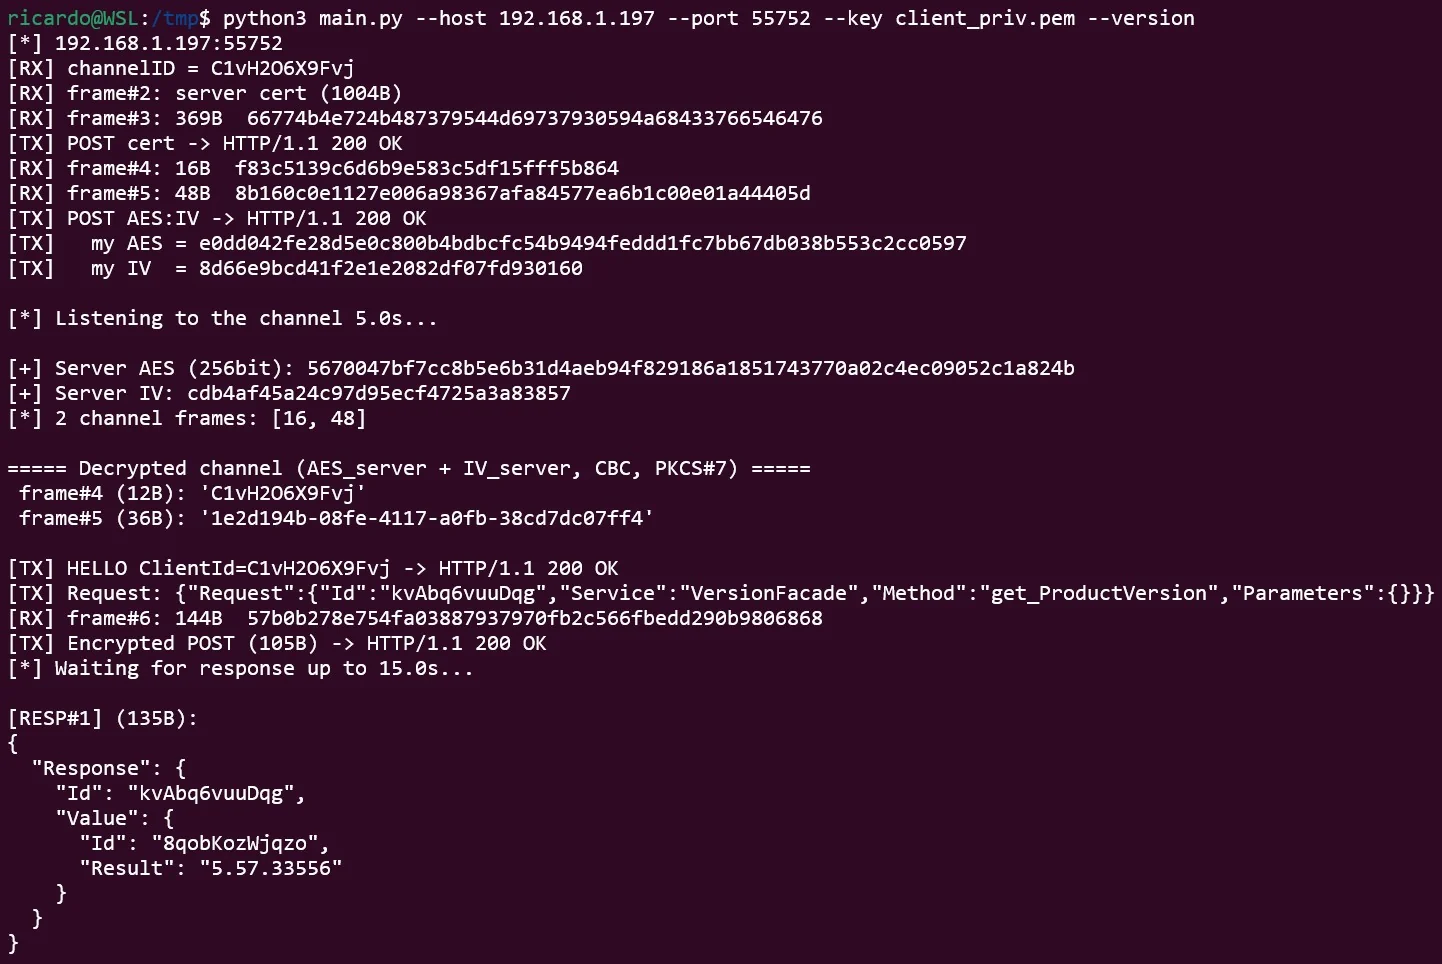 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 d4t4s3c/offensivereverseshellcheatsheet
Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
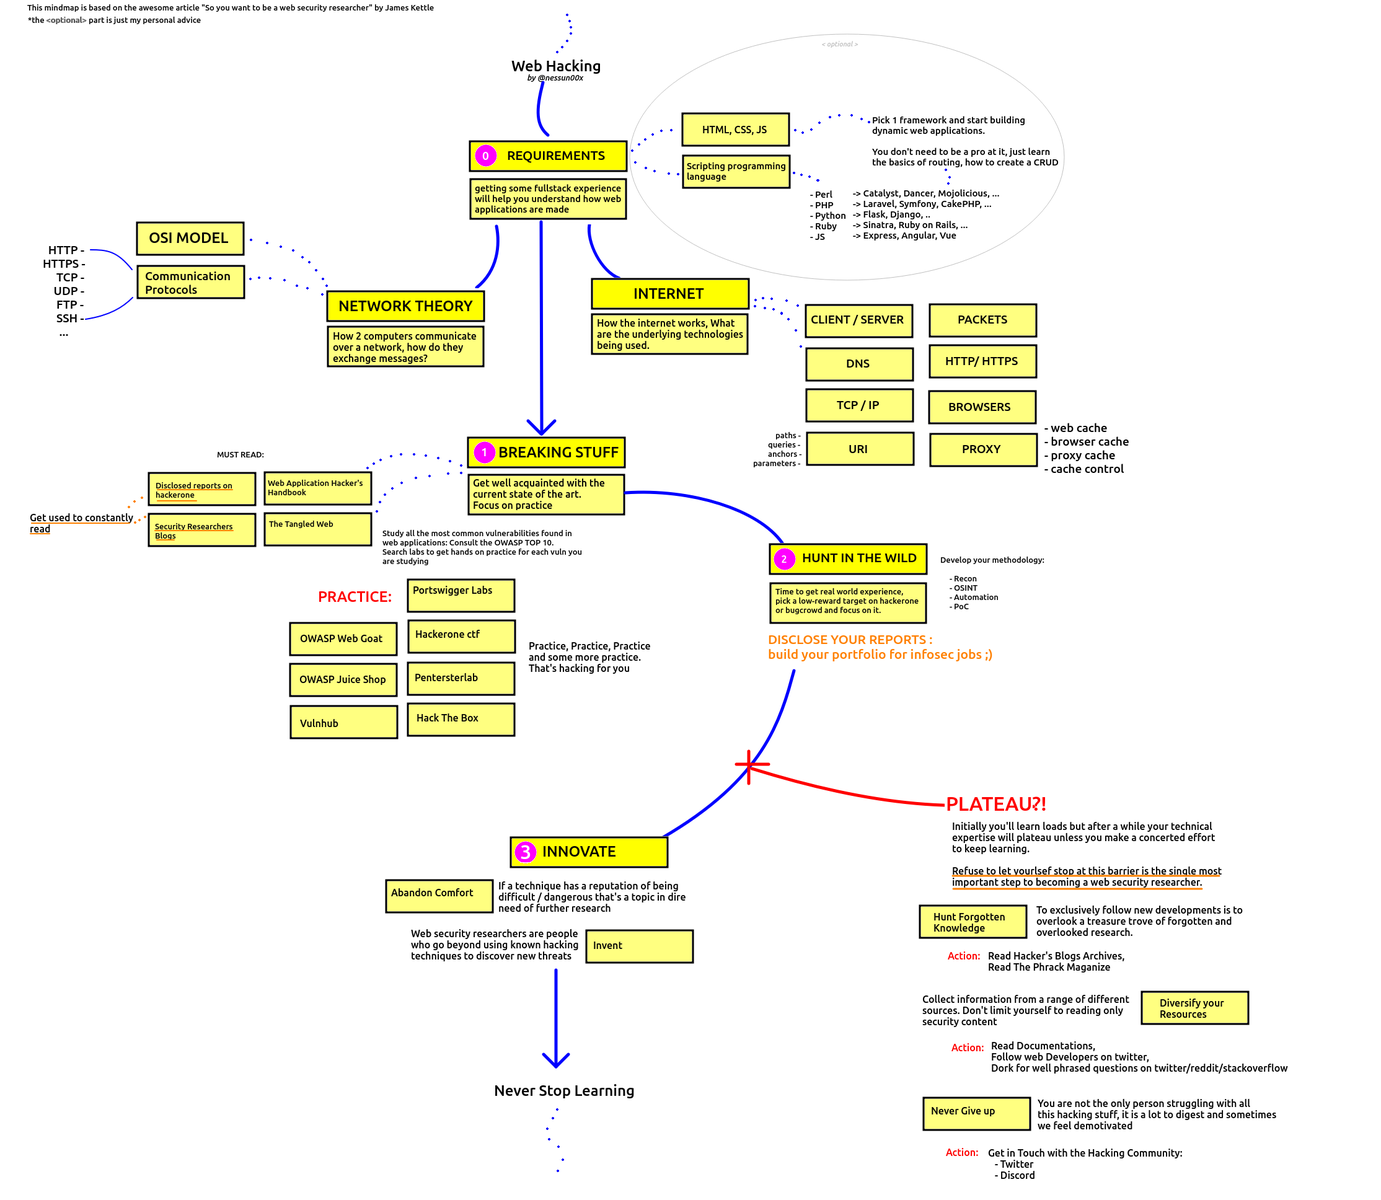 domssilva/vulnsearch
A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…
 moisestapia/twapt
Deploy your own lab of web application penetration testing with docker and docker-compose, webgoat, dvwap, bwapp and Juice Shop
 dev-angelist/ejptv2-notes
eLearnSecurity Junior Penetration Tester (eJPT) v2 Notes
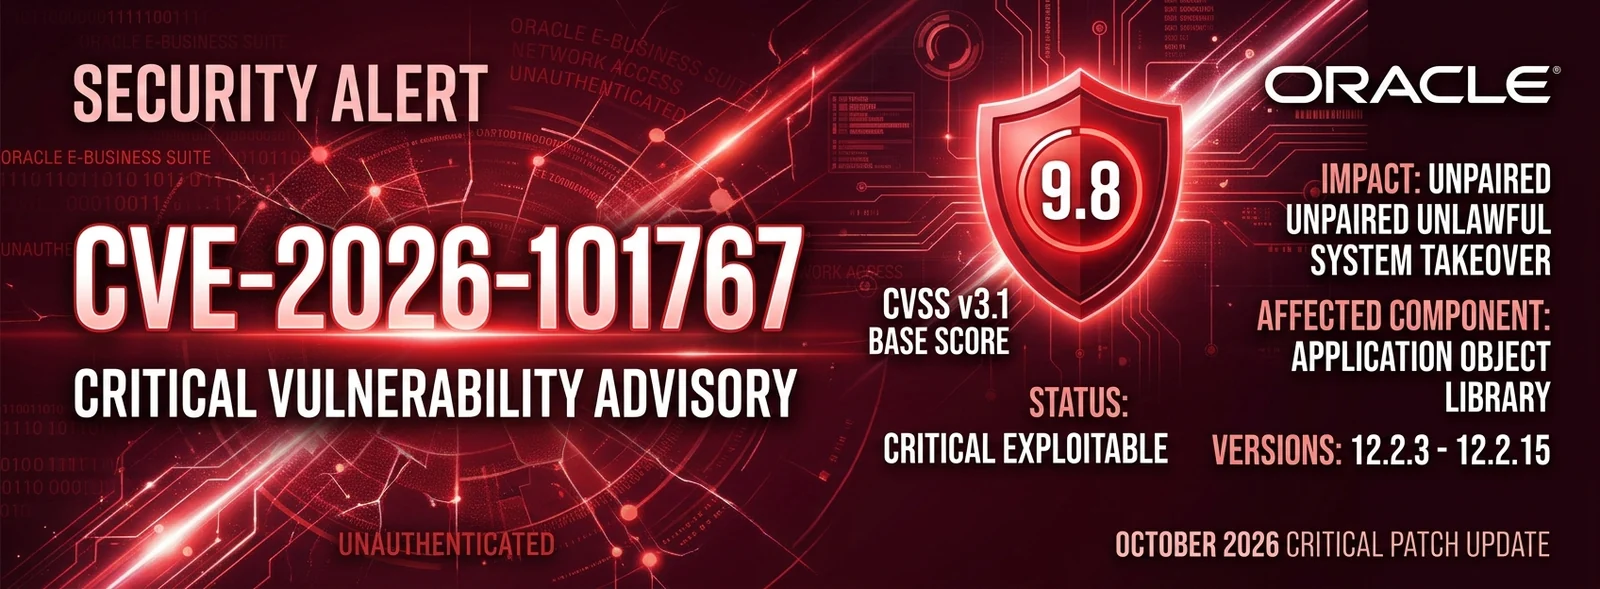 0xblackash/cve-2026-101767
Advisory and technical research analysis of CVE-2026-101767, a critical unauthenticated RCE in Oracle E-Business Suite Application Object Library,…