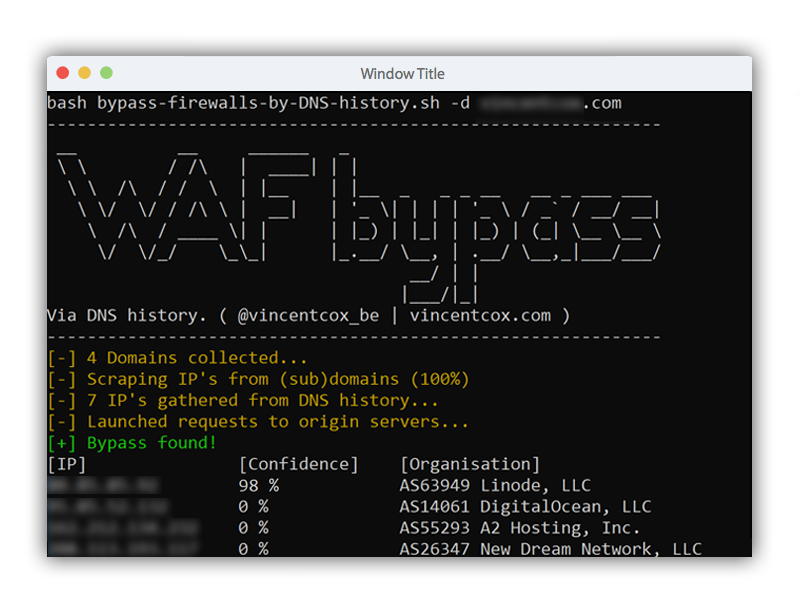
bypass-firewalls-by-DNS-history

Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

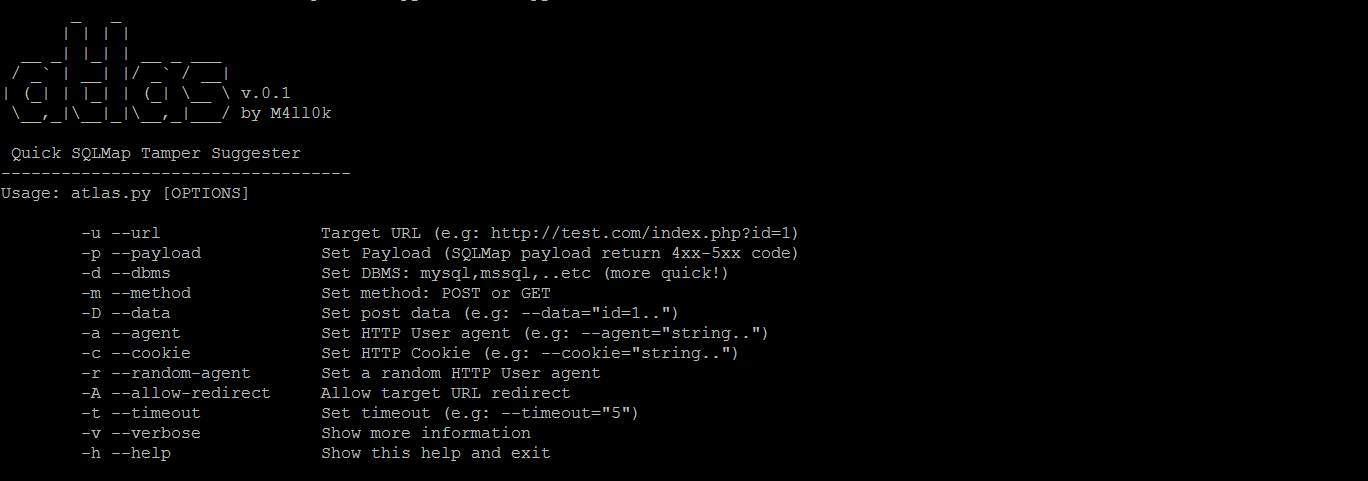
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing

XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.

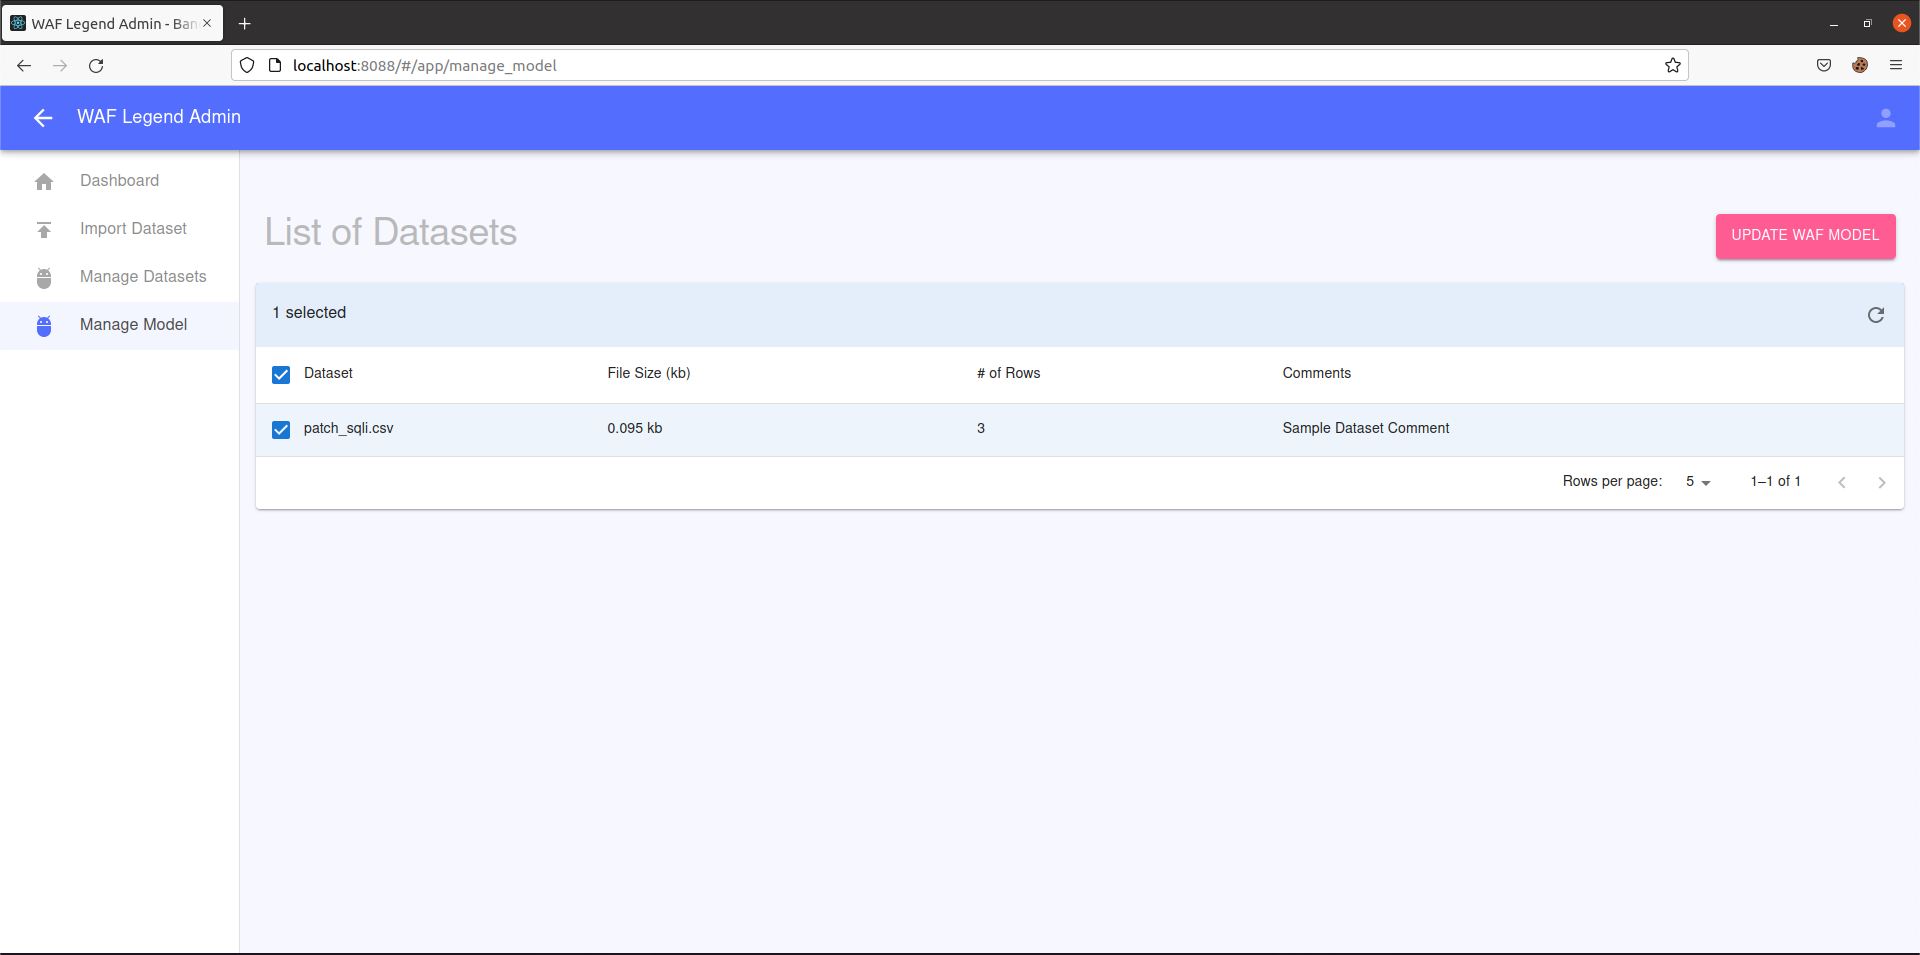
First iteration of ML based Feedback WAF

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

Undetected version of the Playwright testing and automation library.


AWS WAF Solver, full reverse implemented in 100% Python & Golang.

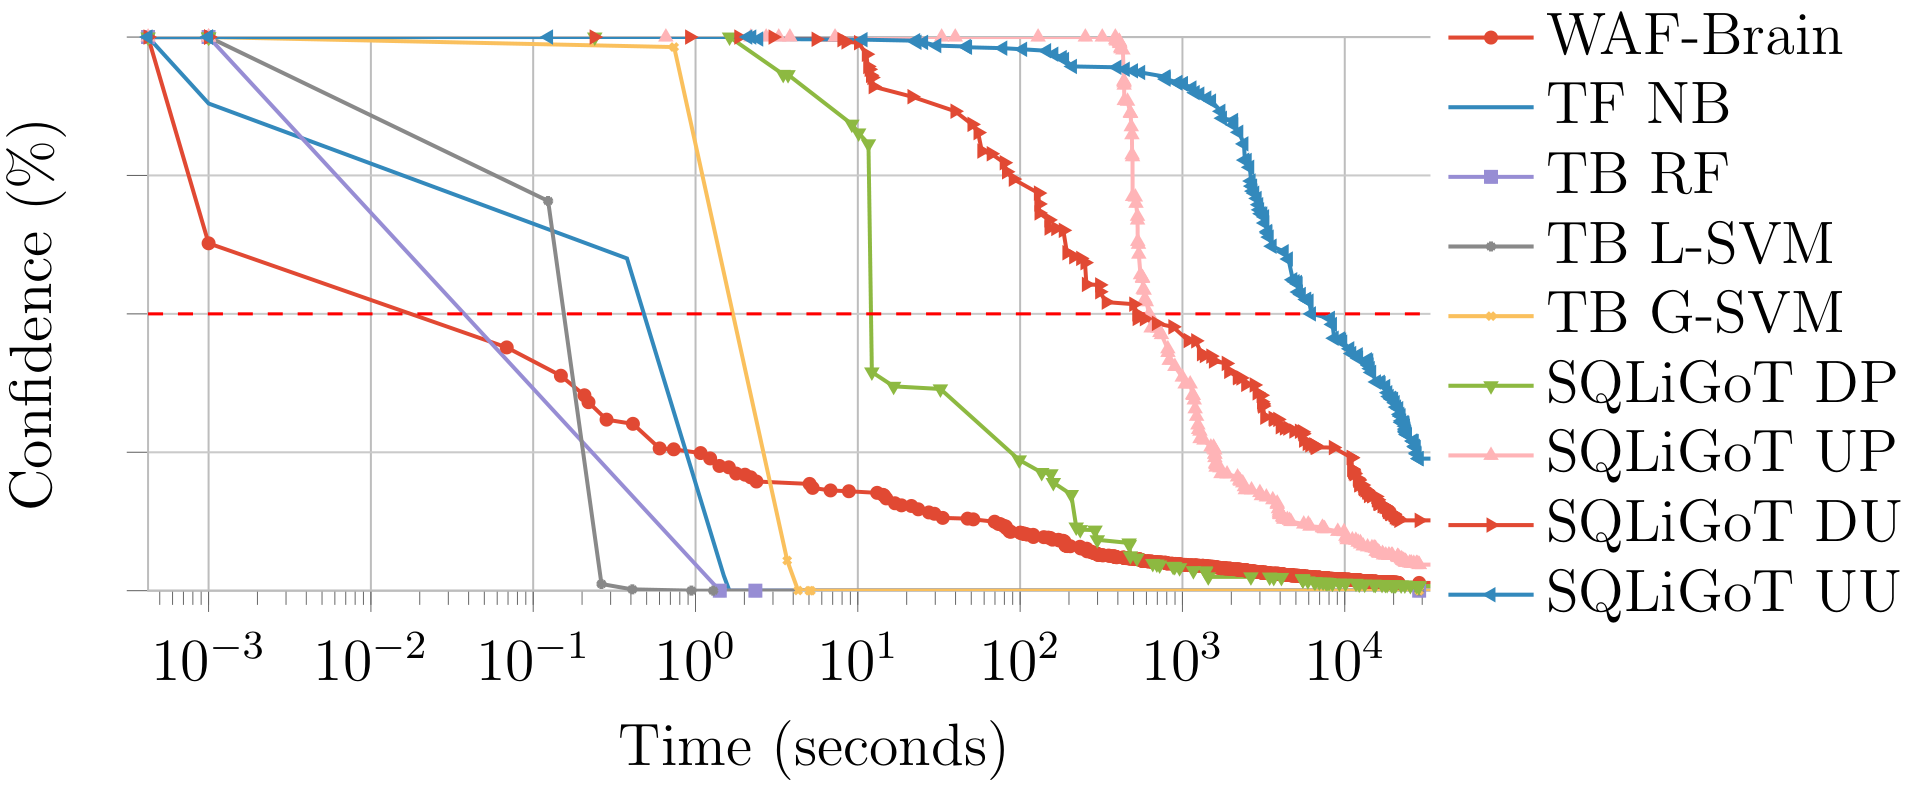
A guided mutation-based fuzzer for ML-based Web Application Firewalls

From Dork to Download: Automating Google Dorks with Playwright

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…

Docker-based security lab demonstrating Apache Struts2 S2-045 (CVE-2017-5638) exploitation and defense, featuring vulnerable and patched applications…

Python-based vulnerability scanner for detecting CVE-2025-32429 SQL injection in XWiki platforms. Supports single/bulk scanning, WAF detection,…