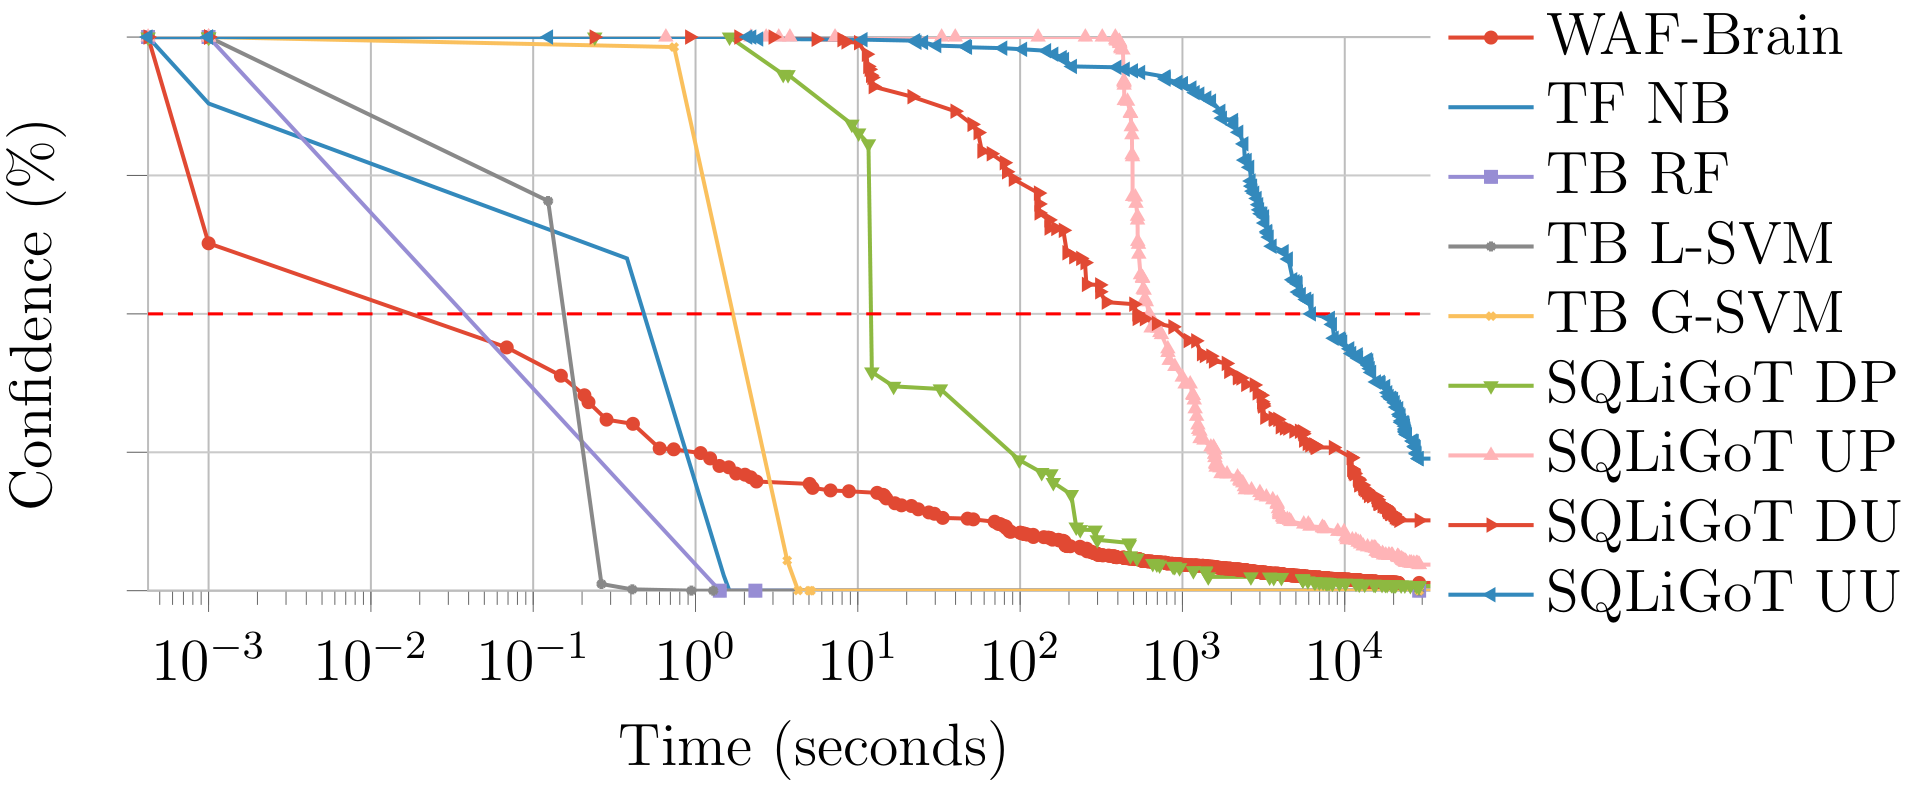
WAF-A-MoLE
 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
adversarial-attackfuzzingmachine-learning+2
avalz/waf-a-moleA guided mutation-based fuzzer for ML-based Web Application Firewalls
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 imbas007/cve-2025-32429-checker
Python-based vulnerability scanner for detecting CVE-2025-32429 SQL injection in XWiki platforms. Supports single/bulk scanning, WAF detection,…
 keramas/mssqli-duet
SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing
 acharaf06/cve-2017-5638-attack-and-defense
Docker-based security lab demonstrating Apache Struts2 S2-045 (CVE-2017-5638) exploitation and defense, featuring vulnerable and patched applications…
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 san-tus/dorkwright
From Dork to Download: Automating Google Dorks with Playwright
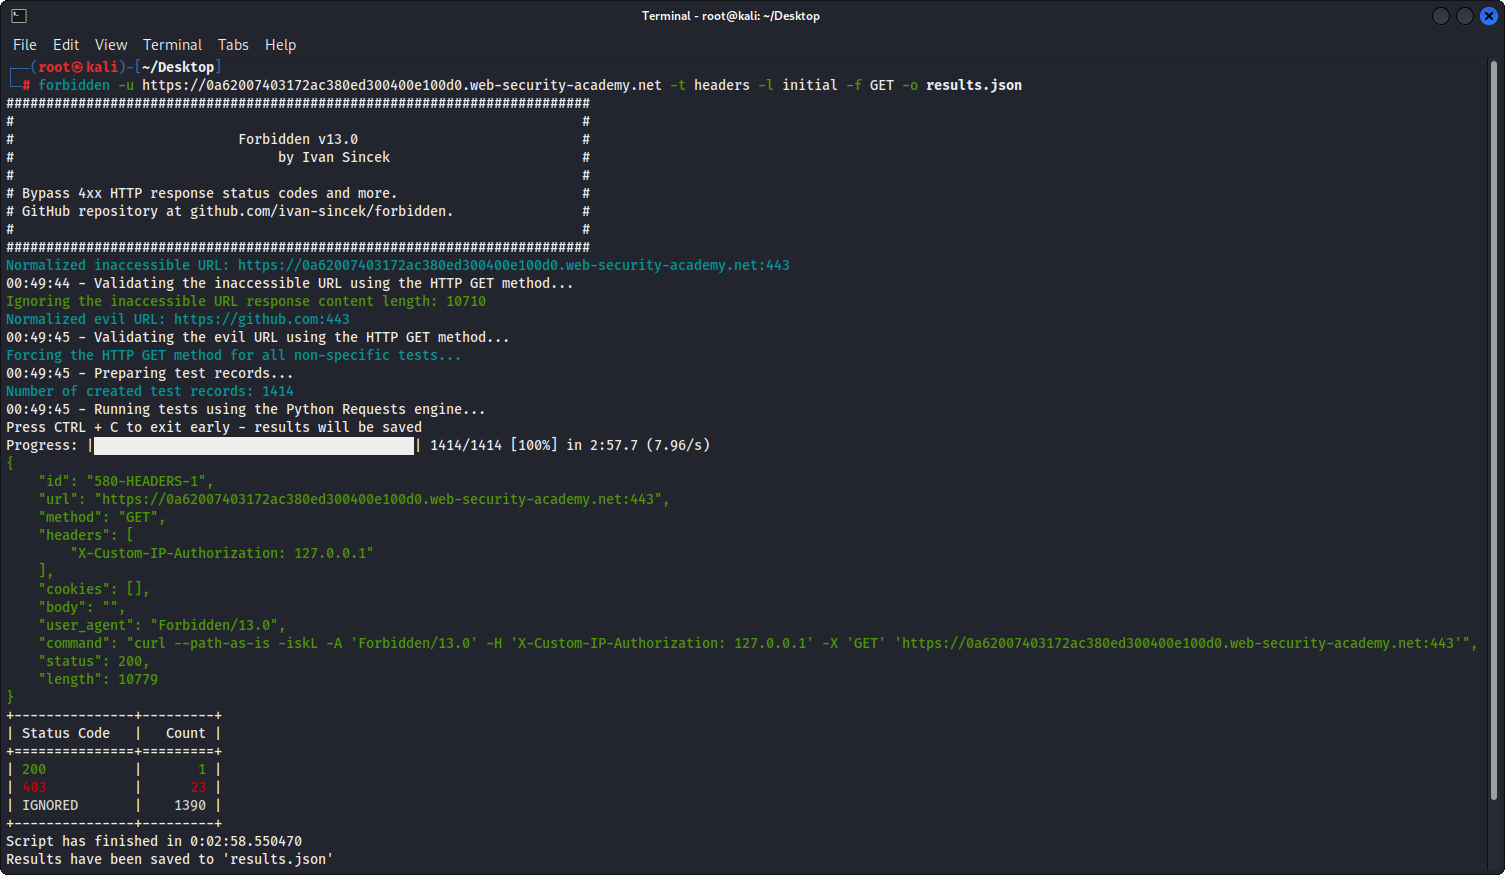 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
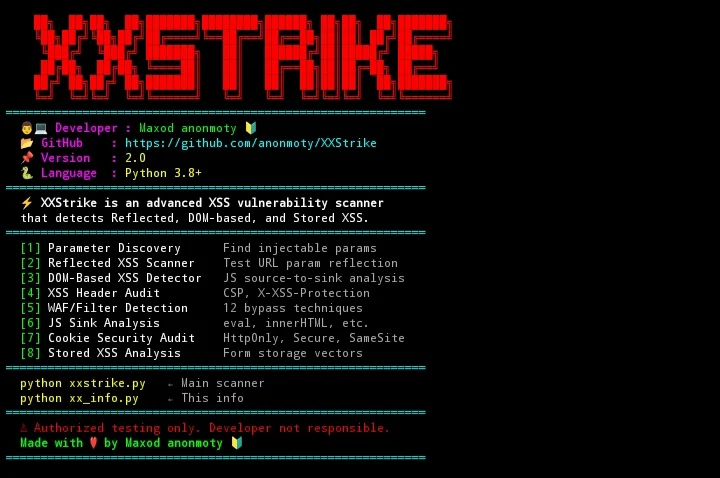 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.