

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.7k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
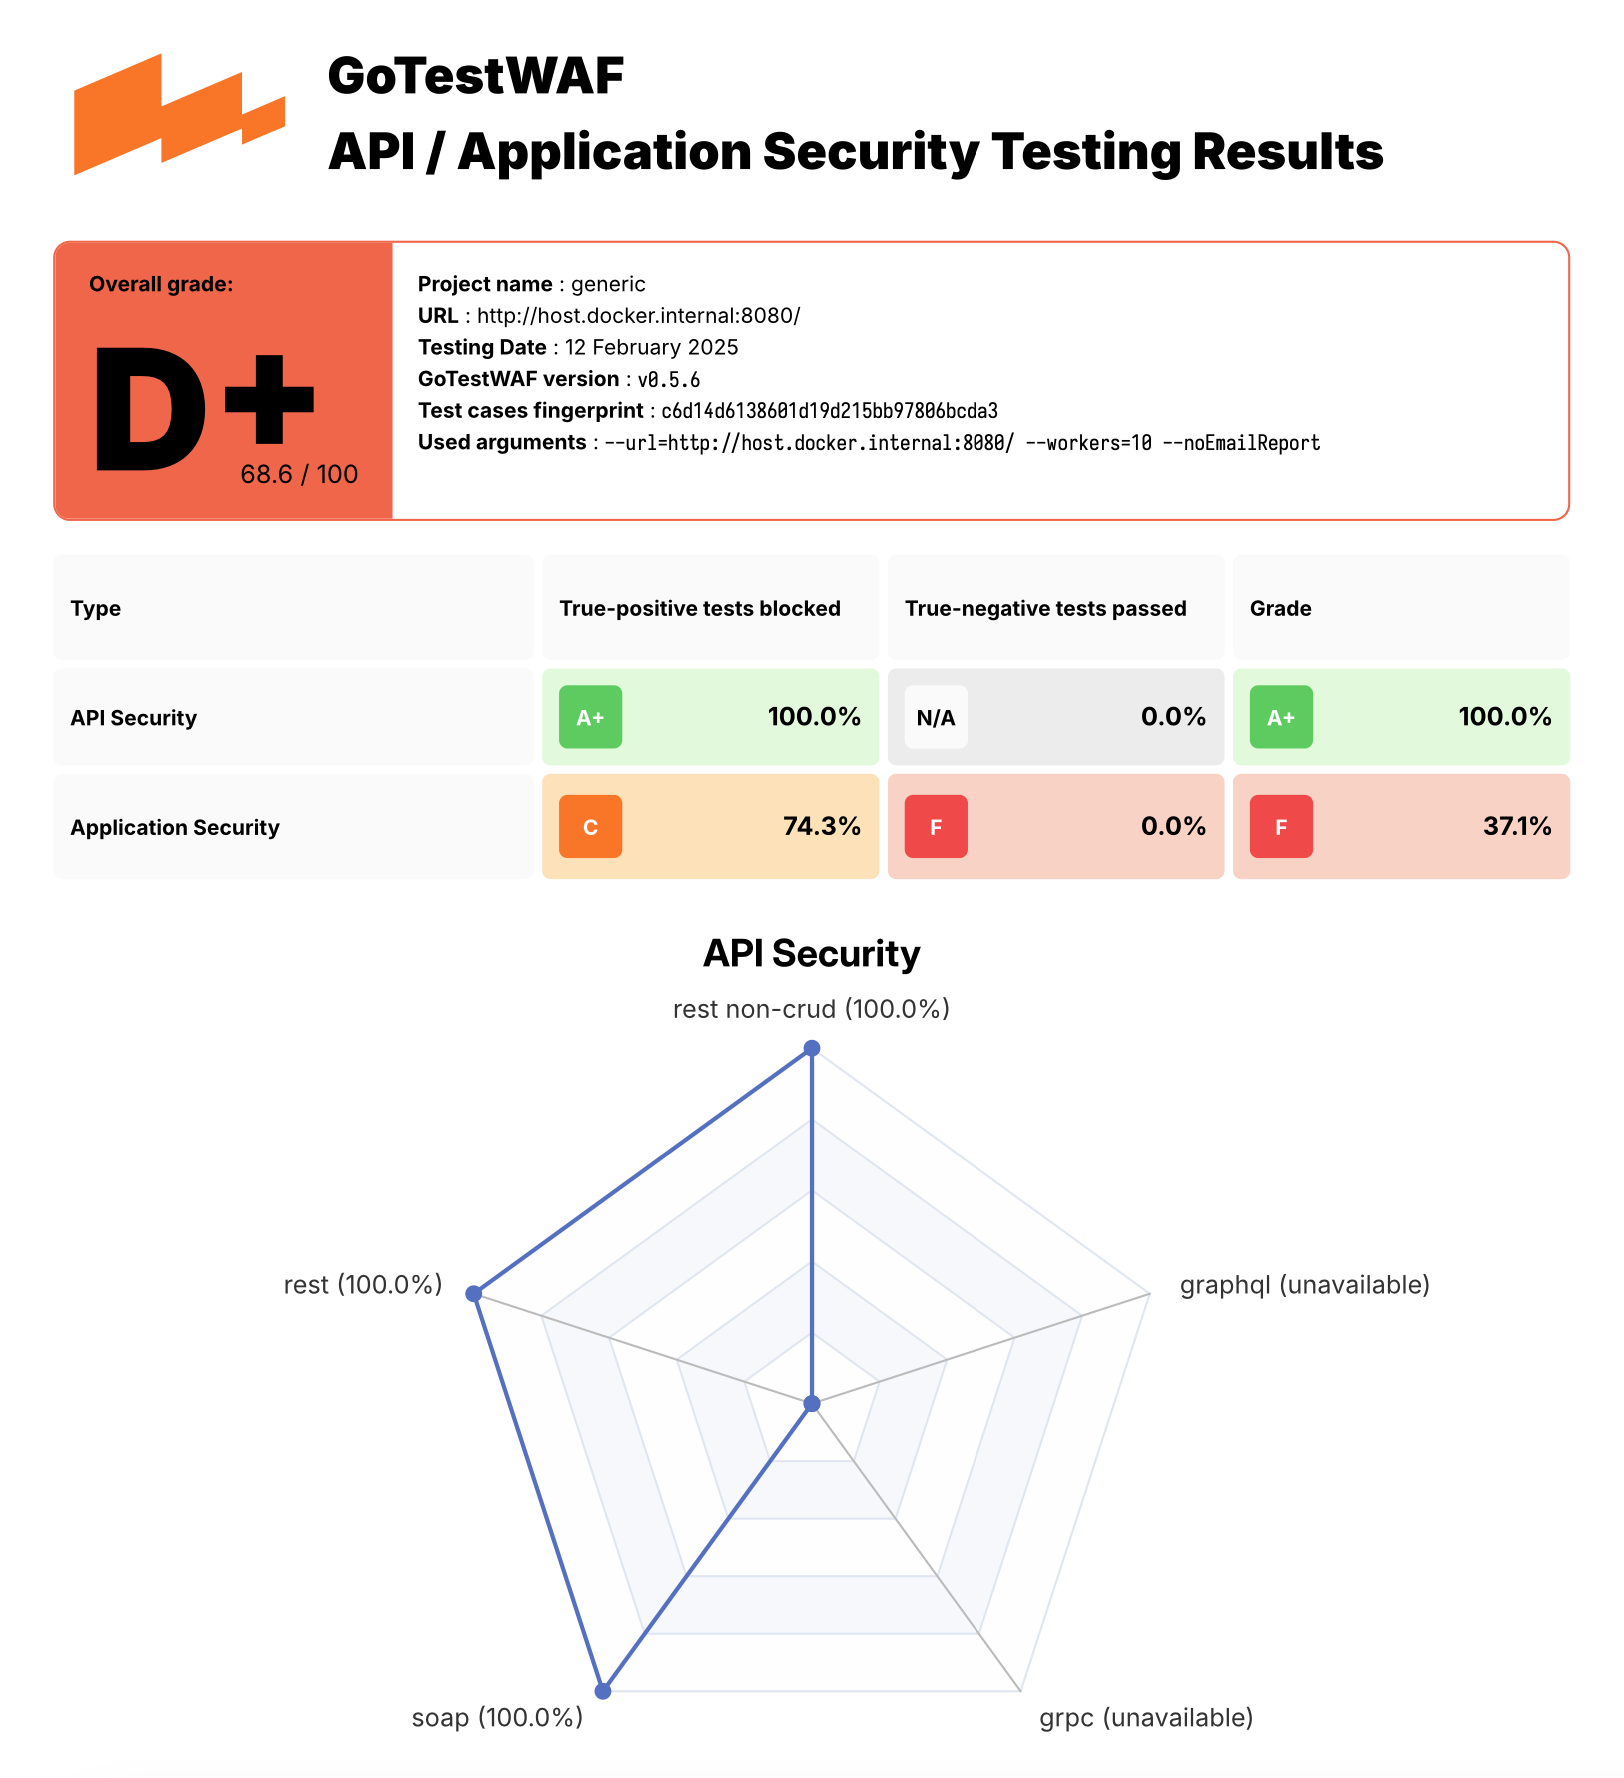 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
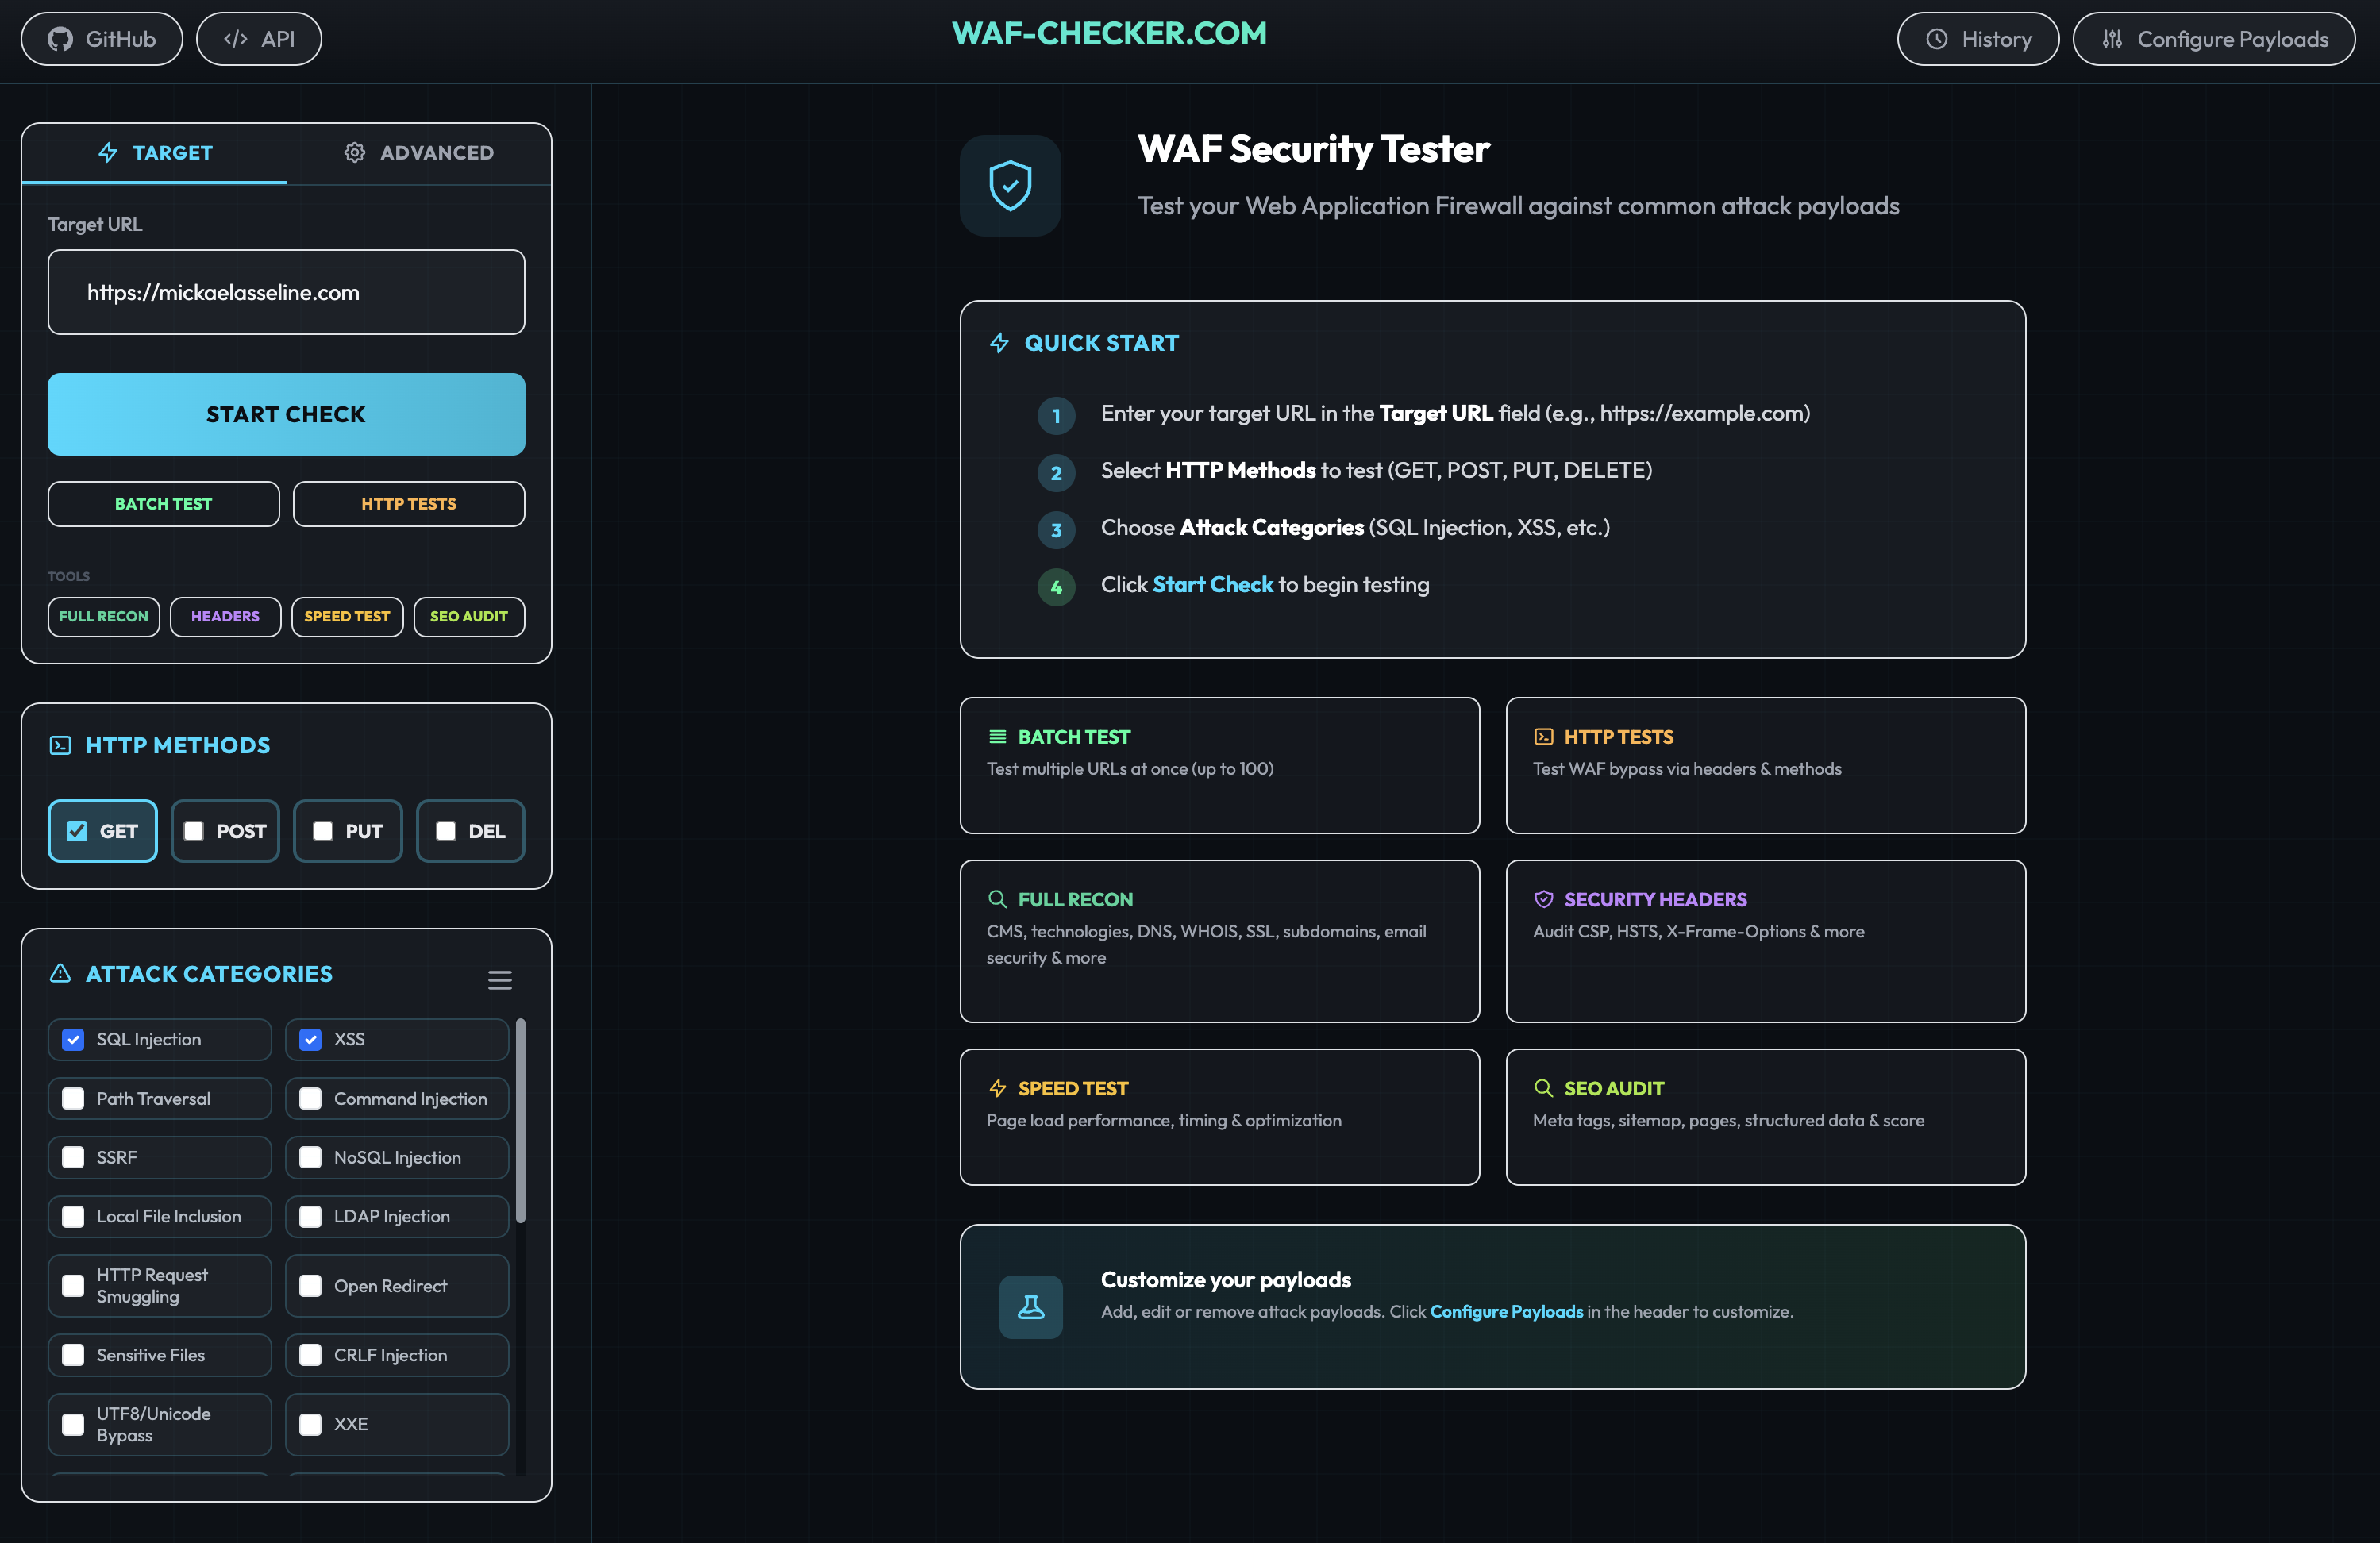 papamica/waf-checker
Tests your WAF with +160 payloads
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 pyroxenites/nextjs_rce_exploit_tool
Exploit for CVE-2025-55182 & CVE-2025-66478
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
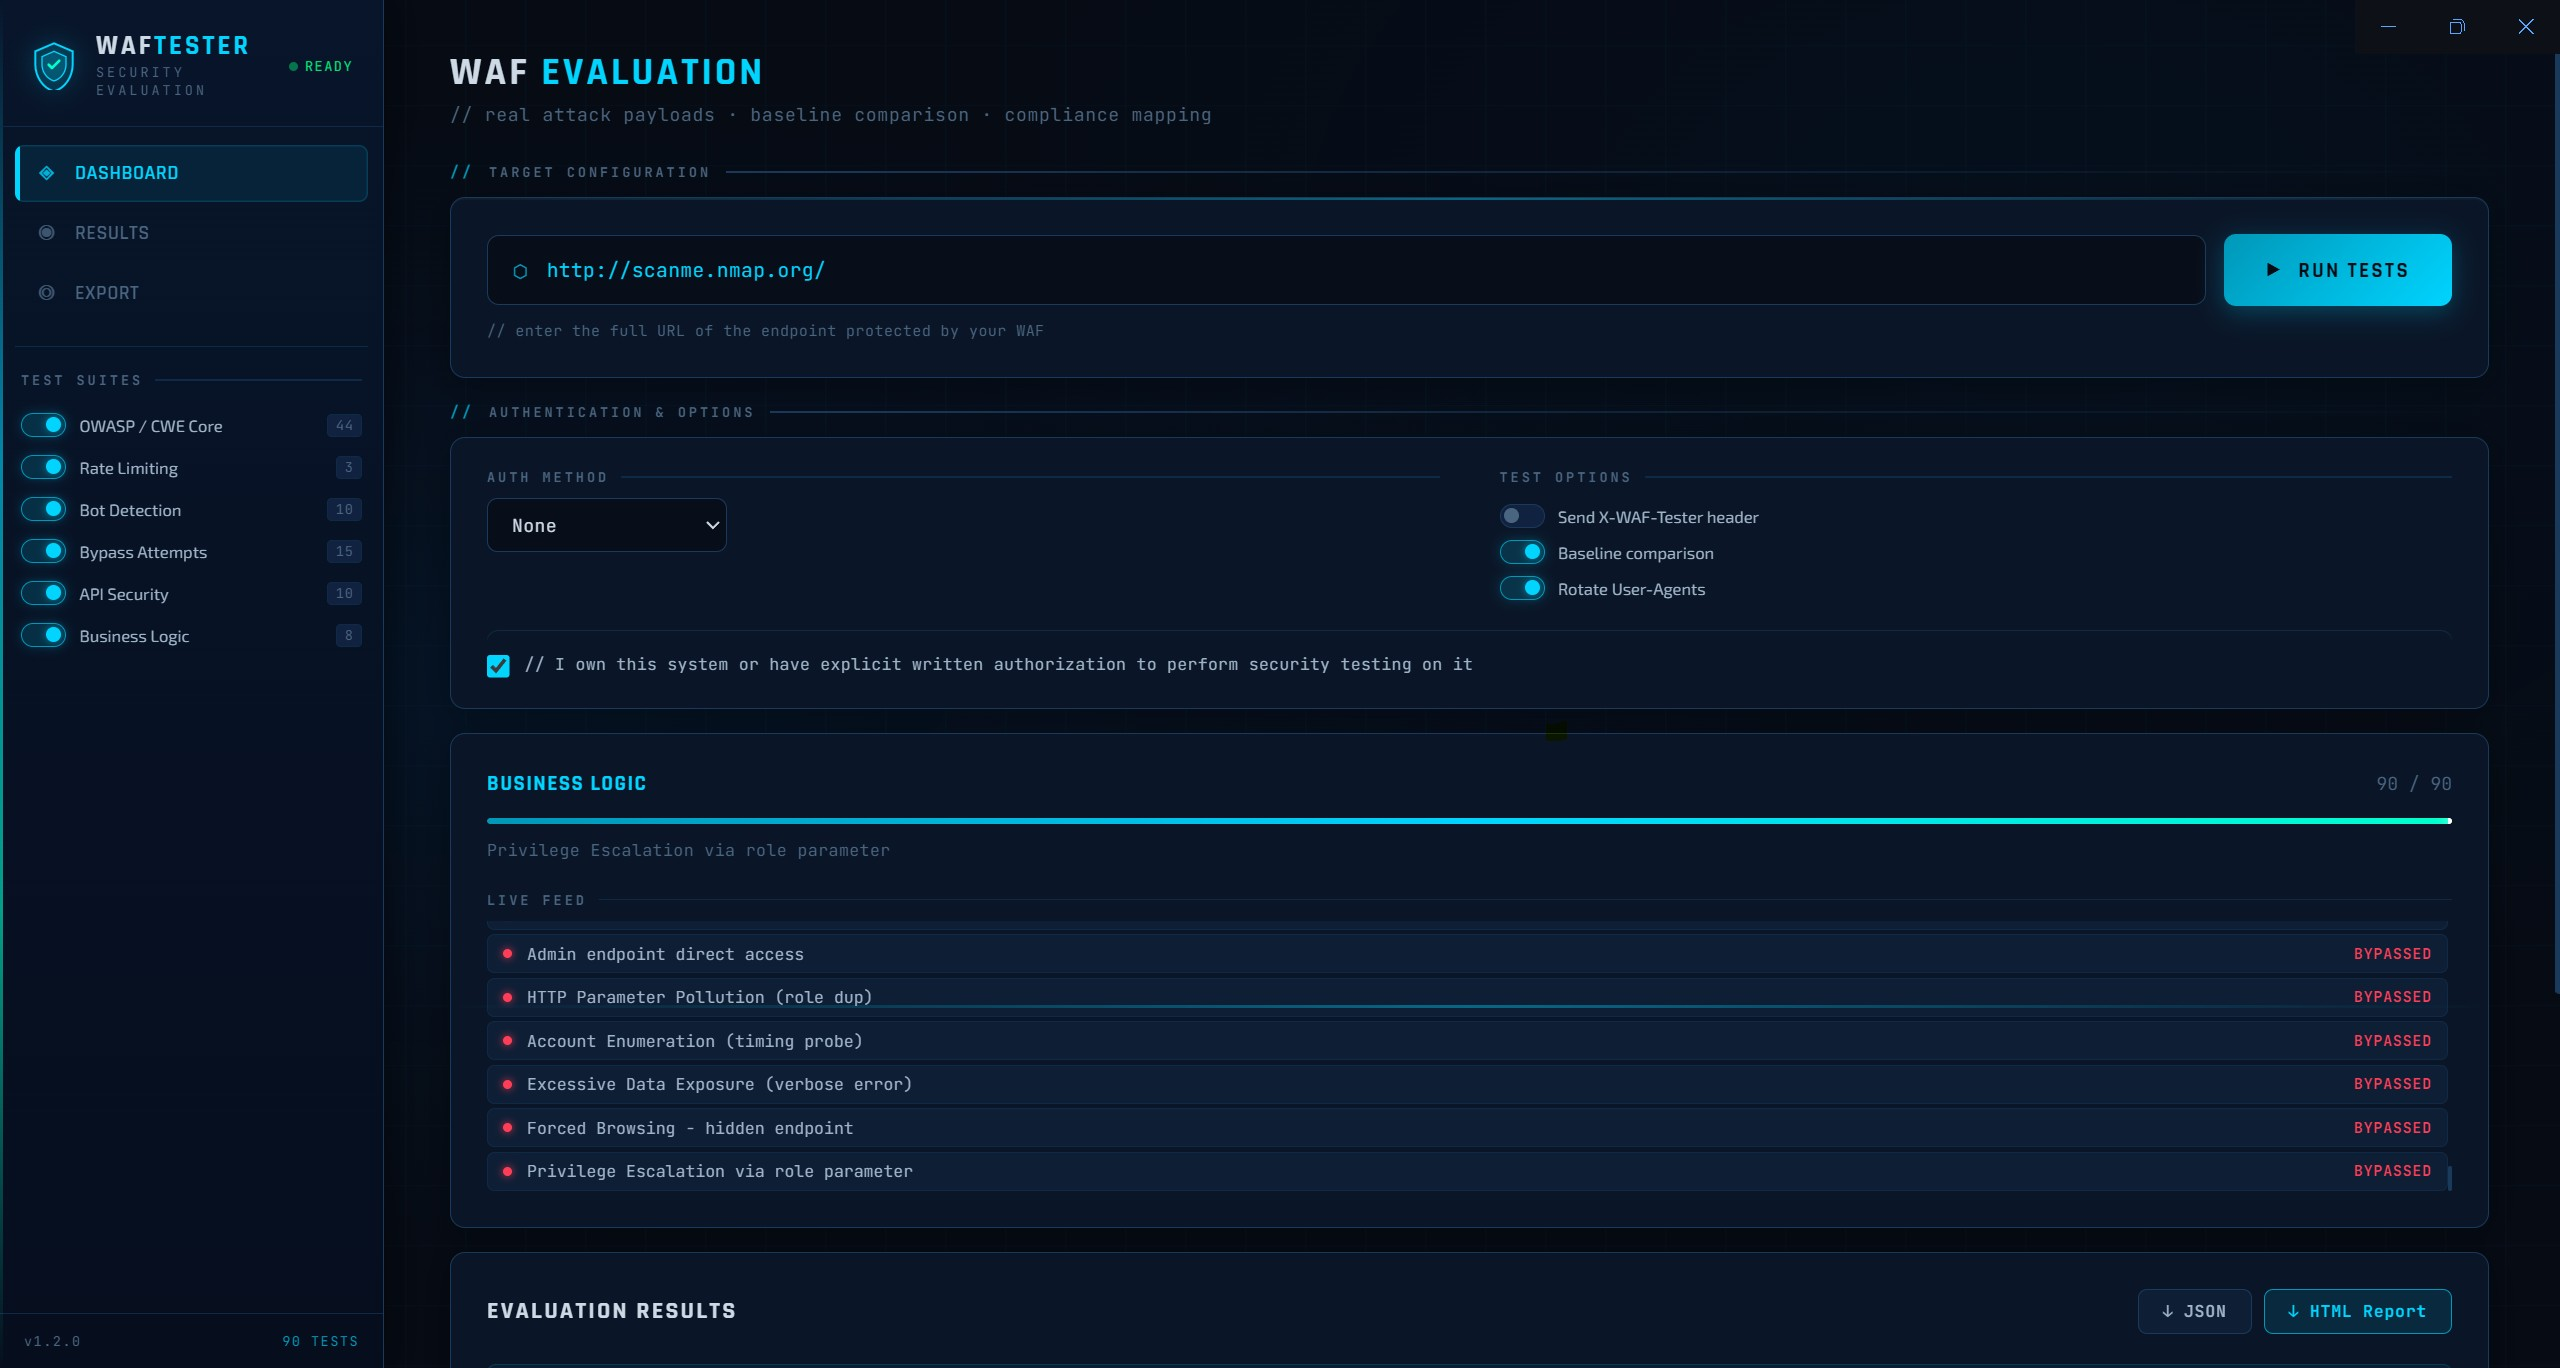 kpomin57/waf-tester
A program for testing WAF functionality
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 knqyf263/cve-2021-40346
CVE-2021-40346 PoC (HAProxy HTTP Smuggling)
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
 sho-luv/react2shell
CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 shinthink/cve-2026-8713
Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)
 hidden-investigations/react2shell-scanner
Precision-Based Detection of RSC/Next.js Remote Code Execution Vulnerabilities (CVE-2025-55182, CVE-2025-66478)
 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit