 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit

A Python script providing an interactive shell for exploiting the critical RCE vulnerability (CVE-2025-55182) in vulnerable React Server Components and Next.js applications. This exploit targets the deserialization flaw that allows unauthenticated remote code execution. It includes a modular system for adding WAF bypass techniques.
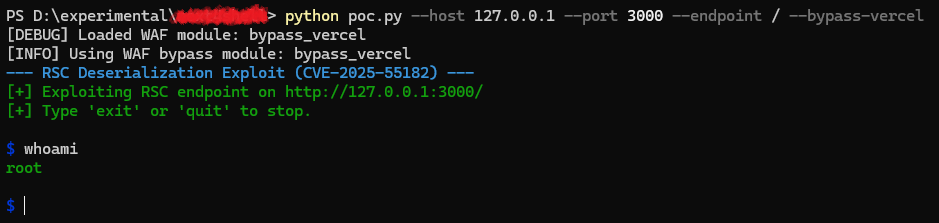
[!NOTE] This exploit is designed to interact with the vulnerable RSC protocol endpoint. Execution results are captured via the server's response mechanism. Commands resulting in no output will return
(empty).
[!CAUTION] This code is for research and educational purposes only. It is intended to help understand, detect, and remediate the CVE-2025-55182 vulnerability. Do not use it against systems without explicit authorization.
The use of this script is at the user's own risk, and the author(s) assume no responsibility for any misuse or unintended consequences.
By using this code, the user acknowledges and agrees to the following:
- The user is solely responsible for any legal consequences arising from the use of this script.
- The user will not hold the author(s) liable for any damages, losses, or legal actions resulting from the use of this code.
- The user agrees to comply with all applicable laws and regulations.
- The user acknowledges that using this script against systems without permission may violate laws and terms of service, potentially leading to severe penalties.
- The user is advised to consult their own legal counsel before using this code.
This exploit features a dynamic WAF bypass module system. Modules are stored in the waf_modules directory as separate Python files. Each module must define a modify_request(body, headers) function that takes the default request body and headers, modifies them as needed for the bypass, and returns the new body, headers.
bypass_custom.py) in the waf_modules directory containing the modify_request function.--help flag to see available bypass options (e.g., --bypass-custom for bypass_custom.py). Use the corresponding flag to activate the module.Example: A bypass_vercel.py module is included as an example, implementing techniques potentially effective against Vercel deployments.
--modify-request)The script allows direct modification of certain attributes of the requests.Session object used for making HTTP requests. This provides granular control over aspects like SSL verification, timeouts, and potentially other session-level settings.
--modify-request <KEY> <VALUE> flag. The <KEY> corresponds to an attribute of the requests.Session object (e.g., verify, timeout).<VALUE>: true/false become booleans, numeric strings become integers or floats, otherwise it remains a string.--modify-request verify True--modify-request verify False (equivalent to the old --insecure flag)python CVE-2025-55182.py --help-modify-request for a tree-like visualization of common options.requirements.txt)python -m venv venv and source venv/bin/activate on Unix-like systems or venv\Scripts\activate on Windows).
pip install -r requirements.txt
waf_modules directory:
mkdir waf_modules
bypass_vercel.py) inside this directory.Set up a vulnerable environment (for testing only):
docker run --rm -p 127.0.0.1:3000:3000 ghcr.io/l4rm4nd/cve-2025-55182:latest
More information: https://github.com/l4rm4nd/CVE-2025-55182
Execute the script:
python CVE-2025-55182.py --help # To see all options, including WAF bypasses
# Example with a bypass module:
python CVE-2025-55182.py --host 127.0.0.1 --port 3000 --endpoint / --bypass-vercel
If not using command-line arguments, the script will prompt interactively for host, port, and endpoint.
Interact with the shell:
exit or quit to terminate the shell session.






