Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
140 results
bypass-firewalls-by-DNS-history preview

bypass-firewalls-by-DNS-history

GitHubvincentcox/bypass-firewalls-by-dns-history

Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

dns-analysispenetration-testingreconnaissance+2
1.3k
6 years ago
hakoriginfinder preview

hakoriginfinder

GitHubhakluke/hakoriginfinder

Tool for discovering the origin host behind a reverse proxy. Useful for bypassing cloud WAFs!

information-gatheringreconnaissancewaf-bypass+1
1.1k2 months ago
nowafpls preview

nowafpls

GitHubassetnote/nowafpls

Burp Plugin to Bypass WAFs through the insertion of Junk Data

ids-ips-evasionpenetration-testingred-teaming+3
1.5k1 year ago
cloudbunny preview

cloudbunny

GitHubwarflop/cloudbunny

CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…

information-gatheringosintreconnaissance+2
3762 years ago
CRLFsuite preview

CRLFsuite

GitHubraghavd3v/crlfsuite

The most powerful CRLF injection (HTTP Response Splitting) scanner.

penetration-testingvulnerability-scannerswaf-bypass+2
5983 years ago
Forbidden-Buster preview

Forbidden-Buster

GitHubsn1r/forbidden-buster

A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…

fuzzingids-ips-evasionpenetration-testing+2
2512 years ago
unwaf preview

unwaf

GitHubmmarting/unwaf

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
1968 months ago
forbidden preview

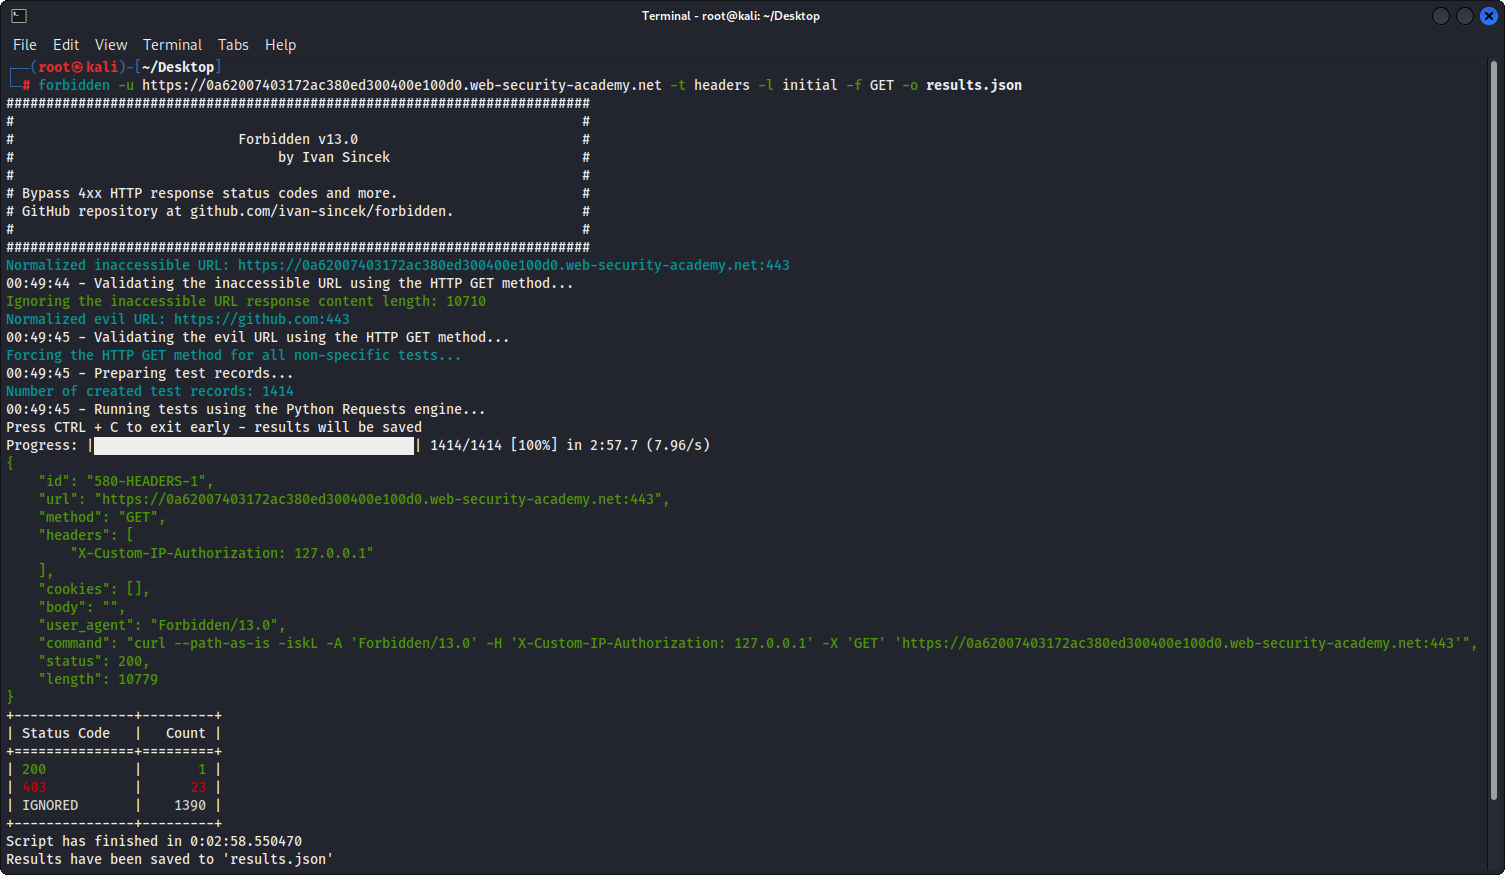
forbidden

GitHubivan-sincek/forbidden

Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

fuzzingids-ips-evasioninformation-gathering+5
2571 year ago
crithit preview

crithit

GitHubcodingo/crithit

Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…

information-gatheringpenetration-testingvulnerability-scanners+2
2126 years ago
burp-vps-proxy preview

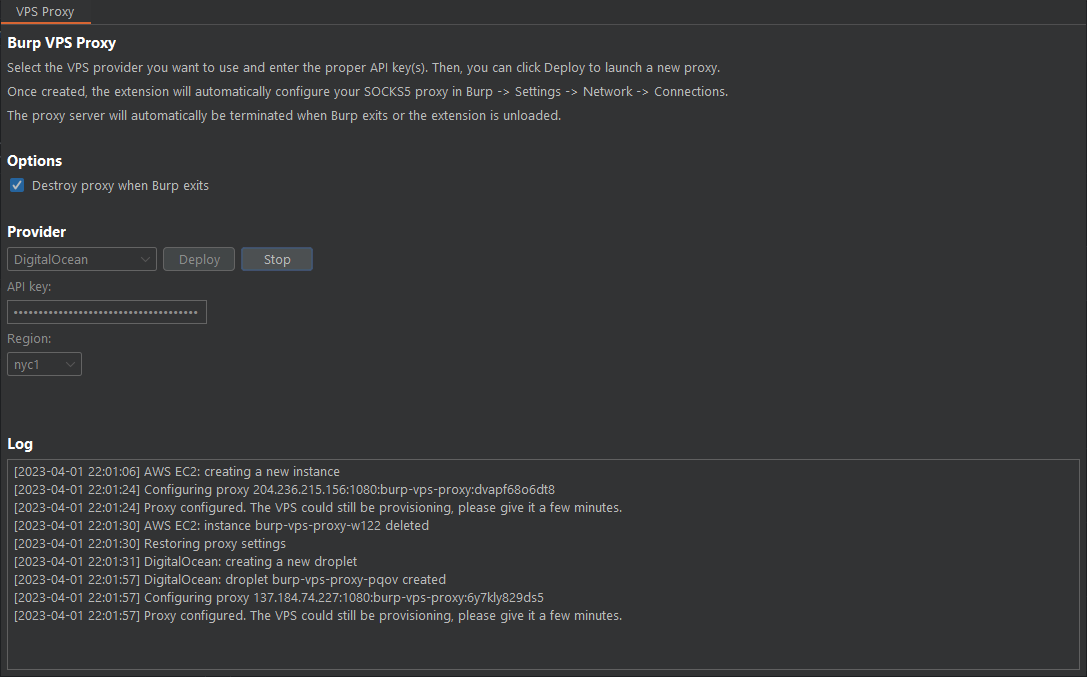
burp-vps-proxy

GitHubd3mondev/burp-vps-proxy

This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.

penetration-testingutilities-frameworkswaf-bypass+1
2483 years ago
react2shell-ultimate preview

react2shell-ultimate

GitHubhackersatyamrastogi/react2shell-ultimate

React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…

command-and-controlexploitationpayload-generation+4
15210 months ago
url-cheatsheet-data preview

url-cheatsheet-data

GitHubportswigger/url-cheatsheet-data

This is the data that powers the PortSwigger URL validation bypass cheat sheet.

curated-resourceseducationvulnerability-analysis+2
629 months ago
cpanel-sessionscribe preview

cpanel-sessionscribe

GitHubrfxn/cpanel-sessionscribe

Detection, mitigation, and reverse-engineering tooling for CVE-2026-41940 (SessionScribe): the cPanel/WHM unauthenticated session-forgery…

defensive-toolsexploitationforensics+7
145 months ago
CVE-2024-34102 preview

CVE-2024-34102

GitHub11whoami99/cve-2024-34102

Proof-of-concept for CVE-2024-34102 exploiting unauthenticated Magento XXE and WAF bypass by sending a crafted request to the…

exploitationpenetration-testingvulnerability-analysis+2
32 years ago
anti-jndi preview

anti-jndi

GitHubph0lk3r/anti-jndi

Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.

defensive-toolsids-ips-evasionmisconfiguration+3
24 years ago
CVE-2026-5524-PoC preview

CVE-2026-5524-PoC

GitHubiicaicai/cve-2026-5524-poc

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

exploitationinformation-gatheringpayload-development+8
4 months ago
log4j-scanner preview

log4j-scanner

GitHubmanishkanyal/log4j-scanner

A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046

exploitationfuzzingpenetration-testing+3
14 years ago
py-log4shellscanner preview

py-log4shellscanner

GitHubscheibling/py-log4shellscanner

Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)

dns-analysisexploitationfuzzing+3
4 years ago
Previous123…8Next