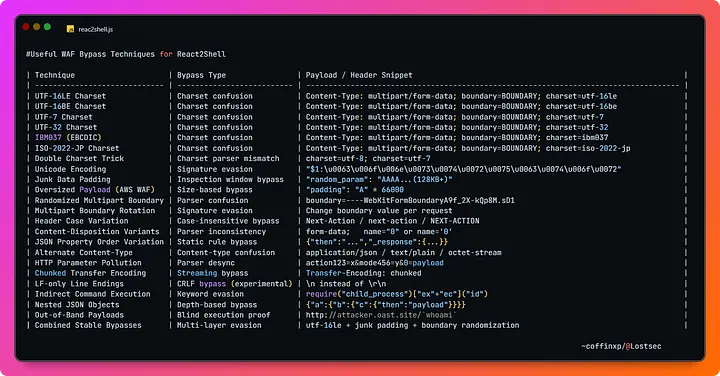
CVE-2025-55182-research

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.

🛡️ Open-source and cloud-native Web Application Firewall (WAF)

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

Local file inclusion exploitation tool

Next generation web scanner

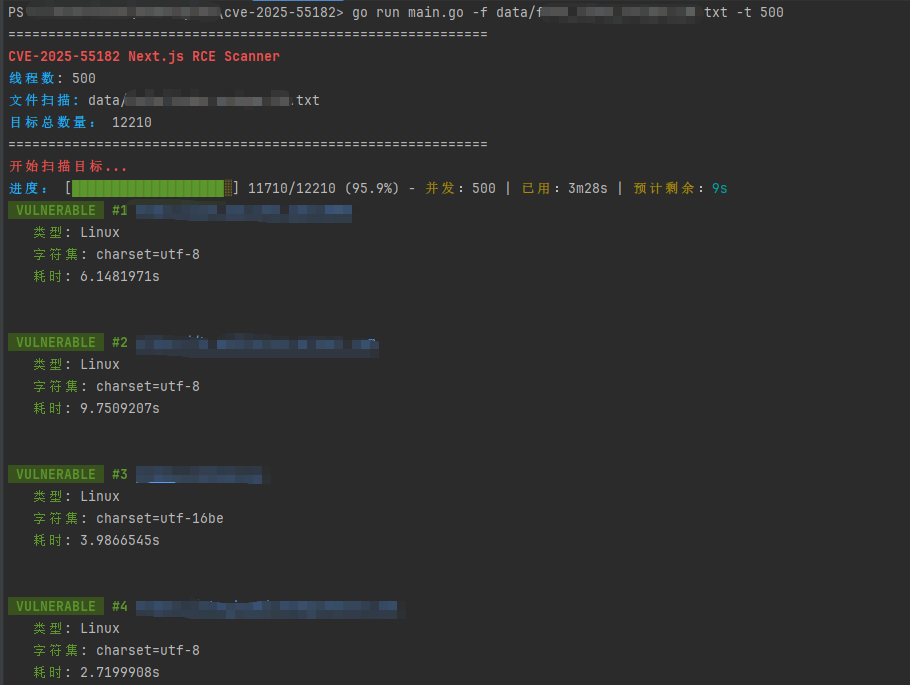
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)

A evolved version of assetnote CVE-2025-55182 scanner

CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)

An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…

Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…

Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…

CVE-2025-6389

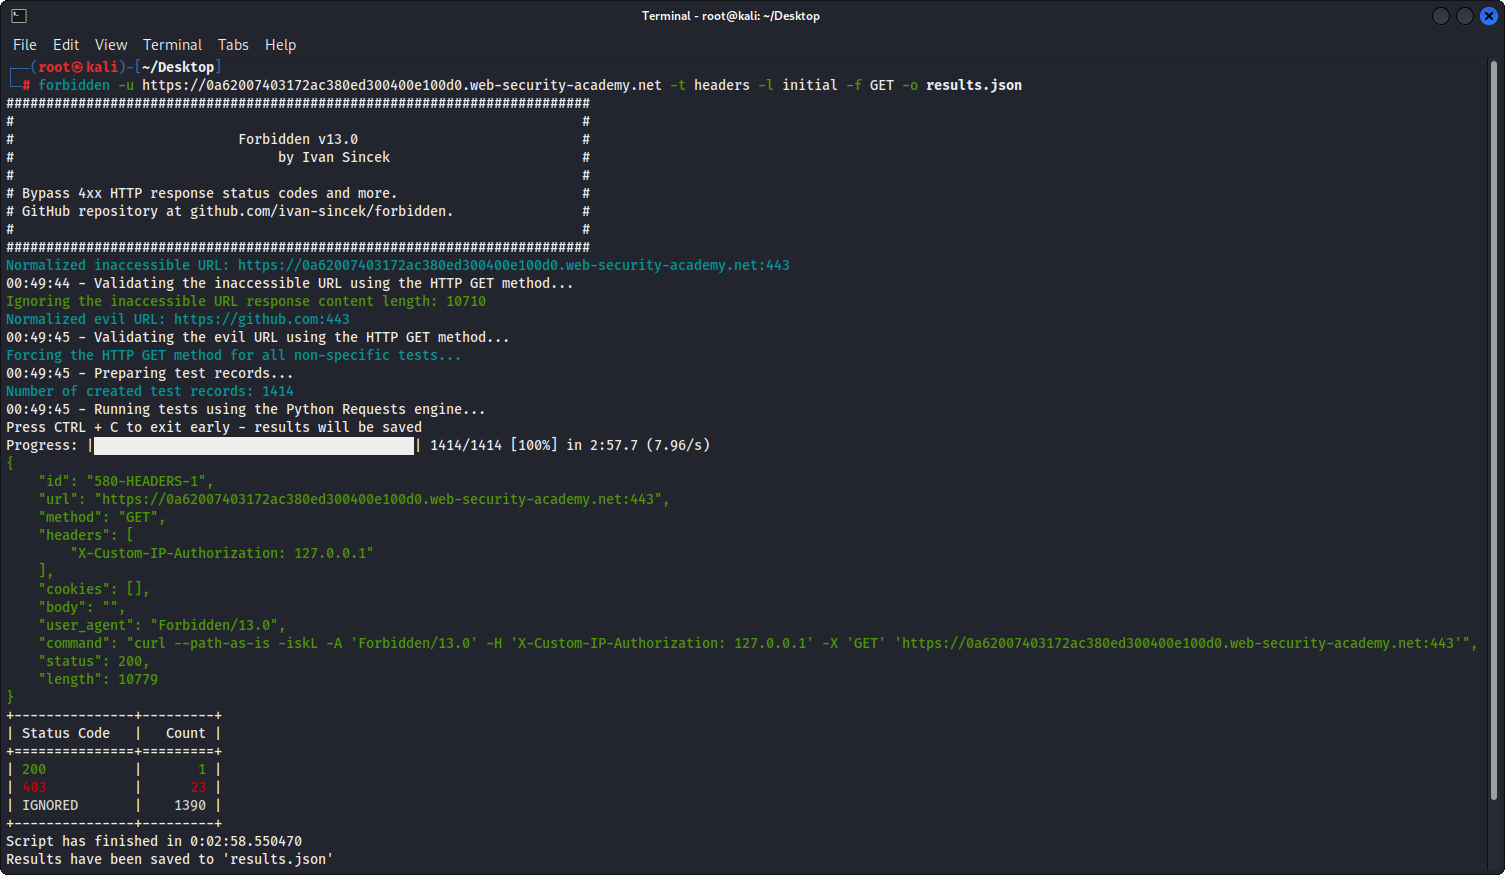
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…

Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)