

scapy
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
bluetooth-securitycryptographydata-exfiltration+23
12.6k
secdev/scapyPython-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 san-tus/dorkwright
From Dork to Download: Automating Google Dorks with Playwright
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 acharaf06/cve-2017-5638-attack-and-defense
Docker-based security lab demonstrating Apache Struts2 S2-045 (CVE-2017-5638) exploitation and defense, featuring vulnerable and patched applications…
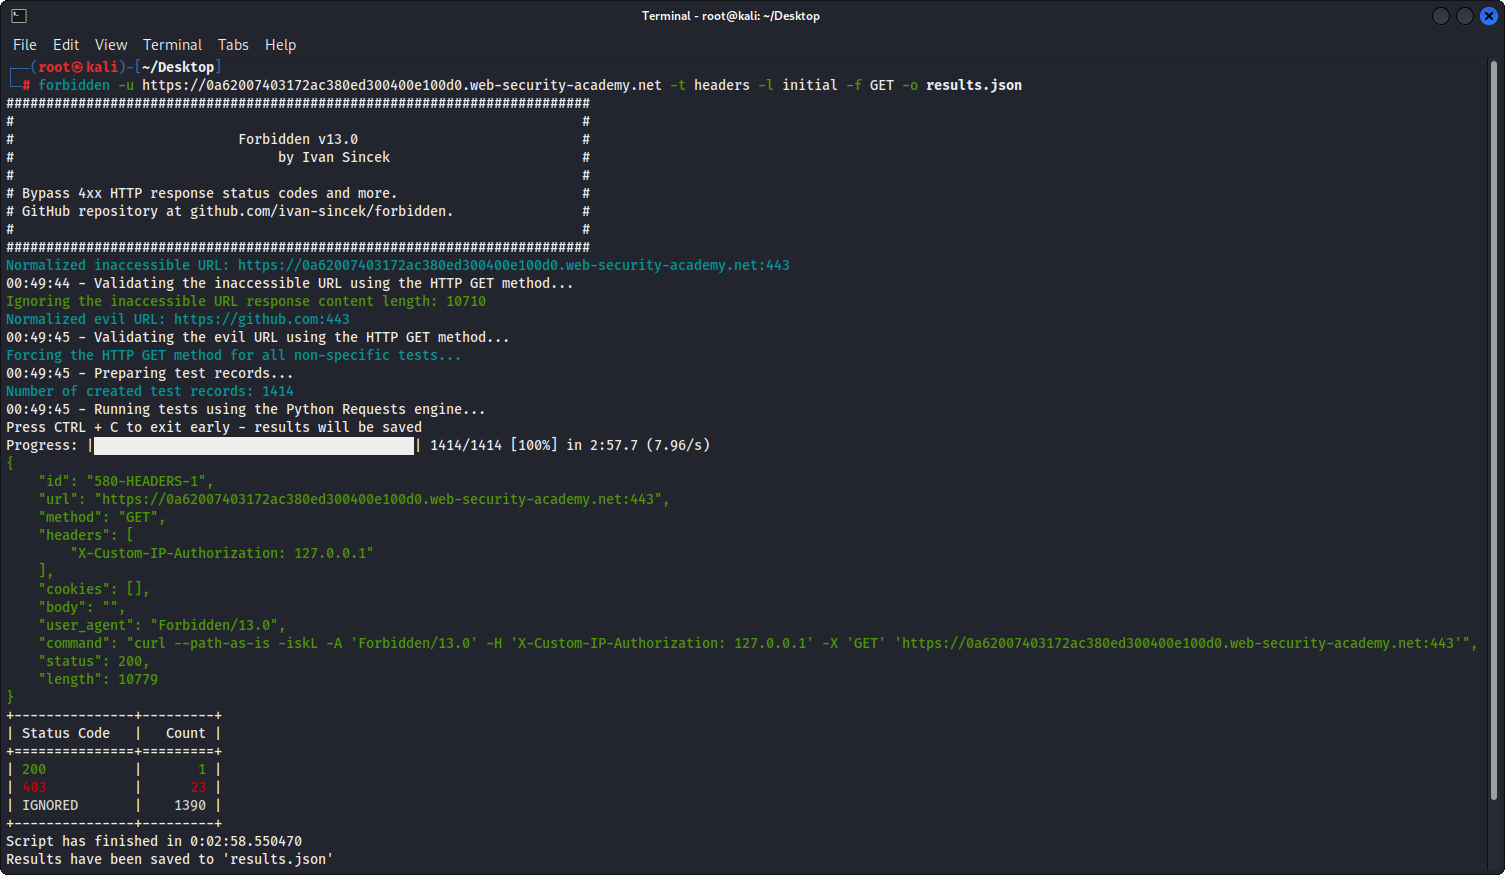 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 imbas007/cve-2025-32429-checker
Python-based vulnerability scanner for detecting CVE-2025-32429 SQL injection in XWiki platforms. Supports single/bulk scanning, WAF detection,…
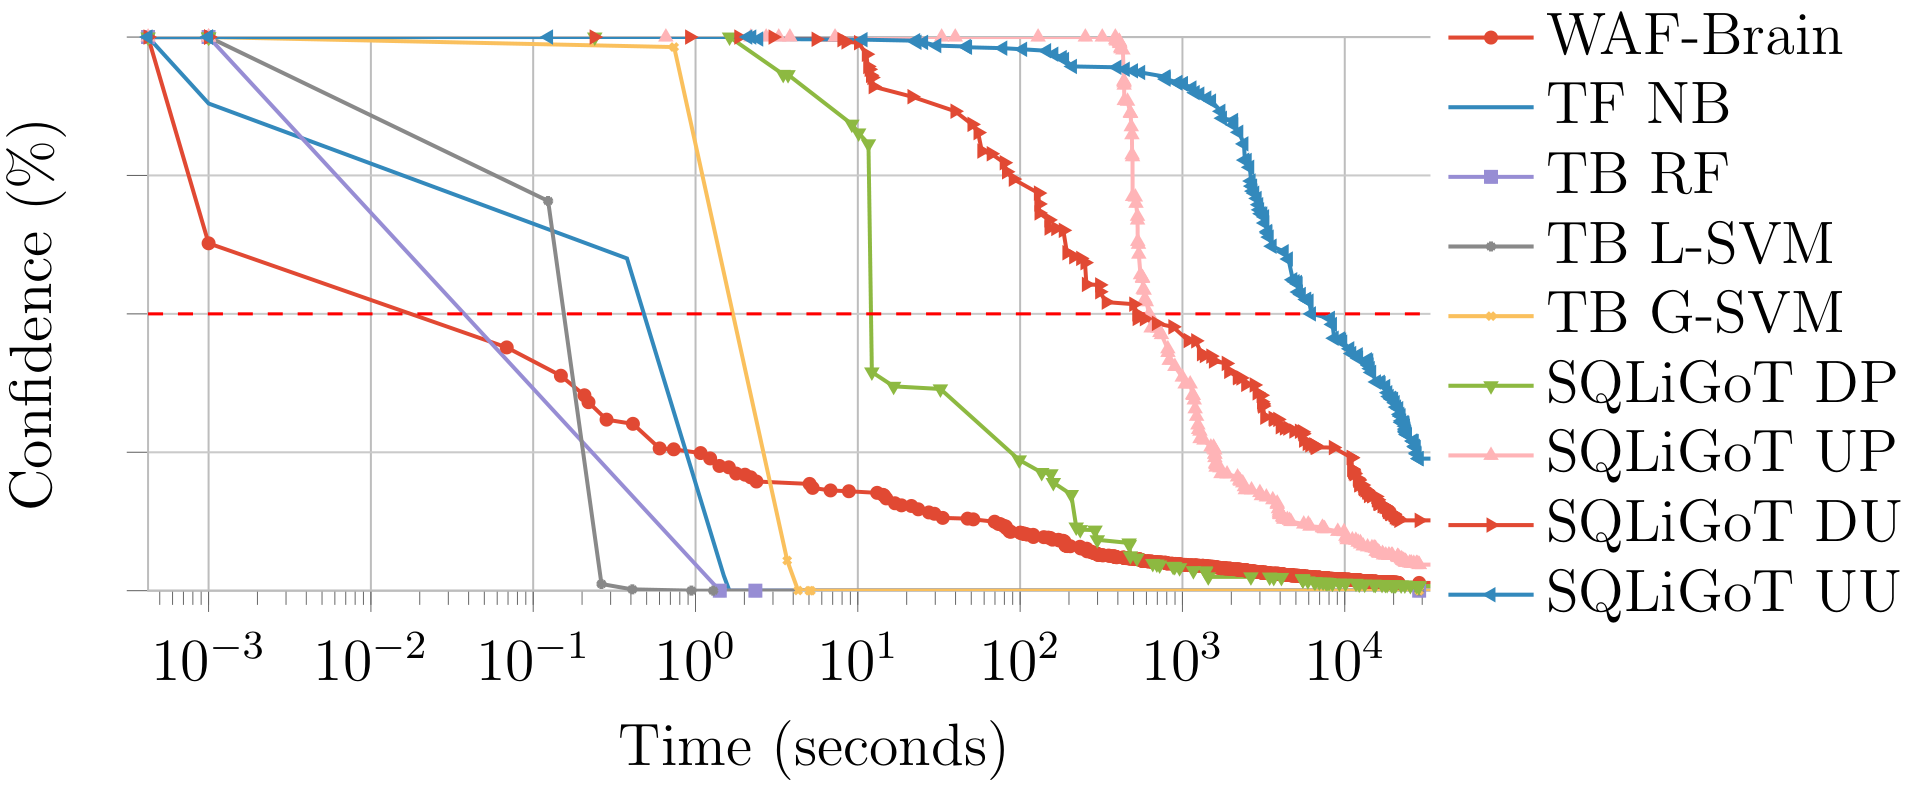 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
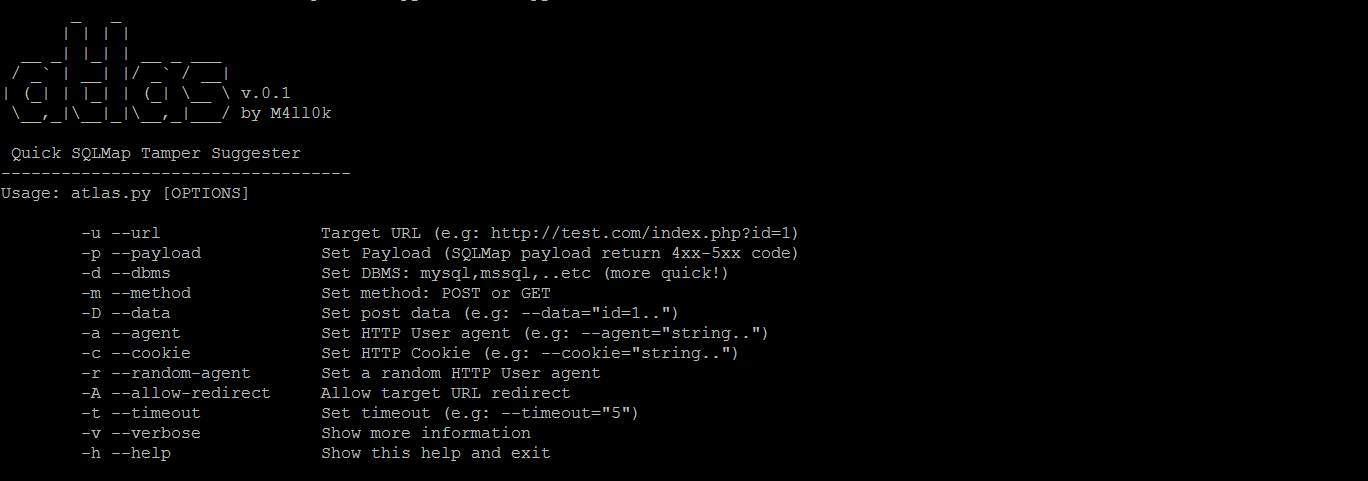
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 keramas/mssqli-duet
SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.