CVE-2026-78006-CVE-2026-78159

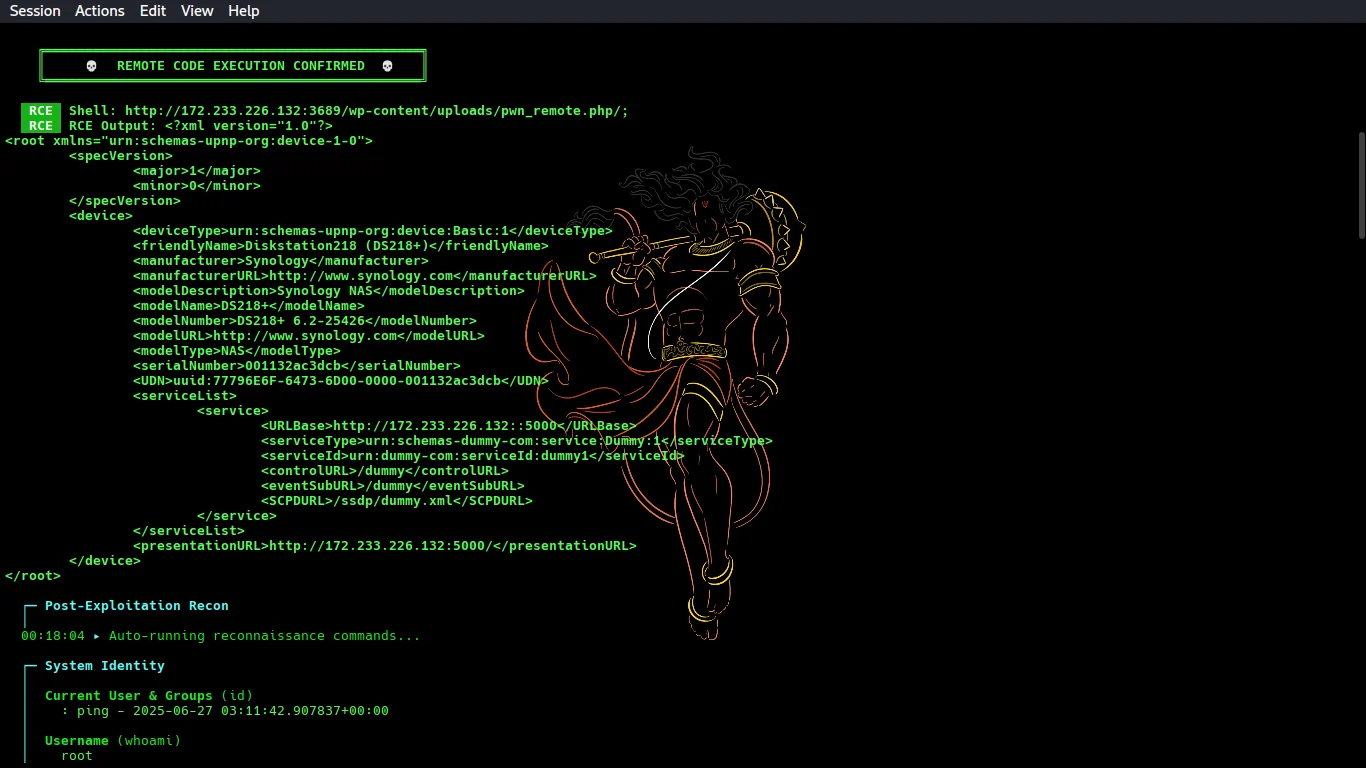
Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…

Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…

Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…

Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…

Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…

Testing WAF protection against CVE-2021-44228 Log4Shell

A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046

Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…

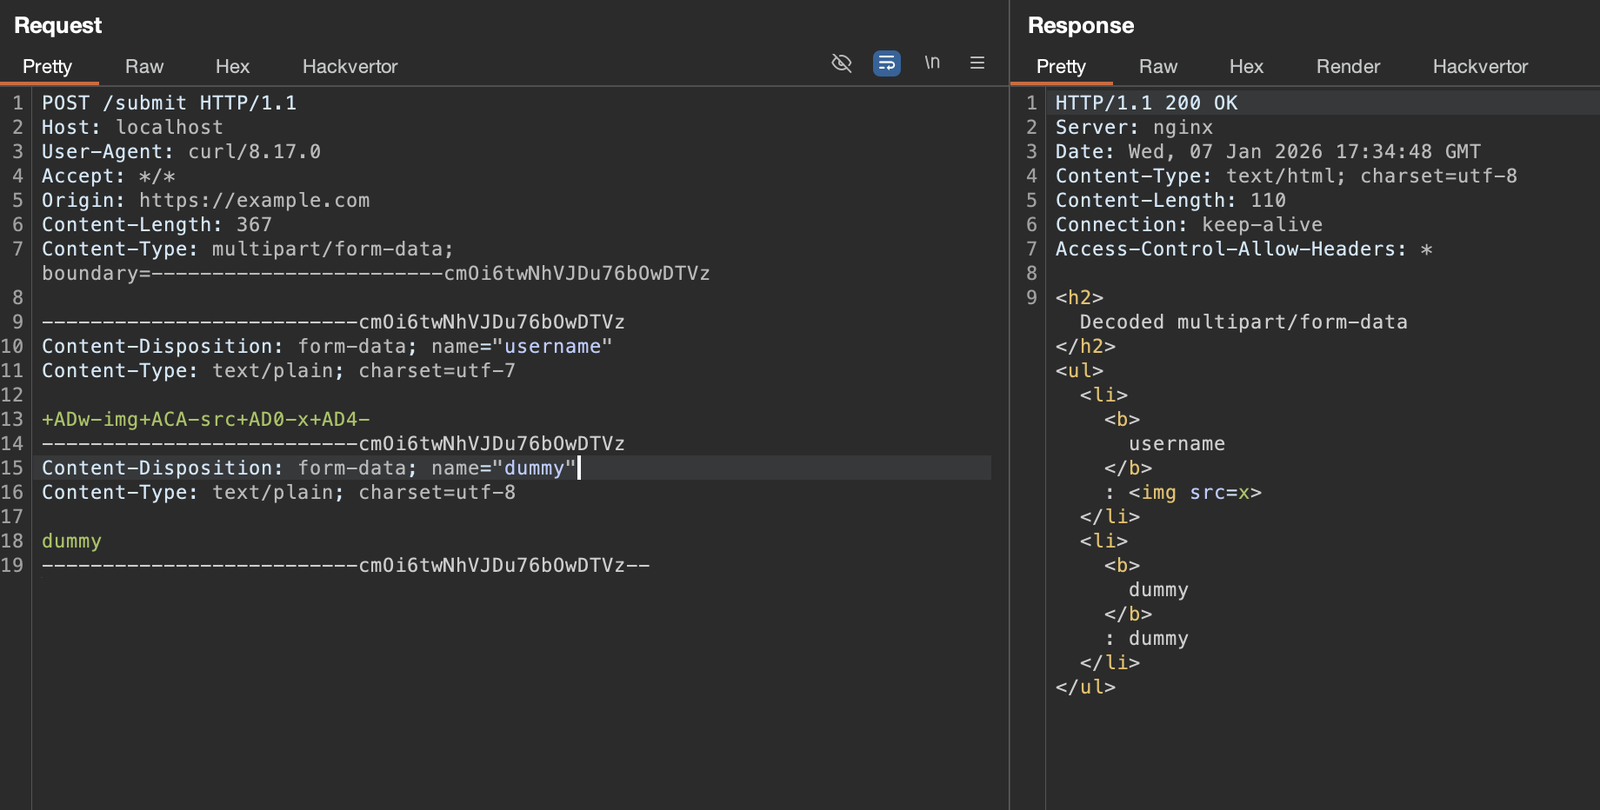
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

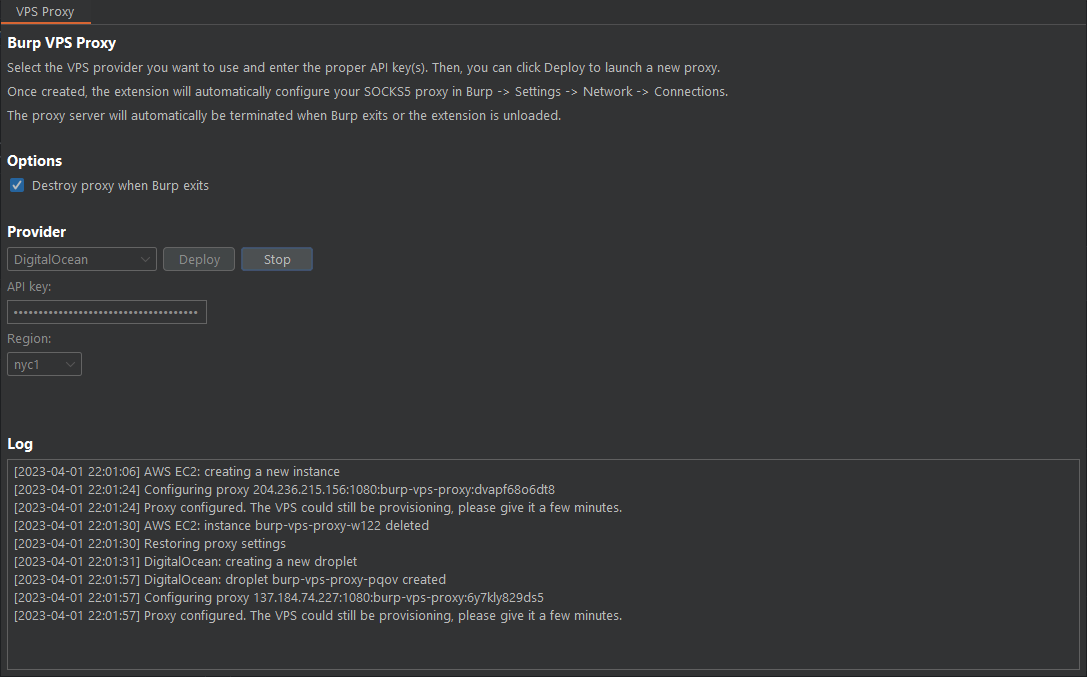
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.

RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)

evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).

Proof-of-concept exploit for CVE-2020-6519 - a Chromium zero-day that fully bypasses Content Security Policy (CSP) across platforms, enabling script…

Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.