

cve-lite-cli
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
code-analysiscurated-resourcesdevsecops+5
756
owasp/cve-lite-cliFast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 google/osv.dev
Open source vulnerability DB and triage service.
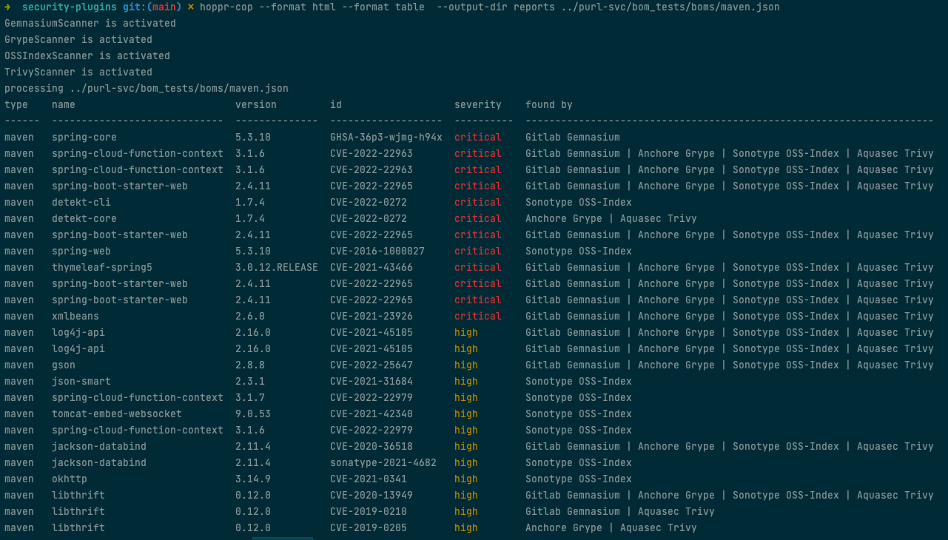
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
 darabium/cve-2026-24733
Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
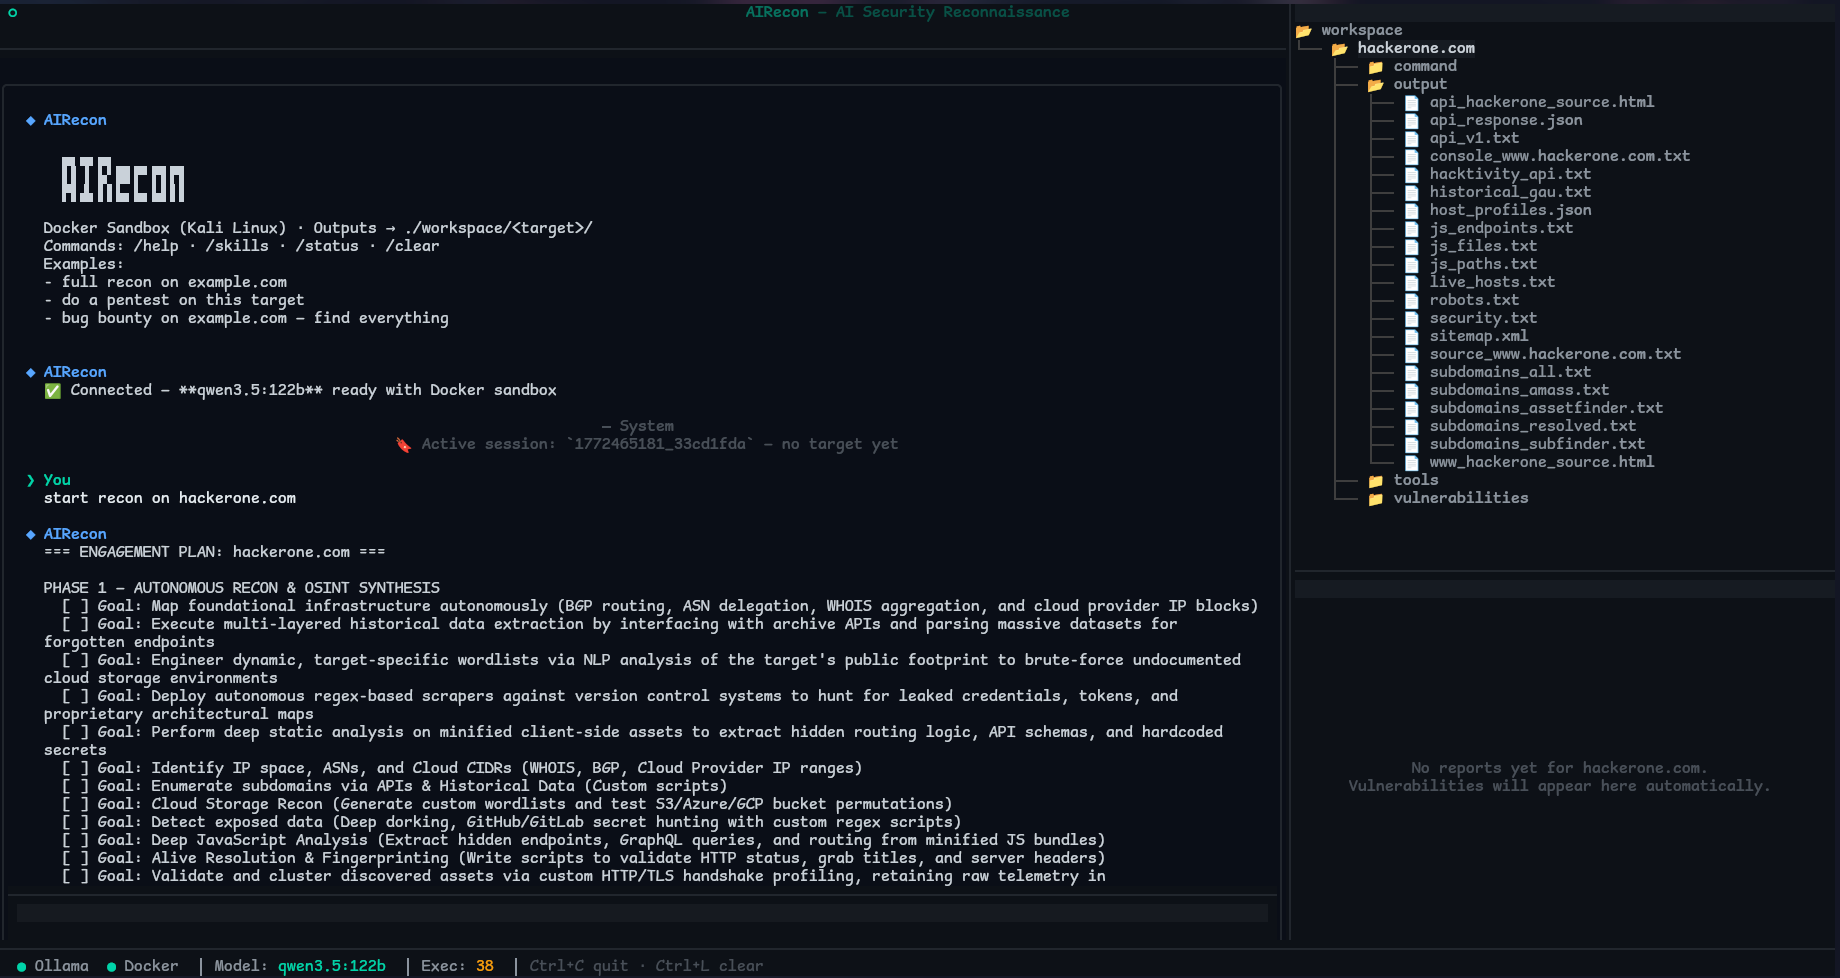 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
 pyupio/safety
Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
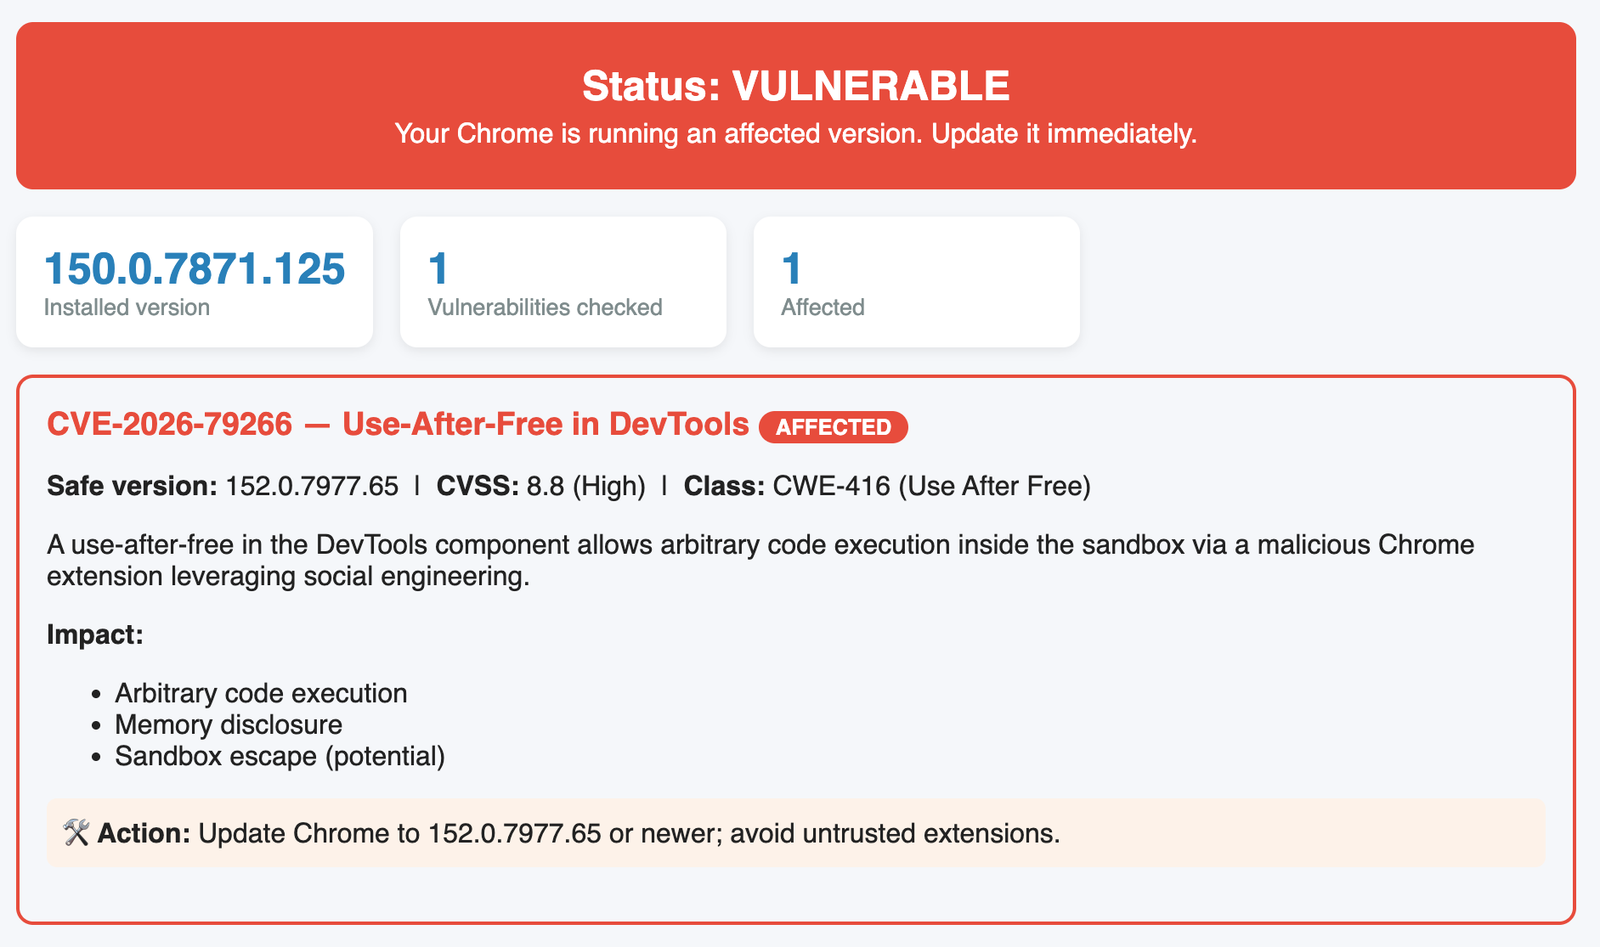 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 sanaullahamanullah/xss2shell-check
Non-destructive detector for CVE-2026-64638 (XSS2Shell) — WordPress pre-auth XSS reflection primitive
 anggatechi/cve-2026-63030
WordPress Core Pre-Auth RCE — Batch Route Confusion + SQL Injection