
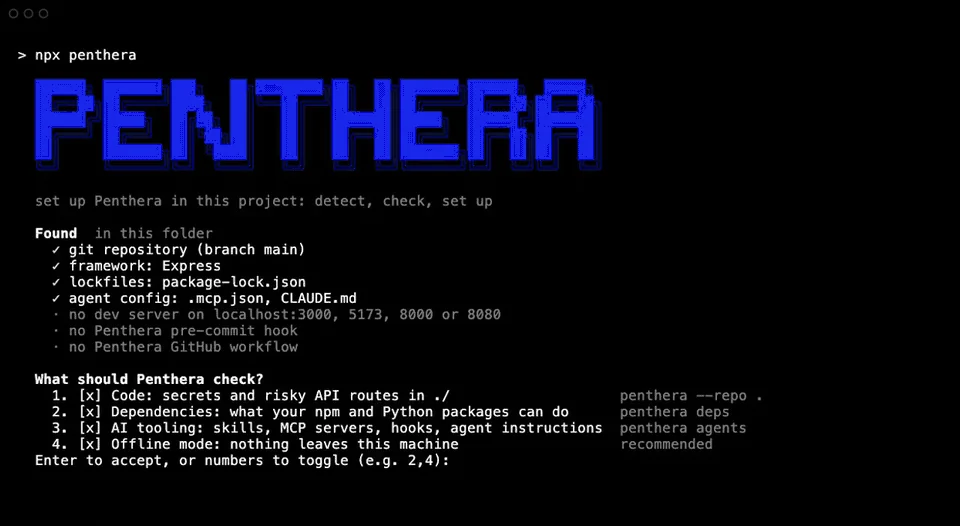
penthera
 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
ai-securitycode-analysisconfiguration-auditing+7
78
danoszz/pentheraOffline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 shadowguardai/ti-a-ti-cveexploitchecker
Determines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
 lu1sdv/wafmeow
wafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
 clearhandreview/vulnerpocalypse-containment
Open-source vulnerability analysis, CVE tracking, patch verification, and temporary security containment tools
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
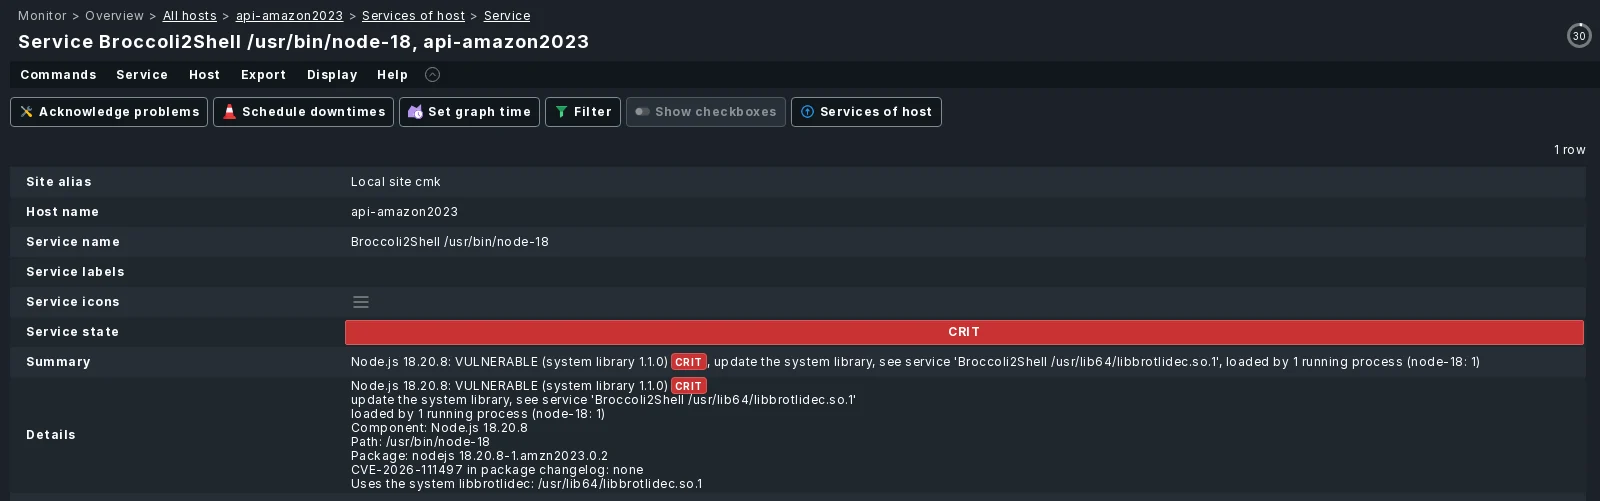
 checkmk1/checkmk_broccoli2shell
Checkmk extension that audits Linux hosts for Brotli decoders (libbrotlidec, Node.js, Python, .NET) affected by CVE-2026-111497, checking versions,…
 lukr54/edk2-security
EDK2 BrotliCustomDecompressLib security findings — coordinated disclosure
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 thebadinteger/p2pwn
Dahua cameras security scanner via P2P
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
 checkmk1/checkmk_php2shell
Checkmk extension with an agent plug-in that inventories PHP binaries and Apache mod_php on Linux hosts and reports PHP2Shell…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 ntoskernel/deepsecrets
Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
 0xblackash/cve-2026-111497
Advisory and proof-of-concept toolkit for CVE-2026-111497 (Node2Shell), a Brotli heap overflow in Node.js, with trigger scripts, version checker, and…
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…