

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
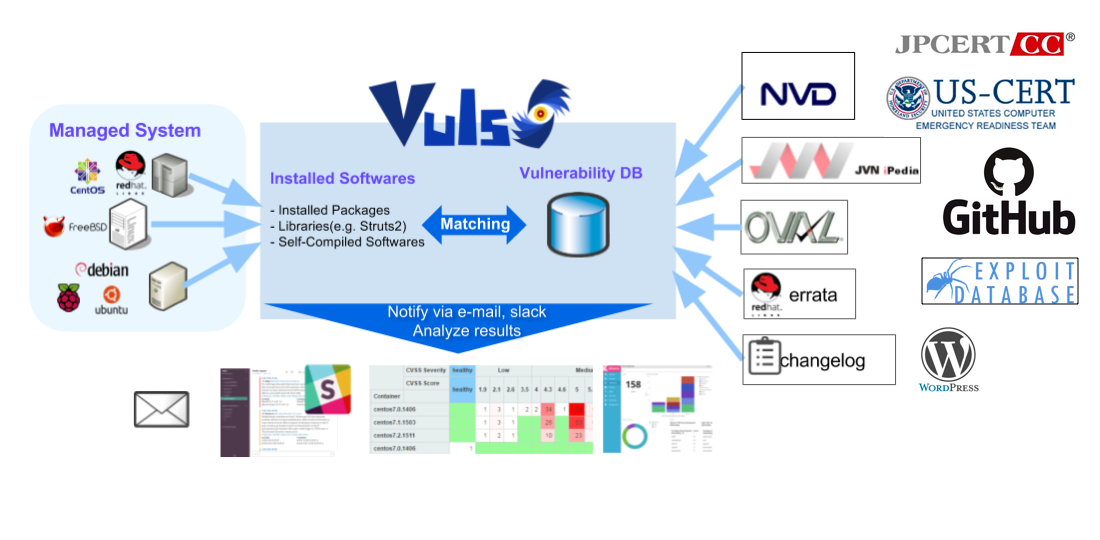 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 urbanadventurer/whatweb
Next generation web scanner
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
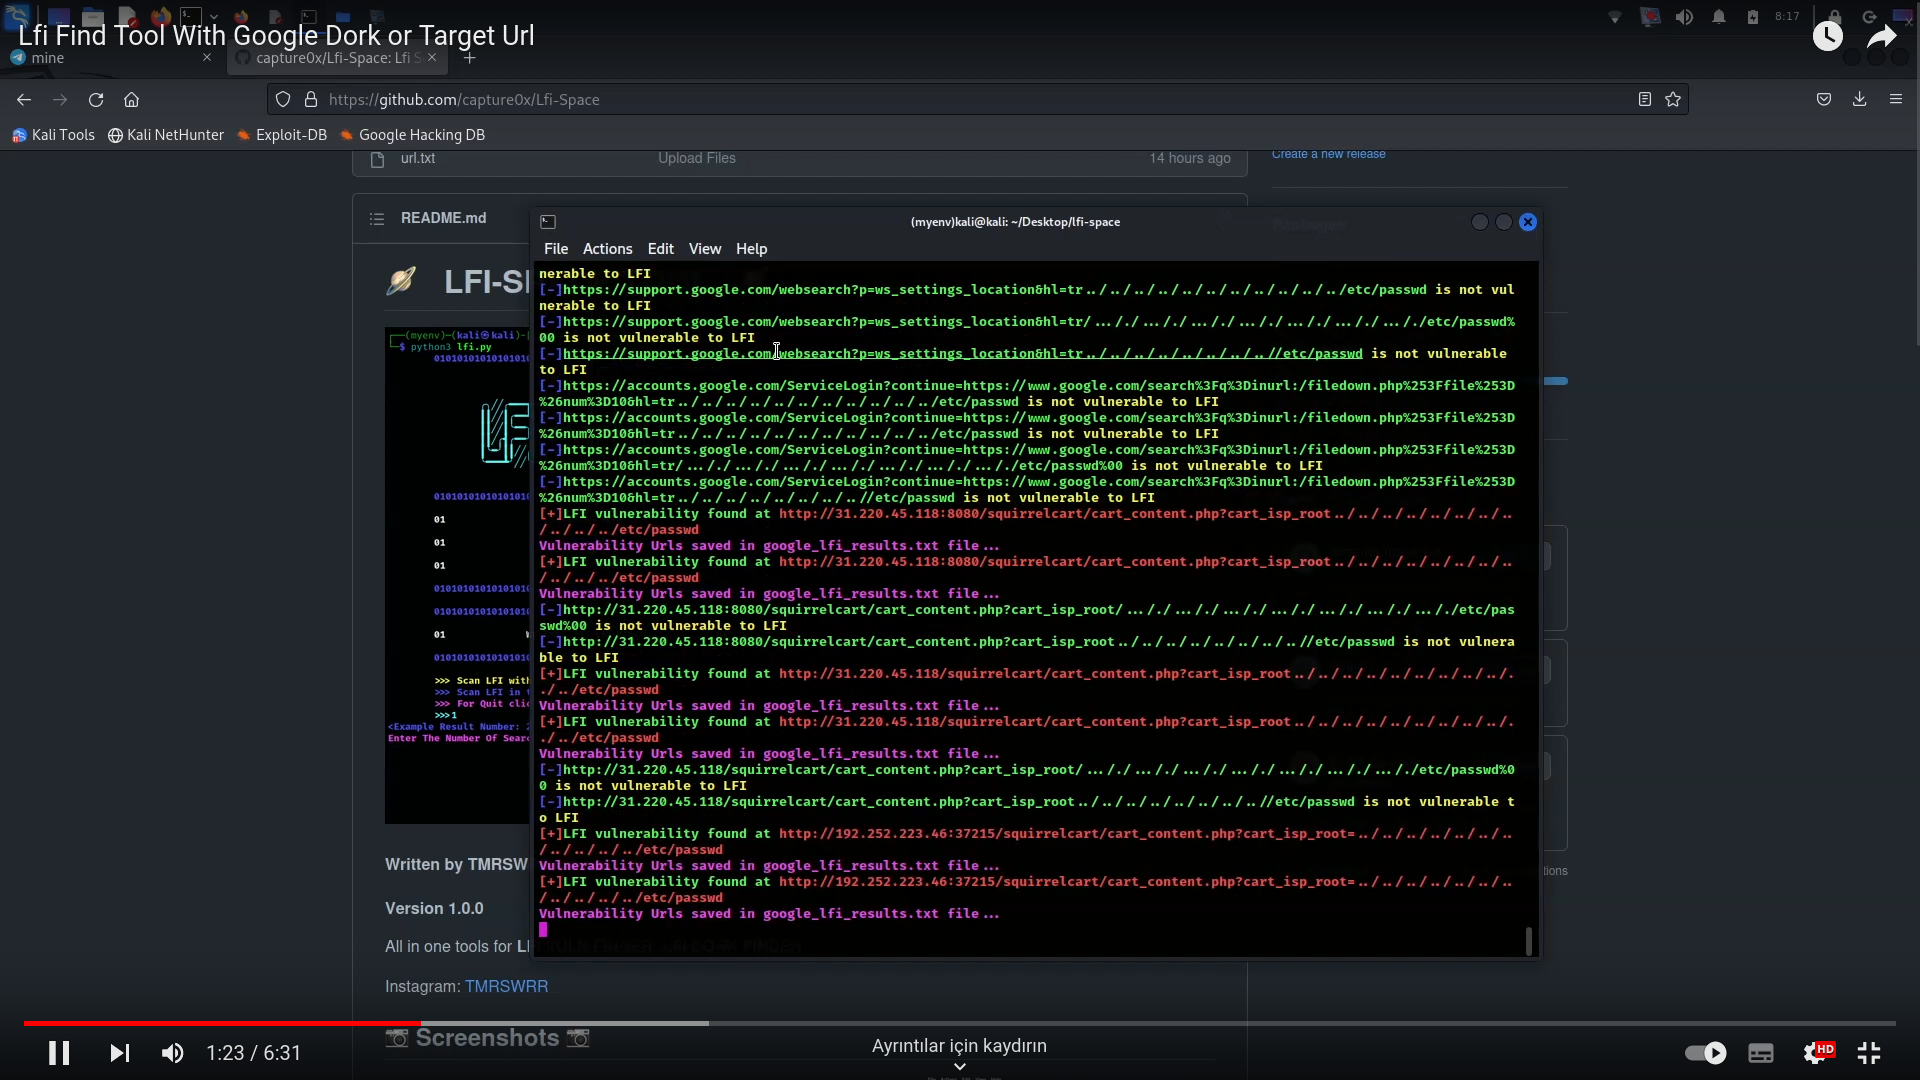 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…