

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.7k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
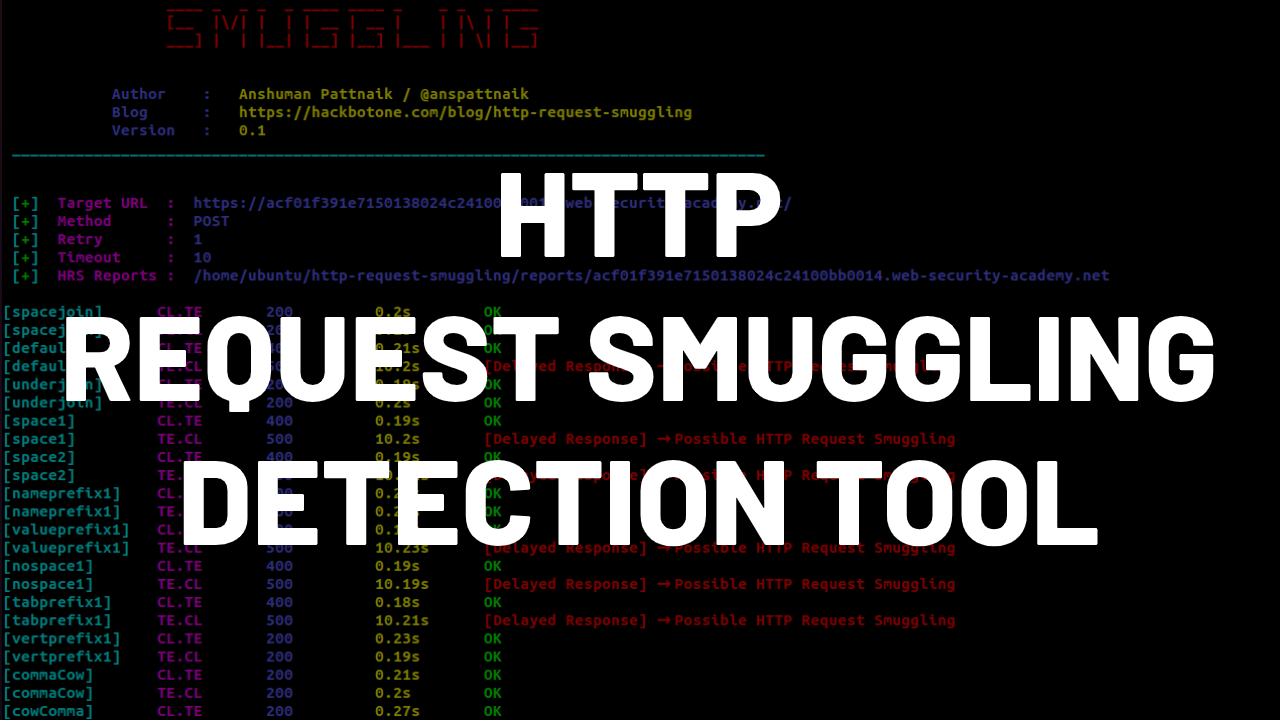 anshumanpattnaik/http-request-smuggling
CLI tool to detect HTTP Request Smuggling vulnerabilities using time-delay analysis with built-in CL.TE and TE.CL payloads for automated security…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
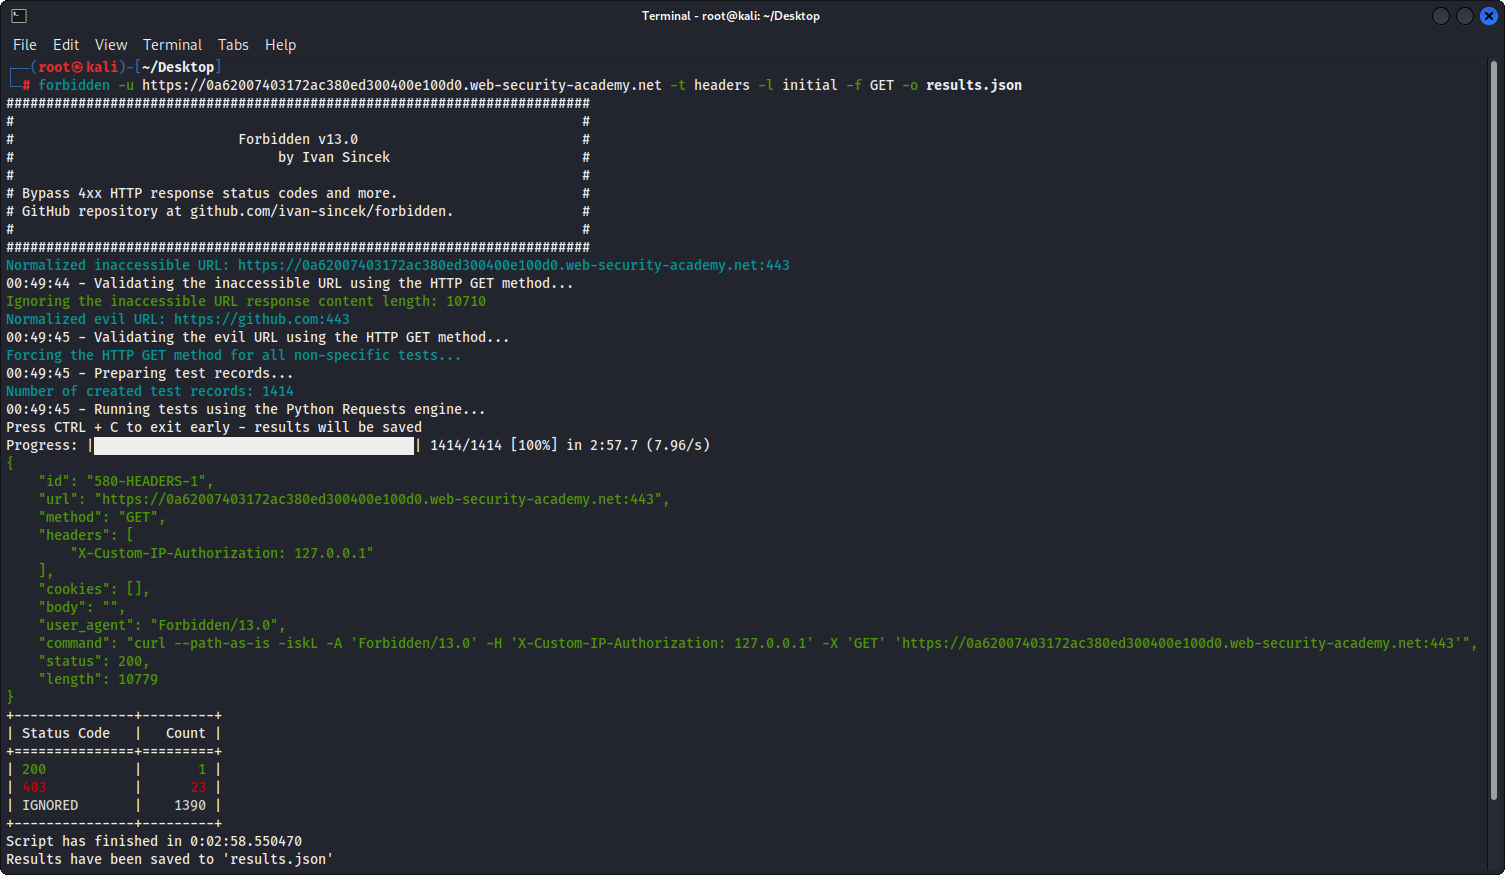 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 gpiechnik2/nmap-cve-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
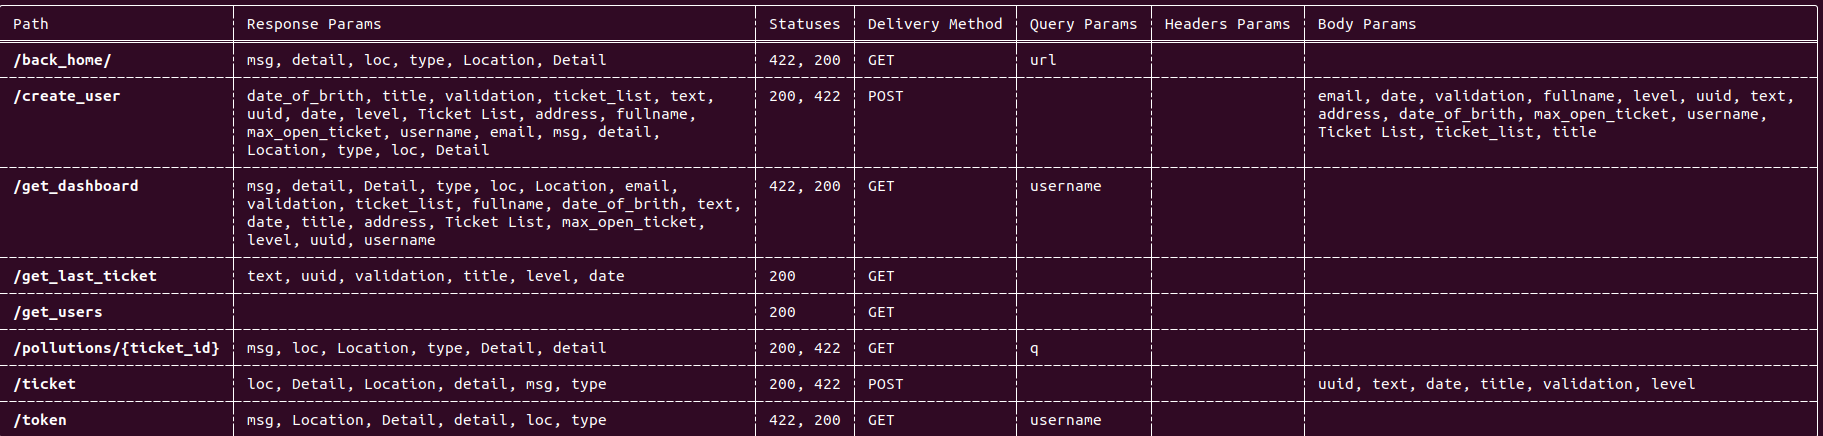 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
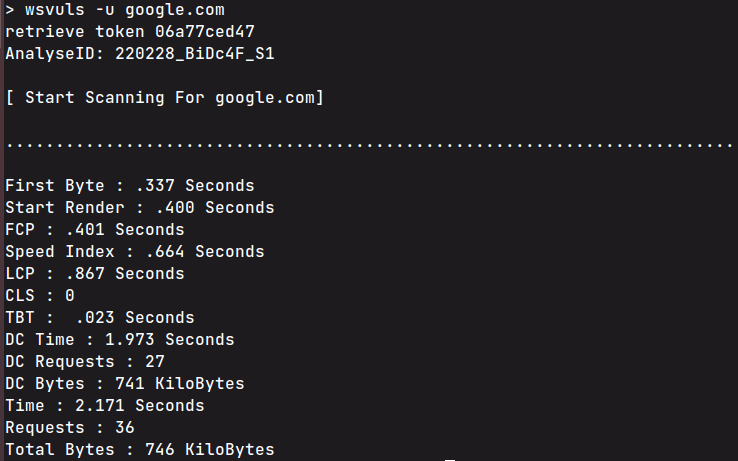 anouarbensaad/wsvuls
CLI website vulnerability scanner that detects outdated server software, insecure HTTP headers, and extracts Cloudflare IP/port data with performance…
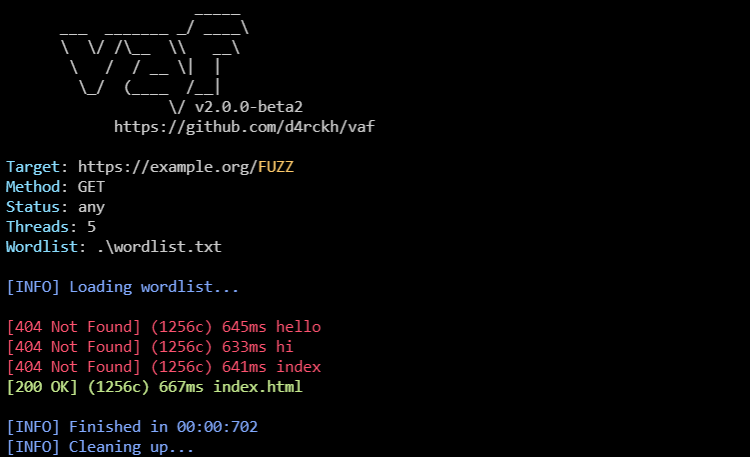 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
 vulnerscom/burp-vulners-scanner
Vulnerability scanner based on vulners.com search API
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities